Tag: emerging threats
8486 articles
China's Silk Typhoon Hacker Extradited to US Over COVID Cyberattacks
A Chinese hacker, Xu Zewei, has been extradited to the US from Italy for masterminding a series of devastating cyberattacks on US universities, immunologists, and virologists working on COVID-19 vaccines, treatments, and testing between 2020 and 2021. He faces charges of wire fraud and conspiracy for his role in the attacks.

Microsoft Urges iPhone Users to Reauthenticate After Outlook Outage
If you're an iPhone user who relies on Outlook, you may need to re-enter your login credentials to access your account after a global outage hit the service. Microsoft has confirmed the issue is resolved, but iOS users will need to manually sign in again through the default Mail app.

North Korean Hackers Exploit Crypto Firms with AI-Driven Zoom Lures
North Korean hackers launched a massive spear-phishing campaign, targeting over 100 crypto organizations worldwide with cleverly crafted Zoom lures and AI-generated deepfakes. They used fake calendar invites and typosquatted meeting links to gain access and exfiltrate sensitive data in a matter of minutes.
NCSC Warns of Flawed SOC Metrics
The National Cyber Security Centre is warning that common security operations center metrics are fundamentally flawed, and that the only metric that truly matters is whether attacks are detected and responded to in a timely manner. By focusing on easily quantifiable but misleading metrics, organizations may inadvertently be encouraging their teams to prioritize speed over substance.
Microsoft Confirms Active Exploitation of Windows Shell Flaw
Microsoft warns of a high-severity Windows Shell flaw that's being actively exploited by attackers, allowing them to spoof victims over a network by simply sending a malicious file to be executed. The vulnerability, patched in April's Patch Tuesday update, poses a significant threat to users if left unprotected.
Microsoft Fixes Entra ID Flaw That Enabled Service Principal Takeovers
Microsoft has patched a vulnerability in Entra ID that allowed hackers to hijack service principals, potentially leading to full takeover of sensitive systems. A security researcher discovered the flaw, which stemmed from overly broad permissions in the Agent ID Administrator role.
Iran Proposes Deal to Open Strait of Hormuz, End War
Iran has made a bold move, proposing a deal to reopen the Strait of Hormuz and bring an end to the war, but with the US holding all the cards, the odds are against it. The surprising offer, delivered via Pakistan, prioritizes lifting the naval blockade and reopening the strait, with nuclear talks to follow later.

Supreme Court Probes Geofence Surveillance Limits
The Supreme Court is scrutinizing the limits of geofence surveillance, with Justice Samuel Alito bluntly questioning whether the issue belongs in a courtroom or a law review. The case, Chatrie v. The United States, challenges the constitutionality of sweeping geofence warrants used to obtain location data from tech giants like Google.

Risk Informed: New Framework Integrates Assessment into Cognitive Ops Design
In cognitive operations, risk multiplies rapidly, making every design decision a high-stakes game - which is why integrating risk assessment into Cognitive Ops Design is a crucial step that can't be ignored. By acknowledging the unpredictable ripple effects of cognitive ops, you can proactively bake risk assessment into your strategy.
Russia Unveils S-71K Air-Launched Missile Details Amid Wartime Development Push
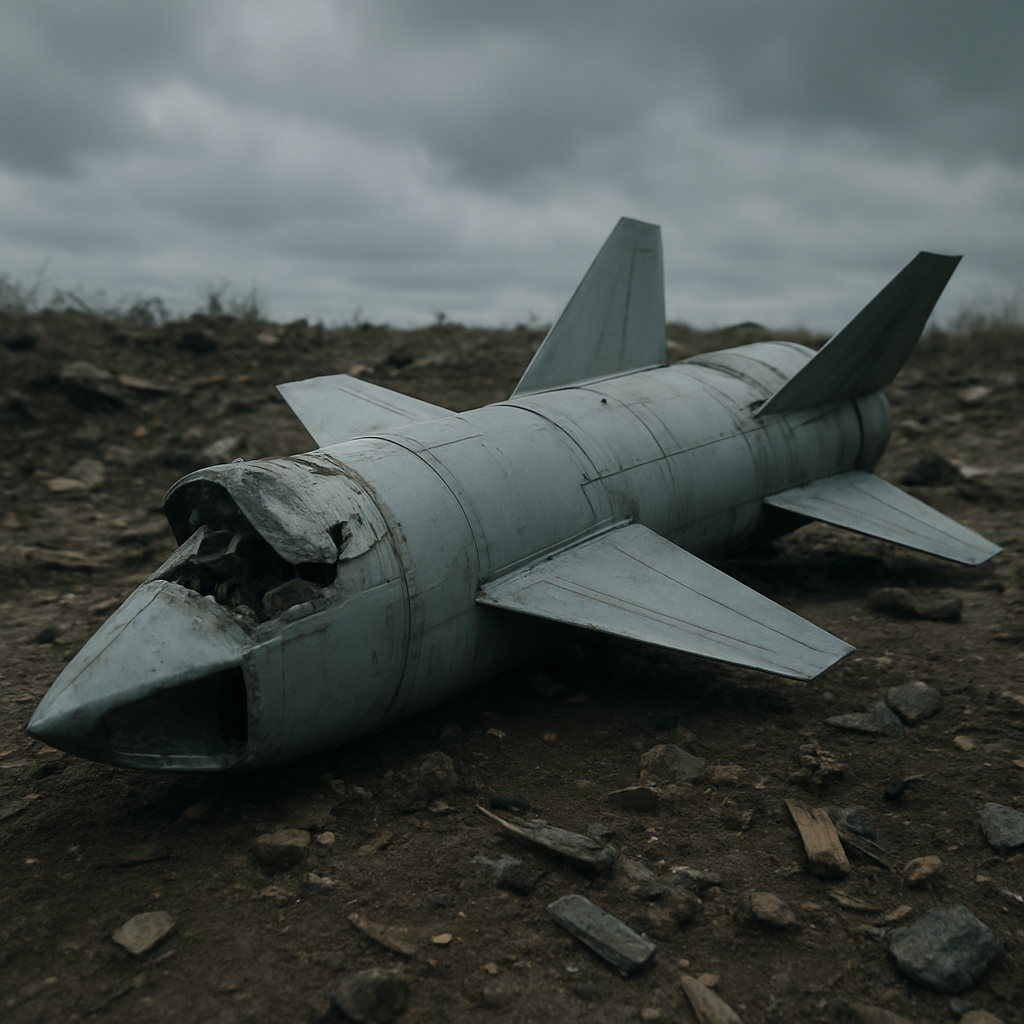
Russia's latest military advancement, the S-71K air-launched missile, has been unveiled amid a wartime development push, with Ukraine's intelligence agency releasing a detailed breakdown of the missile's design and components. The S-71K Kovyor, or Carpet, boasts a cutting-edge, low-observable shape, indicating a significant leap in missile manufacturing technology.
US Charges Chinese National in Silk Typhoon Cyber Attacks
A Chinese national, Xu Zewei, has been extradited to the US from Italy to face charges for his alleged role in the notorious HAFNIUM cyber attacks, a vast intrusion campaign that compromised over 12,700 US organizations. Xu's arrival in US court marks a significant step in holding him accountable for his actions.
Britain's Naval Defence Woes Raise Concerns for Australia's AUKUS Reliance
US Defense Secretary Pete Hegseth recently hit the nail on the head, questioning the strength of the Royal Navy, and it's hard not to wonder if Australia's AUKUS reliance is built on shaky ground. The Royal Navy's current state, with only one deployable submarine, raises serious concerns about its readiness to meet defence expectations.

MP7 Surfaces in High-Profile Security Detail at White House Correspondents' Dinner
Stunning photos from the Washington Hilton reveal a highly trained agent swiftly drawing a Heckler & Koch MP7 from a sleek Crye Precision pack during the chaotic response to the April 25, 2026 shooting near the White House Correspondents' Dinner. The dramatic scene showcases the agent's lightning-fast reflexes and top-notch security measures in action.

Space Force Overhauls Acquisition Strategy with Focus on Rapid Capability Delivery
The Space Force is shaking up its approach to acquiring new capabilities, prioritizing speed over perfection with a focus on delivering 80% solutions now rather than waiting for a flawless, but delayed, 100% solution. By embracing a faster, iterative approach, the Space Force aims to put critical capabilities in the hands of warfighters ASAP.

Healthcare Breaches Decline, But Lax Email Security Persists
Alarmingly, nearly three-quarters of breached healthcare organizations had weak email defenses, with 74% either lacking a DMARC policy or having it set to monitor-only mode, leaving them vulnerable to attacks.

Supply-Chain Attack Targets Security, Dev Tools with Credential Theft
Malicious hackers are exploiting the very tools developers rely on, including security scanners and password managers, to steal sensitive credentials and gain unauthorized access. This latest supply-chain attack has already hit major players like Checkmarx, compromising their GitHub repository and potentially putting customer data at risk.
Robinhood Flaw Exploited to Send Convincing Phishing Emails
Scammers have found a way to send fake emails that look like they're really from Robinhood, complete with convincing details like unusual IP addresses and partial phone numbers. These phishing emails even appeared to come from Robinhood's official email address, making them super convincing.

Ex-DOD Leaders Challenge Pentagon's Anthropic Designation as Illegal
Former national security officials are challenging the Pentagon's designation of Anthropic as a supply-chain risk, calling it a politically motivated move that's legally flawed and actually undermines national security. They argue that the designation was a misuse of authorities meant to address genuine threats, rather than a legitimate national security concern.
GlassWorm Malware Resurfaces Through 73 OpenVSX Extensions
Researchers at Socket have uncovered a sneaky new wave of GlassWorm malware, this time hiding in 73 OpenVSX extensions that behave like sleepers - seemingly harmless at first, but turning malicious after a stealthy update. Six of these extensions have already been activated, unleashing malware on unsuspecting developers.

Medtronic Discloses Cyber Breach by ShinyHunters Gang
Medtronic recently reported a cyber breach by the ShinyHunters gang to federal authorities and the SEC, revealing that hackers had infiltrated its corporate IT system. Fortunately, the company has found no evidence that patient safety or electronic connections to customers were compromised.
North Korean Hackers Exploit Fake Zoom Meetings to Target Crypto Executives
North Korean hackers are using a sneaky tactic to target crypto executives: they pose as legitimate meeting attendees, harvesting video and audio to make future scams more convincing. They start by sending Calendly invites for fake catch-up meetings, then swap the link with a fake Zoom or Teams URL to gain their victim's trust.
US Charges Chinese Hacker in Cyberespionage Case
The US Department of Justice has extradited Chinese national Xu Zewei from Italy to face charges of conducting cyberespionage operations on behalf of China's intelligence services, targeting victims including COVID-19 researchers. Xu's alleged hacking activities, directed by China's Ministry of State Security, spanned over a year, from February 2020 to June 2021.
Canada Cracks Down on Rogue Cellular Tower Used for Mass Phishing Texts
Imagine receiving a text from your bank or favorite store, but it's actually a sneaky scam - that's what happened in Toronto when a rogue cellular tower started sending out mass phishing texts to unsuspecting users. Canadian authorities cracked down on the culprit in a sting operation dubbed Project Lighthouse.
Medtronic, Itron Disclose Breaches by Digital Intruders
Itron sprang into action after detecting an unauthorized break-in on April 13, swiftly notifying law enforcement, and working with cybersecurity experts to investigate and remediate the breach. The company has since confirmed that it has prevented any further unauthorized activity within its corporate systems.