Tag: emerging threats
8478 articles
Army Accelerates Electronic Warfare Development with Budget Boost
The Army is turbocharging its electronic warfare development with a budget boost, aiming to outpace rapid technological advancements and secure spectrum dominance. With a topline funding increase and strategic line-item consolidation, the service plans to swiftly deploy cutting-edge capabilities to the field.

Ukraine Unveils Conditional Drone Export Policy
Ukraine is opening up new opportunities for its drone industry, allowing companies to export domestically produced weapons to select partner countries, but only after meeting the state's own military needs. This strategic move aims to boost Ukraine's economy while prioritizing its own defense requirements.
AI Agents Expose Identity Security Gaps
Imagine an AI agent that can uncover thousands of hidden security vulnerabilities, some of which have gone undetected for nearly 30 years - and the potential risks that come with it falling into the wrong hands. A single powerful AI agent can scan for weaknesses faster and more persistently than hundreds of human hackers, highlighting a pressing need for secure deployment.
French Teen Suspected in Mega-Breach at Secure Document Agency
A massive cyber security breach at France's secure document agency, ANTS, has led to the theft of 12-18 million lines of sensitive data, which was then offered for sale online. A 15-year-old French teen has been detained in connection with the leak, prompting the Paris Public Prosecutor's Office to launch a judicial investigation.

Pakistan's Gulf Strategy Exposes Enduring Ambiguity
Six months after the historic Saudi-Pakistan Strategic Mutual Defence Agreement was signed, its true test has come in the form of Operation Epic Fury, which has dramatically reshaped the Gulf security landscape. The pact, aimed at tackling threats from Iranian drones and missiles, is being put to the ultimate test - can it live up to its promise?
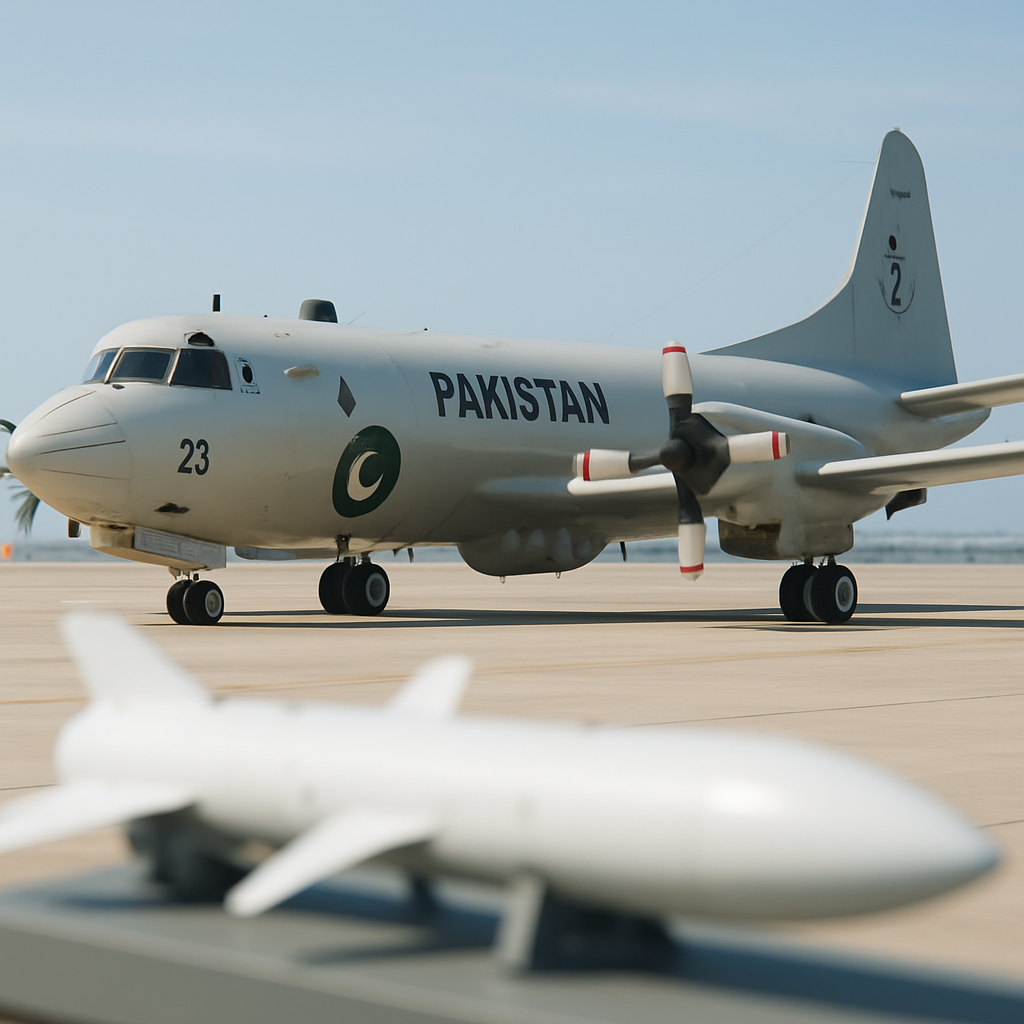
Pakistan Navy Bolsters Sea-Denial Strategy with Advanced Missile Tests
The Pakistan Navy has taken a significant leap in its sea-denial strategy with the successful test of the Taimoor air-launched cruise missile, a game-changing precision-strike weapon with a range of 600 km that can engage both land and sea targets. This latest milestone bolsters the Navy's ability to launch extended-range attacks on enemy naval forces.

Silver Fox APT Targets Russia, India with ABCDoor Backdoor
Over 1,600 malicious emails, disguised as tax-audit notices, were sent to targets in India and Russia between January and February 2026, aiming to trick recipients into downloading a backdoor or clicking on a malicious link. The cleverly crafted phishing campaign unfolded in two waves, using PDFs and archives to spread the ABCDoor backdoor.

Brazilian DDoS Firm Exposes Own Security Breach
A Brazilian firm's bold admission about notifying major internet providers of massive DDoS attacks against small ISPs took an unexpected turn when evidence revealed a shocking security breach of its own. The company's CEO, Erick Nascimento, revealed that an intrusion in January 2026 compromised key servers and his personal security codes.
PyTorch Lightning Targeted in PyPI Supply Chain Credential Heist
Malicious actors have struck PyTorch Lightning with a supply chain attack, publishing two tainted package versions that automatically steal credentials when imported. The attack involves a sneaky _runtime directory with a downloader and obfuscated JavaScript payload.
New Extortion Crews Mimic Scattered Spider Tactics in Rapid Attacks
New extortion crews, Cordial Spider and Snarky Spider, are rapidly carrying out data-theft-for-extortion campaigns, closely mimicking the tactics of notorious group Scattered Spider. These financially motivated groups, tied to The Com, have been targeting US-based organizations since October 2025.
Google's Gemini CLI Fix Sparks CI/CD Pipeline Disruptions
A recent patch for Google's Gemini CLI has sparked disruptions in CI/CD pipelines, ironically caused by a critical infrastructural flaw - not an AI quirk - that allowed remote code execution due to over-permissive workspace trust in headless mode. The fix, while swift, may trip automated pipelines that relied on the old settings.

Researchers Uncover Fast16 Malware's Stealthy Industrial Sabotage Role
Researchers have uncovered a highly sophisticated malware, Fast16, designed to secretly sabotage industrial operations by subtly manipulating critical calculations, leading to potentially catastrophic failures. This stealthy threat can silently spread across networks, altering results in high-precision applications and causing damage to real-world equipment.
Iran's IRGC Crisis Exposes Pakistan's Mediation Limits
Pakistan's bid to mediate between the US and Iran ended in a stalemate, revealing a surprising gap in Tehran's decision-making authority and leaving Islamabad's diplomatic ambitions unfulfilled. The talks exposed that Iran's powerful IRGC leaders, not the negotiators, held the reins of power.

China Unveils Low-Cost Anti-Tank Missile Variant
Meet the AFT-11E, a game-changing, budget-friendly anti-tank missile that packs a punch, weighing just 14-15 kg and boasting an impressive range of 100 to 5,000 meters. This lightweight, precision-guided missile is designed to outsmart electronic countermeasures, making it a top choice for modern warfare.
US Air Force Unveils B-1B Bomber Carrying ARRW Hypersonic Missile
The US Air Force has revealed a game-changing moment with a B-1B bomber proudly carrying an ARRW hypersonic missile on an external hardpoint, marking a significant milestone in military tech advancements. Check out the impressive footage on Edwards Air Force Base's Instagram page!
FBI Warns of Surging Cyber-Enabled Cargo Theft Attacks
The FBI is sounding the alarm on a surge in cyber-enabled cargo theft, where sophisticated hackers impersonate legitimate businesses to hijack high-value shipments and reroute deliveries. With nearly $725 million in losses in 2025 alone, this growing threat is costing businesses big time.

Ukraine Arrests Hackers Behind 610,000 Roblox Account Breach
Ukrainian authorities have cracked down on a group of hackers responsible for breaching over 610,000 Roblox accounts in a months-long phishing scam that harvested credentials and tokens. The stolen access was used to snag in-game items and Robux, Roblox's virtual currency.
AI-Driven Cybercrime Fuels 389% Surge in Ransomware Victims
Get ready for a wake-up call: ransomware victims have skyrocketed by 389% in just one year, thanks to cybercriminals harnessing the power of AI to launch more sophisticated attacks. This alarming trend is driven by the growing availability of malicious AI tools, making it easier for hackers to wreak havoc.
Linux Flaw Exposes Root-Level Access Across Major Distros
A newly discovered Linux flaw, nicknamed "Copy Fail," allows unprivileged users to gain root-level access to major distributions, putting countless systems at risk. This vulnerability, which involves a temporary write of just four bytes during a crypto operation, can be exploited by attackers to take full control of an operating system.
Microsoft Update Disrupts Backup Software on Windows 11
Beware: the latest Windows 11 update, KB5083769, is causing backup software to fail on systems running versions 24H2 and 25H2 by triggering Volume Shadow Copy Service (VSS) timeouts. This disruption can lead to frustrating backup failures, affecting users of popular software like Acronis.
Python Backdoor Evades Detection on Windows with Advanced Evasion Techniques
Meet Deep#Door, a sneaky Python-based backdoor framework that hides its malicious payload inside a batch dropper, making it super hard to detect on Windows systems. By embedding its code, it dodges network-based detection and slips into restricted environments with ease.

Attackers Target New Assets Within Minutes of Exposure
The moment a new asset goes live with a public IP address, the clock starts ticking - and within minutes, attackers are circling, waiting to pounce on unsuspecting targets. In just 24 hours, a newly exposed asset can go from discovery to compromise, with threat actors exploiting vulnerabilities at an alarming rate.
Cyberattacks Expose 1.8M RDP Servers Online
A shocking 1.8 million RDP servers are currently vulnerable to cyberattacks, leaving them open to exploitation by opportunistic hackers. Canadian authorities have also cracked down on SMS blaster phishing, arresting three men and seizing a device that sent fake texts to unsuspecting phones.

US Agencies Issue Zero Trust Guidance for OT Security
US government agencies have just released a game-changing guide to help protect critical infrastructure systems with practical, layered security strategies. The new zero-trust guidance provides a tailored approach for operational technology environments, balancing safety and uptime needs with robust security measures.