Tag: emerging threats
8407 articles
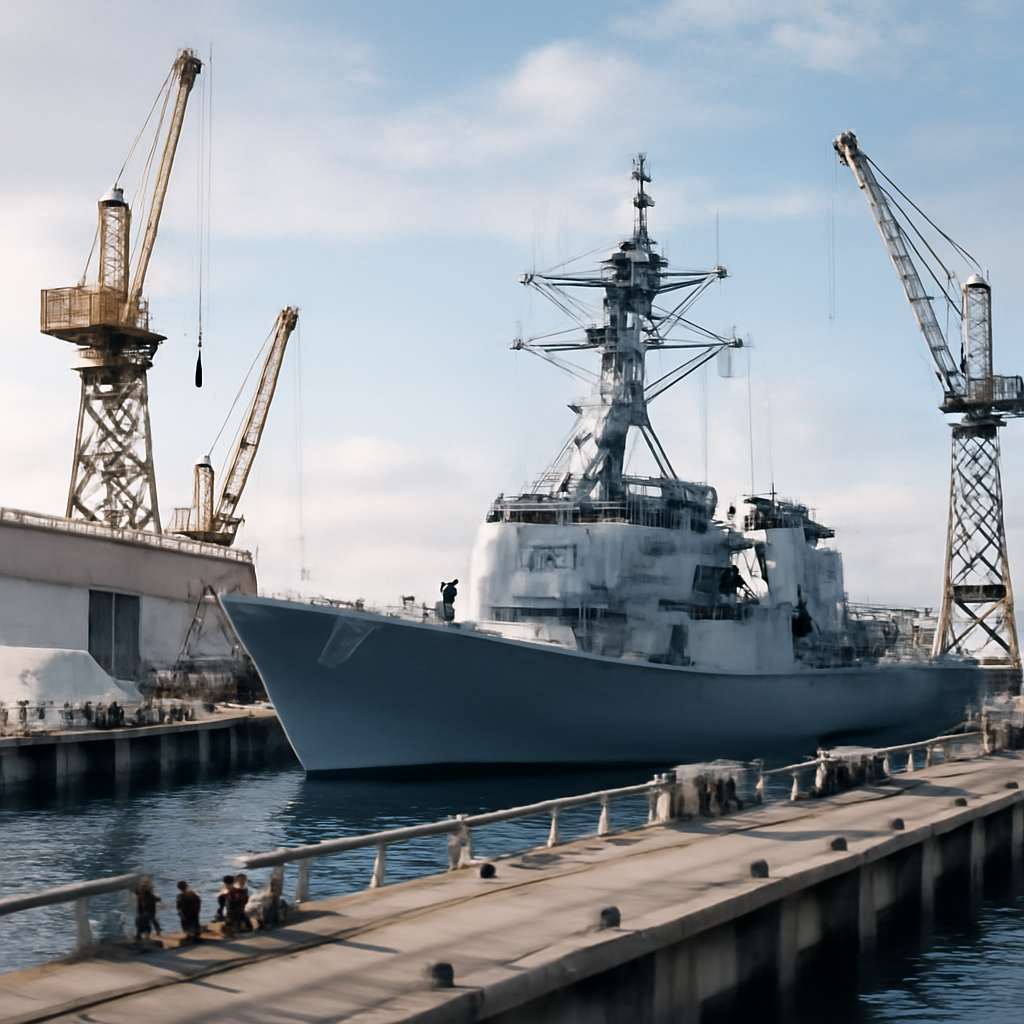
Japan Weighs Taiwan Security Ties Amid Defense Export Reforms
Taiwan's navy is in urgent need of an upgrade, with 15 of its 25 major surface combatants over 25 years old, and some vessels even pushing 50 years of service. The Taiwanese navy is now eyeing Japan's cutting-edge Mogami-class frigate as a potential game-changer for its next-generation surface combatant plans.

CISA Faces Scrutiny Over Leaked Credentials
The US Cybersecurity and Infrastructure Security Agency (CISA) is under fire after dozens of its internal credentials were accidentally exposed on a public GitHub account, sparking concerns over potential security breaches. Despite the agency's assurance that no sensitive data was compromised, lawmakers and experts are demanding answers on how this incident occurred.

Pakistan Pursues Sea-Based Nuclear Deterrent Despite China Rejection
Pakistan aims to bolster its defenses with a sea-based nuclear deterrent, fueled by the successful 2017 test of the Babur-3 submarine-launched cruise missile, which Islamabad claims can deliver a nuclear payload with a range of 450 km from an underwater mobile platform. This move sparks debate about the feasibility of a credible second-strike capability without external assistance.
Pentagon Unleashes $54 Billion Bet on Autonomous Warfare
The Pentagon is making a staggering $54.6 billion bet that autonomous swarms will revolutionize future conflict - a bold move that's being hailed as the largest single commitment to autonomous warfare in history. This massive investment marks a significant shift in the military's strategy, but past initiatives like the Replicator program have faced major hurdles, including technical issues and procurement woes.
FBI Warns of Kali365 Phishing Kit Targeting Microsoft 365 Users
The FBI is sounding the alarm on Kali365, a phishing kit that makes it easy for attackers to target Microsoft 365 users with AI-generated scams, automated templates, and real-time tracking. This powerful tool is lowering the bar for cybercriminals, allowing less tech-savvy attackers to launch sophisticated phishing campaigns.

CISA Breach Exposes Sensitive Government Systems
A shocking security lapse at CISA exposed highly sensitive government systems, thanks to a contractor's careless mistake of leaving credentials to privileged AWS GovCloud accounts and internal systems publicly available on GitHub. The error granted unfettered access to a vast array of agency infrastructure, putting national security at risk.

Russian Hacker Exploits Jailbroken AI in Crypto Fraud Scheme
A solo Russian hacker, known as bandcampro, has orchestrated a massive crypto fraud scheme, reaching 17,000 subscribers on Telegram with AI-generated content that convincingly mimicked popular conspiracy styles. This alarming development marks a turning point in cybercrime conspiracies, with AI-powered threats on the rise.

GitHub Repos Targeted in 5,500+ Malicious Commits
A shocking new campaign, dubbed Megalodon, has injected malware into over 5,500 GitHub repositories, putting sensitive credentials and tokens at risk of being stolen. This alarming attack highlights the growing threat of supply chain attacks, with experts warning that this could be just the beginning.
Authorities Disrupt First VPN Service Used by 25 Ransomware Groups
In a major win for cybersecurity, an international coalition led by France and the Netherlands has disrupted a notorious VPN service used by 25 ransomware groups, taking a significant blow to cybercrime operations. The takedown was made possible through a collaborative effort involving 16 countries and key partners like Europol and Eurojust.

Netherlands Disrupts Russian Cyber Operations with Server Seizure
Dutch authorities have struck a major blow against Russian cyber operations, seizing 800 servers and making several arrests in a crackdown on a web hosting ecosystem accused of enabling cyberattacks, disinformation campaigns, and other malicious activities. This coordinated law-enforcement action aims to disrupt the cyber threat landscape and protect democracy and security.
Ghostwriter Exploits Ukraine Government with Prometheus Phishing Malware
Malicious actors known as Ghostwriter have launched a cunning phishing campaign targeting Ukraine's government, using emails that appear to come from trusted sources and contain links to a seemingly harmless learning platform, Prometheus. These emails contain a hidden threat that can download malware onto victims' devices.
CISA Opens KEV Nominations to Bolster Vulnerability Intelligence
CISA is now accepting nominations for its Known Exploited Vulnerabilities catalog, empowering public reporting to strengthen the nation's cybersecurity posture by quickly identifying and mitigating exploited vulnerabilities. By submitting through the new KEV nomination form, you're helping to keep federal, private, and critical infrastructure networks safe.
Ex-US Execs Plead Guilty to Aiding Global Tech Support Scams
Two former executives, Adam Young and Harrison Gevirtz, have pleaded guilty to hiding a massive tech support scam that duped victims worldwide, and now face up to three years in prison and $250,000 in fines. Their guilty pleas mark a major win in the fight against tech support scams.

US Military Enhances LUCAS Drone with AI-Powered Swarming Capability
The US military is supercharging its LUCAS drone system with a game-changing AI-powered swarming capability, thanks to a new partnership with Shield AI - and Adm. Brad Cooper couldn't be more impressed, calling LUCAS "indispensable". This cutting-edge upgrade is set to revolutionize the drone's potential, unleashing a coordinated army of affordable, long-range attack drones that can overwhelm targets at a fraction of the cost of traditional missiles.
Middle East Tensions Force Cancellation of UK's Royal International Air Tattoo
The Royal International Air Tattoo, a highly anticipated event, has been cancelled due to uncertainty over access to RAF Fairford amid rising tensions in the Middle East. Ticket holders can opt for a full refund or roll over their tickets to the 2027 edition.

Nation-State Actors Exploit ROADtools in Cloud Attacks
Cloud attackers are now leveraging ROADtools, a publicly available toolkit, to exploit vulnerabilities in cloud tenants, allowing them to persist, discover, and evade defenses with ease. This dual-use framework's ability to speak Entra ID and Microsoft Graph makes it a red flag for defenders to take notice.
Norway Warns of Russian Nuclear Threat to US Cities
Norway's Foreign Minister Espen Barth Eide issued a stark warning: Russia's nuclear arsenal poses a catastrophic threat to US cities, capable of unleashing unprecedented destruction. A united NATO is crucial to counter this menace.
Iran-nexus APT Expands Espionage Ops with New RAT Variants
Unit 42 researchers have uncovered a sophisticated espionage campaign by an Iran-linked threat group, dubbed Screening Serpens, which has deployed six new remote access Trojan (RAT) variants to target entities across the US, Israel, and the Middle East. These variants, part of two distinct malware families, signal a significant expansion of the group's cyber spying operations.

Cloud Atlas Expands Arsenal with New Tools, Payloads
Cloud Atlas is beefing up its toolkit with fresh tools and payloads, including a blast from the past - the notorious CVE-2018-0802 Microsoft Office Equation Editor vulnerability. The group is also reviving its use of ZIP archives with malicious LNK shortcuts that trigger PowerShell scripts, keeping security experts on high alert.

Trend Micro Discloses Apex One Zero-Day Exploited in Attacks
A critical zero-day vulnerability, CVE-2026-34926, has been discovered in Trend Micro's Apex One on-premises server, allowing pre-authenticated local attackers to inject malicious code - and it's being actively exploited in attacks. Federal agencies have been ordered to patch affected systems ASAP, with a deadline of June 4, 2026.
Exploiting Windows Drivers Without Hardware: The BYOVD Perspective
Discover how attackers can exploit Windows drivers without hardware, turning kernel-mode driver bugs into powerful tools to bypass security controls. The Atos Threat Research Center reveals a game-changing method to manipulate reachability from userland on Windows 11 23H2.

Fraud Losses Exceed Chargebacks, Threaten Growth
Relying solely on chargeback rates to measure fraud performance can be misleading, as it overlooks significant costs and risks that affect revenue, operations, and customer trust long before a dispute escalates into a chargeback. By focusing on this single metric, teams may be ignoring a much larger problem that's hiding in plain sight.
GitHub Megalodon Attack Targets Repos with Malicious CI/CD Workflows
In a shocking six-hour blitz on May 18, 2026, attackers unleashed a massive supply-chain campaign dubbed "Megalodon," pushing 5,718 malicious commits to 5,561 GitHub repositories. The sneaky assault mimicked routine CI maintenance, using fake author names and convincing commit messages to deceive victims.
Drupal Sites Targeted in SQL Injection Attacks
Drupal sites are under attack as SQL injection exploits are now being detected in the wild, taking advantage of a vulnerability that can be triggered without authentication. This critical flaw, CVE-2026-9082, allows attackers to execute arbitrary SQL and potentially run remote code, putting sites that use PostgreSQL at risk.