Tag: emerging threats
8360 articles
Tech Industry Presses Administration to Unfetter Anthropic AI Model
Over 30 industry and academic leaders are urging the administration to lift restrictions on Anthropic's Fable 5 model, citing its potential to bolster defenses against cyber threats and the robust safeguards already built in to prevent misuse. By freeing up access to this powerful tool, they argue that it could become a game-changer for those fighting to protect against cyber attacks.
Pentagon Science Chief Sees Biotech, AI Transforming Warfare
The Pentagon's science chief says the Ukraine conflict showcases the game-changing power of rapid innovation, with homegrown technologies like drones emerging almost overnight to shift the battlefield balance. This new era of swift, emergent capability is transforming warfare, and it's here to stay.
Police Misuse Flock Cameras for Illegal Stalking
Police officers across the US have been caught misusing Flock surveillance cameras to obsessively and illegally stalk over a dozen individuals nationwide. This shocking abuse of power raises serious concerns about the protection of citizens' privacy and safety.
China Unveils Affordable Yunlong-1P Attack Drone
Meet the Yunlong-1P, China's latest affordable attack drone that's taking high-altitude capabilities to new heights - literally, reaching 8,500 meters in recent trials!
Fortinet Sandbox Flaws Under Active Exploitation
Critical Fortinet Sandbox vulnerabilities are under active attack, with hackers exploiting flaws like CVE-2026-39813, a severe path traversal bug that allows authentication bypass. Fortinet patched these bugs in April, but users must upgrade ASAP to avoid being compromised.
Pakistan's Satellite Launches Expose Kashmir Theatre Ambitions
Pakistan just made a bold move in the Kashmir theatre with the launch of its PRSC-EO3 satellite, which boasts an unusual 38-degree orbital tilt - a strategic departure from its previous launches. This daring maneuver hints at the country's growing ambitions in the region.
Google Cloud Vertex AI Vulnerability Exposes Cross-Tenant RCE Risk
A recent vulnerability in Google Cloud's Vertex AI Python SDK left the door open for cross-tenant attacks, allowing hackers in separate projects to hijack model uploads and potentially execute malicious code remotely. This flaw was fortunately patched in version 1.148.0, released on April 15, 2026.
Breach Notice Error Fuels Patient Skepticism
A simple mistake on breach notices sent by third-party vendor Xsolis sparked skepticism among patients when the letters misnamed Rochester Regional Health as "Rochester Regional Medical Center", leading many to dismiss them as scams. This misstep undermined trust and raised questions about the effectiveness of the breach notification process.
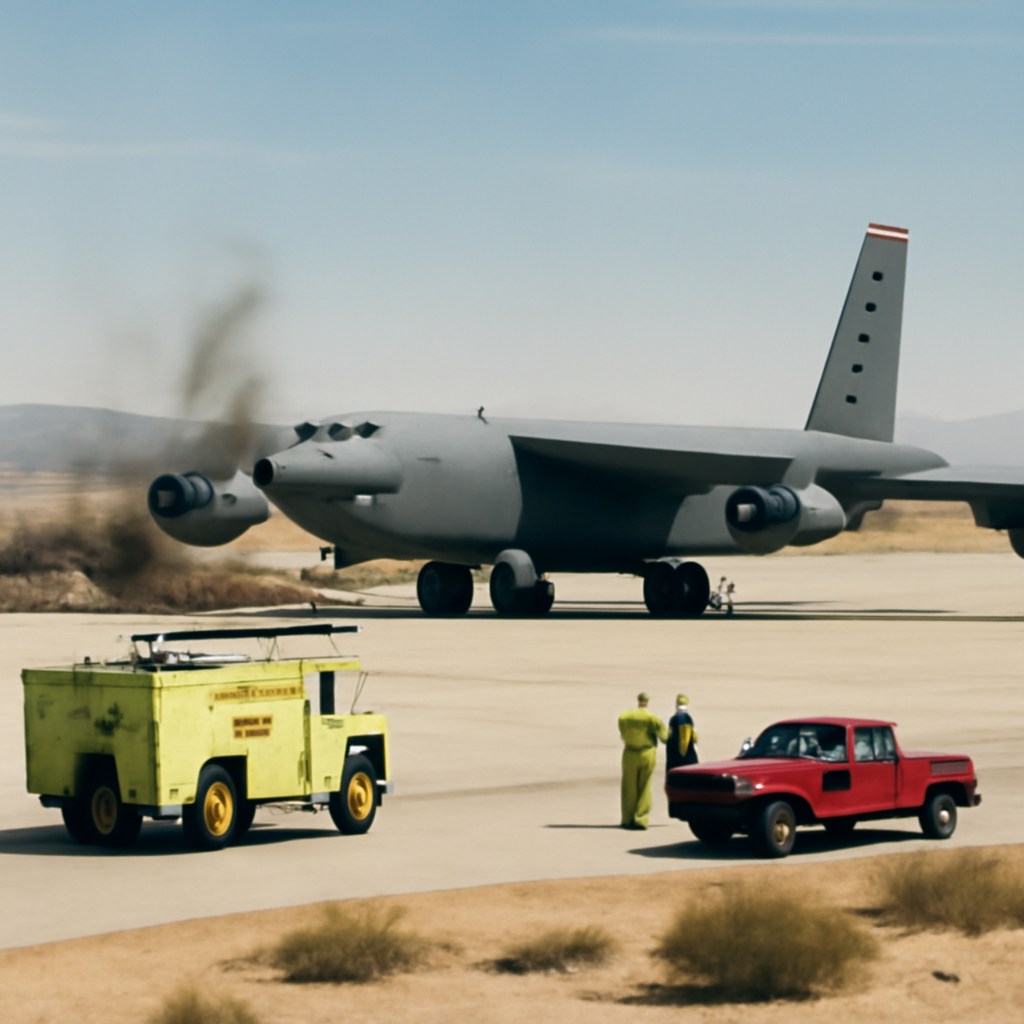
B-52 Crash Disrupts Radar Modernization Efforts
A devastating crash of a B-52 aircraft during takeoff at Edwards Air Force Base in California has dealt a significant blow to the Radar Modernization Program, with the incident deemed unsurvivable. The mishap has prompted an immediate suspension of flight operations at the base.
Experts Push for Standardized AI Model Inventories to Mitigate Cyber Risk
Experts warn that without standardized AI model inventories, we risk a chaotic "fire, ready, aim" approach, where multiple incompatible solutions create more cyber threats than they mitigate. A new policy paper proposes an AI bill of materials (AIBOM) as a crucial step towards reducing cyber risk and improving transparency.
NATO Overhauls Modernization Approach Amid Rising Threats
NATO's modernization approach has undergone a significant transformation in recent years, driven by the need for faster learning, greater experimentation, and interoperable systems in the face of rising threats. This shift, sparked by Russia's invasion of Ukraine, is revolutionizing how the alliance approaches force design and innovation.
Trump Bolsters Military, Intelligence Cybersecurity with New National Security Memo
President Trump just took a major step to fortify America's defenses in the digital age, signing a National Security Presidential Memorandum to boost cybersecurity and modernize governance for our nation's most sensitive computer systems. This move aims to improve accountability and coordination among agencies, protecting the systems that support military and intelligence operations.
Cal Water Probes Alleged Hacking by Iran-Linked Group
Cal Water is taking swift and decisive action to investigate allegations of a cybersecurity incident, swiftly activating its response plan and working around the clock to get to the bottom of the claim. The utility confirms that its probe, launched after learning of the alleged hacking by an Iran-linked group on June 11, 2026, is ongoing with no known operational disruptions reported so far.
Ransomware Gang Exploits Microsoft Teams for C2 Traffic
Meet the sneaky ransomware gang that hijacked Microsoft Teams to secretly control its victims' systems for two whole months, using sophisticated cyber tradecraft to stay under the radar. They pulled off this impressive heist with a custom backdoor and some clever C2 traffic disguises.
UK Plans Facial Scans, ID Checks for Social Media Users
The UK government plans to revolutionize online safety by introducing facial scans and ID checks for social media users, starting with a ban on social media for under-16s. This move aims to give kids their childhood back and protect them from the potential harms of online platforms.
Rokarolla Malware Targets Android Banking Apps with 137 Commands
Meet Rokarolla, a sneaky Android banking trojan that's taking aim at 217 banking and cryptocurrency apps with an arsenal of 137 remote commands, giving attackers alarming control over infected phones. This malicious malware is designed to outsmart even Google's Play Protect defenses, putting your financial security at risk.
China-Linked Backdoor Expands to Windows with Kernel Stealth
A China-linked espionage group has unleashed a stealthy backdoor that infiltrates Windows systems, targeting government bodies in Honduras, Taiwan, Thailand, and Pakistan. The malware, known as SprySOCKS, boasts advanced espionage features and kernel-level stealth, making it a formidable threat.
Windows Junctions Expose Hidden Malware Paths
Malware creators have found a sneaky way to evade detection by using NTFS junctions, a feature that's normally used to connect directories, to create hidden paths that can bypass security defenses like Microsoft Defender. By exploiting this vulnerability, attackers can cleverly disguise their malware's true location, making it harder to detect.
FTC Warns of $3.5 Billion Losses to Imposter Scams
The Federal Trade Commission is sounding the alarm on imposter scams, which have led to a staggering $3.5 billion in losses - nearly triple the amount reported in 2020. This pervasive form of fraud has become the most reported category, accounting for almost a third of all fraud reports filed with the FTC.
Rokarolla Trojan Enables Unseen Banking Fraud via Device Takeover
Meet Rokarolla, a sneaky Android banking trojan that's taking device takeover to a whole new level, allowing scammers to isolate and exploit victims like never before. This malicious malware doesn't just steal credentials - it gives attackers total control over your phone.
Cardiac Monitor Maker's Data Breach Exposes Security Gaps
A recent report has exposed a shocking security gap in a leading cardiac monitor manufacturer's system, leaving sensitive clinical monitoring data vulnerable to data thieves. This alarming breach highlights the urgent need for enhanced medical-device security and protection of patient information.
Cybersecurity Pros Face Mounting Challenges
Cybersecurity professionals are facing a harsh reality: 68% say their job has become significantly harder in just two years, with many also being shut out of key technology decisions that impact their work. This alarming trend is backed by eight years of data, highlighting a growing crisis in the industry.
Anonymized Infrastructure Exposes Reactive Security Gaps
Despite having access to a flood of IP data, security teams are struggling to turn it into actionable insights, with a staggering 94% of security incidents involving anonymized infrastructure that exposes reactive security gaps. The sheer volume of data is creating a clarity crisis, with analysts overwhelmed by signals but lacking the context needed to respond effectively.
Chainguard Launches Athena to Fortify Open Source Against AI Threats
Meet Athena, a groundbreaking coalition and platform that helps safeguard open-source software from AI-driven threats by streamlining vulnerability detection, private remediation, and coordinated disclosure. By joining forces, Athena members can proactively protect the entire open-source ecosystem from emerging risks.