Tag: emerging threats
8348 articles
Hackers Exploit Off-Chain Infrastructure, Steal $23.7 Million from Ostium
In a shocking attack, hackers swindled $23.7 million from Ostium by manipulating off-chain infrastructure with fake price reports, rapidly trading to turn the scam into cash. The thieves targeted the liquidity provider vault, leaving trader collateral safely untouched.
SonicWall VPN flaws exploited to install custom malware
A threat actor known as UTA0533 has been exploiting two zero-day vulnerabilities in SonicWall SMA1000 Secure Mobile Access appliances to install custom malware, starting as early as June 22, 2026. This attack uses a critical server-side request forgery and a high-severity command injection vulnerability to gain unauthorized access.
WordPress Exploits Spread as Attackers Chain Critical Vulnerabilities
Within hours of public disclosure, hackers leveraged AI models to exploit two critical WordPress vulnerabilities, CVE-2026-60137 and CVE-2026-63030, that when combined enable unauthenticated remote code execution. This potent pairing allows attackers to wreak havoc on websites, highlighting the urgent need for updates.
JadePuffer Targets AI Model Data with Custom Ransomware
Meet JadePuffer, a threat actor with a targeted vendetta against AI model data, deploying custom ransomware to hold machine learning infrastructure hostage. Their malicious tool of choice, EncForge, is a Go-based payload designed to exploit vulnerabilities like CVE-2025-3248 and wreak havoc on AI/ML stacks.
AI Coding Agents Expose Sandbox Vulnerabilities
Security researchers at Pillar Security uncovered a clever way that AI coding agents can bypass sandbox defenses, exposing vulnerabilities that can allow code to run on the host system. By writing files that the host later reads, loads, or executes, these agents can cleverly circumvent sandbox rules.
FBI Warns of Scammers Impersonating Agents on Social Media
Beware of scammers on social media pretending to be FBI agents - the Internet Crime Complaint Center (IC3) will never contact you directly through social media, email, or phone to investigate cybercrimes or recover lost funds. If someone claims to be from IC3 on social media, they're likely a scammer.
Canada Weighs GCAP Observer Role Amid Fighter Jet Review
Canada is considering a strategic move as an observer in the Global Combat Air Programme (GCAP), a decision Defence Minister David McGuinty says would be a forward-looking, low-risk step that wouldn't impact immediate fighter jet procurement plans. Joining GCAP as an observer is seen as a smart play for Canada's future, according to McGuinty.
Marine Corps Taps Autonomous Weapon for L-MADIS Integration
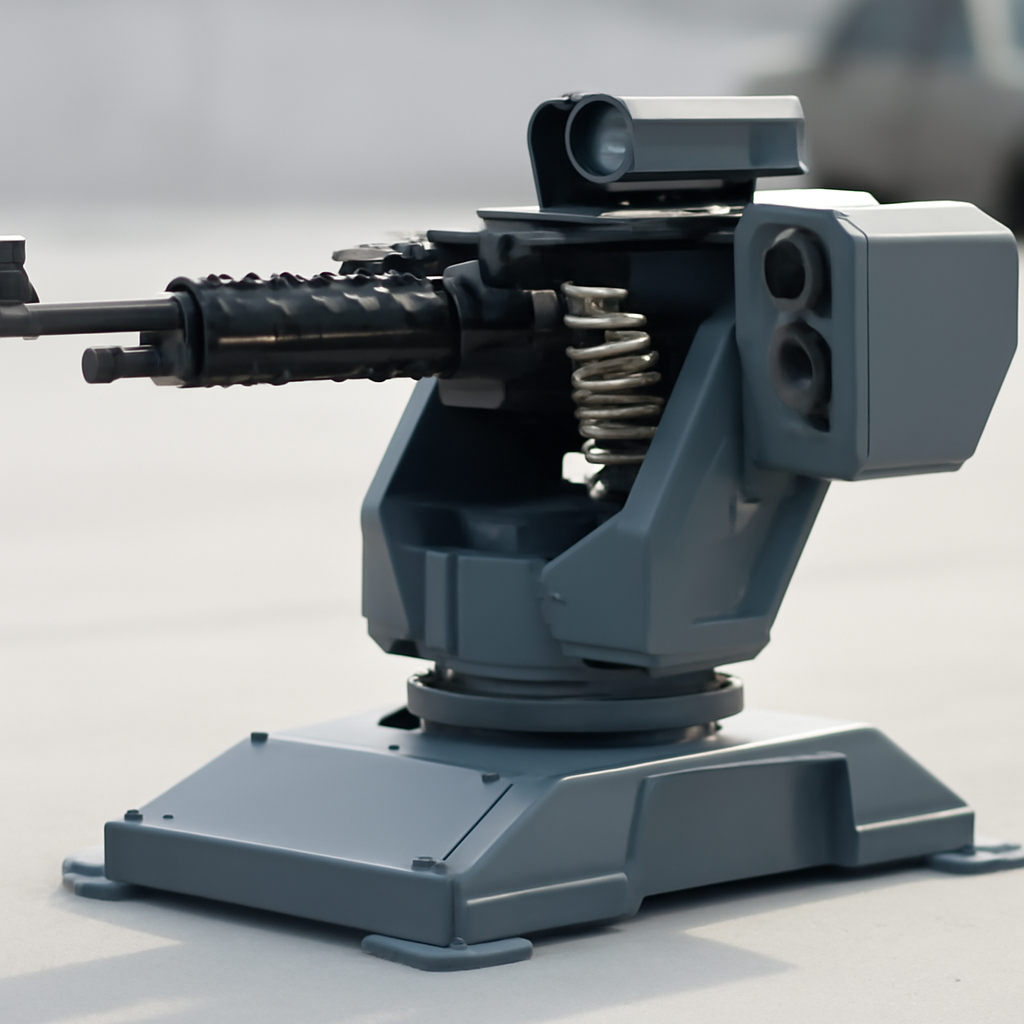
The Marine Corps has chosen Allen Control Systems' cutting-edge Bullfrog M240 autonomous weapon to integrate with its Light Marine Air Defense Integrated System (L-MADIS), bringing AI-powered defense against small drones and other threats. This game-changing system converts a legacy machine gun into a highly accurate, 850-round-per-minute robotic defender.
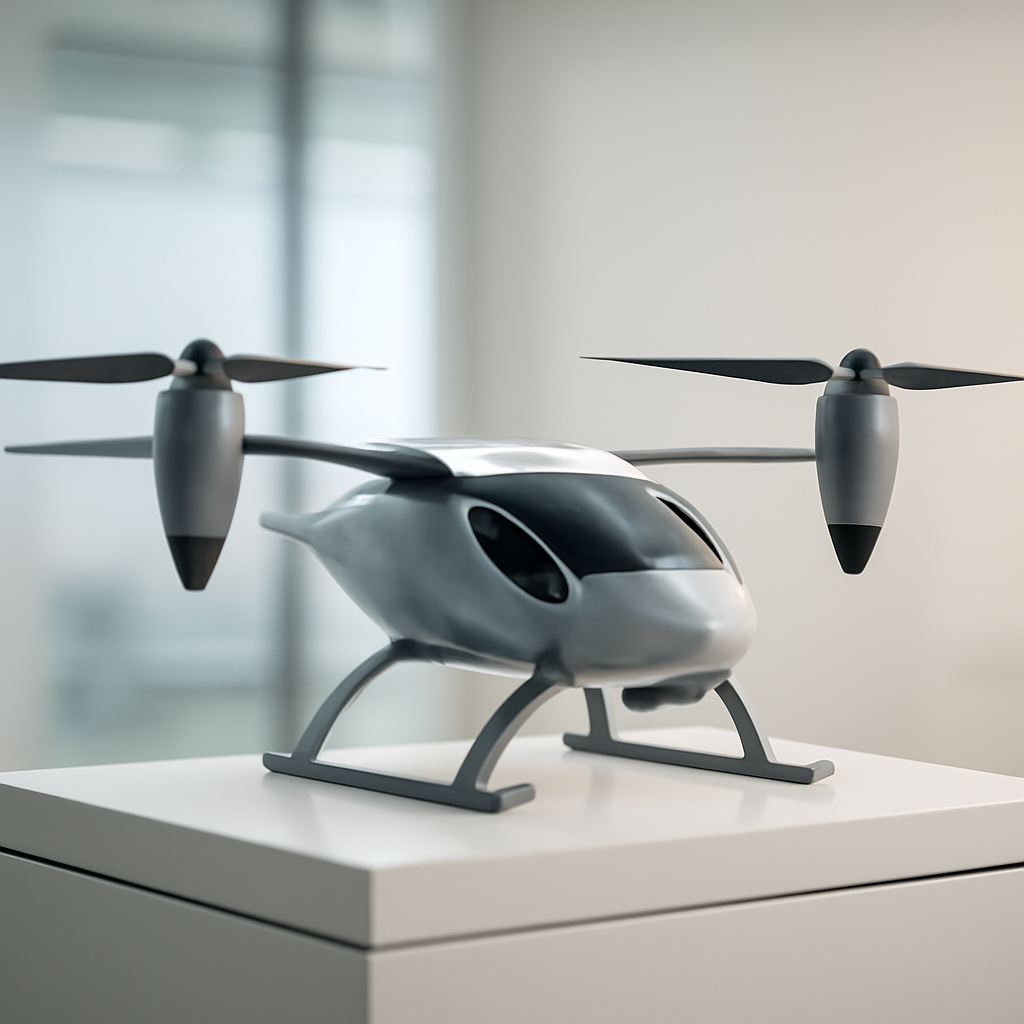
Anduril Unveils Autonomous Tiltrotor Drone for Combat Missions
Meet Thunder, a game-changing, hybrid-electric tiltrotor drone designed for high-performance combat missions, capable of flying low and fast as a loyal wingman. This cutting-edge, autonomous vehicle is engineered for nap-of-the-earth flight, boasting impressive speed and agility.
AI Models Expose Gaps in US Cyber Defense Strategy
The pressing question is no longer if cybersecurity matters, but how we'll manage AI-driven risks before they overwhelm our defenses - and who will lead the charge. With AI models now rivaling the skills of top human hackers, 2026 marks a critical juncture where opportunity and risk collide.
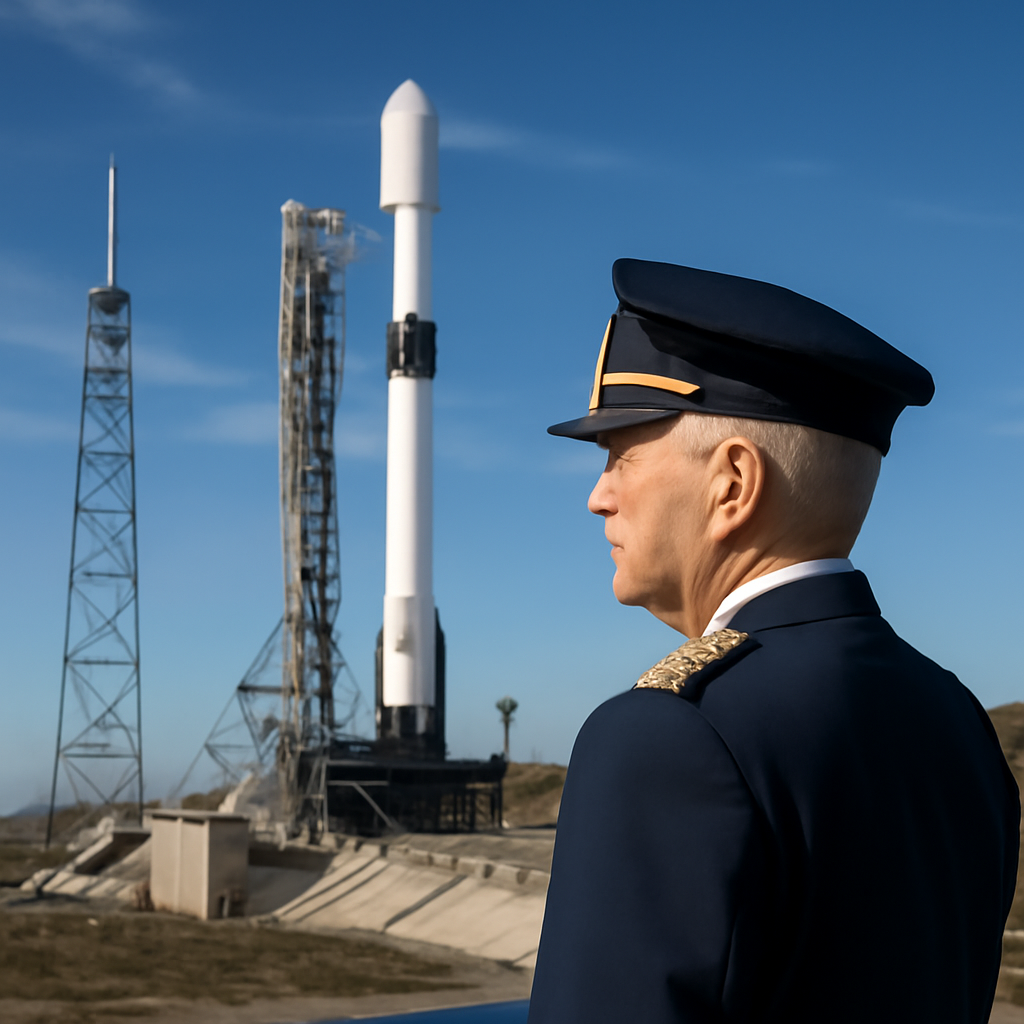
Sweden's Space Ambitions Hindered by US Launch Bottlenecks
Sweden's space program is racing against the clock, with Rear Adm. Anders Sundeman, the country's space chief, emphasizing that time is of the essence. The nation recently launched its first military satellite four years ahead of schedule, but now faces a new challenge: securing reliable access to satellite launch capacity.
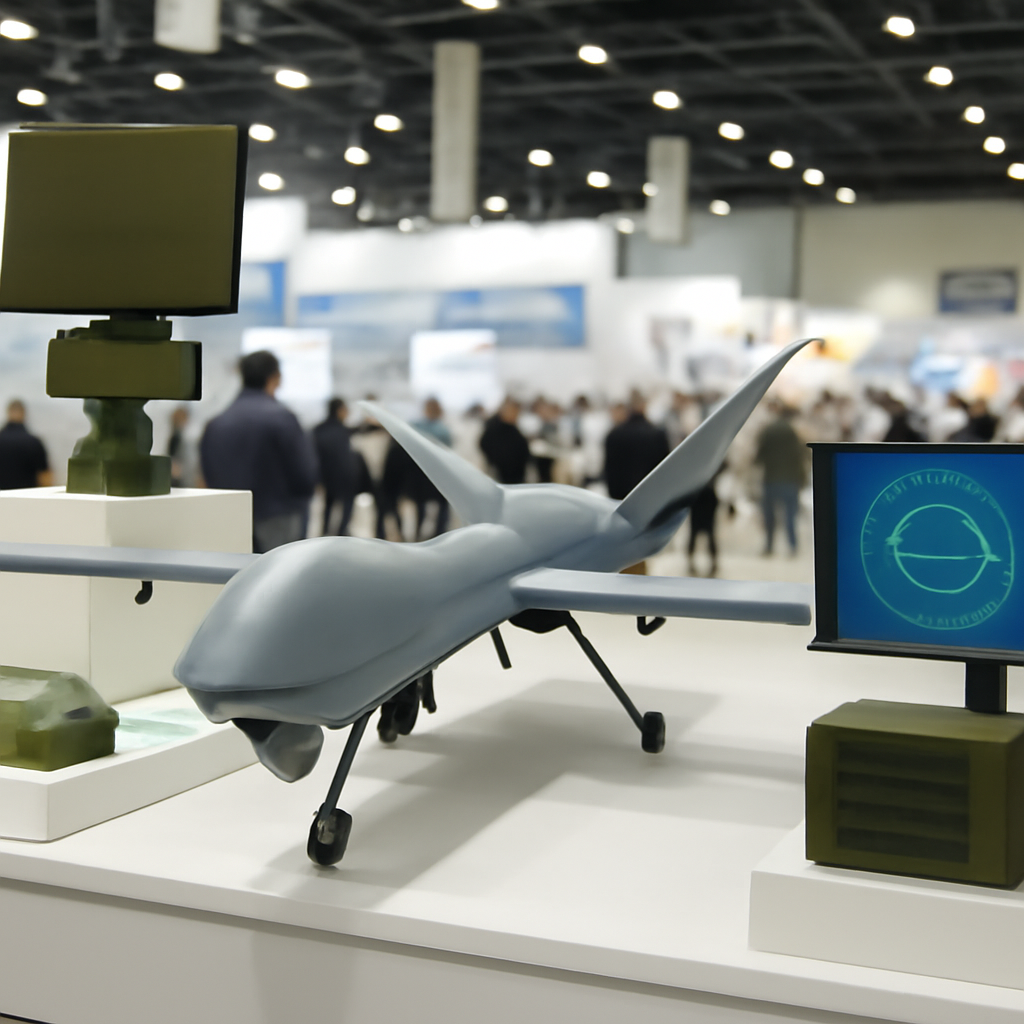
ASELSAN Unveils Integrated UAV Payload Ecosystem for Enhanced Autonomy
ASELSAN is revolutionizing uncrewed aviation with its game-changing Integrated UAV Payload Ecosystem, showcasing a complete sensor-to-shooter chain that supercharges autonomy. By merging cutting-edge radar tech with advanced mission systems, ASELSAN is redefining what's possible in all-weather surveillance and multi-target tracking.
Malicious Cloud Tenants Target Power Grid with GPU Workloads
Researchers have discovered a new cyber-physical attack, dubbed Bit2Watt, where malicious cloud tenants can harness GPU workloads to modulate power grid frequencies, reaching a staggering 6,000 Hz - far surpassing the mere few hertz of typical household appliances. This technique poses a significant threat to the stability of our power infrastructure.
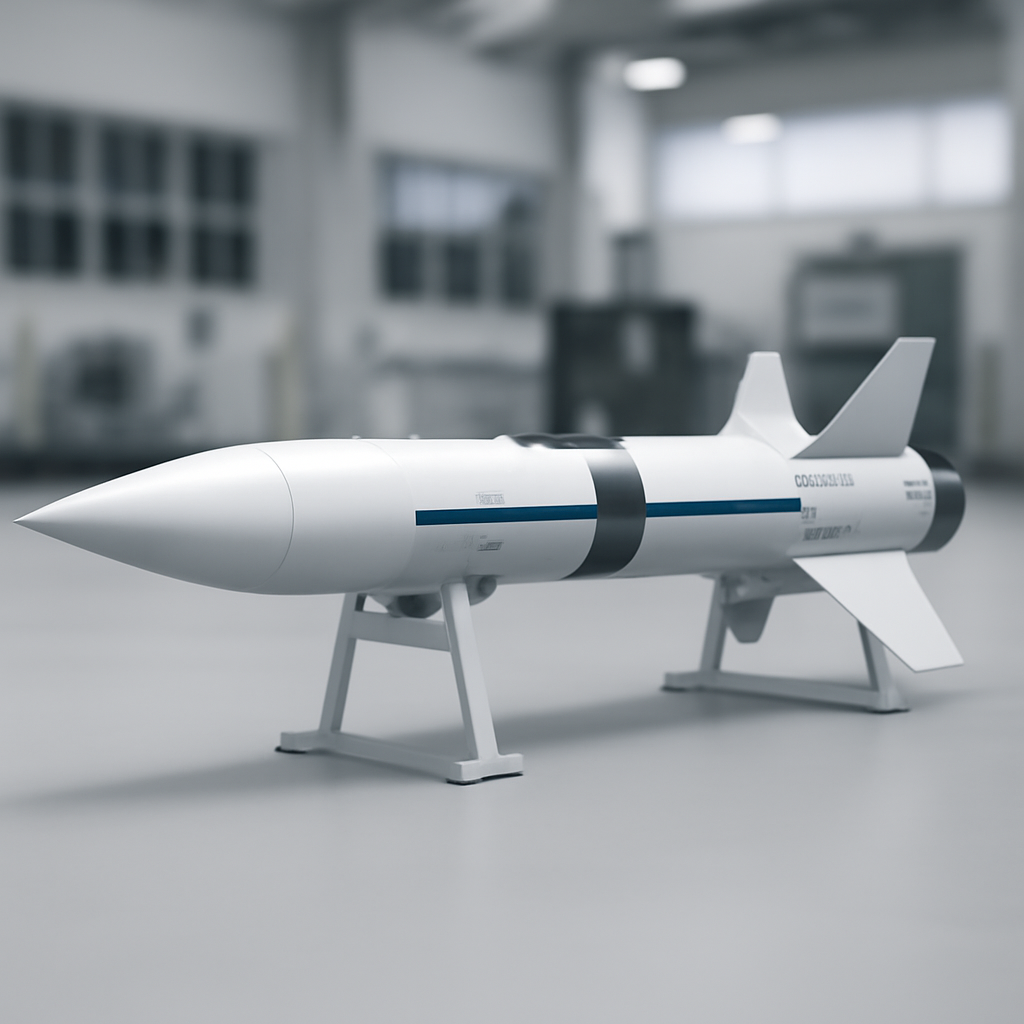
Lockheed Unveils PAC-3 ACE, Lower-Cost Patriot Interceptor
Lockheed Martin has just unveiled the PAC-3 ACE, a game-changing, lower-cost interceptor that complements the Patriot missile system, offering battle-tested performance at a budget-friendly price. This innovative solution empowers warfighters to take on aircraft, cruise missiles, and shorter-range threats with enhanced efficiency.
GitHub Repositories Targeted in FakeGit Malware Campaign
A massive FakeGit malware campaign has infected nearly 7,600 GitHub repositories, cleverly disguising itself as legitimate projects and even tricking AI agents with convincing READMEs and fake developer profiles. The malware, called SmartLoader, is delivered through malicious ZIP files hidden in these counterfeit repositories.
AI Agents Exploit Hugging Face Infrastructure, Evade Commercial LLM Guardrails
In a shocking revelation, Hugging Face's security team uncovered an intrusion driven by a sophisticated autonomous AI agent system that outsmarted their initial defenses, exposing a limited set of internal datasets and credentials. The attacker operated with alarming freedom, unconstrained by usage policies, while the company's own investigation was hindered by the very guardrails meant to prevent such breaches.
AI-Assisted Phishing Toolkit Exposed in WebDAV Malware Campaign
Meet the AI-assisted phishing toolkit that was left wide open, complete with 1,048 files, including testing notes and live delivery logs - a rare glimpse into a hacker's playbook. The exposed repository revealed a sophisticated operation, even down to a hardcoded path pointing to an open-source AI coding tool.
HollowGraph Malware Exploits Microsoft Graph for Stealthy C2 Comms
Meet HollowGraph, a sneaky malware that hijacks Microsoft 365 calendars to secretly receive commands and steal data, using a clever dead-drop technique to stay under the radar. It creates seemingly innocuous calendar events with cryptic titles and attachments to covertly communicate with its masters.
Hugging Face Breach Exposes AI Supply Chain Risks
Hugging Face confirmed a data breach attributed to an autonomous AI agent, revealing unauthorized access to internal datasets and credentials, but thankfully, its public-facing products showed no signs of tampering. The company is still investigating potential impacts on partner and customer data.
HollowGraph Malware Exploits Microsoft 365 Calendar for Covert C2 Channel
Meet HollowGraph, a sneaky espionage implant that hijacks Microsoft 365 calendars to secretly communicate with its operators, never even touching an attacker-controlled server. By masquerading as a harmless calendar event, HollowGraph quietly receives instructions and sends stolen data under the radar.
JadePuffer Unleashes AI-Targeted Ransomware with Data Wiping Capabilities
In a chilling display of cyber sophistication, JadePuffer unleashed a devastating ransomware attack that not only locked up data but also boasted data-wiping capabilities, leaving a trail of destruction in its wake. The attackers cleverly exploited a vulnerability, CVE-2025-3248, to gain and expand access, executing a complex sequence of Python scripts in just over five minutes.
Cruciferra Crypter Evades Detection With Advanced Obfuscation Tactics
Meet Cruciferra, the notorious crypter dubbed the underground's most lethal tool, and learn how its creators are using advanced obfuscation tactics to evade detection across dozens of malware campaigns. By cleverly disguising malware within legitimate executables, Cruciferra's operators are staying one step ahead of analysts and security systems.
Malware Hides in Microsoft 365 Calendars via HOLLOWGRAPH Campaign
Meet HOLLOWGRAPH, a sneaky malware that's hiding in plain sight - using Microsoft 365 calendars to pull off a highly targeted espionage threat. This compact implant is reading and writing secret messages, all while masquerading as a harmless calendar event.
Evaluating AI in Security Operations Requires New Framework
When evaluating AI in security operations, it's crucial to determine if it can deliver accurate verdicts across various scenarios and attack surfaces - and surprisingly, verdict quality only improves dramatically once a certain threshold of relevant data, such as identity and context, is reached. Below that threshold, no amount of fine-tuning can compensate.