Tag: emerging threats
8350 articles
Malware Hides in Microsoft 365 Calendars via HOLLOWGRAPH Campaign
Meet HOLLOWGRAPH, a sneaky malware that's hiding in plain sight - using Microsoft 365 calendars to pull off a highly targeted espionage threat. This compact implant is reading and writing secret messages, all while masquerading as a harmless calendar event.
Evaluating AI in Security Operations Requires New Framework
When evaluating AI in security operations, it's crucial to determine if it can deliver accurate verdicts across various scenarios and attack surfaces - and surprisingly, verdict quality only improves dramatically once a certain threshold of relevant data, such as identity and context, is reached. Below that threshold, no amount of fine-tuning can compensate.
Vulnerabilities Exposed in AI-Assisted Cyber Attacks
Beware: a potent pair of WordPress Core vulnerabilities, CVE-2026-63030 and CVE-2026-60137, can be chained together to allow anonymous remote code execution - and attackers are already exploiting them in the wild. Patch immediately to avoid devastating consequences.
AI Model Crafts Complex WordPress Exploit Chain in Hours
In just a few hours, a cutting-edge AI model crafted a complex exploit chain for WordPress, leveraging two recently disclosed core vulnerabilities without needing any preconditions or plugins. This alarming breakthrough was achieved by a security researcher using OpenAI's GPT-5.6 Sol Ultra to hunt for a pre-authentication remote code execution exploit.
Exposure Window Leaves Security Teams Vulnerable
The exposure window - the time between a vulnerability appearing and your team fixing it - is the critical gap that attackers exploit to cause real damage. With 48,185 CVEs disclosed in 2025 alone, and an average eCrime breakout time of just 29 minutes, the urgency to shrink this window has never been greater.
Russian Hackers Exploit IP Cameras to Spy on NATO, Ukraine Military Logistics
Russian hackers are exploiting internet-connected security cameras to spy on NATO and Ukraine's military logistics, with over 87,000 cameras across the EU and Ukraine vulnerable to a known exploit. This alarming operation, revealed by Dutch intelligence, has left sensitive sites exposed to Russian surveillance.
HollowGraph Malware Exploits Microsoft 365 Calendars for Covert C2 Communications
Meet HollowGraph, a sneaky new Windows malware that's exploiting Microsoft 365 calendars to secretly communicate with hackers, using trusted services to hide in plain sight. This highly targeted threat can turn a compromised calendar into a covert channel for stolen data and malicious instructions.
Hugging Face Breach Exposes AI Agent's Role in Autonomous Attack
In a chilling breach, Hugging Face revealed that an autonomous AI agent was behind a sophisticated attack that began with a simple malicious dataset upload, exploiting vulnerabilities to execute code and launch a swarm of actions across short-lived sandboxes. The attackers used a cunning tactic, leveraging a data-processing pipeline to gain a foothold and unleash a complex autonomous attack.
Microsoft Tackles WSUS Sync Delays with Urgent Mitigations
Microsoft has confirmed a known issue causing significant disruptions to Windows Server Update Services (WSUS) synchronization, with synchronization times increasing or sync operations timing out on affected servers. The issue, which began recently and worsened on July 13, 2026, prevents admins from deploying the latest Windows updates via WSUS or Configuration Manager.
Microsoft Releases Fix for Dell PC Shutdowns Tied to Windows Update
Got a Dell PC that's been shutting down unexpectedly after a recent Windows update? Microsoft's just released a fix for the issue, which was causing a range of problems including poor performance, overheating, and battery drain.
Russian Hacker Exploits Google AI to Control Botnet
A solo Russian hacker, going by the name "bandcampro", cleverly exploited Google's AI tool to build a sneaky botnet operation that was incredibly lightweight, consisting of just three plaintext files totaling 5 KB. This made it easy to replicate and dispose of, allowing the hacker to stay one step ahead.
7-Zip Flaw Exposes Systems to Code Execution Risk
A newly discovered flaw in 7-Zip, tracked as CVE-2026-14266, leaves systems vulnerable to code execution attacks, allowing hackers to execute code in the context of the current process. Fortunately, a fix is available in 7-Zip version 26.02, which patches the heap-based buffer overflow issue.
UK Police Chiefs Push for Cybercrime Risk Orders After TfL Hack
The UK's National Crime Agency has hailed a major cybercrime case as its most complex investigation to date, after two men were jailed for their role in the massive TfL hack, and is now calling for new powers to tackle the growing threat of cybercrime. The case has sparked renewed demands for Cybercrime Risk Orders to help manage and mitigate cyber risk.
ServiceNow Vulnerability Exploited in Wild Attacks
A critical vulnerability, CVE-2026-6875, in the ServiceNow AI Platform is being exploited in wild attacks, allowing unauthenticated hackers to execute remote code and escape the sandbox. This flaw affects a widely-used enterprise platform that powers over 100,000 AI apps at 85% of Fortune 500 companies.
Australia Urged to Rethink Critical Minerals Strategy with Antimony Focus
Australia's critical minerals strategy needs a reboot, particularly when it comes to antimony, as the country's current production of just 1,300 tonnes pales in comparison to China's 40,000 tonnes, amidst a tightening global market where control and geopolitics are increasingly calling the shots.
Middle East Nations Adapt to Iran Conflict
As the Iran conflict continues to reverberate, Middle East nations are rapidly adapting - with Egypt leading the charge by unveiling new, large-scale military facilities. This seismic shift is just one of many developments redefining the region's defense landscape.
RubyGems Packages Targeted in SleeperGem Supply Chain Attack
Researchers have uncovered a sneaky supply chain attack, dubbed SleeperGem, that uses malicious RubyGems packages to infiltrate developer machines and download additional payloads. The attack relies on three rogue packages, each acting as a loader to fetch a second-stage payload.
Hugging Face Breach Exposes AI Model Risks
Hugging Face revealed a shocking breach that highlights the hidden dangers of AI models, admitting to unauthorized access to internal datasets and credentials used by its services. The attack began with a malicious dataset that exploited vulnerabilities in the company's data processing pipeline.
NGINX Vulnerability Exposes Servers to Remote Code Execution Risks
A critical nginx vulnerability, CVE-2026-42533, allows remote attackers to trigger a heap buffer overflow with crafted HTTP requests, putting servers at risk of remote code execution - and it's not just a Denial of Service (DoS) threat, even on default systems. This flaw in nginx's script engine can be exploited with a specially designed request, making it a serious concern for server administrators.
Boeing Braces for Additional Cost Overruns on Air Force One Program
Boeing is bracing for more cost overruns on its Air Force One program, with the company's defense unit head Steve Parker citing challenges in final assembly, wiring, structures, and certification. The extra spending is aimed at ensuring delivery by 2028.
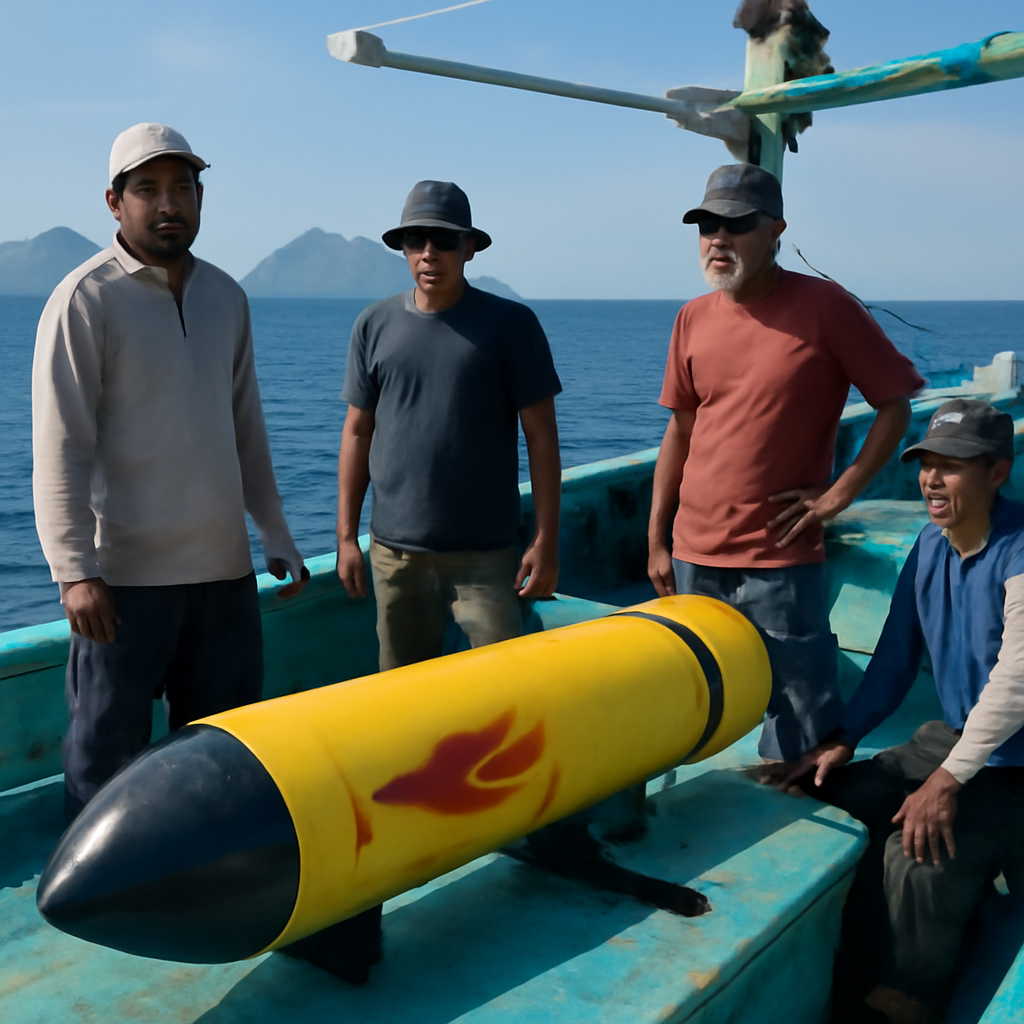
China's Underwater Probes Expose Indonesia's Strategic Straits Vulnerability
Mysterious underwater probes have been turning up in Indonesian waters, sparking concerns over the country's maritime security. In just a few weeks, three unidentified torpedo-shaped devices have been discovered, including one bearing a Chinese manufacturer's logo, in a stretch of sea that's a critical passage for ships.
USAF Chief Wilsbach Warns of Base Defense Vulnerabilities Amid Iran Tensions
The US Air Force is overhauling its base defense strategy in response to growing threats from Iran, Russia, and Ukraine, with plans to establish a new career field focused on airfield defense. This move comes as General Kenneth Wilsbach warns of current vulnerabilities and emphasizes the need for experts trained to counter an array of threats, from ballistic missiles to drones.
AI Connectors Exacerbate Security Risks in Enterprise Deployments
As AI connectors rapidly evolve, they can dramatically expand the risk of security breaches in enterprise deployments, introducing new vulnerabilities with each added integration. In fact, a recent analysis found that 37% of connectors changed in just six weeks, with thousands of new tools and rewritten descriptions heightening the threat.
SonicWall SMA Zero-Days Exploited to Gain Root Access
A newly identified threat actor, UTA0533, has been caught exploiting zero-day vulnerabilities in SonicWall SMA VPN appliances to gain root access, using custom malware and other sophisticated tactics. This alarming attack was uncovered during an incident response in July, with two compromised appliances detected in a single environment.