Tag: critical infrastructure
636 articles
UK, EU Attribute Poland Cyberattack to Russian Spies, Warn Infrastructure Operators
The UK and EU have called out Russia's Federal Security Service for a brazen cyberattack on Poland's power grid, saying it's just another example of their reckless attempts to wreak havoc across Europe. The attack, attributed to FSB's Centre 16, was foiled, but serves as a stark warning for infrastructure operators to stay vigilant.
EU Targets Russian Hackers with Sanctions Over Europe Cyberattacks
The European Union is cracking down on Russian hackers, imposing sanctions on nine individuals and four entities linked to malicious cyber operations that threaten the continent's security and stability. This move targets those behind a foiled attack on Poland's critical infrastructure, which could have left 500,000 people in the dark during winter.
Russian Hackers Target Routers Globally, Warn Cybersecurity Agencies
A brazen plot by Russian hackers to disrupt global networks was thwarted, but not before cybersecurity agencies warned of a potentially catastrophic attack that could have left 500,000 citizens shivering in the dark. The hackers, linked to Russia's Federal Security Service, targeted vulnerable routers worldwide using simple and easily exploitable passwords.
Russian Hackers Target Critical Infrastructure via Router Exploits
Russian state-backed hackers have infected 18,000 routers in 120 countries, sparking a multinational warning about the threat to critical infrastructure networks. The alarming campaign is linked to Russia's Federal Security Service (FSB) Centre 16, notorious for exploiting poorly configured routers to gain access to sensitive networks.
Australia Urged to Empower ACSC as Cybersecurity Regulator
As cyber threats increasingly put Australia's critical infrastructure, economy, and national resilience at risk, the country faces a critical choice: rely on voluntary measures or establish a robust cybersecurity regulator with the power to enforce minimum standards and hold organizations accountable. Empowering the Australian Cyber Security Centre (ACSC) as a formal regulator could be the key to bolstering the nation's cyber defenses.
US AI Clearinghouse Must Bridge Vulnerability Gap
The US AI cybersecurity clearinghouse has a crucial role to play in bridging the vulnerability gap, but time is of the essence - AI tools are surfacing vulnerabilities at a pace that's outstripping our ability to act on them. With a 30-day deadline now expired, the clearinghouse must swiftly coordinate efforts to scan, discover, and prioritize critical infrastructure vulnerabilities.
Pacific Seabed Becomes Contested Zone in Regional Power Struggle
The Pacific seabed, once a vast and empty space, has become a hotly contested zone as a growing number of nations and interests converge on its valuable resources, transforming the way power and risk are distributed in the region. This emerging crowded landscape is sparking new tensions, as mining, military operations, and other activities increasingly overlap and collide.
Democracies Need Critical-Minerals Stockpile Alignment
Democratic governments are taking a proactive approach to securing their critical mineral supplies, with Australia's recent announcement of a Critical Minerals Strategic Reserve being the latest example. This move is part of a growing trend to build resilience and reduce reliance on vulnerable supply chains dominated by a single country.
DHS Probes Breach of Homeland Security Information Network
The Department of Homeland Security is investigating a recent cyber breach targeting a legacy information sharing environment used by its Homeland Security Information Network. This platform is a critical tool for sharing sensitive information among partners to protect communities and respond to incidents.
Australia Secures Modified Pacific Pact with Vanuatu Amid China's Rise
Vanuatu's Prime Minister Jotham Napat revealed that last-minute concerns over a single clause - specifically the wording around third-party investment in critical infrastructure - led to his country's dramatic decision to decline signing the Nakamal Agreement with Australia. The clause sparked fears that Vanuatu might have to compromise its sovereignty or limit partnerships with other nations.
Microsoft Accelerates Quantum-Safe Transition Amid Rising Risks
Microsoft is speeding up its transition to quantum-safe cryptography, aiming to protect critical products and services from the growing threat of quantum computer attacks by 2029. The move is a response to rapid advances in quantum research, which have brought the risks of quantum computing closer than expected.
UK Boosts Defense Spending to $105 Billion by 2029
The UK is set to bolster its defense capabilities with a significant boost in spending, reaching $105 billion annually by 2029, as Prime Minister Keir Starmer vows to prioritize national security. This substantial increase, from 2.3% to 2.7% of GDP, is just the beginning, with a target of 3% in the next parliament.
DHS Revives Cybersecurity Council for Critical Infrastructure
The Department of Homeland Security is launching the Alliance of National Councils for Homeland Operational Resilience – Critical Infrastructure program to boost cybersecurity coordination between government agencies and private sector partners. This new initiative aims to bring together experts from various fields to tackle the latest threats and protect critical infrastructure.
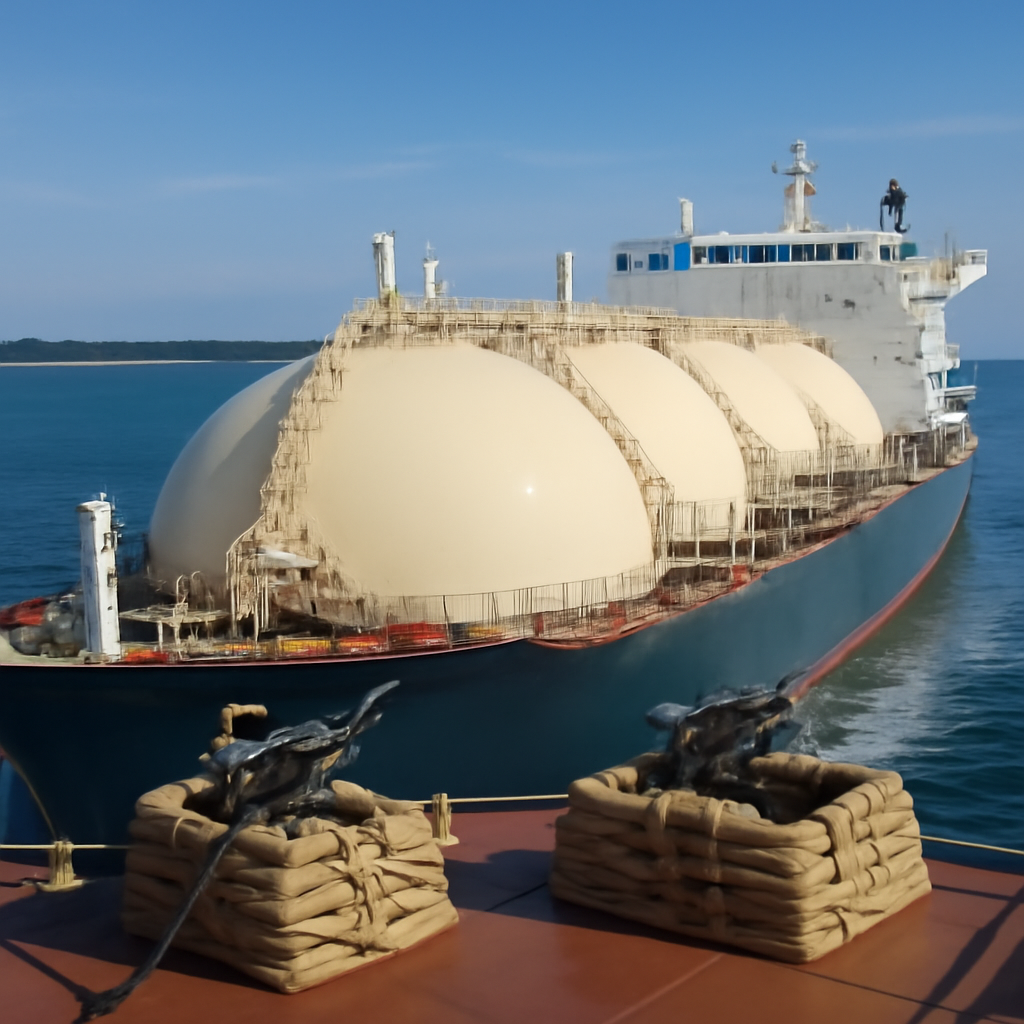
Russia Arms Commercial Tanker with Heavy Machine Guns
Meet the Marshal Vasilevskiy, a 945-foot LNG tanker that's moonlighting as a heavily armed behemoth, sporting sandbagged machine-gun positions on its deck. This unusual floating fortress is Russia's only floating storage and regasification vessel, supplying the exclave of Kaliningrad with a secure gas supply.
China-Linked Hackers Deploy TinyRCT Backdoor in Southeast Asian Infrastructure Attacks
For years, a stealthy China-linked hacking group has been quietly targeting critical infrastructure in Southeast Asia, with a clear strategic interest in disrupting or monitoring key regional industries. Their sophisticated attacks have zeroed in on state-owned energy and government sectors, using a potent tool called the TinyRCT backdoor.
FCC Tightens Cybersecurity Rules for Emergency Alert Systems, Undersea Cables
The FCC has just tightened cybersecurity rules for emergency alert systems and undersea cables to prevent vulnerabilities that could be exploited by rogue actors, foreign governments, or cybercriminals to spread chaos and misinformation. This move aims to safeguard the nation's primary public-warning platforms, including the Emergency Alert System and Wireless Emergency Alerts.
Iranian Hackers Exploit Credentials in Cal Water Breach
Cal Water swiftly sprang into action when an Iranian-linked group, Handala, claimed to have hacked their system, activating their cybersecurity response plan and launching a thorough investigation. Thankfully, experts from Mandiant found that the breach was limited to third-party accounts, containing no evidence of a larger-scale attack.
Australia's Security Threats Converge as AI Compresses Risk Timeline
When Australia's critical infrastructure is disrupted, it will be a shock, but not a surprise - and with AI supercharging threats, that disruption may come sooner than we think. The warning signs are clear: AI is rapidly expanding the offensive toolkit, making threats more immediate, concurrent, and devastating.
ASIO Disrupts Nation-State Cyber Sabotage Targeting Australian Infrastructure
ASIO director general Mike Burgess revealed that nation-state hackers had infiltrated a critical Australian infrastructure provider's network, gaining login credentials to sabotage it at will. The alarming breach was thwarted thanks to ASIO's swift action and dedicated response.
CISA Warns of Active Exploitation of Lantronix EDS5000 Flaw
A critical code-injection flaw, CVE-2025-67038, has been discovered in Lantronix EDS5000 Series devices, allowing attackers to inject arbitrary OS commands with root privileges due to a lack of input sanitization in the HTTP RPC module. This vulnerability has a CVSS score of 9.8, indicating a high severity level.
Scattered Spider hackers plead guilty to TfL cyberattack
Two young hackers, part of the notorious Scattered Spider group, have pleaded guilty to orchestrating a devastating cyberattack on Transport for London, causing millions in losses and disrupting the lives of countless commuters. The breach, which lasted several days in September 2024, forced TfL to acknowledge that sensitive customer data had been stolen.
US Accelerates Post-Quantum Cryptography Migration with 2030 Deadline
The White House is taking a major step to protect America's sensitive data and digital economy by mandating a rapid migration to quantum-safe encryption, with a deadline of 2030 for key establishment and 2031 for digital signatures. This move aims to safeguard critical infrastructure, jobs, and growth by future-proofing the nation's cybersecurity.
Hacktivism Surges as Geopolitical Crises Expose Cybersecurity Gaps
Hacktivist attacks have skyrocketed amid rising geopolitical tensions, with over 149 incidents reported in just three days - a stark reminder of the growing cybersecurity gaps. This alarming surge is part of a larger trend that began in February 2022, with hacktivist groups increasingly targeting critical infrastructure during times of conflict.
Australia's Food Security Prepares for Stress Test
A year of global turmoil has put Australia's food security to the test, proving that ensuring a steady food supply is crucial to national resilience. Recent events, from the Iran-Israel missile exchange to Strait of Hormuz pressures, have highlighted the need for governments to address vulnerabilities in the country's food system before it's too late.