Tag: asia
41 articles
Ledger Halts Asia Sales After Supply-Chain Attack Compromises Wallets
Trezor is stepping up its game to protect users, implementing a stricter legal framework and tighter checks on device sourcing, storage, and handling. Ledger, meanwhile, is warning users to be vigilant after discovering that devices sold by a Southeast Asian reseller had been compromised, allowing thieves to steal cryptocurrency recovery phrases.
Data Quality Overtakes Skills as Top Threat Hunting Barrier
Even the best threat hunters can come up empty-handed if their data is incomplete, inconsistent, or hard to access. Data quality has now overtaken skills as the top barrier to effective threat hunting, with 50% of cybersecurity practitioners citing it as their biggest hurdle.
Chinese Hackers Exploit Chrome-Windows Zero-Days to Deploy CLEANGULP Malware
Chinese hackers masqueraded as reputable media organizations and NGOs, using convincing phishing messages and fake sites to deploy the CLEANGULP malware, with one recent campaign targeting Asian government entities over support for a Hong Kong activist. They sent spoofed emails that appeared to be from the Center for American Progress, complete with links to suspicious domains.
MovieReaper Malware Targets Users via Compromised Torrents
Meet MovieReaper, a sneaky new malware that's been infecting hundreds of victims worldwide by hiding in compromised torrents, and Kaspersky's security researchers are sounding the alarm. This modular threat has been spreading rapidly across Europe, Asia, and Africa, putting both individuals and organizations at risk.
Xi Jinping's China Prepares for Power Transition
With China's Communist Party's national congress just over a year away, all eyes are on Xi Jinping as China watchers refresh their knowledge on the country's enigmatic leader. This pivotal event, held every five years, sets the stage for a major power transition in China.
Chinese Cargo Ships Gather Signals Intelligence Covertly
China's state-run shipping company COSCO has been secretly gathering signals intelligence for decades, using its commercial vessels to collect communication signals from ships and aircraft across Europe, North America, and Asia. This covert operation allows China to tap into a vast amount of sensitive information, giving it a significant edge in the global arena.
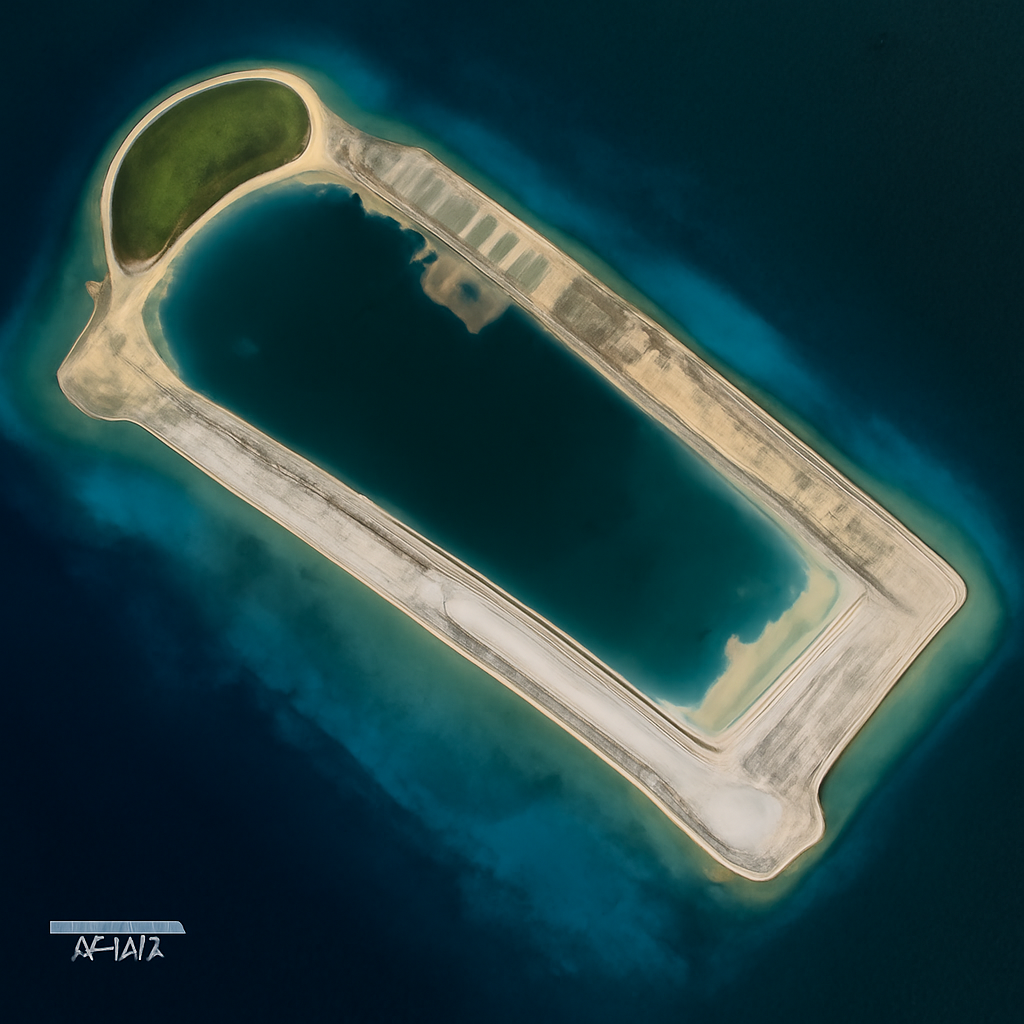
China Bolsters South China Sea Claim with Massive New Artificial Island
China has dramatically expanded its presence in the South China Sea, rapidly transforming a submerged shoal into a massive 3.7-mile-long artificial island, complete with a deep-water port and the makings of a military-grade runway. The astonishing reclamation project, fueled by over a million tons of dredged sand, has been nearly completed in under a year.
Zimbra Vulnerability Exploited in Active Attacks
A critical vulnerability in the Zimbra Collaboration Suite is under active attack, putting over 12,100 exposed servers worldwide at risk, with most located in Europe and Asia. Attackers can exploit this flaw, tracked as CVE-2026-73570, to execute remote code without authentication, simply by sending specially crafted SMTP requests.
Xi Jinping Consolidates Power in China
In 1978, Deng Xiaoping's groundbreaking "reform and opening" of China's economy sparked hopes for gradual political liberalization, but Minxin Pei argues that Deng's true intention was to preserve the Communist Party's grip on power, not pave the way for democracy.
US Commerce Speeds Defense Sales Advocacy Amid Global Competition
US Undersecretary of Commerce for International Trade William Kimmitt reveals that US defense firms are facing fierce competition from European and Asian rivals as they vie for a slice of the growing global defense market. With Europe's rising defense budgets, Kimmitt is rallying industry input to pinpoint key opportunities and give top picks a boost.
Cisco Confirms Active Exploitation of Unified CM Flaw
Over 200 Cisco Unified Communications Manager instances are vulnerable to a remotely exploitable flaw, CVE-2026-20230, which allows low-complexity server-side request forgery attacks with a simple crafted HTTP request. This critical vulnerability puts widely used IP telephony systems at risk, particularly in Asia and North America.
Asia's Future Hinges on Shifting Geopolitics
Asia stands at a critical juncture, where rapid development has given way to rising military competition and nationalist ambitions - but can it find a way to harness these forces before they spiral out of control?
Microsoft Uncovers ZIP Phishing Campaign Targeting Hotels with Node.js Implant
Microsoft warns of a sneaky ZIP phishing campaign that's been targeting hotels across Europe and Asia since April 2026, using photo-themed attachments to deliver a Node.js implant to front-desk machines. The cleverly crafted emails, often written in Japanese, Danish, or Dutch, use urgent and reputation-focused themes to trick recipients into opening the malicious attachments.

AI Agents Expose Blind Spots in APAC Enterprise Security
Attackers are now targeting AI agents embedded within APAC enterprises, exploiting weaknesses in non-human identities to gain access to sensitive systems, data, and workflows. This emerging threat highlights a significant blind spot in enterprise security, one that's ripe for exploitation by malicious actors.
Fraudulent Call History Apps Drain Millions via 7.3M Play Store Downloads
Millions of Android users have been duped into downloading 28 fake call history apps from the Google Play Store, with over 7.3 million downloads recorded before they were finally removed. These apps, which promised access to call logs and more, actually delivered nothing but randomly generated data - and a hefty price tag.

Novel Chinese Spy Group Infiltrates Critical Networks in Poland, Asia
A recent investigation by TrendAI has uncovered a concerning China-linked espionage campaign, with a novel spy group infiltrating over a dozen critical networks across Poland and Asia, leaving behind a lingering threat that's experts' biggest worry. The threat group, tracked as Shadow-Earth-053, has been actively compromising networks since December 2024.

AtlasCross RAT Fuels Alarming Asia Cyber Espionage Expansion
A new and sophisticated cyber threat, AtlasCross RAT, is targeting Chinese-speaking users in Asia, sparking concerns about the region's growing vulnerability to cyber espionage. As cyber adversaries expand their reach, the question is: are we prepared to face the rising tide of cyber attacks?
Investment Scams: Exclusive Asia Report on Alarming Spread
Our exclusive Asia report exposes the alarming spread of investment scams across the region—read on to spot the red flags and protect your money.

Winos 40 Stunning Risky Asia-Pacific Expansion
Winos 4.0 (ValleyRAT) is widening its reach into Japan and Malaysia using weaponized PDFs that drop links to a follow-on RAT (HoldingHands/Gh0stBins), making multi-stage phishing attacks more potent — now’s the time to lock down PDF handling, enforce URL filtering, and boost behavioral detection before attackers exploit language- and region-specific gaps.

NET malware Dangerous: Exclusive Phantom Taurus Threat
A Beijing-linked group dubbed Phantom Taurus is quietly using custom .NET malware to hunt credentials and siphon sensitive files from government web servers across Asia, Africa and the Middle East — a sharp reminder that everyday frameworks can hide serious threats. Defenders should harden .NET apps, tighten logging and MFA, and share indicators fast to turn the tables before secrets slip away.
ShadowSilk campaign: Exclusive, Alarming Threat
A stealthy campaign called ShadowSilk is quietly probing Central Asian and Asia‑Pacific government networks—stealing credentials, planting webshells and exfiltrating sensitive data—exposing how under-resourced states can be pawns in wider geopolitical espionage. Strengthening basic cyber hygiene, regional cooperation and fast incident response can blunt its impact before the next covert breach reshapes diplomacy and public trust.
ShadowSilk Exclusive: Risky Cyber Heist Exposes 36 Govs
Group-IB says ShadowSilk quietly siphoned sensitive data from 36 government-linked targets across Central Asia and the Asia‑Pacific, proving stealthy, data-driven espionage can outflank regional defenses. Its modular tools and persistent backdoors underscore why governments must share intelligence, harden networks, and treat cybersecurity as an ongoing strategic priority.
web hijacking: Stunning Diplomatic Threat
Imagine being a diplomat and not knowing your web traffic is being silently rerouted—Google has warned of a suspected state-backed web hijacking campaign hitting foreign ministries and diplomats across Asia. This stealthy interception can steal credentials, deploy malware, and influence negotiations, so stronger encryption, hardened captive‑portal workflows, and robust MFA are now mission‑critical.

cyber incident: Urgent Recovery Guide for Best Resilience
Colt has taken key systems offline after a cyber incident, leaving customers without access to portals and Voice APIs while it investigates and works to restore services. The outage underscores how much businesses depend on third-party networks and why clear communication, contingency plans, and rapid remediation are crucial.