[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongGeneral cybersecurity news and analysis
Join the ultimate online discussion crew and dive into a weekend of free-wheeling conversation - just remember to keep it respectful, even when opinions clash. In this off-the-cuff thread, anything goes, from the week's hottest topics to anything else that sparks your interest.
Reddit is evolving into a logged-in service, where users will need to be signed in to access content, in a bid to offer more personalized experiences and drive community connection. This change, led by co-founder Steve Huffman, aims to help users find relevant content and foster a sense of belonging on the platform.
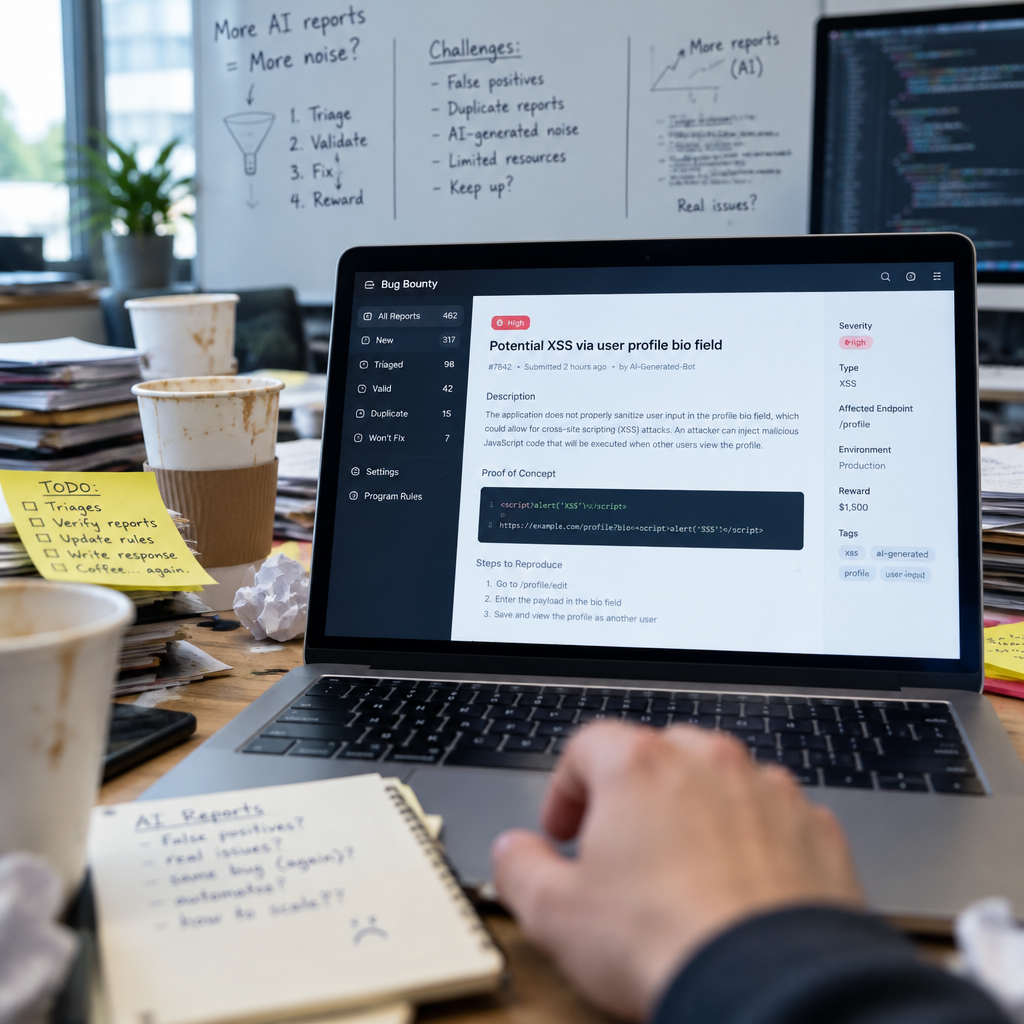
The curl bug bounty program came to a close on January 31, 2026, after being overwhelmed by a flood of low-quality, AI-generated reports that made it harder to identify real vulnerabilities. Fortunately, the program's maintainer reported a partial recovery, with confirmed vulnerabilities rebounding to 15%-16% and researchers continuing to uncover genuine issues amidst the noise.
A critical security flaw in ChatGPT was recently discovered, allowing hackers to access private conversations through malicious links - a vulnerability that was fortunately patched within just eight days. OpenAI responded swiftly, shelling out a $5,000 bug bounty to the security researchers who exposed the weakness.
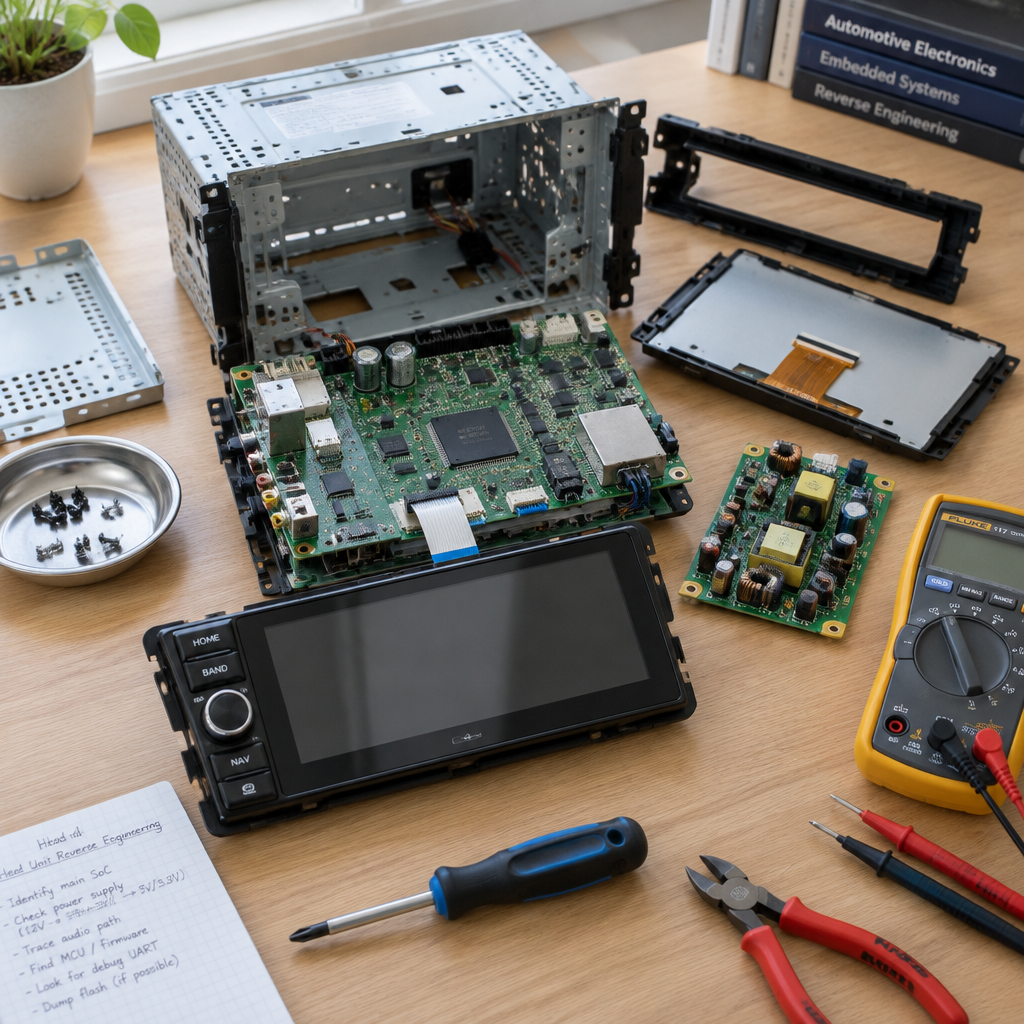
What happens when you plug a cheap aftermarket head unit into your car? One curious Civic owner discovered a suite of pre-installed apps that raised red flags about performance, privacy, and security.
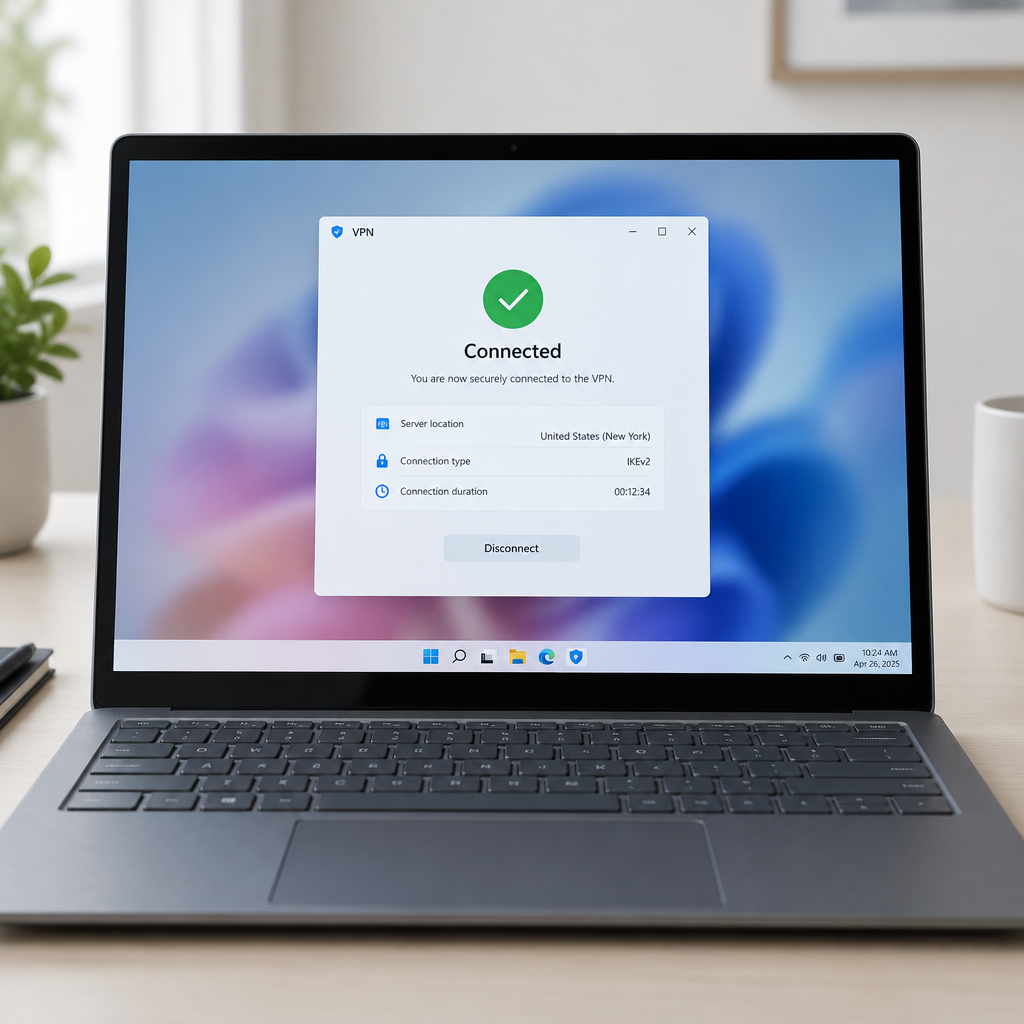
Microsoft has finally resolved a frustrating VPN issue affecting Windows 11 users who installed September's security updates, and the fix is now available in the October preview update KB5127936. This update brings relief to admins who've been dealing with Always On VPN connection failures since late September.
A newly discovered Linux flaw, CVE-2026-98432, puts servers at risk of remote root attacks, allowing hackers to execute commands as root on vulnerable servers running Multipath TCP (MPTCP) listeners. This severe bug, rated 9.8 out of 10, is a use-after-free vulnerability in the Linux IPv4 TCP stack that can be exploited by unauthenticated attackers.
A newly discovered flaw in TeamViewer, tracked as CVE-2026-111585, leaves users vulnerable to remote attacks, with a severity score of 8.8 out of 10, allowing hackers to take control with just a single remote-control session. All it takes is for a user to connect to a malicious host for the attacker to gain access.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Ransomware attacks on AI systems are on the rise, and a new online tool called RAID-AI helps security teams proactively identify vulnerabilities that could put their AI assets at risk. This free framework provides a structured assessment to bolster defenses against ransomware threats.
Imagine slashing false positives in cybersecurity alerts by 99% - that's the impressive result from experiments testing AI-powered filtering approaches. By harnessing the power of large language models, analysts can significantly reduce noise and focus on real threats.
Cyber threats are evolving at an alarming rate, and experts like Randolph Barr, Chief Information Security Officer at Cequence Security, are sounding the alarm about the dangers of AI-driven attacks. What keeps him up at night isn't a single exploit, but a disturbing convergence of factors that are compounding cyber risk.
Stay ahead of cyber threats by prioritising robust defence strategies over AI adoption, as Australian organisations face a growing number of attacks exploiting known weaknesses. With over 1,500 incidents reported last year, a solid cyber defence foundation is crucial, and that starts with basic yet essential knowledge of your software, updates, and data exposure.
Security fixes are stuck in limbo, waiting for proof of safe deployment, leaving critical alerts lingering for days. The solution lies in a four-stage approach: Observe, Prove, Act, and Confirm, ensuring that fixes are thoroughly tested and validated before implementation.
Despite the AI-driven infosec revolution, crypto exchanges are still struggling with basic security flaws, leaving them vulnerable to phishing, zero-days, ransomware, and other threats. It's a harsh reminder that some old security problems refuse to fade away.
AI developer tools have a hidden flaw - they embed browsers with supercharged capabilities that put host machines at risk of code execution attacks. A security startup discovered this weakness, dubbed the Embrace class of vulnerabilities, in five popular tools.
A critical Linux kernel flaw, CVE-2026-98432, has been discovered with a near-perfect CVSS score of 9.8, potentially allowing hackers to remotely take control of servers. This vulnerability stems from a use-after-free bug in IPv4 TCP handshakes, which could enable remote code execution.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Microsoft confirms that a recent update, released on October 28, 2026, has fixed Remote Desktop connection failures that prevented non-administrator users from connecting, and recommends installing the latest security update for a smoother experience. This fix, included in the KB5127936 preview update and later cumulative updates, resolves the frustrating error issue.
In today's digital landscape, bolstering financial cyber resilience requires a united front - and CREST is leading the charge with a whole-ecosystem approach that brings together financial institutions, supervisors, and cyber service providers. By sharing responsibility across these three key domains, we can build a stronger, more resilient financial system.
To build a resilient architecture, Nutanix experts Dan Fallon and Jason Langone advocate for a four-pronged approach centered around four key principles: secure, sovereign, scalable, and simple. This framework is crucial for enabling AI-driven decision-making in distributed environments.
Meet the sneaky side of AI agents: they can now operate quietly within your browser, using tools like the Chrome DevTools Protocol to navigate sites, extract info, and interact with web apps - all while hiding in plain sight. This stealthy access poses a significant security risk, allowing external apps to hijack your authenticated sessions.
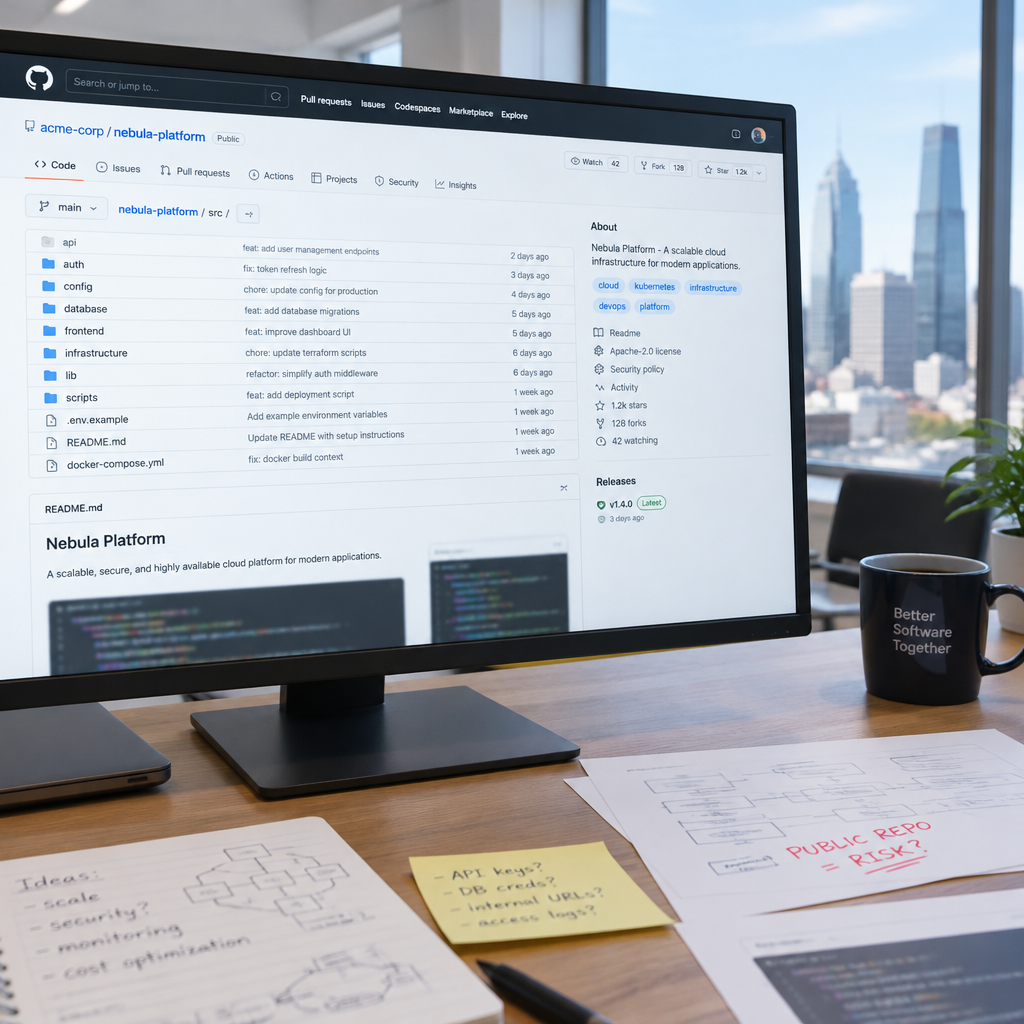
A recent scan of public Gitee repositories uncovered a staggering 26,400 exposed cloud credentials that still worked when tested, highlighting the alarming risk of long-discarded secrets remaining live and exploitable. This shocking discovery was made by independent researcher Ben Zimmermann, who analyzed a massive 7.25 million public repositories.
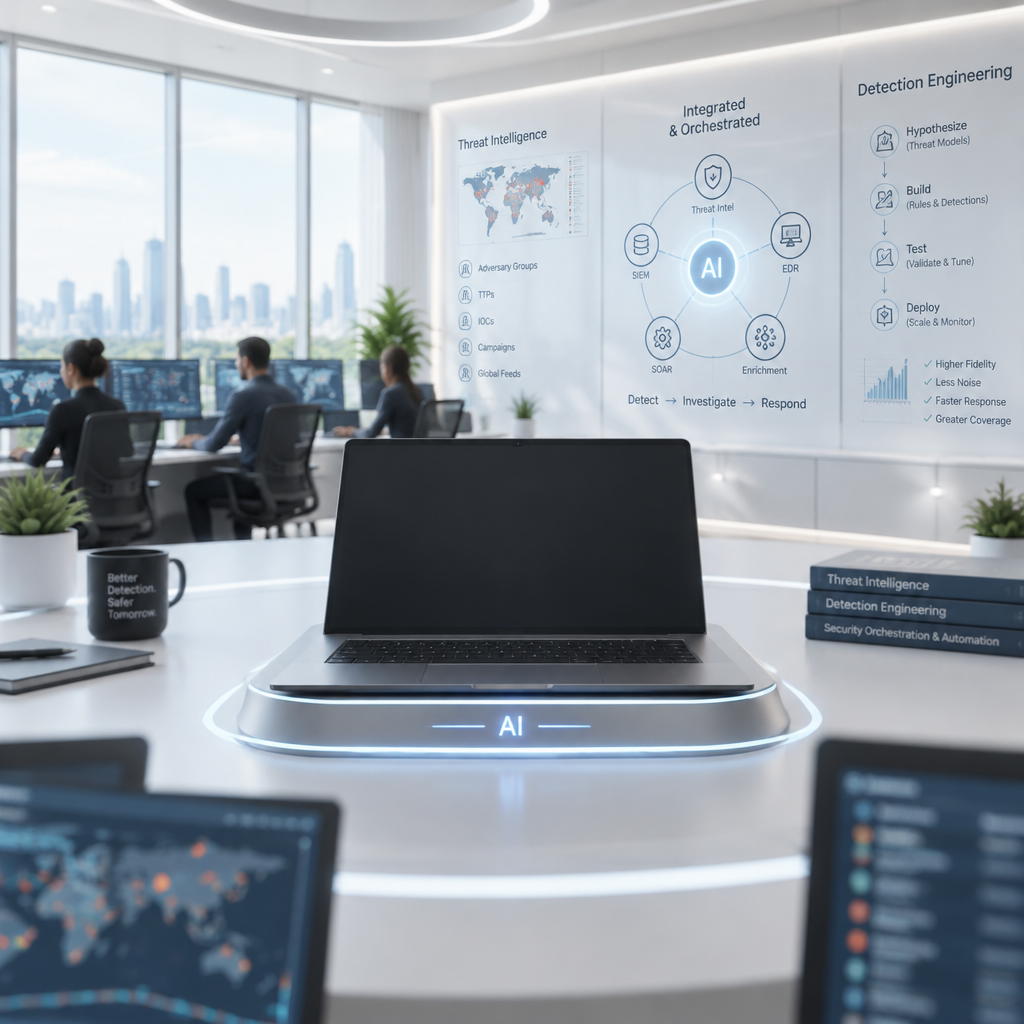
AI is revolutionizing security operations by taking over tasks traditionally handled by security analysts, paving the way for a new era of AI-driven threat detection and response. By integrating functions like threat intelligence, hunting, and incident response, AI agents can now tackle security challenges with unprecedented speed and efficiency.
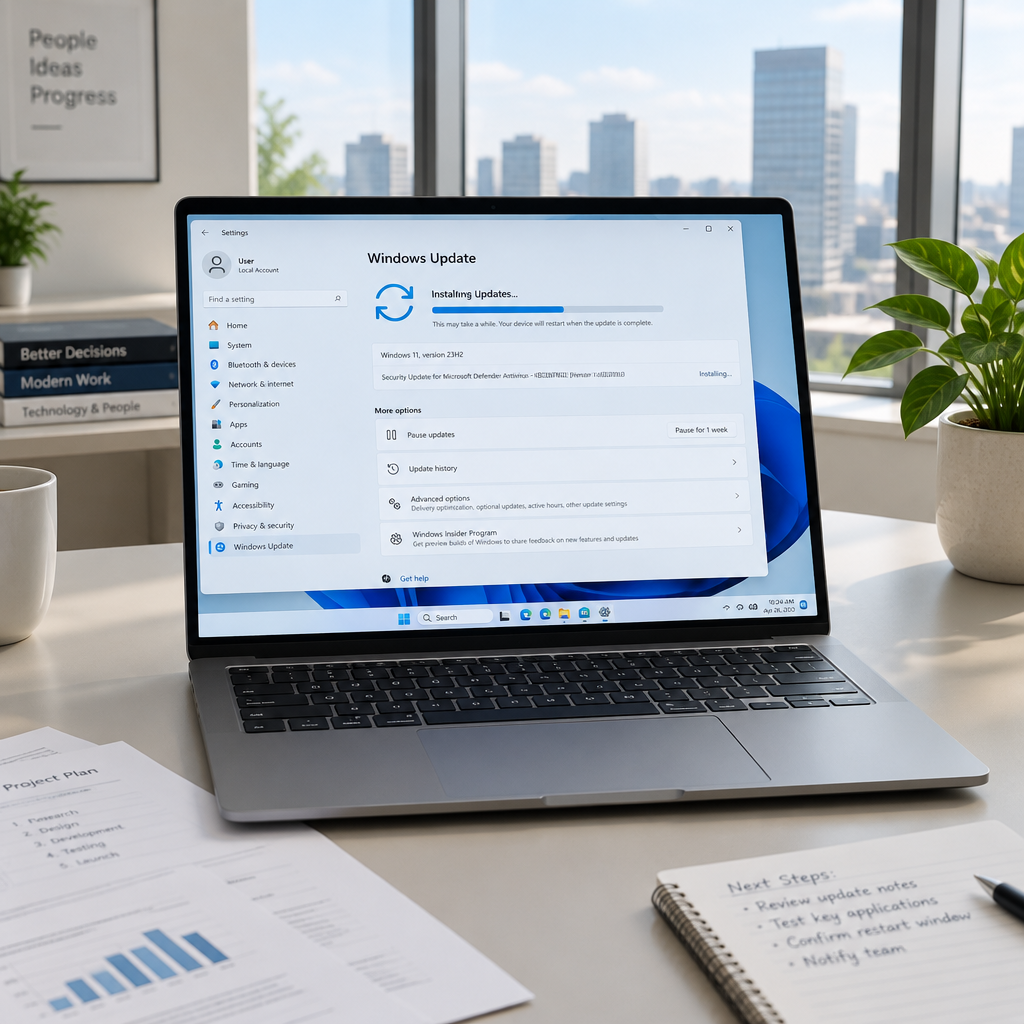
Microsoft just dropped a new update, KB5127936, for Windows 11, packing 41 changes and fixes to supercharge your experience. This optional update is a sneak peek at what's coming next, and you can grab it now from the Microsoft Update Catalog to try out the latest features and improvements.
GitHub is stepping up its security game with a new package firewall for npm, blocking suspicious packages from being installed and protecting against malware attacks. This innovative firewall acts as a gatekeeper, inspecting metadata requests and package downloads to keep your systems safe.