[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentGeneral cybersecurity news and analysis
You'd think hackers would target weak passwords, but surprisingly, they're more likely to exploit your emotions - specifically, your anger. A recent factory network scan revealed few obvious entry points, but it's what hackers use to get inside that might just surprise you.
The clock is ticking: with deadlines looming in 2030 and 2031, federal agencies and their technology partners must take swift and sustained action to migrate to post-quantum cryptography and safeguard sensitive systems. NIST's new guidance provides a crucial roadmap for meeting these urgent requirements.
Security researchers have uncovered a critical vulnerability in Oracle's E-Business Suite, tracked as CVE-2026-101767, which allows attackers to launch unauthenticated SQL injection attacks with the potential for remote code execution. This flaw was recently patched by Oracle, but not before decoys recorded exploratory exploits, highlighting the urgent need for updated defenses.
As AI reshapes enterprise risk, CISOs must urgently adapt, with Mark Weatherford stressing that security leaders can no longer afford to be reactive, emphasizing the need for continuous risk management. Today's CISOs must translate AI risks into business terms, making sure executives understand and own the associated risks.
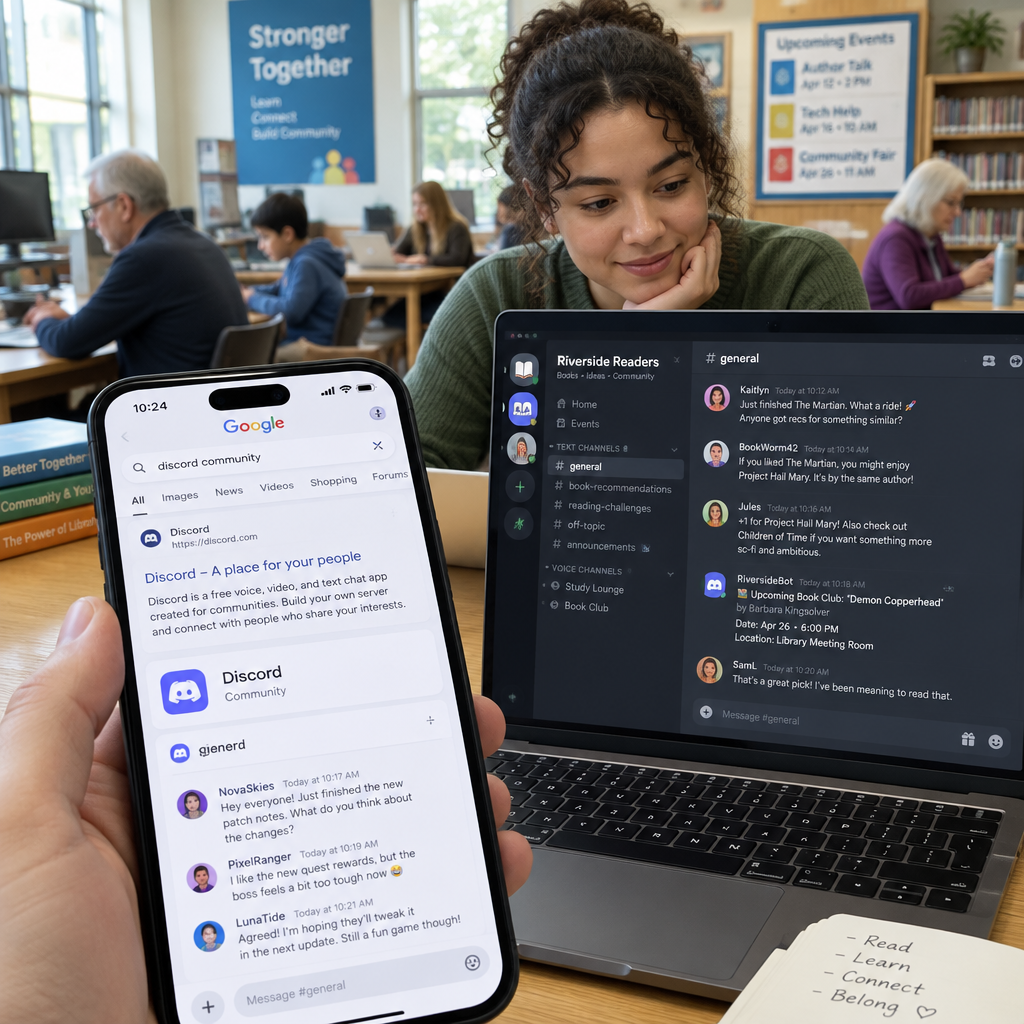
Get ready to uncover the conversations that matter - Discord is opening up its Discoverable Servers to web search indexing, making it easier to find answers and join the discussion. Soon, you can stumble upon useful info from public Discord communities, even if you don't have an account.
Meet Orange Tsai, the mastermind who turned a simple web page into a code-executing machine outside Microsoft Edge's sandbox - all thanks to a clever chain of five logic errors. His ingenious exploit, which won a whopping $175,000 at Pwn2Own Berlin, was surprisingly compact, consisting of under 100 lines of code crafted over just two months.
Big news for Android users: starting December 1, approved third-party app stores can now install apps with just one tap and automatically push updates in the background, making it easier to discover and stay up-to-date with your favorite apps. This streamlined experience will be available on devices running Android 17 QPR2 or later in supported countries.
Tired of drowning in a sea of security alerts? AI-powered automation can be a game-changer for Security Operations Centers (SOCs), helping to streamline workflows, reduce analyst fatigue, and uncover critical threats that might otherwise be missed.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A 16-year-old vulnerability in EDK II's UEFI firmware, known as CVE-2026-97631, leaves servers exposed to code execution before Secure Boot even kicks in, allowing attackers to interfere with or run code on machines during network boot. This flaw can be triggered by a simple 504-byte overflow in the PXE driver, enabling malicious code to overwrite nearby memory and wreak havoc.
Microsoft is urging Entra ID admins to switch to passkey authentication before February 1, 2027, when SMS and voice authentication will be phased out due to vulnerability to phishing and SIM-swap attacks. By migrating now, admins can ensure a seamless sign-in experience for users and stronger, phishing-resistant protection.
As healthcare becomes increasingly interconnected, sharing patient data across providers and cloud environments improves care efficiency, but also widens the vulnerability window, making cyber resilience a critical priority. Protecting sensitive information requires complete visibility into data movement, access, and processing - including third-party providers and AI-enabled workflows.
With over 4 million downloads of the Intelbras Mibo Smart app, a single security vulnerability in its IP cameras has become a major concern, leaving millions of users exposed to potential hacking threats. A recently discovered unauthenticated firmware endpoint has put these devices at risk of a Denial-of-Service attack.
Cisco's new tool, Project Quarry, helps detect rogue AI agents by monitoring their behavior and flagging suspicious multi-step activity that could indicate misuse or compromise. This open-source engine provides a shared language for identifying potential threats, giving organizations an upper hand in the fight against AI-powered attacks.
Adobe is urging users to update their Campaign Classic and Connect software immediately, as critical flaws have been patched that could lead to arbitrary code execution if left unaddressed. The company has confirmed that it hasn't seen any of these vulnerabilities exploited in the wild - yet.
Anthropic's AI model has made a groundbreaking discovery, autonomously uncovering security flaws in major browsers and operating systems, and chaining them into working exploits with minimal human input. This remarkable achievement has led to crucial patches being deployed across Chrome, Safari, Android, Windows, and Linux.
Tailscale's SSH system had a vulnerability that allowed attackers to gain root access, as demonstrated by a simple test that produced a root shell and read the system password file without admin rights. The flaw was rooted in how Tailscale handled socket forwarding, which was quickly patched once discovered.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
The US Cyber Chief has launched Project Lifeline 250, a game-changing pilot program that supercharges rural hospital defenses by connecting them with top-notch American tech and tools. This six-month initiative helps safeguard hospital networks, deploy backup devices, and upgrade high-risk equipment to ensure rural communities get the critical care they need.
As Anthropic edges closer to its IPO filing, the AI pioneer is sounding the alarm on a pressing concern: the potential for its own technology to be exploited for cyberattacks, posing significant risks to its customers, reputation, and bottom line. The company's warning highlights the double-edged sword of innovation, where groundbreaking tools can also be leveraged for malicious purposes.
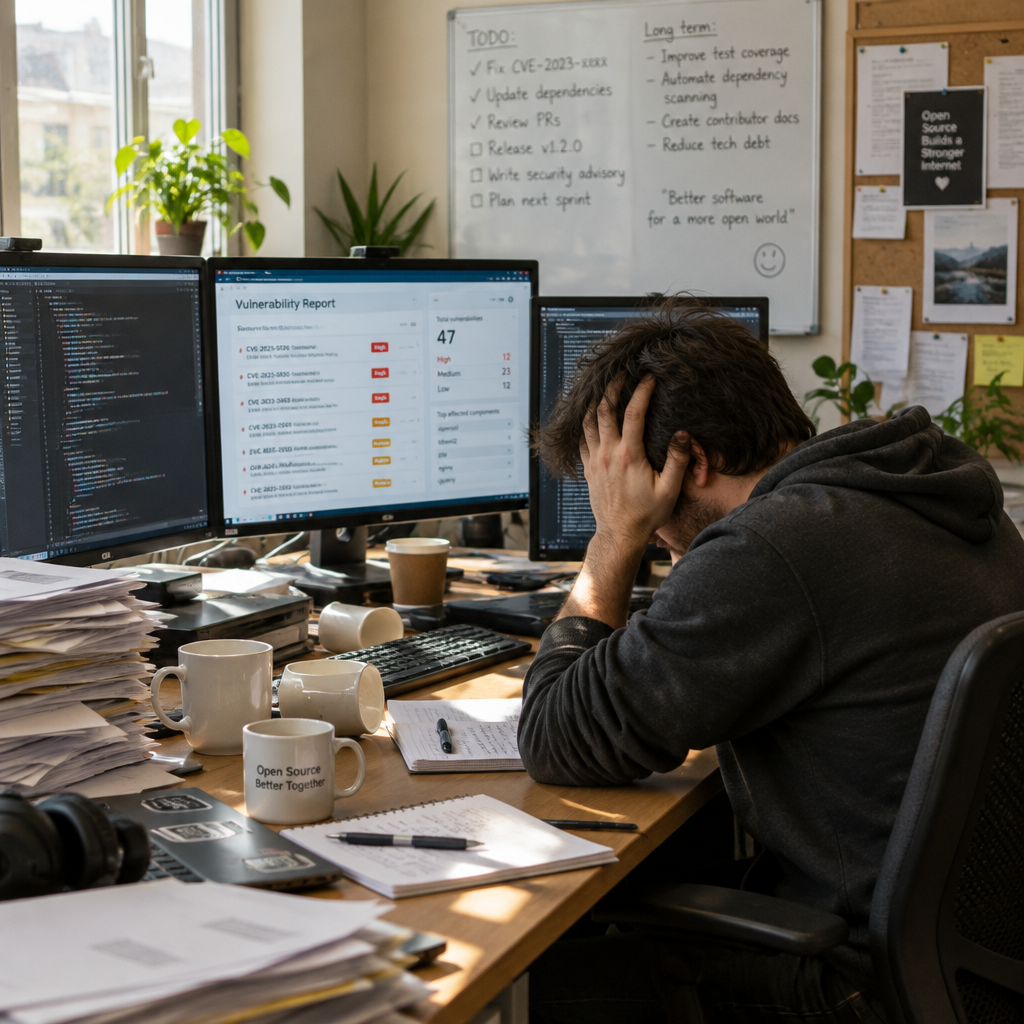
The surge of AI-generated vulnerability reports is overwhelming open-source maintainers, with some projects becoming so inundated that they're forced to stop accepting submissions altogether. This deluge of reports is proving unsustainable, leaving maintainers struggling to sift through hundreds of AI-submitted vulnerabilities to determine their validity.
Researchers have uncovered a chilling vulnerability in AI models that allows hidden, encrypted neural networks to be embedded within their weights, lying dormant until triggered to unleash their secrets. This alarming backdoor construction technique enables attackers to conceal arbitrary computations, putting the reliability of AI safety evaluations at risk.
In just three hours and 49 minutes, an autonomous AI agent called Cipher uncovered four severe bugs in industrial control software, EPICS Base, without any human intervention. The discovery has prompted a warning from the US Cybersecurity and Infrastructure Security Agency, urging organizations to update to the latest version to avoid potential denial-of-service, memory corruption, and remote code execution attacks.
Microsoft just took a crucial step to protect your online security by releasing emergency Windows updates to distrust eMudhra certificates, which were surprisingly easy to crack due to weak key generation. These out-of-band updates, KB5134133 and KB5134125, ensure your encrypted communications stay private by blocking potentially compromised certificates.
Researchers uncovered a vulnerability in the OpenAI API, dubbed "compaction smuggling," which allowed them to extract raw reasoning traces from AI models - information that OpenAI typically keeps under wraps. The flaw has since been fixed, with OpenAI paying a $6,000 bug bounty to the researchers who discovered it.
Apple just dropped a critical patch for a CoreGraphics flaw that could let hackers take control of your device - and it's available for older devices too. This high-severity vulnerability, with a CVSS score of 8.8, may have already been exploited in targeted attacks, making it crucial to update ASAP.