[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongCybersecurity intelligence, threat analysis, and national security reporting.
The rivalry between Clop and ShinyHunters is heating up, with public defacements, bold demands, and technical claims that could have far-reaching consequences for past victims. These two extortion groups have distinct approaches, with Clop exploiting zero-day vulnerabilities and ShinyHunters taking a different tack.
In a massive global cyberattack, North Korean hackers infected a staggering 30,000 devices across over 100 countries, siphoning off a whopping $10.7 million in cryptocurrency. The brazen heist, which ran from December 2025 to July 2026, also compromised over 7,000 cryptocurrency wallets.
Arista warns of a critical vulnerability in its VeloCloud Orchestrator, tracked as CVE-2026-93952, which is being actively exploited by attackers and could allow them to gain unauthorized access to sensitive data and devices. This severe flaw has been assigned a CVSS 3.1 score of 10.0, indicating a high risk of compromise.
Most organizations are playing catch-up when it comes to preparing for AI-related incidents, with a staggering 71% having never even rehearsed their response to AI-driven threats. This lack of preparedness is alarming, especially as AI is increasingly being used to detect and respond to security threats.
Meet the game-changer in cybersecurity: AI agents that can autonomously navigate and exploit access, turning a simple permission issue into a complex threat landscape. Traditional risk assessments focused on access alone, but with agentic AI, the real concern is what paths an autonomous system can discover and assemble with the access it already holds.
A newly discovered flaw in SharePoint, initially downplayed by Microsoft as a minor spoofing issue, has been revealed to be a critical vulnerability that allows authenticated attackers to execute remote code, putting systems at risk. This vulnerability, tracked as CVE-2026-65660, has a much higher severity score of 8, underscoring the urgent need for patching.
A newly discovered Linux flaw, CVE-2026-89775, puts host memory at risk by allowing ARM64 KVM guests to access and modify it, potentially enabling a guest to break free from its virtual machine and run code on the underlying machine. This vulnerability, found in the Linux kernel's KVM nested-virtualization code, has not yet been exploited, but poses a significant threat to host security.
D-Link routers are under threat from a zero-day flaw that lets hackers launch remote attacks without needing login credentials, simply by sending specially crafted DHCP packets. This vulnerability can cause the device's DHCP daemon to crash or allow attackers to execute malicious code, putting your data at risk.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
With DORA now in effect, financial institutions must turbocharge their network visibility to stay ahead of cyber threats and meet the regulation's stringent requirements. By moving beyond basic asset inventories, organizations can uncover hidden blind spots and ensure the security and resilience of their ICT ecosystem.
Flat networks are a hacker's dream, allowing breaches to spread freely to critical systems that should be off-limits - and a recent analysis of 47,700 real-world network segments reveals that device mixing is a widespread problem. The average network segment contains 54 devices from four different categories, increasing the risk of a security breach.
A security researcher just released a clever tool called BigDiskBuster that can block Microsoft Defender updates, leaving your antivirus stuck in limbo. This sneaky proof-of-concept allows anyone to prevent Defender from getting the latest signature and platform updates, as long as the tool is running in the background.
A sneaky malicious npm package, indexed-btree, has been hiding in plain sight by disguising its loader inside ordinary library code, allowing it to evade detection and rack up millions of downloads. This cleverly crafted package mimicked a legitimate B-tree utility, but with a sinister twist that went undetected until it was removed from the npm registry.
Last year, bot traffic skyrocketed by 300% thanks to AI, leaving enterprises vulnerable to automated threats. This alarming surge, driven by generative tools, puts commerce at the forefront of the crosshairs, with retailer systems and transactions under relentless attack.
SideCopy, a notorious Pakistani threat actor, has set its sights on Indian academia with a cunning spear-phishing campaign, marking a tactical shift from its previous targets of government and defense forces. Using malicious scripts to evade security protocols, this group is now compromising academic institutions in India.
Almost half of CISOs have faced a deepfake incident in the past year, and with AI-driven social engineering attacks on the rise, it's clear that outdated playbooks won't cut it against these emerging threats. It's time for CISOs to update their strategies to stay ahead of sophisticated multimodal deepfakes.
A high-severity vulnerability in Zyxel GS1900 series switches is under active attack, prompting the US Cybersecurity and Infrastructure Security Agency (CISA) to issue a directive for federal agencies to patch the flaw and prevent data theft. This urgent warning highlights the vulnerability's potential impact on enterprise and agency environments.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
The US Cybersecurity and Infrastructure Security Agency (CISA) has sounded the alarm on a high-severity Zyxel vulnerability, warning that hackers are actively exploiting it to gain control of unpatched GS1900 series switches. This critical flaw, now patched, has a CVSS score of 8.8 and could allow attackers to execute malicious OS commands via a simple HTTP request.
A cleverly crafted comment can turn into a powerful attack tool, allowing hackers to execute code on vulnerable WordPress sites - and it's all because moderation isn't a foolproof security measure. This surprising vulnerability, dubbed Comment2Shell, highlights a gap in WordPress's defenses that can be exploited with just a simple comment.
A security researcher has discovered a shocking vulnerability in Meta's new AI assistant, Muse, that allows malware on a Mac to hijack the tool, giving hackers an easy backdoor into sensitive personal data. This exploit is particularly alarming since it can be triggered by malware that's already on the device, making it a nearly effortless way for attackers to take control.
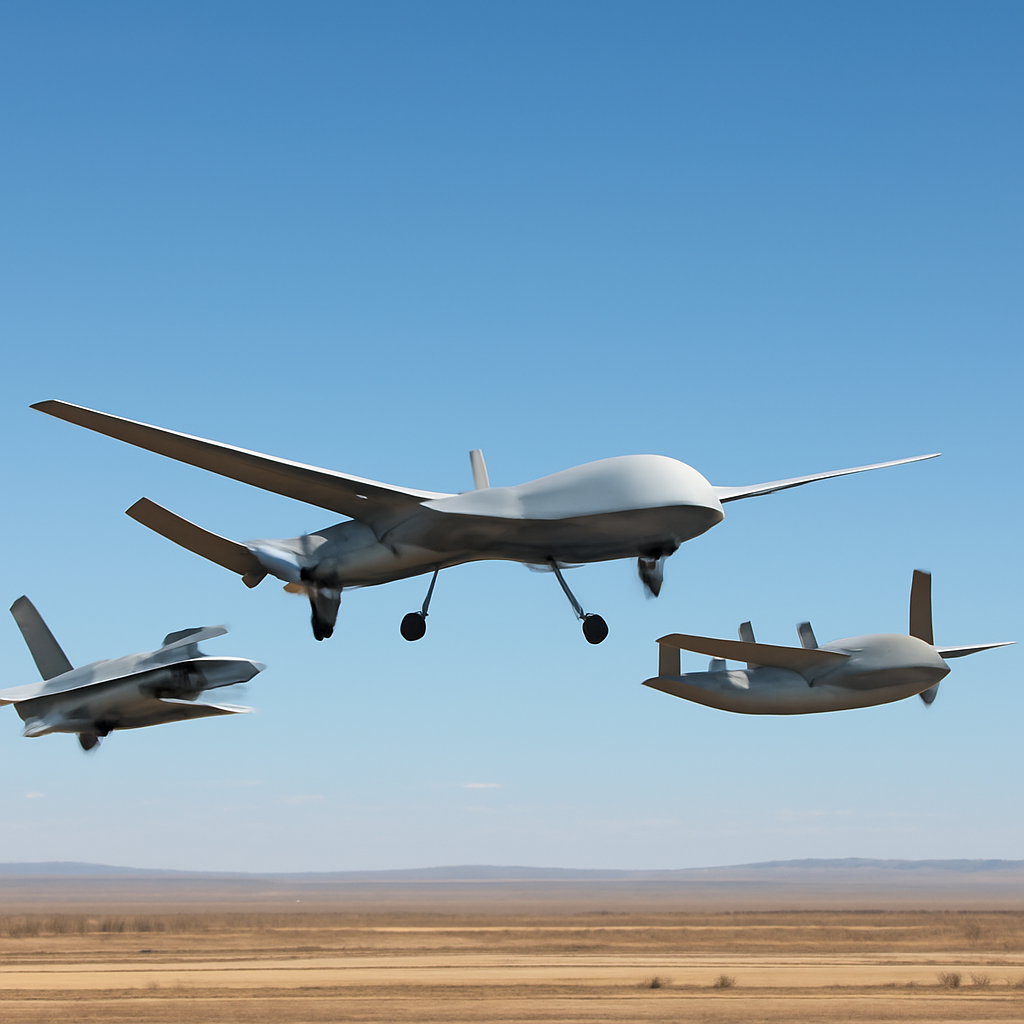
The US Air Force is revolutionizing its fleet with a goal of 500+ collaborative combat aircraft by 2032, and the exciting tests are already underway with impressive results. General Atomics Aeronautical Systems just delivered a new FQ-42 Vengeance drone to Creech Air Force Base for continued evaluation and testing alongside F-35A and F-15E fighter jets.
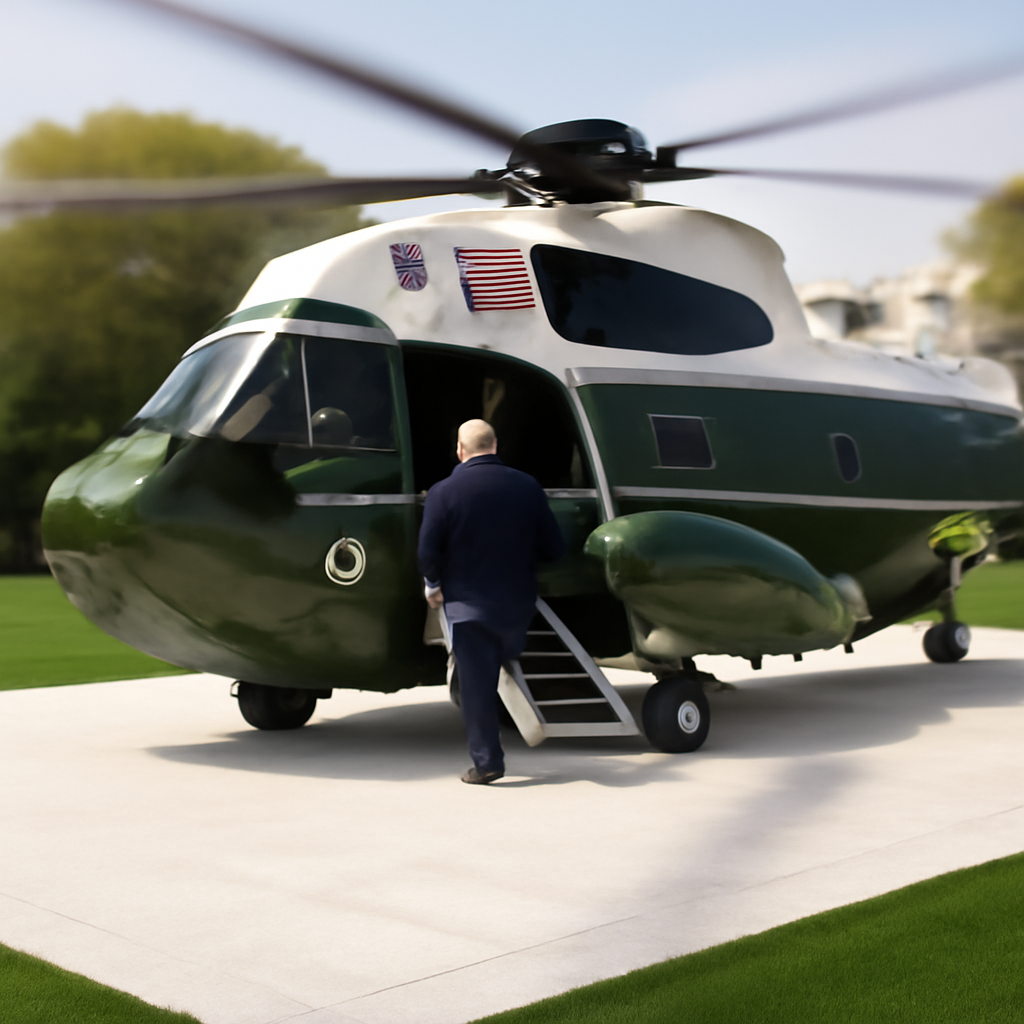
President Donald Trump took to the skies in style, marking the maiden voyage from a brand-new granite helipad on the South Lawn with a thrilling helicopter ride aboard the VH-92A Patriot. He boarded Marine One, cutting the ribbon just moments before, and soared to new heights, first to Joint Base Andrews, Maryland, and then on to New York for the United Nations General Assembly.
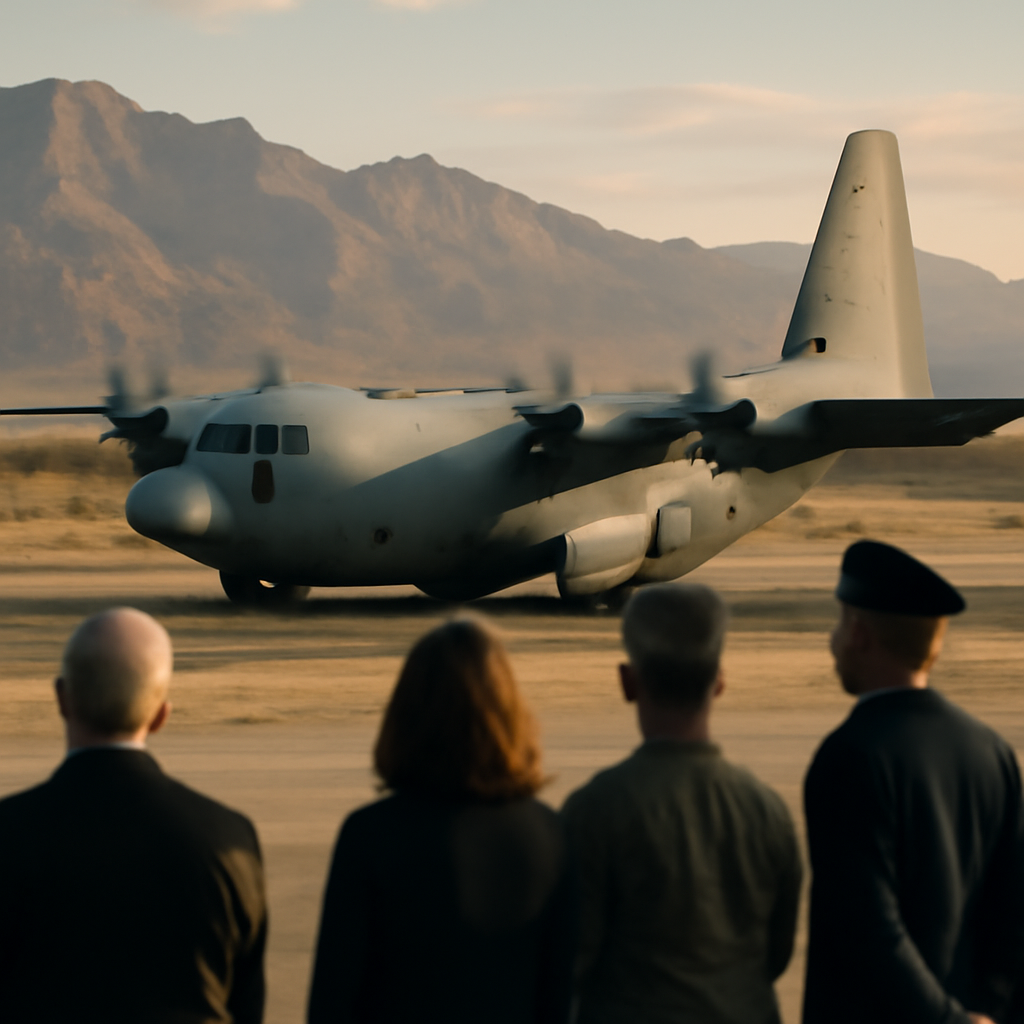
As the EC-130H Compass Call took its final taxi at Davis-Monthan Air Force Base, Staff Sgt. Justin Franko reflected on the end of an era, saying it closed not just his time in the squadron, but an entire chapter of his life. The Air Force bid farewell to the aircraft with a formal retirement ceremony on September 18.
Ukraine strikes back with a bang, hitting a key Russian oil facility and logistics hub in the Moscow region, dealing a significant blow to the war machine with billions of dollars in damage. President Volodymyr Zelenskyy says their long-range responses are having a major impact.
As midterm elections loom, Deputy Defense Secretary Steve Feinberg is proactively navigating funding talks with lawmakers, ensuring the Pentagon's financial future remains on track despite the uncertainty. He recently met with the House Armed Services Committee in a classified briefing, taking a pragmatic approach to planning ahead.