[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
A recent FBI breach was caused by a security failure at a third-party organization, Accenture, after a contractor neglected to apply a crucial security patch, exposing sensitive employee information. This incident highlights the significant risks associated with relying on outside vendors and the importance of stringent security measures.
Ransomware attackers are now targeting backup infrastructure, leaving victims with a harrowing choice: pay up or lose everything. UnitedHealth's $22 million ransom payment was a stark reminder of this new reality, as they still didn't recover their data.
The Operational Technology Cybersecurity Coalition is urging CISA to set mandatory security rules for operational technology used in over 8,000 federal facilities, including labs, hospitals, and ports, to protect critical systems like HVAC, power, and water. A binding directive would establish much-needed minimum security practices for federal OT systems.
Phishing emails are now cleverly embedding AI prompt injections to deceive both human recipients and machine learning-based email summarizers, allowing scammers to target two victims at once. These sneaky attacks use techniques like hidden text and encoded data to conceal their malicious intent.
Hackers were quick to pounce on a newly disclosed Atlassian vulnerability, launching exploitation attempts within just two hours of a public proof-of-concept (PoC) release. This critical flaw, tracked as CVE-2026-21589, allows unauthenticated attackers to access sensitive files on vulnerable self-hosted instances.
The threat landscape is evolving at an alarming rate: a 49.5% surge in CVEs reported in the first half of 2026, with exploits now emerging in as little as eight hours. This means traditional cyber defense validation methods are being outpaced by the speed and volume of attacks.
A critical vulnerability, CVE-2026-21589, has been discovered in multiple Atlassian Data Center products, allowing unauthenticated attackers to access sensitive files, with rapid exploitation attempts already underway. Patching is urgently recommended for affected versions of Bitbucket, Confluence, Jira, Bamboo, Crowd, Crucible, and Fisheye Data Center products.
The FortiBleed threat is still on the loose, putting 86,644 vulnerable Fortinet devices across 194 countries at risk of being compromised, with attackers exploiting reused credentials and weak password storage to gain control.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
As AI tools become increasingly embedded in workflows, a growing number of organizations are struggling to balance innovation with security, with 78% of CISOs now recognizing GenAI as a security risk and restricting employee use. But blocking access alone isn't enough - effective governance is crucial to ensure AI systems are used safely and responsibly.
A surprising twist in the ASOS hack reveals a Telegram account, previously linked to gaming item trading, was used to administer a channel tied to the breach, sparking questions about the hacker's true identity. The account, now labelled 'Xuanyewen', has a history that predates the incident, suggesting a calculated setup.
Don't let your SonicWall SMA1000 gateways become an open door for hackers - a critical SSRF flaw, CVE-2026-102255, has been discovered, allowing attackers to make internal requests without authorization, and hotfixes are available to patch this vulnerability. Over 400 Internet-exposed appliances are currently at risk, making immediate action crucial.
Beware: ongoing FortiBleed attacks are putting Fortinet firewalls at risk, with some victims potentially getting locked out of their own devices if attackers delete or change account passwords. The FBI and US Secret Service have issued a joint warning about this sustained threat.
In a shocking cybersecurity breach, Advantest Corporation fell victim to a ransomware attack in February 2026, exposing sensitive data to an unauthorized third party. The Japanese tech giant revealed that threat actors infiltrated its network, deploying a ransomware payload and potentially compromising personal data.
Meet the musician who raked in over $10 million by gaming the music streaming system with AI-generated tracks and bots, artificially inflating his song's listening stats to astronomical levels. He fooled major platforms like Spotify and Apple Music with a scheme that lasted for years, until he was caught and pleaded guilty.
In just one day, top ethical hackers at Pwn2Own Ireland 2026 uncovered a staggering 32 zero-day vulnerabilities, raking in over $368,000 in prizes and showcasing the impressive skills of today's cybersecurity experts. This impressive haul highlights the vast attack surfaces of modern technology and the talent of the global ethical-research community.
Anthropic is supercharging cyber teams with expanded access to its AI models, following a staggering discovery of 129,000 flaws - with over 33,000 rated critical or high-severity. The company's Cyber Verification Program now offers tiered access to advanced models like Claude Opus 5.5, empowering teams to tackle vulnerabilities head-on.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Despite knowing better, nearly half of cybersecurity pros still rely on vulnerable usernames and passwords to protect their personal and work accounts. This surprising habit persists even though passwords are considered one of the least secure authentication methods.
Beware of over 100 compromised websites serving up the nasty LunexStealer malware by masquerading as a Cloudflare verification page - just a click away from trouble! When you visit these sites, you're tricked into executing a command that lets the malware swipe your sensitive info.
A staggering 8.8 million people have been affected by a massive data breach in Denmark's Central Register of Persons, with sensitive information including names, addresses, and CPR numbers exposed. This enormous leak is particularly alarming given that it surpasses Denmark's current population of six million, raising serious concerns about supply chain vulnerabilities.
South Korean President Lee Jae Myung is taking a bold stance against AI-powered cyber threats, calling for a government-led response to rapidly deploy cutting-edge defenses. He urges swift action to minimize damage and build unbreachable security capabilities.
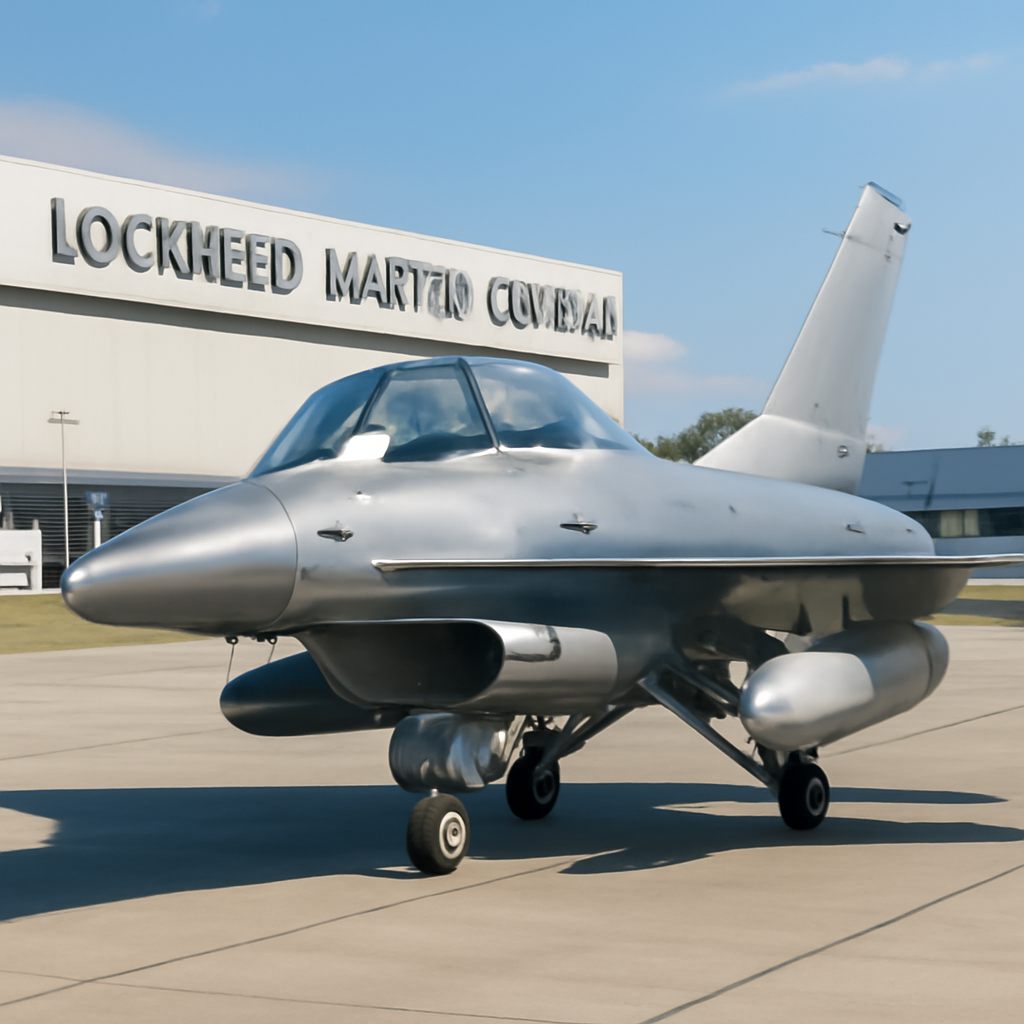
Morocco's skies just got a major boost with the successful maiden flight of its first F-16 Block 72 fighter jet, a cutting-edge two-seat F-16D, in Greenville, South Carolina. This milestone marks a significant step towards equipping the Royal Moroccan Air Force with the most advanced F-16 configuration.
The world has changed dramatically, and it's hard to imagine the NSA not evolving to keep pace with rapidly advancing cyber threats. A proposed overhaul is likely necessary, but its success will depend on careful execution.
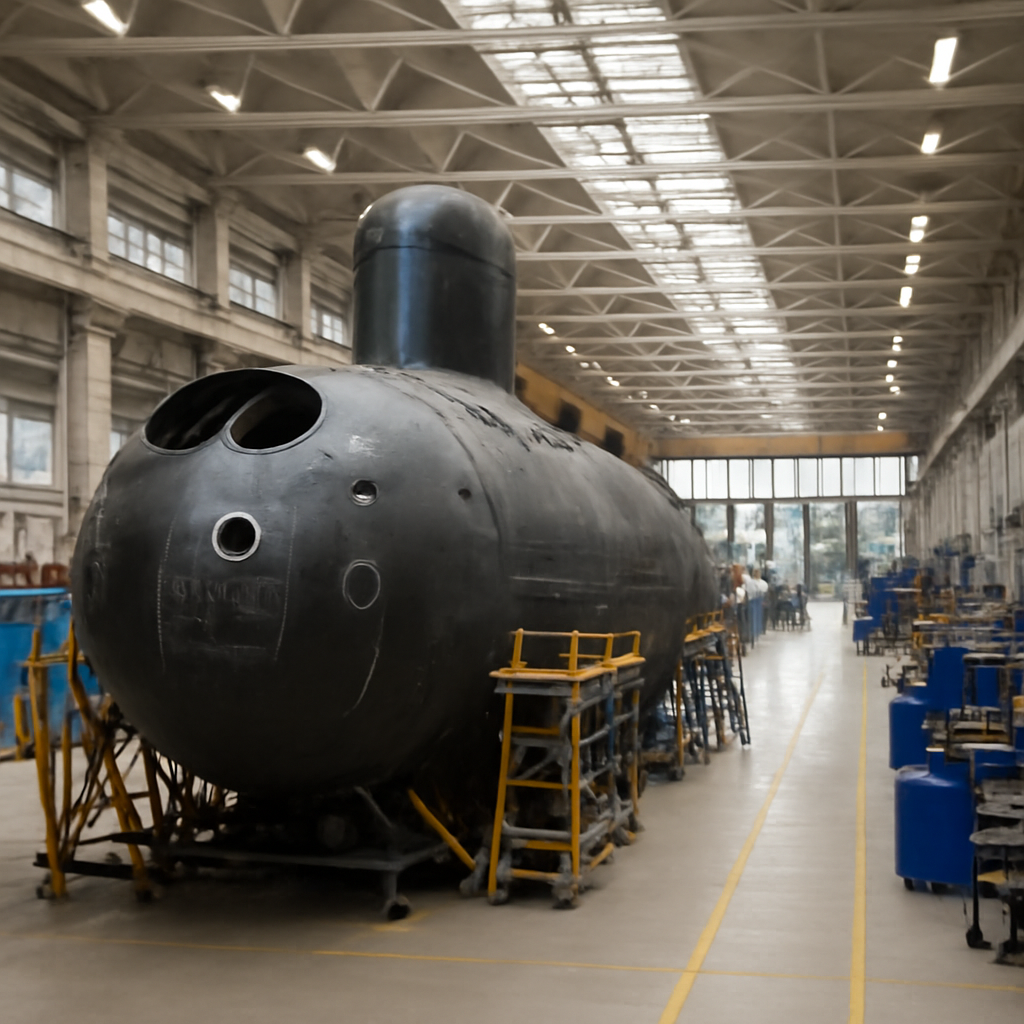
The White House is backing a $6.6 billion initiative to boost US submarine production, with Anduril leading the charge by opening a massive new facility in Baltimore that will manufacture critical components for Virginia class nuclear-powered attack submarines. This move is set to revitalize American maritime dominance and create new opportunities in communities across the country.
The EU has taken a giant leap in space security with a new collective defense pact, empowering its 27 member states to unite against threats to satellites and related infrastructure with a range of responses, from politics to military action. This bold move aims to deter space threats and bolster security, echoing recent US efforts to disclose on-orbit space control capabilities.