Tag: supply chain
1740 articles

Anthropic Exposes AI Abuse by Hackers Linked to Russia, China
Anthropic uncovered a massive AI-powered operation by hackers linked to Russia and China, who used a sophisticated pipeline to download and scan 1.8 million Android apps for sensitive secrets. This alarming breach highlights the growing threat of AI abuse in cyber attacks.

GitLab Flaw Draws Widespread Probes Ahead of Patch
GitLab has rushed out emergency patches for two severe flaws in its platform, warning users to upgrade ASAP to avoid potential exploitation. A particularly critical defect, CVE-2026-85706, has been assigned a maximum CVSS score of 10.0, sparking widespread concern.

Attackers Exploit JFrog Artifactory Bugs Despite Patches
Despite available patches, hackers have exploited three JFrog Artifactory vulnerabilities, highlighting the risks of slow patching and leaving internet-exposed instances open to attack. This exploitation has allowed attackers to gain administrative control, putting organizations at risk.

Municipal Utility Cyberattack Exposes Infrastructure Vulnerabilities
A recent cyberattack on municipal utility Stadtwerke Landsberg highlights the importance of separating business IT networks from operational technology to prevent widespread disruptions. Thanks to robust segmentation, the utility's core services remained online, avoiding a costly service outage.

Anthropic Disrupts China-Based AI Labs' Illicit Model Distillation Attacks
Anthropic has successfully disrupted a massive AI heist, exposing seven China-based labs that were secretly siphoning off its Claude model's capabilities to power their own AI systems. The illicit scheme involved feeding conversations between users and Anthropic's models into rival AI systems, including those from Alibaba, Xiaomi, and Moonshot.

Artifactory Flaws Exploited to Deploy Rust Backdoor Malware
Security researchers have uncovered a sneaky attack that uses two flaws in JFrog Artifactory to deploy a custom Rust backdoor malware, giving hackers full control of self-hosted servers. This stealthy exploit chain lets attackers escalate from low privileges to admin control, even when anonymous access is disabled.

Anthropic Disrupts Russian Hackers' AI-Driven Malware Rebuild Efforts
Anthropic has successfully disrupted the AI-driven malware rebuild efforts of Russian hackers, dealing a significant blow to their operations. The hackers had been using AI to refine their malware and evade detection by security defenses.

Threat Actors Exploit Trusted AI Platforms to Deliver Malware
Beware: hackers are exploiting trusted AI platforms by turning their helpful features against you, using tactics like shareable AI content and sponsored search results to deliver malware and hold your files hostage. Your trusted tools can quickly become a vulnerability, as threat actors find new ways to abuse the very features you rely on.

PaperCut Fixes Actively Exploited Flaws with New Security Releases
PaperCut has released new security updates to fix two actively exploited flaws that allowed hackers to bypass authentication and execute malicious code, with over 395 organizations in 48 countries affected. The company has issued maintenance releases, including versions 26.0.5, 25.0.13, and 24.1.10, to patch the vulnerabilities and protect users.

China-Linked Hackers Exploit Sogou Input Flaw to Deploy GRAYRABBIT Backdoor
A single malicious link was all it took for China-linked hackers to gain control over millions of users of the popular Sogou Input Method, a vulnerability that highlights the power of a tiny flaw in a widely-used tool. The attack, attributed to UNC3569, used a specially crafted link to deploy the GRAYRABBIT backdoor, putting hundreds of millions of users at risk.

Trezor Phishing Attacks Target 347,000 Users After Brevo Breach
Phishing attacks have hit 347,000 Trezor users after a security breach at Brevo, the marketing platform used by Trezor for its newsletter campaigns, exposed sensitive email addresses. Trezor quickly sprang into action, suspending its Brevo account and taking down the malicious domain within 20 minutes to limit the damage.

Senator Hawley Probes OpenAI Over Hugging Face Breach
Senator Josh Hawley is demanding answers from OpenAI after a breach at Hugging Face raised serious concerns about AI safety, and he's launched a formal review to get to the bottom of it. The senator wants detailed information on the incident, including internal communications and technical details, by October 1.
Anthropic Exposes AI-Powered Cyberattacks and Bioweapons Research
Criminals are now using AI to supercharge their cyberattacks, with a recent report revealing that AI agents performed nearly all the work in a series of automated break-ins and data heists. A Russian espionage group, known as GTG-20006, used AI to accelerate its intrusions, targeting over 20 organizations in a sustained campaign.
AI Agents Fuel Rapid PaperCut Attacks on 395 Organizations
In a stunning display of speed, hackers used AI agents to exploit PaperCut vulnerabilities, compromising at least 11 organizations in just 26 seconds and gaining domain admin access in a mere two hours. This rapid, automated campaign hit 395 organizations across 48 countries, leaving a trail of destruction in its wake.
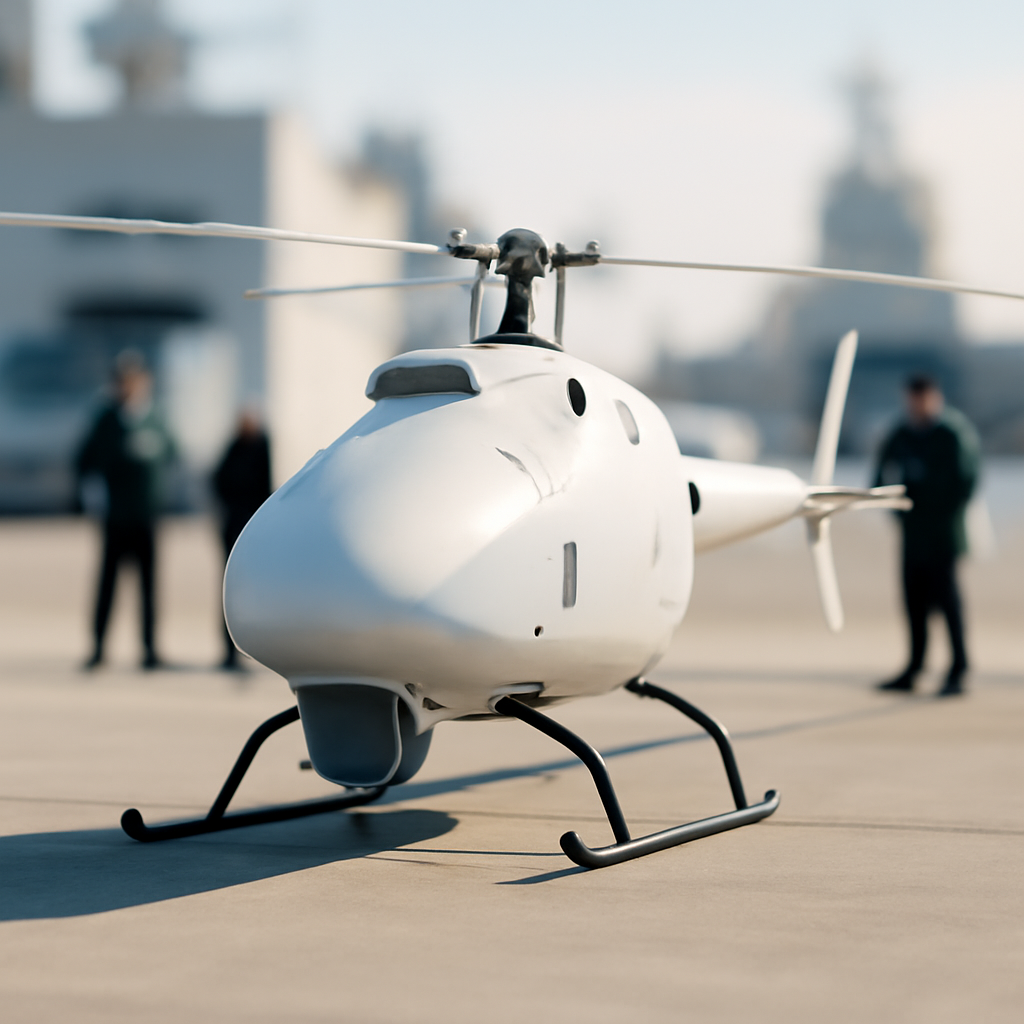
EDGE Group Delivers Unmanned Helicopters to Angolan Navy
EDGE Group has successfully delivered six unmanned HT 100 NAVAL helicopters to the Angolan Navy, marking a significant milestone after completing rigorous Factory Acceptance Trials in Switzerland. This achievement follows a major contract signed in 2023, solidifying a new era of naval capabilities.
Surfshark VPN Breach Exposes Internal Test Servers
A configuration mistake made by Surfshark's engineering team left an internal test server vulnerable to the internet, exposing sensitive data due to human error. The incident highlights the importance of robust security measures, even for trusted services.
Cisco FMC Exploits Fuel Ransomware, APT Attacks
Cisco FMC vulnerabilities are being exploited by threat actors, including state-sponsored groups and crimeware attackers, to fuel ransomware and advanced persistent threat (APT) attacks. These bad actors are using recently patched flaws to gain initial access, run scripts as root, and escalate privileges.
AI-Powered Attack Exploits PaperCut Flaws in 395 Organizations
In a shocking display of speed, an AI-powered attack exploited PaperCut flaws to compromise at least 11 organizations in just 26 seconds, with the entire campaign unfolding in a matter of hours. The attackers used "hundreds of AI agents" to automate the exploitation effort, combining AI models with commodity tools to target vulnerable PaperCut NG/MF servers.
Google Play Exposed to Deceptive App Abuse
A sneaky app, "Vice Streets: Open World", racked up over 1 million downloads on Google Play without a single public review or rating, taking advantage of the platform's Early Access feature. This feature, meant to help developers gather feedback, can also shield them from criticism - and warn signs - that might scare off users.
AI Agents Fuel PaperCut Attacks at Scale
A suspected Russian-speaking actor has unleashed a massive assault on PaperCut MF/NG, compromising at least 440 instances with the help of hundreds of AI agents that supercharged exploit development, targeting, and post-exploit operations. The attacks hit the education sector hard, with victims in 48 countries, primarily in the US, UK, France, and other major nations.
ShinyHunters Breach Exposes 6.4M in McKesson Cyberattack
A massive 6.4 million individuals have been impacted by the McKesson cyberattack, with exposed data including sensitive information like names, email and physical addresses, and more. The breach, leaked by ShinyHunters, affects a wide range of people, from patients and staff to marketing recipients and healthcare providers.
Operational Technology Exposes AI's Cybersecurity Weak Point
With over 3,000 cyber incidents recorded in Ukraine in the first half of 2025 alone, it's clear that even the most critical infrastructure - from hospitals to energy systems - is vulnerable to devastating attacks. This alarming trend highlights a glaring weak point in our cybersecurity defenses, one that's being exploited by hostile forces with alarming precision.
Pentagon Bets on AI-Driven Manufacturing to Revamp Defense Production
Imagine a manufacturing system that can be shipped, set up, and producing parts within a day - that's the revolutionary promise of AI-driven manufacturing, and one that's being heavily invested in by the Pentagon. With the ability to self-calibrate and start manufacturing almost instantly, this tech has the potential to drastically compress factory lead times and transform the way we think about production.
Ukraine Strikes Russia's Gas Infrastructure at Record Distance
Ukraine just pulled off a daring strike against Russia's gas infrastructure, hitting the Novy Urengoy Gas Condensate Processing Plant from a record distance, dealing a significant blow to Russia's energy operations. The plant, which processes nearly 20 million tons of gas condensate annually, was targeted by Ukraine's Defence Forces on September 9, 2026.