Tag: supply chain
1740 articles
Trezor Users Targeted in Phishing Attacks After Email Breach
Beware of a phishing scam targeting Trezor users: a fake "Critical Security Alert" email is circulating, claiming to be from Trezor but is actually an attempt to steal your info. Don't click on any links - Trezor has confirmed it's a scam and is investigating.
China-linked groups exploit BlueMoon kit to breach US and Southeast Asia targets
China-linked groups are leveraging the BlueMoon exploit kit to launch targeted attacks on organizations in the US and Southeast Asia, with a surprisingly small number of groups behind a large-scale intrusion campaign that quickly evolved from testing to widespread reuse. Fewer than 20 organizations globally were hit, but experts warn the actual number is likely much higher.
AdaptHealth Breach Exposes 4.1 Million Patients' Data
A massive data breach at AdaptHealth has put the personal information of 4.1 million patients at risk after hackers compromised the company's systems in June and demanded a ransom. The breach was first disclosed in a July SEC filing, and it's been confirmed that the ShinyHunters threat group was behind the attack.
Skullcandy Earbuds Expose Users to Bluetooth Hijacking Risk
Thousands of Skullcandy earbud owners may be vulnerable to Bluetooth hijacking due to a high-severity flaw in the Airoha Bluetooth Audio SDK - leaving them with a tough decision: risk compromised hardware or toss their earbuds.
Pentagon Expands AI-Powered Maven System Across Operations
The Pentagon is supercharging its decision-making with the AI-powered Maven Smart System, which is being expanded across operations to help officials make faster, data-driven decisions. What started as a tool to connect intelligence and operations is now being used to analyze logistics, supply chain, and budgeting data, and more.
Lawmakers Urge Treasury to Target Indian Hack-for-Hire Groups
US lawmakers are calling on the Treasury Department to take action against Indian hack-for-hire groups that have been targeting American citizens and businesses for over 15 years. By adding these firms to the Entity List, they aim to restrict their access to US software, tools, and infrastructure.
AI-Powered Attacks Target ID Databases
A staggering 153 million driver's licenses are now being sold on the dark web, highlighting the alarming vulnerability of our personal ID information. This massive breach is a wake-up call to rethink how we collect, store, and protect sensitive documents in the age of AI-powered attacks.
Veradigm Breach Exposes Patient Data After Third-Party Hack
Veradigm is alerting patients to a data breach caused by a third-party hack, which exposed sensitive patient information after a malicious actor stole credentials and accessed API environments. The breach, linked to a busy ransomware operation, has not disrupted Veradigm's operations.
Cybercrime Group Exposes Massive PPI Marketplace
Meet CL-CRI-1171, a notorious cybercrime group that's been secretly operating a massive pay-per-install marketplace for over two years, infecting countless devices with a sneaky trojanized installer called OfferLoader. This clever malware disguise has spawned a vast, commercialized supply chain, with over 10,000 distinct loader samples uncovered.
Microsoft Floods Patch Pipeline with 974 Security Fixes
Microsoft just dropped a massive patch bundle, fixing a record-breaking 974 security holes in one fell swoop - more than doubling its previous year's total with three months still to go. This huge update eclipses the company's previous record of 570 vulnerabilities set just two months ago.
Veradigm Breach Exposes Patient Data After Ransomware Attack
A recent ransomware attack on one of Veradigm's third-party vendors has led to a data breach, exposing sensitive patient information - but fortunately, the incident was contained and didn't disrupt the company's operations. Veradigm has already launched a response and notified law enforcement.
Pakistan's Defence Procurement Spreads Across 40 Channels
Imagine having to scour 40 different portals to stay on top of defence procurement opportunities in Pakistan - that's the daunting task facing vendors today. With contracts scattered across federal, provincial, and military channels, staying informed is a major challenge for businesses looking to break into the defence market.
Alby Hub Flaw Exposes Internet-Facing Bitcoin Wallets to Takeover Risk
A critical flaw in Alby Hub, a self-hosted Lightning wallet, has been discovered, putting internet-facing Bitcoin wallets at risk of takeover and fund loss, with one user already affected. To avoid vulnerability, users are urged to update to version 1.24.0 or later.
Microsoft Unveils Record 974 CVE Fixes in September Patch Tuesday Release
This September Patch Tuesday release is a doozy, with a record 974 CVEs fixed - a staggering number that more than doubles the previous record and demands immediate attention from IT and security teams. The challenge is clear: prioritize and patch with lightning speed to stay ahead of potential threats.
Trump Targets Bombardier Jets In Trade Dispute
President Donald Trump fired a fresh warning shot across Bombardier's bow, declaring on his Truth Social platform that the US should no longer sell the Canadian company's jets. This bold statement revives a contentious trade dispute that could impact US military aerial surveillance plans.
MBDA Expands Presence in Poland with New Industrial Facility
MBDA is bolstering its presence in Poland with a brand-new industrial facility in Czosnow, creating exciting job opportunities for local talent, including engineers, to work on pioneering European defense technology. The state-of-the-art center will serve as a hub for innovation, collaboration, and growth, further solidifying MBDA's partnership with Poland.
Australia's Mining Sector Targets Electrification Push to Curb Diesel Reliance
Australia's mining sector is on a mission to ditch diesel and go electric, driven by a pressing need to reduce its staggering 32 million litres-per-day fuel consumption - and a sobering wake-up call from the Iran crisis that left the industry vulnerable to soaring diesel prices.
EU Cyber Resilience Act Spurs Rush to Track Software Vulnerabilities
Get ready for a new era of cyber transparency: by September 11, 2026, EU manufacturers with digital products must report vulnerabilities to ENISA within 24 hours of discovery, and provide a detailed report within 72 hours. This mandate is just the beginning, with stricter engineering requirements kicking in on December 11, 2027.
Hackers Deploy Linux Rootkit via F5 BIG-IP Flaw
Hackers are exploiting a critical F5 BIG-IP flaw, known as CVE-2025-53521, to deploy a sneaky Linux rootkit that allows them to execute code on vulnerable servers. This alarming attack vector has already exposed 795 endpoints online, putting countless systems at risk.
Data Breaches Expose Vulnerable Supply Chains
Recent data breaches at the Pokémon Center, McKesson, and other major players in freight, retail, airports, finance, and healthcare reveal a disturbing trend: third-party vulnerabilities and social engineering are leaving supply chains exposed. A staggering 284 million records were allegedly stolen, highlighting the urgent need for stronger security measures.
Boston Scientific Revises Outlook as Cyberattack Disrupts Operations
Boston Scientific's operations have been significantly disrupted by a cyberattack, forcing the company to revise its financial outlook and warning investors of a potential material impact on its third-quarter and full-year results. The incident, detected on August 25, has left the company's net sales growth and earnings guidance in jeopardy.
Threat Actors Exploit AI for Large-Scale Credential Harvesting
Threat actors are supercharging their attacks with AI, using it to scale up credential harvesting and launch more sophisticated campaigns. Google Threat Intelligence Group reports that financially motivated and espionage-focused attackers are increasingly turning to AI to target high-value sectors like healthcare, government, and media.
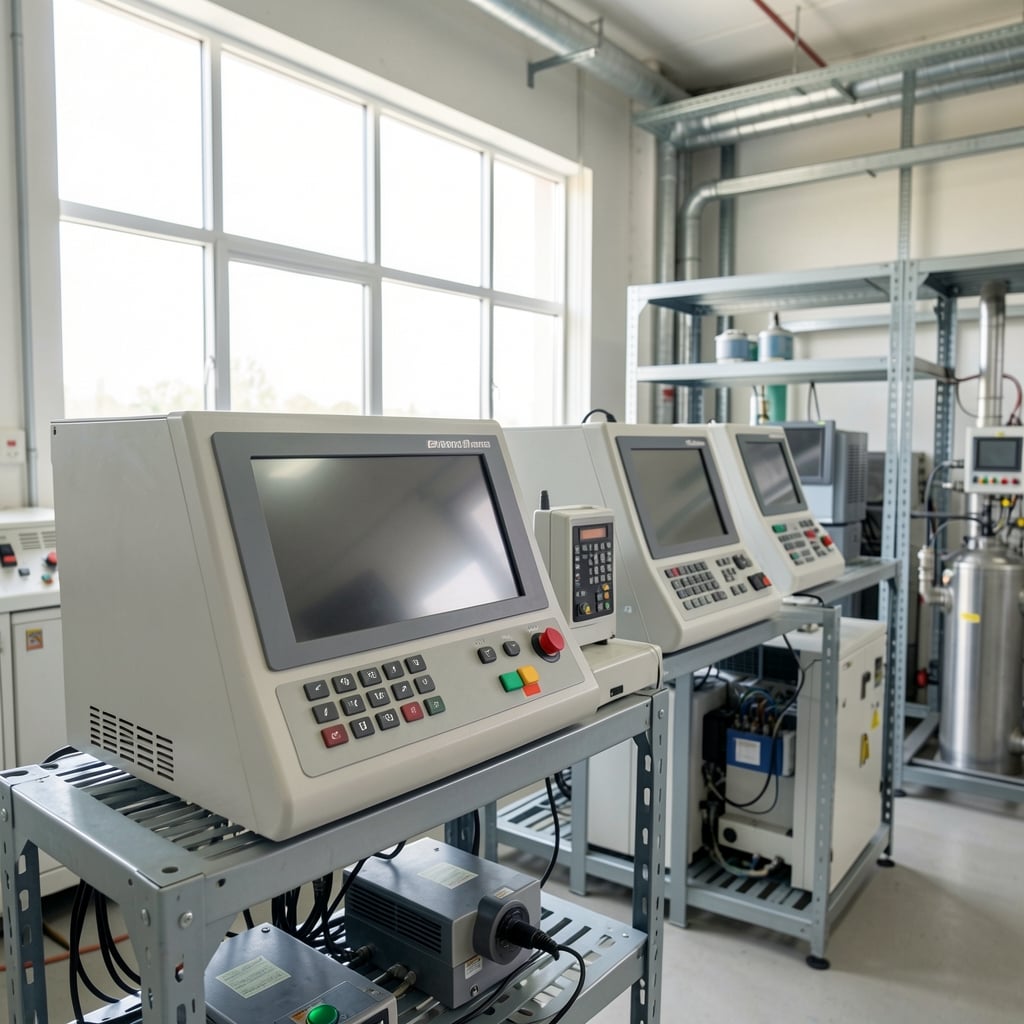
Utilities Face Unseen Network Threats
The water and wastewater sector is under attack, with over 100 compromised systems identified in July alone, often due to vulnerable controllers linked directly to cellular modems. This alarming trend has prompted joint warnings from CISA, the FBI, and the EPA, highlighting the urgent need for utilities to bolster their network defenses.
CISA Slashes Cybersecurity Resources for Critical Infrastructure
Big news: CISA is cutting back on free cybersecurity resources for critical infrastructure operators, leaving many in the security community scrambling to adapt. Recently touted as a go-to solution, these now-retired tools included Cyber Resilience Reviews and Ransomware Readiness Assessments.