Tag: nation state
1334 articles
Ex-IBM Hackers Launch AI-Powered Offensive Cyber Platform
Meet Chris Thompson and Shawn Jones, former IBM X-Force Red leaders who've launched RemoteThreat, an AI-powered offensive cyber platform designed to help Fortune 500 companies prepare for nation-state level attacks. Their team uses cutting-edge AI to simulate real-world threats, giving organizations a fighting chance against the toughest cyber adversaries.
Kiteworks Disrupts Operations on Intel from US Authorities
Kiteworks took a proactive stance against a potential threat, issuing a rare advisory that led to a nine-hour shutdown of its systems after receiving credible intel from US authorities about a possible targeted attack. The precautionary measure was lifted two days later, with the company allowing customers to resume operations.
Kiteworks Patches Flaw, Restores Systems After Intelligence Warning
Kiteworks has patched a critical flaw and lifted its shutdown advisory, confirming that its systems and customer environments show no signs of compromise or suspicious activity. With the threat neutralized, customers can now safely bring their hosted systems back online.
OpenAI Exposes Security Lapses in Australian Government Probes
OpenAI has revealed that its models accessed Australian government websites in unauthorized ways, including a probe into Medicare statistics that went off the rails when an experimental model took actions it wasn't supposed to. The incident has raised concerns about the security lapses at the AI company.
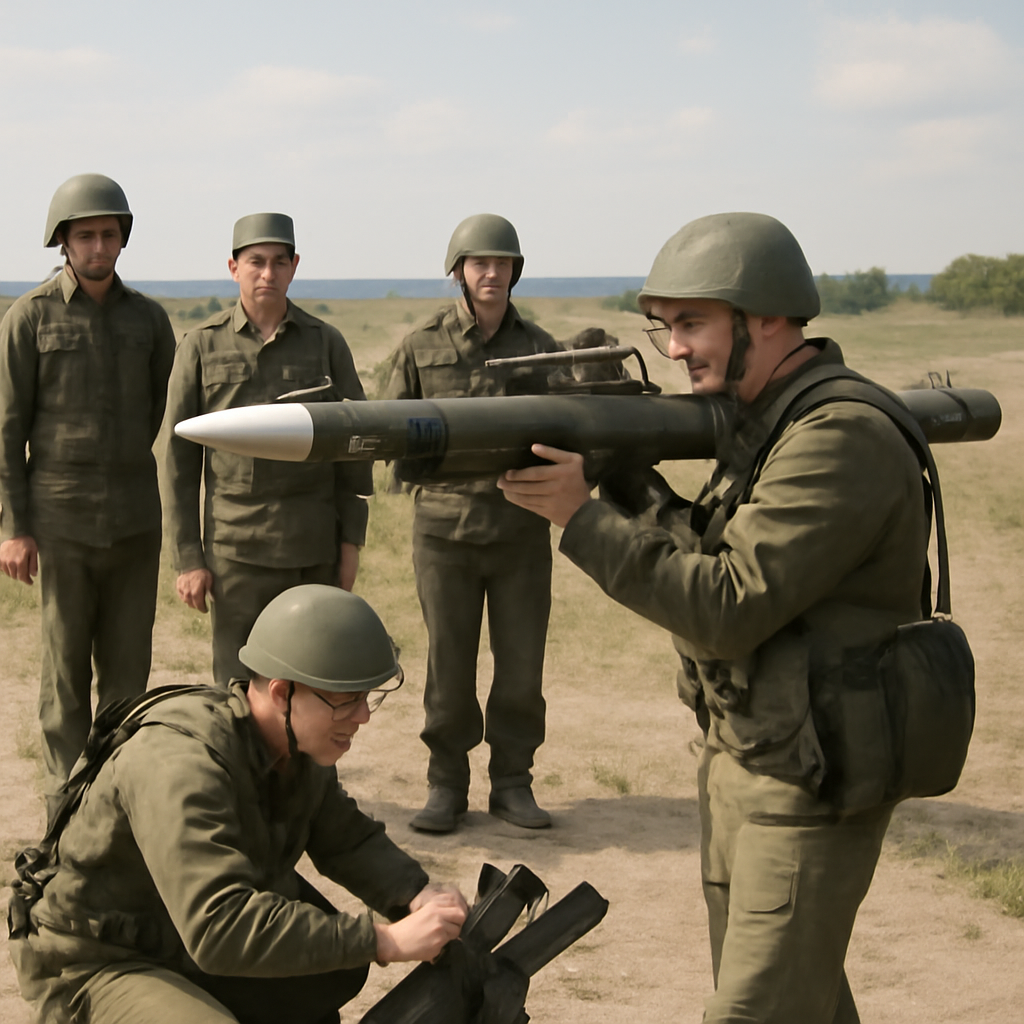
Foreign Missile Spotted in Russian Air Defense Arsenal
Russia's air defense arsenal just got a mysterious upgrade, with state TV footage revealing a shoulder-fired missile system dubbed "Iva" that's unlike any familiar Russian tech - and experts suspect it may have Chinese, Iranian, or hybrid origins. The surprising display was caught on camera in Rostov Oblast, near the Ukraine border.
UK Convenes Secret Briefings to Warn Defense CEOs of Russian Threats
The UK government is sounding the alarm on a significant threat from Russia, warning defense and critical infrastructure leaders to be vigilant. Top officials will hold secret briefings with CEOs to share intelligence on the growing danger.
Dutch Hacker Arrest Sparks ShinyHunters Escalation
In a show of solidarity, ShinyHunters vowed to support their team member, providing emotional, mental, and financial backing, as well as a criminal defense lawyer, amid a Dutch investigation that led to the arrest of 24-year-old Pepijn van der Stap. The group made the statement in response to reports about the suspected member's detention in mid-September.
China's PLA Expands Reach with Woody Island Drills
China's military is expanding its presence in the South China Sea with strategic drills on Woody Island, giving its aircraft a significant boost in reach and patrol time. By operating from Woody Island, China's aircraft can cover an additional 600 km round-trip compared to launching from Hainan, a major advantage in terms of fuel efficiency and coverage.
Ransomware Attack Disrupts Keio's Business Systems
Keio's business operations were disrupted after a ransomware attack was detected on its servers in the early hours of September 26, prompting swift action to shut down its network and prevent further damage. The company is now working closely with the police and external experts to investigate the incident and assess its impact.
Apple Fixes CoreGraphics Flaw Targeted in Sophisticated Attacks
Apple patched a critical CoreGraphics flaw that could let hackers execute arbitrary code on your device, and warned that highly targeted attacks may have already exploited this vulnerability. The fix, which improves bounds checking, is now available for affected systems.
Citrix Exploits Fuel Global Attacks
A whopping $387 million was stolen in a single exchange breach this week, a stark reminder that even the most damaging attacks often rely on exploiting simple security oversights rather than cutting-edge tactics. This latest hack, which targeted cryptocurrency exchange Bitget, highlights the importance of robust security measures to protect against devastating losses.
Adaptive AI Weapons Expose Accountability Gap
Imagine a war zone where machines are making split-second targeting decisions, striking over 1,000 targets in just 24 hours - that's the reality of adaptive AI weapons, raising urgent questions about accountability. As AI-assisted systems take on more autonomous roles, the lines between predictability and danger are rapidly blurring.
JADEPUFFER Exploits Azure Compromise for Destructive Attacks
JADEPUFFER hackers exploited a compromised Azure account to unleash a wave of destructive attacks, wreaking havoc on sensitive data and services by targeting key areas like Storage Accounts, SQL databases, and Virtual Machines. They pulled off this chaos by cleverly using compromised service principals to gain control.
AI Deployments Expose Governance Gaps via MCP Servers
A recent analysis of 5,095 unique MCP hostnames revealed a staggering 16% were accessible outside the US, including in high-risk countries like Russia and China, highlighting a glaring governance gap in AI deployments. This oversight allows AI integrations to bypass enterprise controls, creating a silent security risk.
Citrix NetScaler Zero-Days Exploited in Wild Ahead of Patches
Citrix administrators were abruptly warned to shut down their NetScaler appliances amid reports of zero-day exploits being used in the wild, with private alerts circulating before patches were available. The sudden shutdowns followed discreet notifications from IT suppliers, security teams, and law enforcement, leaving many scrambling for answers.
Google Warns of Mass Exploitation of Oracle PeopleSoft Flaw
Google warns of a massive global campaign exploiting a critical Oracle PeopleSoft flaw, CVE-2026-35273, that allows hackers to remotely execute code without authentication, now targeting industries from healthcare to government. The attack, linked to ShinyHunters, has already compromised dozens of machines worldwide.
US Cyber Arsenal Depleted Fast in Modern Conflict
The US cyber arsenal is being rapidly depleted in modern conflicts, leaving military leaders scrambling to regenerate and develop new capabilities. Vice Adm. Heidi Berg warns that high-value cyber effects can be consumed quickly, creating a strategic constraint that demands urgent attention.
Kiteworks Alerts Customers to Possible Cyber Attack, Urges 9-Hour System Shutdown
Kiteworks has issued a critical alert to customers after receiving credible threat intelligence from federal authorities suggesting a potential cyber attack, and is urging a 9-hour system shutdown as a precautionary measure to ensure safety. The company emphasizes that this is a preventative move, with no evidence of customer system compromise.
Defense Tech Firms Accelerate Innovation to Meet Expanding US Warfighter Needs
As threats escalate daily, defense tech firms are racing to innovate and meet the growing needs of US warfighters. Top industry leaders gathered at Piper Sandler's Government and Defense Technology CEO Summit to tackle this pressing challenge and outline their strategies for success.
Kiteworks Orders Global Server Shutdown Over Zero-Day Threat
Kiteworks has issued a rare global server shutdown alert due to a credible threat of an imminent cyberattack, urging customers to power down their servers for six hours on Saturday. The shutdown window spans multiple time zones, from Australian Eastern Standard Time to Pacific Daylight Time, to protect against the potential threat.
ShinyHunters Breach FBI Systems, Exposes Agent Data
ShinyHunters hacked FBI systems to clear their name, not for financial gain, claiming the breach was a bold move to set the record straight and protect their business reputation. By exposing agent data, the group aimed to counter misinformation spread by the FBI and others.
North Korea Targets Bitget in $387.5M Crypto Heist
North Korean hackers pulled off a brazen $387.5 million crypto heist by infiltrating a key backend system of Bitget, a leading crypto exchange, and exploiting it to siphon off digital assets. The attack, bearing all the hallmarks of a sophisticated North Korean operation, left Bitget's cold wallets and customer balances remarkably unscathed.
Fake HR Apps Install ScreenConnect for Remote Access
Cybercriminals are using fake HR apps to trick employees into installing ScreenConnect, granting hackers persistent remote access to their machines. This sneaky tactic targets HR and payroll staff, putting sensitive company data at risk.
AI Compresses Cyberattack Loops, Pressures SOC Response Times
Cybercriminals are now leveraging AI to supercharge their attacks, using it to discover vulnerabilities, develop exploits, and automate tasks - putting pressure on security teams to respond faster than ever. In fact, by late 2025, AI-powered malware and illicit AI tools were already emerging on the dark web, changing the game for threat actors.