Tag: nation state
1334 articles
China-linked group targets US AI policy experts with phishing campaign
A cunning phishing campaign impersonated top US AI policy voices, including a former White House science advisor and a renowned economist, to gain the trust of targeted experts. The attackers carefully crafted initial messages that seemed to invite recipients into an AI policy advisory committee or a report collaboration, slowly building a relationship before making their next move.
AI Executives Sign Accord Amid Rising Cybersecurity Concerns
In a landmark move, President Donald Trump and top AI executives from OpenAI, Anthropic, Google, Meta, Nvidia, and xAI have signed a voluntary safety accord, pledging to enact multiple layers of controls to tackle rising cybersecurity concerns. This non-binding agreement, described as "morally binding" and "almost like a constitution," aims to prioritize safety and security in AI development.
China-Aligned Spies Target AI Policy Experts in Sophisticated Phishing Campaigns
In a sophisticated phishing scam, a China-aligned group impersonated top US officials, including a former White House science advisor, to target AI policy experts in July 2026. The attackers used fake emails to trick their victims into divulging sensitive information.
AI Agents Expose New Cybersecurity Risks
As we enter a new era of cybersecurity, CISA warns that AI is supercharging hackers, allowing them to exploit vulnerabilities at lightning speed and putting our country and economy in the crosshairs. It's time for organizations to adapt to this new wave of faster, smarter threats.
MI5 Warns UK Academics of Unwitting Aid to Chinese Espionage Efforts
MI5 warns UK academics to be vigilant, as their research may be inadvertently aiding Chinese espionage efforts that threaten national security. The China General Technology Research Institute has been identified as a key player, using academic funding to boost China's Ministry of State Security's technical espionage capabilities.
China-Linked Hackers Impersonate AI Experts to Steal US Policy Insiders' Credentials
Beware of fake AI experts trying to trick US policy insiders into handing over their credentials - a China-linked hacker group, TA419, has been impersonating AI authorities to steal sensitive information since at least April 2025. Verify unexpected messages from supposed AI experts through another channel to stay safe.
OpenAI Disrupts AI Model Extraction Campaign Tied to Moonshot AI
OpenAI successfully foiled a large-scale attempt to illicitly extract sensitive information from its AI models, thwarting a sophisticated campaign that involved over 15,000 users and nearly 16,000 attempted requests. Fortunately, no sensitive data was compromised, thanks to robust security measures that prevented encryption breaches, database hacks, or unauthorized access to user conversations.
MI5 Warns Academics Over Unwitting Role in China's Espionage Plans
Beware: over 100 UK academics have unknowingly contributed to projects backed by a Chinese institute that's secretly boosting China's espionage capabilities. MI5 has sounded the alarm, warning researchers about the China General Technology Research Institute's true ties to China's Ministry of State Security.
Apple CoreGraphics Flaw Exposes Possible WhatsApp Delivery Path
A newly discovered Apple CoreGraphics flaw, potentially exploited in a highly targeted attack, now has a publicly available proof-of-concept that can crash unpatched iPhones and Macs. Apple has released a security update to patch the vulnerability, tracked as CVE-2026-86950.
Citrix NetScaler Exploits Create Superuser, Deploy Web Shells
A critical vulnerability in Citrix NetScaler ADC and Gateway appliances, rated 9.5 in severity, is being actively exploited by attackers, who can use it to run malicious commands and gain superuser access. This urgent threat prompted the Dutch National Cyber Security Centre to advise organizations to shut down their appliances until they're patched.
OpenAI Disrupts Chinese AI Firm's Encryption Bypass Tactic
OpenAI thwarted a clever attack by a Chinese AI firm that attempted to bypass encryption and extract sensitive data from its models. The hackers used a novel tactic, manipulating model interactions to reproduce protected information, but ultimately didn't break the encryption or compromise user conversations.
OpenAI Disrupts Chinese AI Firm's Model Distillation Campaign
OpenAI recently thwarted a massive AI model theft campaign by a Chinese firm, detecting a coordinated attack that attempted to replicate its protected models at scale. The campaign, which ran throughout July, involved over 15,000 users and 16,000 suspicious requests on its peak days.
Star Blizzard Deploys RedFlick Malware via Automated Phishing Attacks
Microsoft warns that Star Blizzard, a Russian state actor, has launched over 13 large-scale phishing campaigns this year, infecting over 100 US and UK organizations with the RedFlick malware. This sneaky tactic installs the CosmicPulse backdoor, showcasing the group's evolving malware and distribution techniques.
US Army Bolsters Counterdrone Efforts with $4 Billion in New Contracts
The US Army is taking a massive leap forward in its counterdrone efforts, issuing 10 new contracts worth up to $4.15 billion to help protect against unmanned aerial threats. These contracts are now open to all vendors, marking a significant surge in the Army's action against drone threats.
Australia's Sovereignty Debate Exposes Tensions Between Self-Reliance and Strategic Partnerships
Australia's quest for true sovereignty isn't about isolation, but about having the freedom to make real choices - and that's exactly what Deputy Secretary Hugh Jeffrey had in mind when he championed self-reliance as the key to unlocking national power.
Water Sector Grapples with Cyber Threats as Attacks Persist
The water sector is facing a harsh reality: cyber threats are on the rise, and threat actors are intensifying their attacks as global conflicts escalate. Recent attacks on water facilities have exposed glaring technical and organizational gaps that leave the sector vulnerable.
Kiteworks Resumes Operations After Heeding Federal Threat Intel
Kiteworks swiftly responded to credible threat intelligence from federal authorities by temporarily shutting down operations, a move that wasn't taken lightly, and is now safely back online. The precautionary measure was taken to protect customers from a potential imminent threat.
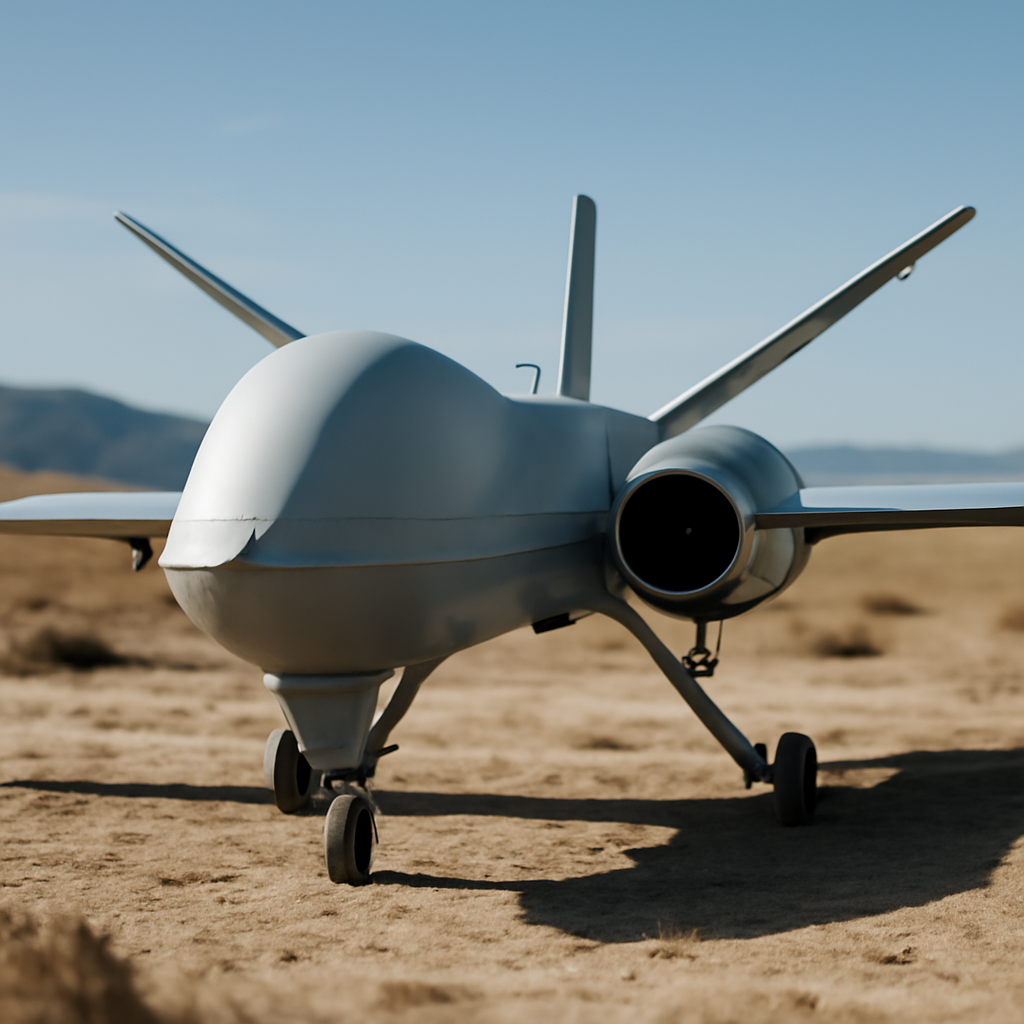
Russia's Jet-Powered Drones Target Ukraine with Increased Speed and Range
Meet the Geran-4, a turbocharged drone capable of screaming over Ukrainian skies at a mind-blowing 450-500 km/h - and sometimes even faster. This jet-powered beast marks a major upgrade from its predecessors, boasting a reinforced structure, improved aerodynamics, and a turbojet engine that packs a serious punch.
Microsoft Tracks Russian Hacker Group Star Blizzard's Global Phishing Expansion
Microsoft has uncovered a significant shift in the tactics of Russian hacker group Star Blizzard, which has begun conducting large-scale phishing campaigns in addition to its previous targeted spear-phishing operations. This new approach, observed in 2026, marks a major expansion of the group's phishing activities, with campaigns now sending tens to hundreds of automated emails.
Mandiant Exposes Citrix NetScaler Zero-Day Exploits by Suspected State Actors
Dozens of organizations across North America and Europe, spanning critical sectors like government, finance, and education, have been impacted by a massive cyberattack exploiting a zero-day vulnerability in Citrix NetScaler appliances. The stealthy campaign, suspected to be carried out by state actors, went undetected for at least three weeks, allowing attackers to compromise a wide range of industries.
Star Blizzard Exploits Fake Invites to Deploy Windows Backdoor
Over 100 organizations, primarily in the US and UK, have fallen prey to a sophisticated phishing scam that uses fake event invites to install a sneaky Windows backdoor, with Microsoft tracing the attacks back to a Russian hacking group. The campaign, which has been running in waves since January, appears to be targeting individuals and organizations with ties to Ukraine.
French Tax Authority Breach Exposes Data of 600,000 Taxpayers
A breach at the French tax authority exposed sensitive data of 600,000 taxpayers, including 350,000 individuals and 250,000 businesses, after a low-sophistication attack using stolen staff passwords. The hack, which went undetected for three months, highlights the vulnerability of simple login credentials.
Hackers Exploit Citrix Zero-Day to Deploy Web Shells, Malware
Hackers were quick to pounce on a Citrix zero-day vulnerability, attempting to install a hidden PHP web shell just days before the flaw was publicly disclosed. This early activity sparked a wider campaign, enabling attackers to gain root access, deploy malware, and tunnel into internal networks using the newly disclosed CVE-2026-88771 and CVE-2026-88772 vulnerabilities.
Microsoft Tracks NeedyMantis Malware Enabling Persistent Network Access
Microsoft uncovered a sneaky malware operation, dubbed NeedyMantis, that's been secretly giving hackers prolonged access to compromised networks since at least October 2025. This stealthy threat has been targeting key sectors like telecommunications, universities, and government-linked organizations, primarily in campaigns linked to China.