Tag: nation state
1342 articles
US Unveils Cyberattacks as Counterterrorism Tool
The US has officially added cyberattacks to its counterterrorism arsenal, vowing to use offensive cyber operations against those who plan to harm Americans or support terrorist plots. This bold move is part of a new strategy that combines diplomatic, financial, and covert actions to disrupt and deter threats to US interests.
Agentic AI Empowers Cyber Criminals with Nation-State Capabilities
The Department of Defense is leveraging agentic AI tools to revolutionize its operations, with Emil Michael reporting that tasks that once took two weeks can now be completed in just three hours, freeing up teams to focus on high-priority work. This game-changing tech has already shown tremendous success since its rollout on the GenAI.mil platform in December.
Australia's Security Architecture Needs Diversity to Counter Complex Threats
Australia's national security ecosystem is drowning in data, but struggling to cut through complexity - and simply adding more information can make things worse, not better. To stay ahead of evolving threats, its security architecture needs a fresh approach that prioritises what matters most.
Palo Alto Networks Zero-Day Exploited in Wild, Firm Warns
Palo Alto Networks has warned of a critical zero-day vulnerability, CVE-2026-0300, being exploited in the wild, allowing unauthenticated attackers to execute code with root privileges on certain firewalls. This flaw affects a limited number of customers with exposed User-ID Authentication Portals.
Iranian Spies Masquerade as Ransomware Gangs in Espionage Ops
A new wave of cyber threats has emerged, where Iranian spies masquerade as ransomware gangs to secretly infiltrate and gather intel from targeted organizations. Behind the scenes, they're hiding a wide-open backdoor, putting defenders and the organizations they protect at risk.
MuddyWater Exploits Microsoft Teams in False Flag Ransomware Attacks
MuddyWater hackers are impersonating Chaos ransomware affiliates, using clever social engineering tactics via Microsoft Teams to steal credentials and gain access to sensitive systems. Their sophisticated campaign involves interactive screen-sharing and manipulation of multi-factor authentication.
OceanLotus Exploits PyPI to Deliver ZiChatBot Malware
Kaspersky's analysis uncovered a sneaky malware attack on PyPI, where OceanLotus hackers uploaded fake packages that looked like harmless libraries, tricking users into installing the ZiChatBot malware. The malicious packages, uploaded in July 2025, masqueraded as legitimate tools like uuid32-utils, colorinal, and termncolor.
CISA Launches Framework to Fortify Critical Infrastructure Against Cyber-Attacks
The US Cybersecurity and Infrastructure Security Agency (CISA) has launched CI Fortify, a vital planning framework designed to shield critical infrastructure sectors like water, energy, and transportation from devastating cyber-attacks. This timely guidance helps organizations safeguard their networks and essential services from threat actors seeking to disrupt and degrade infrastructure.

Iran-Linked APT Exploits Ransomware Disguise for Espionage
MuddyWater, an Iran-linked APT group, has been caught exploiting a ransomware disguise to secretly infiltrate systems, using interactive tactics to harvest credentials and gain internal access. By masquerading as a Chaos ransomware affiliate, the group aimed to throw off detectives and cover its espionage tracks.
MuddyWater hackers exploit Chaos ransomware as cyber-espionage decoy
MuddyWater hackers have cleverly used Chaos ransomware as a decoy to mask their true intentions - and it's not about making a quick buck. Instead, their tactics suggest a more sinister goal, blurring the lines between state-sponsored espionage and cybercrime.
CloudZ RAT Exploits Windows Phone Link for Credential Theft
Cyber attackers have cleverly exploited the Microsoft Phone Link feature to steal sensitive credentials and one-time passwords, all without needing to infect mobile devices with malware. By targeting this built-in Windows application, hackers can access synced phone data and extract valuable information.
Palo Alto Networks Firewalls Targeted in Zero-Day Exploits
Palo Alto Networks firewalls are under attack by zero-day exploits targeting a vulnerability in the User-ID Authentication Portal, allowing hackers to execute malicious code with root privileges. This buffer overflow flaw, tracked as CVE-2026-0300, poses a significant risk to organizations with Internet-exposed firewalls.
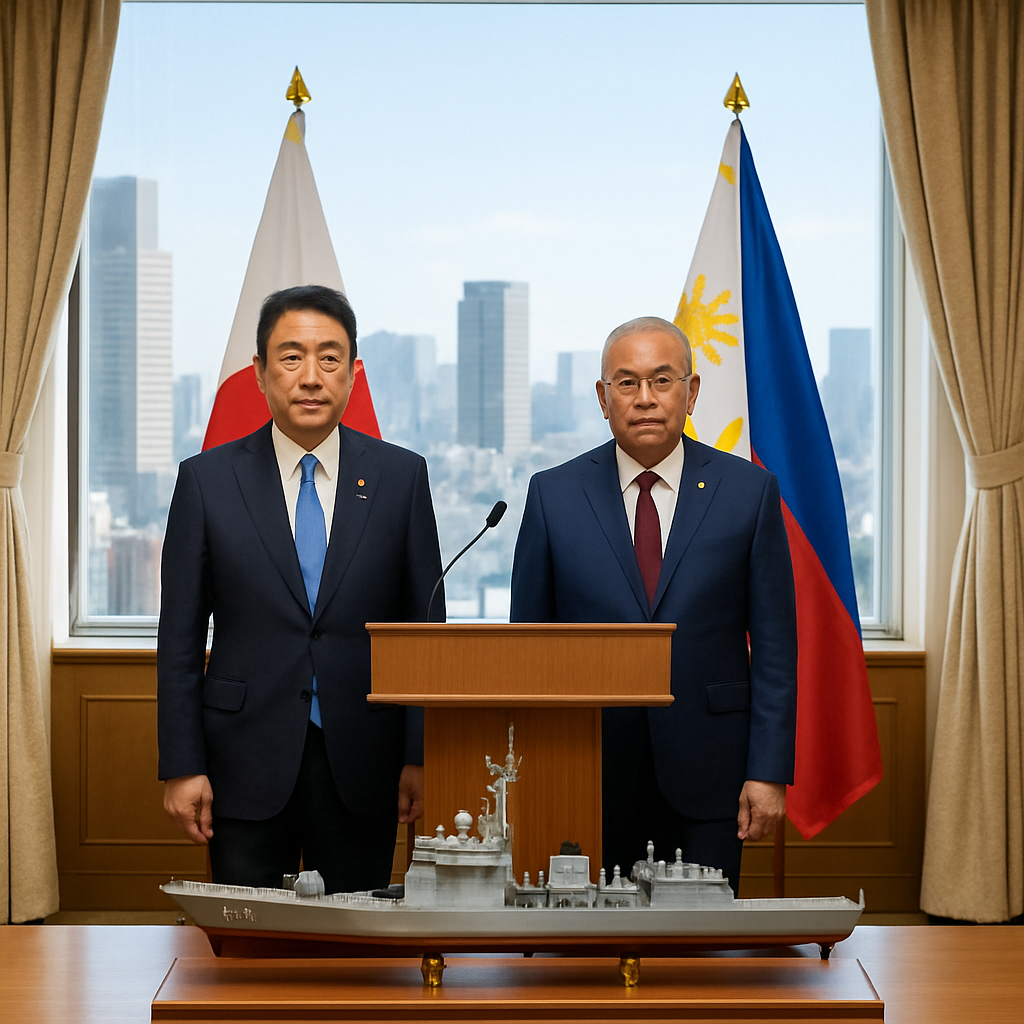
Japan Shifts Defense Export Strategy with Philippines Deal
Japan is taking a significant leap in its defense export strategy with a groundbreaking deal with the Philippines, aiming to fast-track the export of advanced destroyer escorts through bilateral working-level consultations. This move follows the establishment of a joint working group by Japanese Defense Minister Koizumi Shinjiro and Philippine Defense Secretary Gilberto Teodoro to facilitate the transfer of Maritime Self-Defense Force equipment.
Australia, Japan Forge Deterent Against China's Regional Ambitions
The 2026 National Defence Strategy makes it clear: a strong balance of military power in the Indo-Pacific requires not just the US, but also load-bearing partnerships like the one between Australia and Japan. By teaming up, Australia aims to become more self-reliant and counter China's growing regional ambitions.
DarkSword Malware Targets iOS with Sophisticated Exploit Chain
Meet DarkSword, a sneaky malware that's been targeting iOS devices with a sophisticated exploit chain, leveraging six different vulnerabilities to deploy its final-stage payloads across iOS versions 18.4 through 18.7. Google Threat Intelligence Group has tracked its use back to November 2025, with multiple actors - from commercial vendors to suspected state-sponsored operators - employing it to compromise devices.

Former NASA Chief Jim Bridenstine Steers Quantum Space Toward National Security Orbit
Quantum Space is taking a giant leap forward with Jim Bridenstine at the helm, poised to propel the company into a new era of growth and innovation in national security and space exploration. As the former NASA chief and newly appointed CEO, Bridenstine is set to lead Quantum Space as spending on space defense and exploration accelerates.
Latvian Hacker Sentenced for Role in Former Conti Leaders' Ransomware Extortion Scheme
A Latvian hacker has been sentenced to 8.5 years in federal prison for his role in a massive ransomware extortion scheme that targeted over 54 companies, causing hundreds of millions of dollars in losses. Deniss Zolotarjovs, 35, helped former Conti leaders extort payments from victims over a two-year period.
China-Linked UAT-8302 Exploits Shared Malware to Target Global Governments
Meet UAT-8302, a sophisticated China-linked threat group that's been secretly targeting governments worldwide, deploying custom malware to infiltrate and gather intel. Its recent attacks have hit government entities in South America and southeastern Europe, raising global cybersecurity concerns.
ScarCruft APT Exploits Yanbian Gaming Platform for Intelligence Gathering
Meet ScarCruft, a notorious North Korea-aligned espionage group that's been caught exploiting a popular gaming platform in China to gather intel on its users. The group trojanized a site serving traditional Yanbian-themed games, compromising both Windows and Android software.

Karakurt Ransomware Operative Sentenced for Extortion Role
Meet Deniss Zolotarjovs, a Latvian national who helped his ransomware gang extort dozens of companies - and even a government entity with a crippled 911 system - by leveraging stolen sensitive data, including children's health information. He's now facing 8.5 years in prison for his role in the Karakurt extortion operation.
North Korean Hackers Infiltrate Android Games to Spy on Defectors
Security researchers at Eset stumbled upon a sneaky plot by North Korean hackers, who infiltrated popular Android games to spy on defectors by hiding a backdoor called BirdCall in the apps. The malicious code was cleverly disguised in game files available for download on a regional gaming platform's official website.
ScarCruft hackers deploy BirdCall malware via gaming platform.
North Korean hackers APT37, also known as ScarCruft, have cleverly expanded their BirdCall malware to target Android devices, adapting their Windows backdoor to spy on mobile users. They even used a popular gaming platform to sneak the malware onto unsuspecting devices.
Weaver E-cology Flaw Exploited Through Debug API Endpoint
A critical bug in Weaver E-cology, known as CVE-2026-22679, is being actively exploited - allowing hackers to take full control of your system with a CVSS score of 9.8. This severe vulnerability lets attackers execute commands without needing login credentials, putting your entire system at risk.
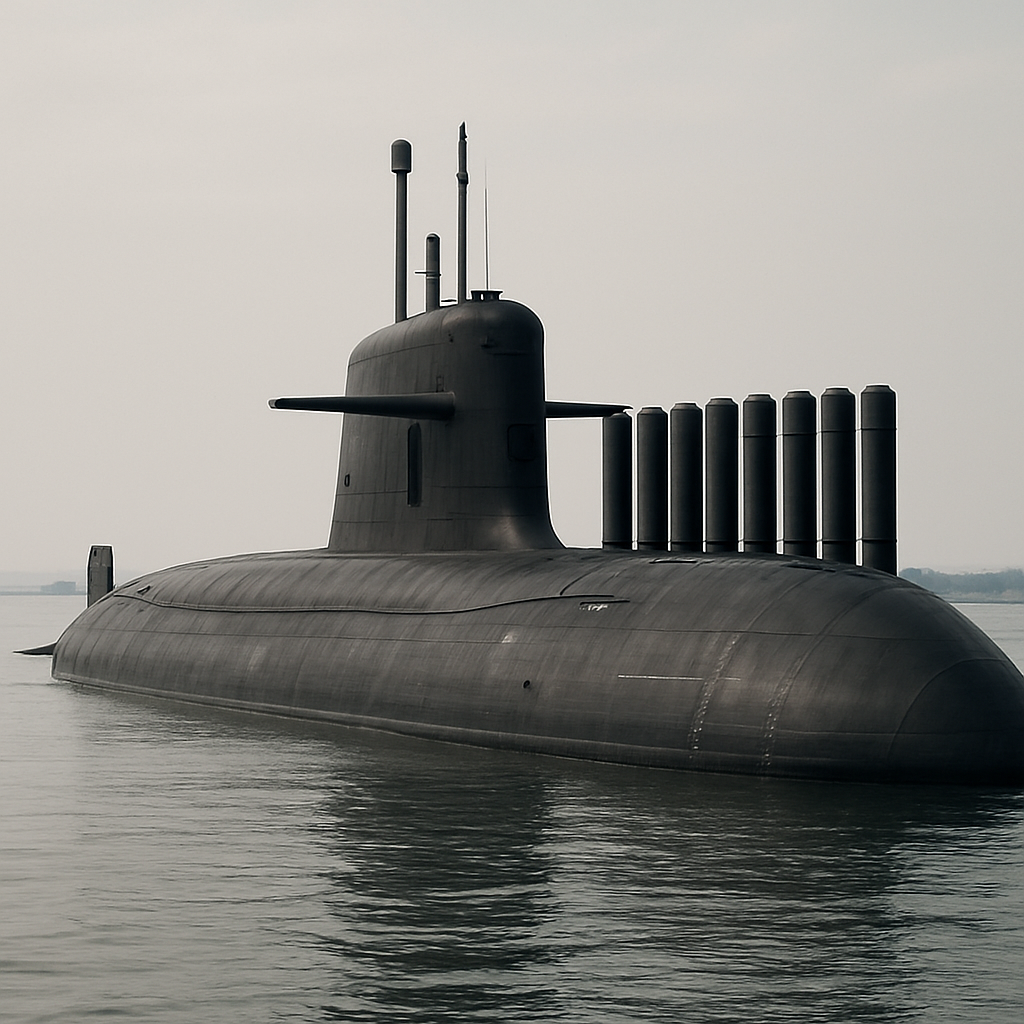
India Bolsters Nuclear Deterrent with Third SSBN Submarine
Meet INS Aridhaman, India's game-changing submarine that boasts double the missile capacity of its predecessors, thanks to its eight vertical launch tubes, revolutionizing the country's sea-based nuclear deterrent capabilities. This upgraded vessel displaces 7,000 tonnes submerged and can carry powerful K-4 missiles with a range of 3,500 km or 24 K-15 missiles with a range of 750 km.