Tag: emerging threats
8128 articles
Fake LastPass Installer Exploits Microsoft Driver to Disable Antivirus Software
Beware of fake LastPass installers that can disable your antivirus software and steal your saved credentials. A convincing fake LastPass Authenticator page on GitHub tricked victims into downloading a malicious ZIP archive that paved the way for a password stealer.
WordPress Flaw Exposes Servers to Remote Code Execution
A newly discovered WordPress vulnerability, dubbed Click2Shell, can be exploited to execute remote code on servers, and security researchers have already published technical details and a proof-of-concept. This critical flaw was patched in WordPress 7.1.1, but earlier versions remain vulnerable.
Microsoft Axes Companion Apps, Shifts Focus to New Authentication Methods
Microsoft is phasing out its 365 companion apps - Calendar, People, and Files - and setting December 16, 2026 as the end-of-life date, after which they'll no longer function or be supported. Admins are advised to remove the apps from devices by then to ensure a seamless transition.
AWS Neutralizes Compromised IAM Credentials with Managed Policy Updates
In a controlled test, AWS swiftly responded to a compromised access key by attaching a managed policy that quarantines the threat, all within 10 seconds of the key being publicly exposed on GitHub. By doing so, AWS effectively limited potential damage by denying access to certain high-risk actions.
Ransomware Actors Exploit Active Directory Group Policy
In a clever twist, hackers used Active Directory Group Policy to spread ransomware across an entire domain without installing a single malicious file on individual computers. By exploiting this native tool, they were able to hijack wallpapers, lock screens, and even disable admin accounts, all with just a few clicks.
Air Force Achieves Pilot Goal, But Backlog Persists
The Air Force has finally hit its stride in producing 1,500 pilots per year, but it's only the first step in solving a stubborn shortage of over 2,000 aviators that's not easily solved overnight. Replacing the missing pilots won't be a quick fix, as many of those needed to fill the gap are currently in mid-career staff positions.
Democrats Push for CISA Workforce Assessment Amid Cyber Threats
House Democrats are pushing for a comprehensive review of the Cybersecurity and Infrastructure Security Agency's workforce to ensure America's cyber defenses are equipped to tackle growing threats. The proposed assessment would determine if the agency has the right personnel, training, and certifications to succeed.
Hackers Reverse-Engineer Flock Cameras, Expose Surveillance Capabilities
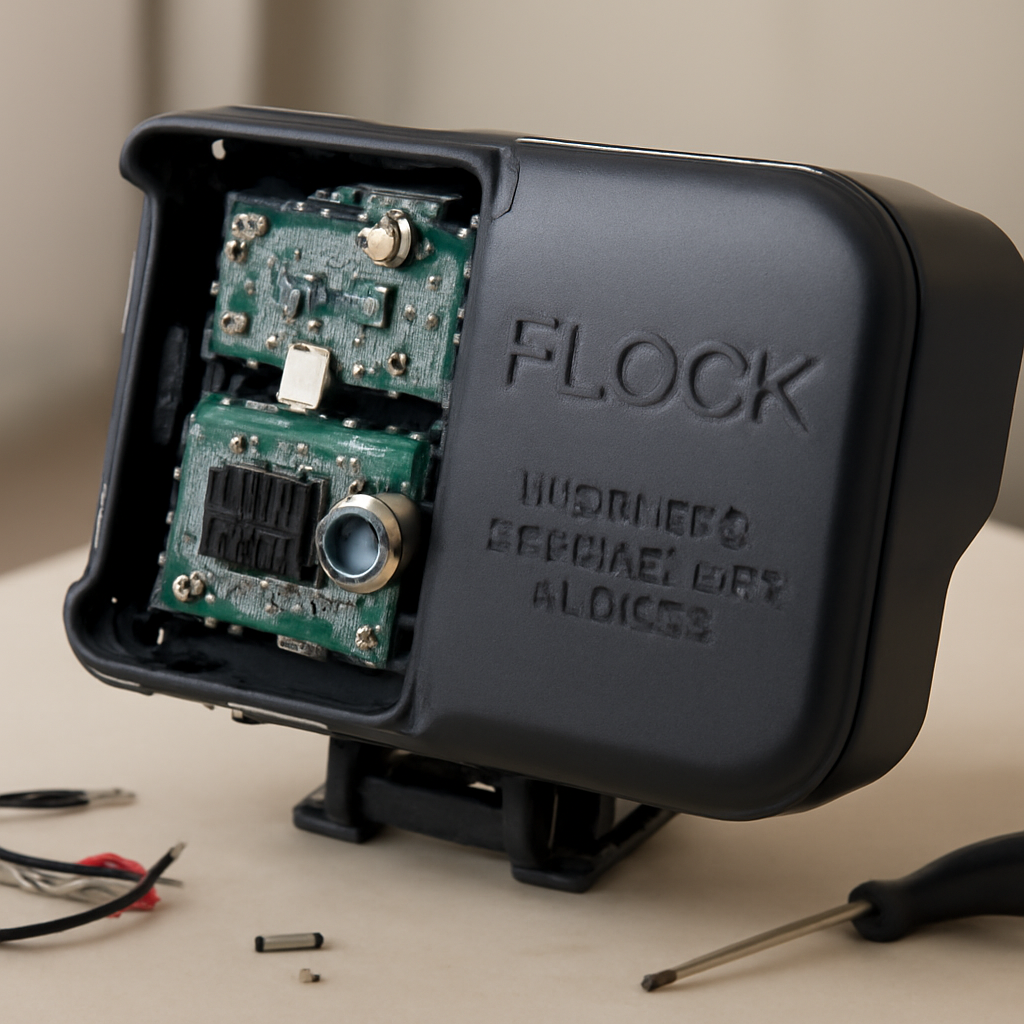
In a fascinating hack, experts got their hands on a Flock camera and uncovered a treasure trove of data, including over a million images captured over several weeks, revealing the surprising extent of its surveillance capabilities. The recovered data showed that the camera's software can detect not just license plates, but also people, vehicles, and bicycles.
Identity Infrastructure Exposes Hidden Risks in Active Directory
In today's cybersecurity landscape, identity has become the new perimeter - and Active Directory and Entra ID are the control centers that keep it all connected, making them prime targets for attackers. Compromising these identity infrastructures can give hackers access to an entire environment, not just a single system.
Google Fined $463M for GDPR Violations on Location Data Handling
Google's careless handling of location data has landed it a hefty €403 million fine for GDPR violations, sparking concerns that users may have unknowingly surrendered control over their personal info to influence ad targeting and infer interests.
Google Fined €403m for GDPR Breach on Location Data Handling
The Irish Data Protection Commission has fined Google a whopping €403m for mishandling users' location data, violating the EU's strict General Data Protection Regulation (GDPR) rules. This hefty penalty comes after a two-year investigation into how Google handled location information from 2018 to 2020.
PowerShell Backdoor TASK#STOMP Exfiltrates Sensitive Data in Stealthy Campaign
Meet TASK#STOMP, a sneaky PowerShell backdoor that's quietly harvesting sensitive business data, including documents, Wi-Fi passwords, and clipboard contents, while also taking screenshots and allowing remote control. This stealthy campaign uses a clever VBS-driven framework to evade detection and keep its operators informed.
Cisco Zero-Day Exploited in Active Attacks
Cisco is warning of a critical zero-day flaw in its Identity Services Engine (ISE) that's being actively exploited, allowing attackers to bypass authentication and gain unauthorized access with just a crafted request. This severe vulnerability, tracked as CVE-2026-76460, has been assigned a maximum CVSS score of 10.0.
Exvicy Malware Framework Exploits Rival Code to Target WordPress Sites
Malware operators are sounding the alarm: detections of the Exvicy Malware Framework are on the rise, with one seller warning that daily detections are making their service less effective. The Russian-speaking actor behind Exvicy is now charging $2,000 a month for the malware-as-a-service framework, up from $1,200 just a few months ago.
Microsoft Resolves Excel Copy-Paste Issue After Security Updates
Microsoft has fixed a frustrating issue in Excel where copying and pasting data would fail silently, leaving users none the wiser - until now, that is! The problem, which emerged after September's security updates, affected various versions of Excel, including 2016, 2019, 2021, and 2024, as well as Excel Online.
FBI Tightens CJIS Encryption, Vulnerability Rules
The FBI's latest update to the CJIS Security Policy, version 6.1, strengthens encryption rules and closes security gaps, building on the December 2024 modernization. Key changes include upgraded encryption requirements, now mandating 256-bit strength for SC-13 and SC-28.
Attackers Exploit npm Trusted Publishing in GHAPPIER Supply Chain Campaign
Malicious actors have cleverly exploited npm's trusted publishing feature to unleash a supply-chain attack, using a hijacked maintainer account to distribute a sneaky loader called GHAPPIER. They got away with it by hiding behind a valid provenance attestation, highlighting a loophole in the system.
Microsoft Updates Disrupt File History Backup Feature in Windows
Beware: the latest September 2026 Windows security updates may have an unexpected side effect - disrupting the File History backup feature and leaving you unable to create or update your backups. If you rely on File History, you may want to hold off on installing these updates until the issue is resolved.
Microsoft Urges Admins to Migrate Entra ID Users to Phishing-Resistant Auth Methods
Microsoft is sounding the alarm: by February 1, 2027, admins must migrate Entra ID users to phishing-resistant auth methods, as the company will retire SMS and voice authentication, leaving users vulnerable to cyber threats if they don't make the switch.
ShinyHunters Disrupts Clop Ransomware Gang's Operations
In a bold move, ShinyHunters infiltrated and defaced Clop's dark web leak site, claiming to have stolen sensitive private keys and server data that could dismantle the notorious ransomware gang's operations. This daring cyber heist has sent shockwaves through the ransomware underworld.
Rivals Hijack Clop's Leak Site, Demand Eight-Figure Payout
A rival hacking crew, ShinyHunters, has hijacked Clop's dark-web leak site, posting a bold takeover message and demanding an eight-figure payout in a shocking display of cyber power. The group claimed to have exploited a vulnerability in Clop's software to seize control of the site.
Rust Project Warns of Fake Job Interviews Used to Spread Malware
Scammers are tricking people into installing malware or executing malicious commands by posing as potential employers or clients on video calls, often under the guise of a job interview or contract opportunity. They set up fake company profiles and LinkedIn pages to make their ruse appear legitimate.
Revolut Phishing Attacks Surge After Data Breach
Hackers are taking advantage of a recent data breach at Revolut to ramp up phishing attacks, with scammers sending convincing smishing messages to customers in an attempt to harvest more account information. These attacks are getting more sophisticated, with scammers even collecting selfies or videos to fuel further identity fraud or scams.
Gyazo Breach Exposes 490 Million Metadata Records
A staggering 490 million metadata records were exposed in a Gyazo data breach, putting sensitive information at risk of being exploited by attackers. This massive leak, triggered by a vulnerability in an upload server, could allow hackers to uncover hidden details and track users' online activities.