Tag: emerging threats
8338 articles
South Korea Slaps KT with $39 Million Fine for 11-Month Data Breach
South Korea's Personal Information Protection Commission has slapped KT Corporation with a hefty $39 million fine for a data breach that went undetected for a staggering 11 months, exposing sensitive info of over 16,647 customers. The penalty, equivalent to KRW 53.979 billion, is a stern reminder of the importance of robust cybersecurity measures.
Air Force Faces Engine Dilemma for F-47 Fighter
The Air Force is caught in a timing squeeze with its F-47 fighter engine plans, as it works to build its current system while preparing for future integration activities. With the Next-Generation Air Power (NGAP) program's prototype phase slated to run through 2031, the service is racing against the clock.
Airpower Fails to Secure Hormuz Despite Dominance in Iranian Skies
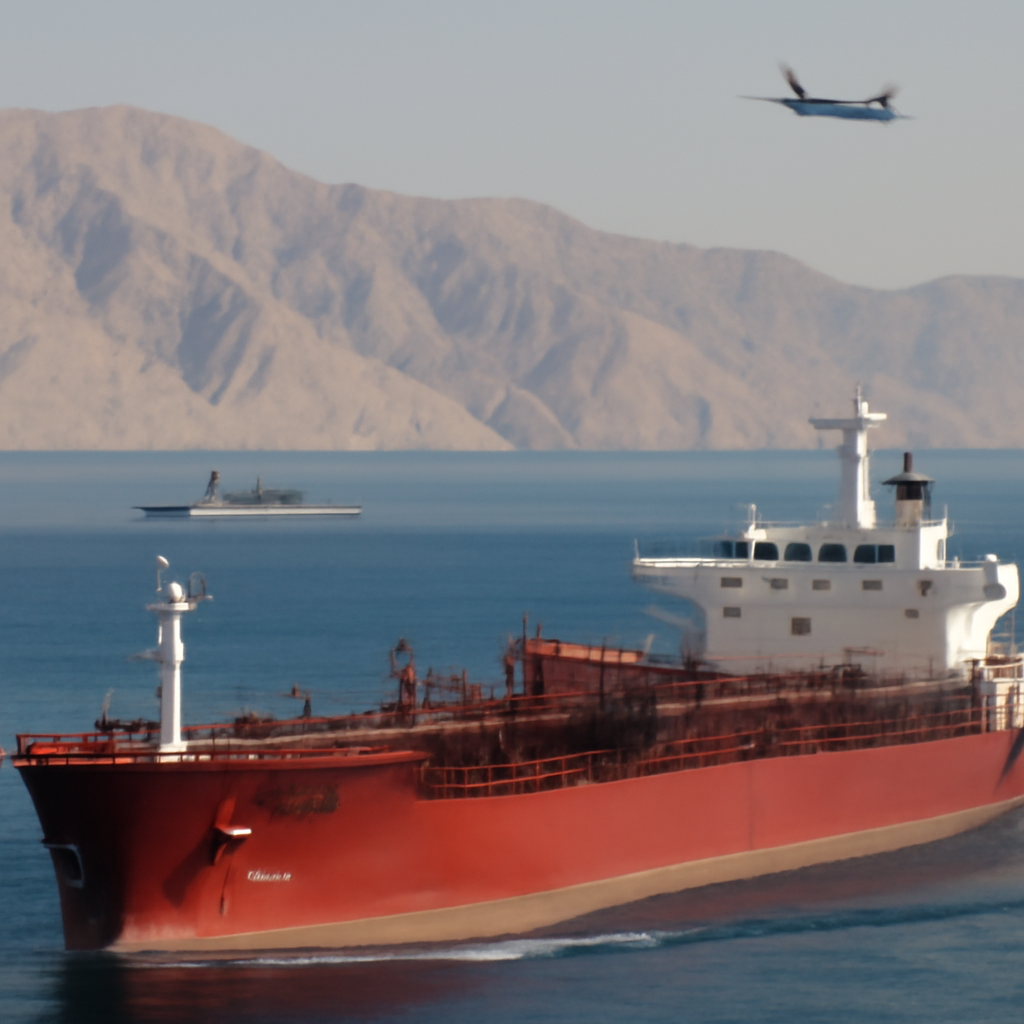
Despite the Defense Secretary's boast of a historic win, Iranian drones and missiles are still shutting down the Strait of Hormuz to commercial traffic, exposing a gaping hole in airpower's ability to secure the vital waterway. The US military's impressive destruction of Iran's navy and defense infrastructure has failed to translate to control of the skies and seas.
Ghanaian National Jailed for Stealing $10M in Romance Scams
Meet Derrick Van Yeboah, a 41-year-old Ghanaian national who was sentenced to nearly 7 years in prison for masterminding romance scams that swindled $10 million from unsuspecting victims, leaving a trail of heartbreak and financial ruin in his wake. As a "sakawa boy," Van Yeboah expertly impersonated romantic partners online, exploiting trust and vulnerability with devastating consequences.
Toy Ghouls Unveils GenieLocker Ransomware
Meet GenieLocker, the latest ransomware threat from the notorious Toy Ghouls group, which has been wreaking havoc on businesses since March 2026, with a particular focus on Russian industries. The attackers are using clever tactics, like infiltrating through OpenVPN connections, to gain access and spread their malicious reach.
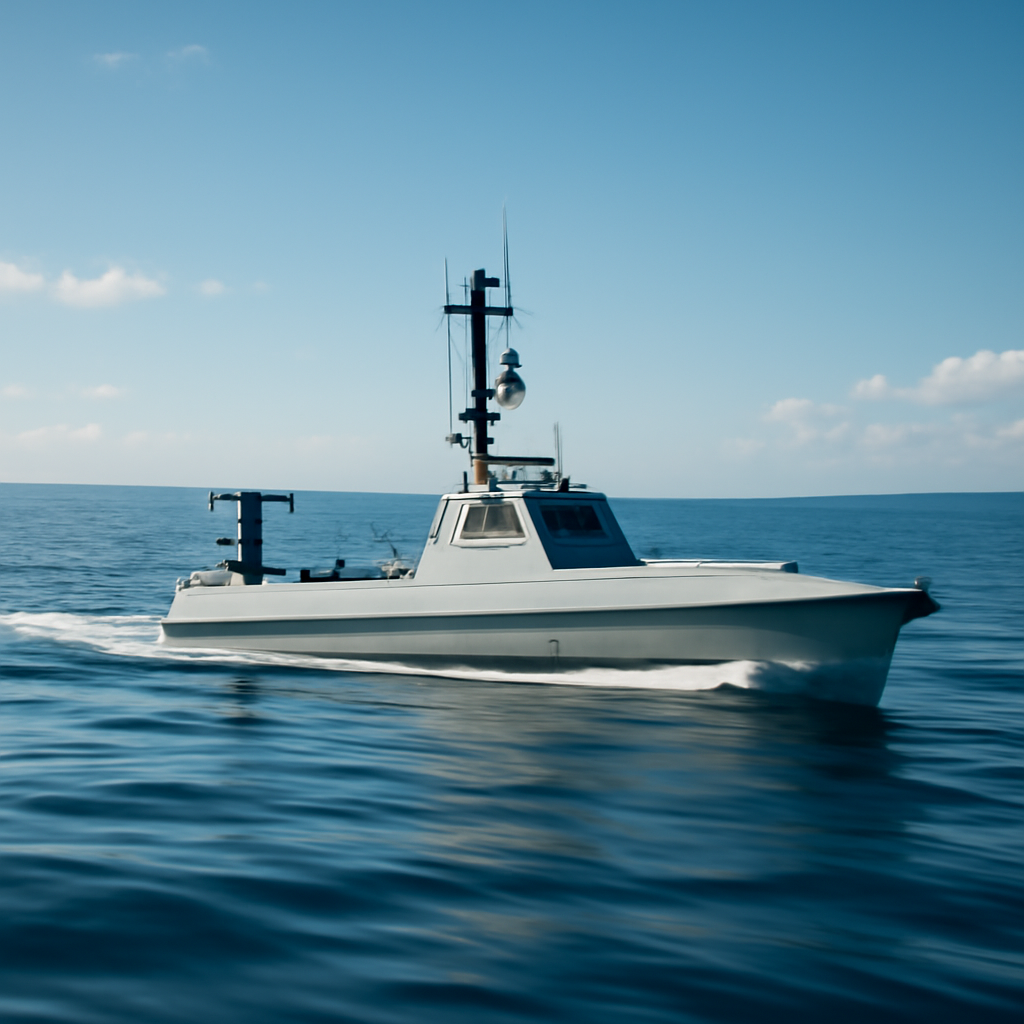
USVs Spark New Rules of Engagement Queries
Meet the Lightfish, a game-changing uncrewed surface vessel that recently tracked a Chinese vessel for hundreds of meters, sparking fresh questions about the rules of engagement at sea. This innovative, long-endurance USV can operate for up to six months, covering over 8,000 nautical miles at a leisurely pace.
US Military Left Vulnerable to Telecom Attacks
The US military's vulnerability to telecom attacks has been exposed, with numerous successful breaches resulting in stolen location data, intercepted communications, and even manipulation of American voters through text messages. This alarming threat isn't caused by a new malware strain, but rather a decades-old signaling system that underpins global telephony and has been left open to exploitation.
CMMC Pause Spurs Urgent Gap Assessments
The Department of Defense's sudden pause on CMMC Phase 2 has created an urgent need for gap assessments, especially for small and non-traditional businesses struggling to meet compliance requirements. This 60-day review aims to ease the burden, but existing obligations, including Phase 1 self-assessment requirements, remain in force.
Chinese Threat Actor Exploits AI for Autonomous Cyberattacks
Meet the Chinese threat actor who's taking cyberattacks to the next level with AI - by combining autonomous AI-driven enumeration with manual exploitation to wreak havoc on infrastructure through a arsenal of seven cleverly exploited vulnerabilities. Their cutting-edge toolkit, featuring DeepSeek and Hermes Agent, enables lightning-fast target selection, vulnerability assessment, and decision-making.
Chinese Cyber-Attacks Expose Central Asian Governments to Espionage.
Since January 2025, a sneaky cyber-attack campaign has been targeting government organizations across Central Asia, with victims in six countries, including Afghanistan, Kazakhstan, and Uzbekistan. The attacks, involving customized malware, have hit a wide range of sectors, from healthcare and research to law enforcement and education.
DPRK Hackers Target macOS Users with Crypto-Stealing Malware via Fake Updates
DPRK hackers have launched a sneaky attack on macOS users, using fake update screens to trick them into installing crypto-stealing malware. The clever tactic involves a full-screen fake update that quietly copies an attack command to the clipboard, making it look like the computer is frozen or rebooting.
Army Launches Reveille Forge for Air Defense Integration Testing
The Army has launched Reveille Forge, a cutting-edge facility that unites military, industry, and academic teams to revolutionize air defense integration testing. Located at Redstone Arsenal in Alabama, this game-changing environment enables seamless collaboration and integration of innovative solutions with existing defense systems.
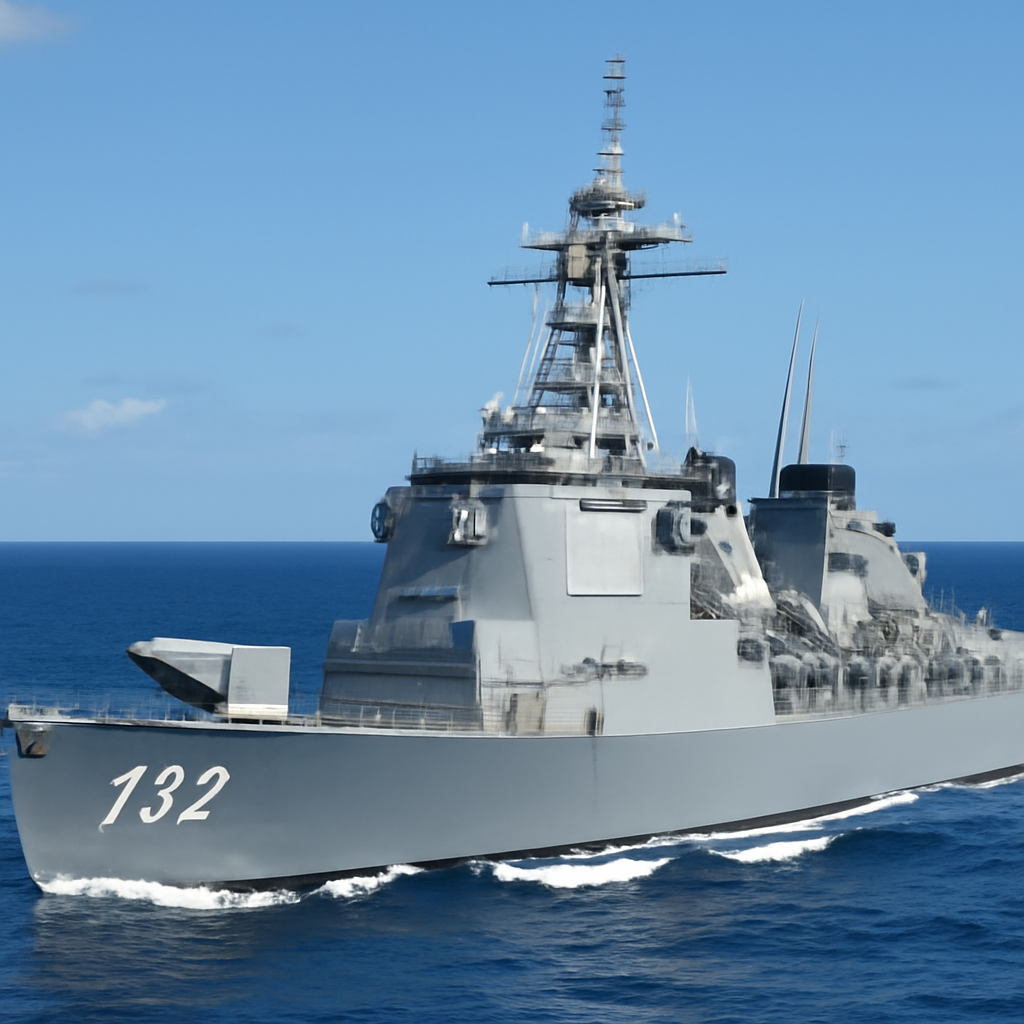
Japan Launches Tomahawk Missile from Warship in Pacific Test
Japan just took a major leap forward in its defense capabilities with the successful launch of a Tomahawk missile from a warship in the Pacific Ocean, marking a significant milestone in the country's pursuit of stand-off defense. This impressive live-fire test showcases the nation's steady progress in advancing its military technology.
Australia Urged to Audit and Fix Economic Vulnerabilities
Australia's reliance on imports leaves it alarmingly vulnerable, with just 30 days of net-import cover - a far cry from the 90 days recommended by the International Energy Agency. A government-led national audit could be the key to identifying and fixing these weaknesses before it's too late.
CISA Issues Guidance on Open-Source Software Security Risks
The Cybersecurity and Infrastructure Security Agency is stepping up to help manage open-source software security risks with a new guidebook titled "Open Source Software: Security Principles and Practices". This move aims to enhance the nation's cybersecurity by providing federal agencies with essential security recommendations.
Indonesia's Fighter Jet Gamble Tests ASEAN Ties and Military Cohesion
Indonesia's bold move to acquire combat aircraft from China and Pakistan is testing its delicate balance of military ties with ASEAN and beyond. With its bebas aktif foreign policy, President Prabowo Subianto is walking a tightrope, seeking to stay free and active without taking sides.
Broadcom Disrupts VMware with Emergency Patches for Critical Flaws
Broadcom has just released emergency security patches to tackle critical flaws in VMware's vCenter, ESX, Workstation, and Fusion - and it's urging admins to act fast, treating affected systems as immediately vulnerable. Three critical vulnerabilities, including CVE-2026-59309, CVE-2026-59310, and CVE-2026-47876, are among the five patched across these products and others that contain vCenter or ESX.
Vandalism Targets Flock Cameras, Backfires with Arrest
In a case of payback, a vandal who targeted Flock cameras in Monterey County has been arrested and will face the consequences, sending a strong message that damaging public safety equipment won't be tolerated. The suspect, 40-year-old Marcus Bee, caused thousands of dollars in damage before being taken into custody.
Google Leverages AI to Fix 1,072 Chrome Security Bugs
Google is supercharging Chrome's security with AI, and the results are staggering: a whopping 1,072 security bugs were squashed in Chrome 149 and 150, outpacing the total fixed in the previous 23 milestones combined. The tech giant is now using large language models to turbocharge its vulnerability management process, from sniffing out flaws to generating patches.
Microsoft Teams Impersonation Attacks Deploy Chaos Ransomware
Cyber attackers are impersonating IT helpdesk staff on Microsoft Teams to trick employees into installing ransomware, with one financially motivated operation deploying Chaos ransomware in a matter of minutes. They use convincing voice calls and chats to gain remote access, often within just 2-3 minutes.
ShinyHunters Breach Exposes Brinks Home Data
Brinks Home recently disclosed a security breach, with an extortion group claiming to have exposed millions of customer records, prompting the company to activate its incident response procedure and work with leading forensics experts to contain the damage. The breach, identified on July 20, thankfully didn't impact alarm monitoring and system functionality.
Azure Flaw Exposes Platform-Wide Key to All Databases
Microsoft patched a vulnerability in Azure Cosmos DB, dubbed CosmosEscape, which exposed a platform-wide key to all databases, but fortunately, no customer data was accessed and no action is required. The flaw was discovered by security firm Wiz, which detailed the exploit chain that could be used to take advantage of the vulnerability.
Analog Devices Exposes Data Breach, Probes Incident
Analog Devices recently uncovered a data breach, swiftly springing into action to contain the incident and minimize damage after detecting unauthorized access to its systems on June 23. The company has launched a thorough investigation, working with cybersecurity experts and law enforcement to understand the breach and prevent future threats.
AI Attacks Expose Enterprise Security Gaps
Nearly a quarter of organizations have been hit with AI-powered attacks, exposing significant security gaps in their defenses. Are your company's critical business platforms protected from the growing threat of artificial intelligence-driven exploitation?