Tag: emerging threats
8241 articles
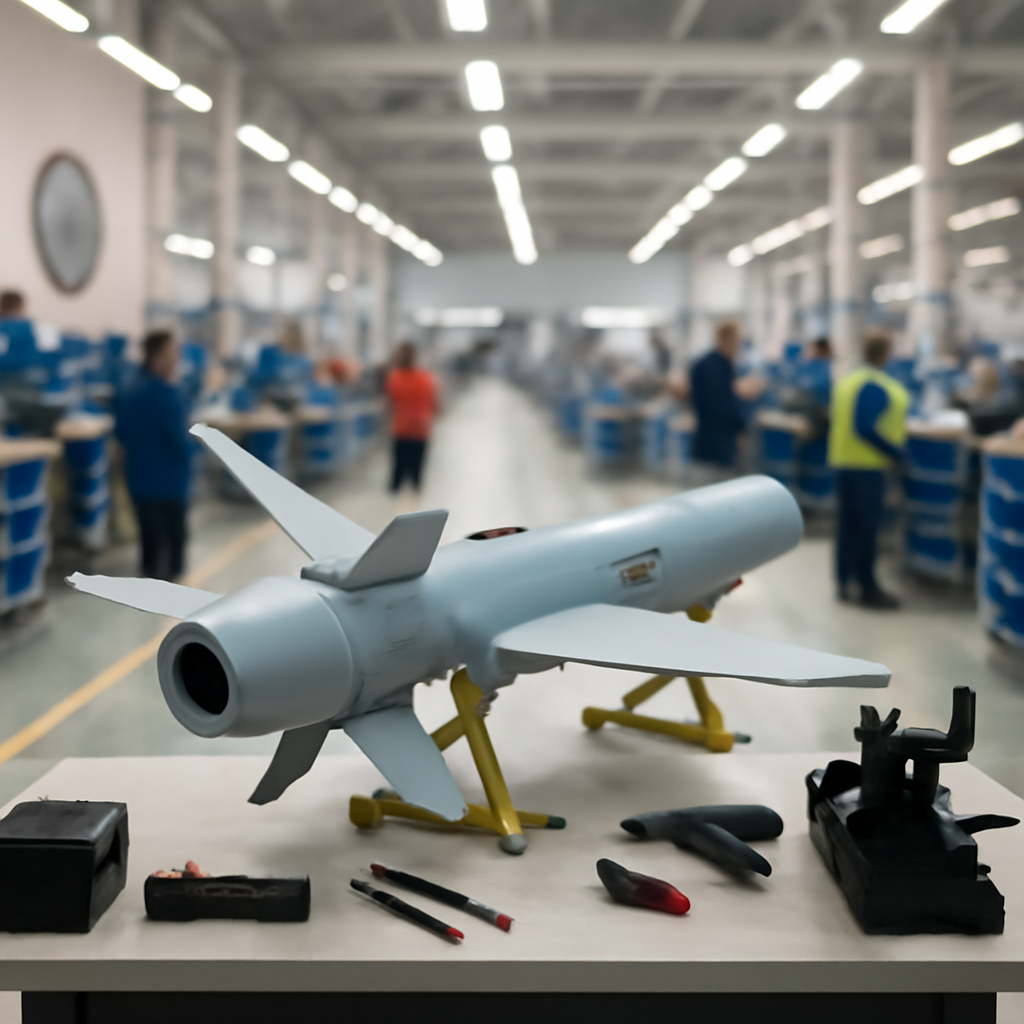
Defense Industry Targets Affordable Munitions Mass Production
We're at a critical juncture where combat power hinges on rapidly delivering advanced capabilities at scale - and L3Harris is rising to the challenge with affordable munitions production. With a proven track record of delivering over 1,200 unmanned aerial vehicles and completing more than 50 successful flight tests, the company is poised to revolutionize mass production.
Fake Chrome VPN Extensions Expose Users to Proxy Routing Risks
Beware of Chrome VPN extensions that may be putting your online security at risk: over 737 extensions impersonated popular VPN and proxy services, secretly routing users' traffic through unsecured SOCKS5 proxies. This exposed users to potential data breaches and surveillance, as their browsing activity was intercepted by a single, unknown provider.
Lazarus Exploits Windows Zero-Day to Deploy Trojan Backdoor
Meet the sneaky Trojan backdoor, Troy, that's been secretly infiltrating defense and aerospace companies worldwide by exploiting a newly discovered Windows zero-day vulnerability. This stealthy attack, part of Operation Dream Job, tricks victims with fake job offers on LinkedIn before deploying the malware.
Windows Plug and Play Feature Exploited for SYSTEM Access via Fake USB Devices
Imagine a scenario where hackers can gain SYSTEM access to a Windows computer without needing a single click or logged-in user - and even exploit it remotely over RDP with no hardware involved. Researchers have just revealed a chilling new class of attacks, dubbed "Plug and Pwn", that takes advantage of Windows' Plug and Play feature to execute malicious software with alarming ease.
Lazarus Exploits Windows Zero-Day in Targeted Defense Sector Attacks
The notorious Lazarus threat group has been exploiting a newly patched Windows zero-day vulnerability, CVE-2026-68820, to gain SYSTEM privileges and escalate their attacks on high-value targets in the defense sector. This alarming exploit has been active since early July, making it crucial for organizations to stay vigilant.
WindRelay Malware Enables Live-Call Loan Fraud via NFC Relay Attack
In just 13 minutes, a scammer can use a single phone call to trick victims into installing malware, allowing them to commit card and loan fraud - all thanks to the cunning WindRelay malware. This sneaky software uses NFC relay attacks to enable live-call loan fraud, leaving victims none the wiser.
Malicious Chrome Extensions Route Traffic Through Proxies
Hundreds of malicious Chrome extensions have been found to secretly route users' traffic through proxy servers controlled by hackers, allowing them to intercept and spy on sensitive information. This sneaky tactic puts users at risk of having their online activity monitored and exploited.
Uber Freight Probes Data Breach by Helix Extortion Group
Uber Freight is investigating a data security incident after a hacktivist group claimed to have breached its systems, but fortunately, the issue has been identified, contained, and resolved, with operations now secure and running smoothly. The breach hasn't disrupted daily operations, and the company is working to put customers' minds at ease.
Fake Remote Workers Exploit Hiring Process Gaps
Scammers are exploiting gaps in the hiring process to land remote jobs, using stolen credentials and impersonating others to get their hands on sensitive corporate information. They're taking advantage of the rise of remote work to gain access to company networks and exfiltrate proprietary data.
FBI Warns of Rising Sextortion Attacks Targeting Online Accounts
Beware: cybercriminals are on the hunt for intimate content on social media and online accounts, using stolen images and videos to blackmail victims or sell them on shady marketplaces. Once they have your secrets, they can use them to extort and exploit you, often without you even knowing.
Gunra Ransomware Targets Infrastructure via Fortinet Flaws
Gunra Ransomware is exploiting critical Fortinet flaws, including CVE-2024-55591, to gain super-admin privileges and infiltrate government and critical infrastructure networks. This alarming vulnerability allows remote attackers to craft requests and bypass authentication, putting sensitive systems at risk.
Enterprise Defenses Exposed to Quiet Attacks Within Network Perimeters
While defenses at the network perimeter are getting stronger, with a 69% prevention rate, the harsh reality is that attackers who breach this outer layer can still wreak havoc inside, with a surprisingly low 37% prevention rate. The latest Blue Report 2026 reveals a concerning gap in enterprise security, highlighting the need for stronger internal defenses.
Lazarus Exploits Windows Zero-Day with Post-Quantum Key Exchange Tactics
Lazarus hackers have taken a cutting-edge approach, using a post-quantum key exchange to secure their command channel before exploiting a Windows zero-day vulnerability in a targeted campaign against defense and aerospace companies. They leveraged Kyber/ML-KEM, a key encapsulation scheme designed to withstand quantum computer attacks, to generate fresh key material and evade detection.
UK Criminal Records Office Breach Exposes 11,000 People's Sensitive Data
A shocking data breach at the UK's Criminal Records Office has left 11,000 individuals vulnerable after sensitive information was exposed due to basic cyber security failings. The breach went undetected for seven months, highlighting the devastating consequences of neglecting online security.
AI API Flaw Exposes Secrets Across OpenAI, Anthropic, Google Models
A shocking security flaw in AI APIs has been uncovered, exposing sensitive secrets like API keys, passwords, and private keys across major models from OpenAI, Anthropic, and Google. Researchers decoded hundreds of thousands of "thinking" blocks, revealing a treasure trove of confidential data.
Akira Ransomware Gang Foiled by Safe Mode Reboot
In a surprising twist, an Akira ransomware affiliate inadvertently sabotaged its own attack by rebooting a victim's system into Safe Mode, thwarting the mass-encryption step but not before exfiltrating sensitive credentials and files. This unexpected turn of events highlights the unpredictable nature of cyber attacks.
NIST Seeks Input on NVD Overhaul Amid AI-Driven Cybersecurity Shift
The US government's quest to modernize the National Vulnerability Database is underway, and it's seeking your input - with an October 13 deadline to share innovative ideas on how to bring this critical cybersecurity resource into the automation age. NIST wants to hear your forward-looking perspectives on how to scale the NVD and supercharge its support for automated security workflows.
Hackers Exploit New Microsoft SharePoint Vulnerability in Attacks
Hackers are already exploiting a newly discovered critical flaw in Microsoft SharePoint, with over 8,500 servers exposed online and vulnerable to attacks. This authentication bypass vulnerability, known as CVE-2026-55040, allows hackers to disclose files, modify data, and wreak havoc on your system.
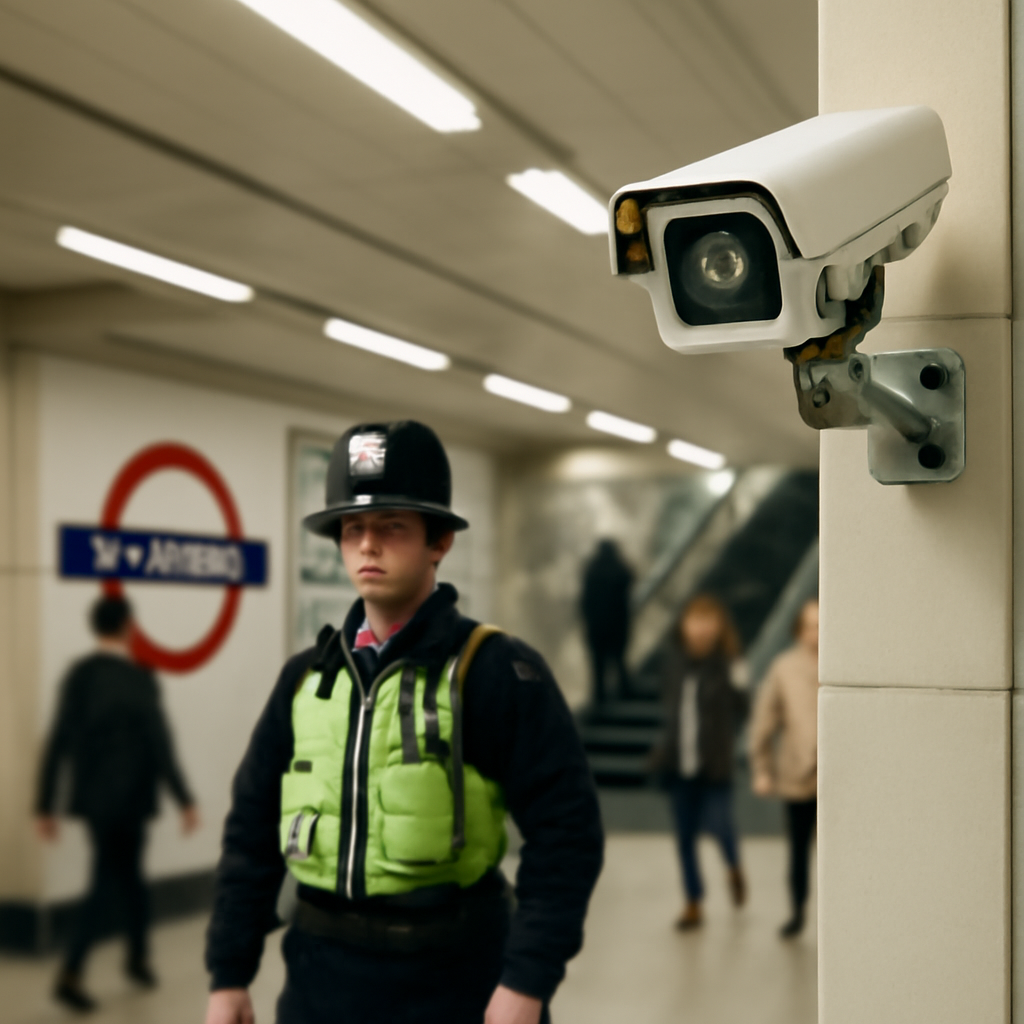
British Transport Police Deploys Live Facial Recognition on London Underground
The London Underground has become the latest testing ground for live facial recognition, with British Transport Police rolling out the technology at Victoria station, sparking concerns that millions of innocent faces will be scanned. This move has civil liberties groups sounding the alarm, with Big Brother Watch director Silkie Carlo calling it a "disturbing and dystopian" expansion.
Adobe Fixes Zero-Day Flaws in ColdFusion, Campaign Classic
Adobe has patched critical vulnerabilities in ColdFusion, Commerce, and Campaign Classic, including a zero-day flaw with a perfect 10.0 CVSS score that could allow hackers to execute arbitrary code or escalate privileges. These high-severity flaws, including operating system command injection and eval injection, require immediate attention to prevent exploitation.
Signal Bolsters Encryption with Automatic Key Verification Feature
Say goodbye to the hassle of manually verifying safety numbers - Signal's new Automatic Key Verification feature adds an extra layer of protection to ensure your encrypted chats remain private and secure. This innovative update lets you confirm your chats haven't been intercepted, without needing to meet in person or use another channel.
Microsoft Defender Zero-Day Exploited to Gain System Privileges
A security researcher known as Nightmare Eclipse has unveiled a new exploit, ShieldBreak, which can bypass Microsoft's patch for the RoguePlanet vulnerability and grant SYSTEM privileges on fully patched Windows systems. This alarming development highlights a significant gap in Microsoft Defender's defenses, leaving users vulnerable to potential attacks.
Russian Hackers Breach Polish Power Plant via Private APN
In a chilling cyberattack, Russian hackers infiltrated a Polish power plant by breaching a wind farm's VPN and firewall, then exploited a cellular router to gain control of the plant's systems. The attackers forced a combined heat and power plant into a controlled shutdown, overriding its operations with a password-protected lock.
VMware vCenter Vulnerability Exploited for Persistent Remote Access
Hackers are quickly exploiting a high-severity vulnerability in VMware vCenter, using it to gain persistent remote access to affected systems, with evidence of attacks emerging just days after patches were released. This alarming timeline suggests that publicly disclosing vulnerabilities can sometimes inadvertently hand attackers a roadmap for exploitation.