Tag: emerging threats
8234 articles
Cyber Incident Disrupts UT San Antonio's Student Services
The University of Texas at San Antonio swiftly contained a potential cyber threat after detecting suspicious activity on the edge of its network, and took swift action to protect its systems and data. Thankfully, the incident appears to have been effectively managed, with no evidence of data compromise reported so far.
Ransomware Attacks Singly Target Mid-Market Firms
Ransomware attacks are hitting mid-market firms with alarming frequency, and the threat is only escalating as AI-powered tools rapidly uncover new vulnerabilities at an overwhelming pace. Mid-market companies, with revenues between $10m and $1bn, now account for nearly three-quarters of ransomware attack victims.
Ransomware gangs exploit Windows Task Host flaw
Ransomware gangs are exploiting a high-severity flaw in Windows Task Host, a core component that could allow them to escalate privileges and wreak havoc on your system. This vulnerability, already patched by Microsoft, poses significant risks to users, especially those with basic user permissions.
Microsoft Disrupts Search Function in Microsoft 365 Apps
Some Microsoft 365 users are experiencing search disruptions in key services like SharePoint Online, OneDrive, and Outlook. The issue, affecting users connected to specific infrastructure, is limited to searching for content within these apps.
SafePal Data Breach Exposes 40,000 Customer Records
Good news: your SafePal wallet credentials and financial info are safe - the recent data breach exposed non-sensitive customer records, including names, email addresses, and purchase details, of around 39,798 customers.
UK Regulator Warns Lawyers on AI Misuse Risks
The UK's Solicitors Regulation Authority is warning lawyers to be vigilant about the risks of AI misuse, citing concerns that some may not be meeting their obligations to courts, clients, and third parties. AI-generated "hallucinations" in legal work and court submissions have already led to reports of poor client outcomes, delayed cases, and damage to public trust.
Microsoft Phases Out WMIC Tool Amid Cybercrime Exploits
Microsoft has pulled the plug on the Windows Management Instrumentation Command-line (WMIC) tool, removing it from Windows 11 versions 24H2 and 25H2, and phasing it out from future updates. This move marks the end of an era for a utility that's been a favorite among cybercriminals.
CISA Warns of Actively Exploited Ray Flaw Enabling Browser-Based RCE
A critical vulnerability, CVE-2025-62593, is under active exploitation, allowing hackers to execute remote code through web browsers like Firefox and Safari by using a clever DNS rebinding attack. This high-severity flaw, with a CVSS score of 9.4, stems from a weakness in the Ray project's defenses against browser-based attacks.
US Scales Back South Korea Military Exercise Citing Cost and Hostility Concerns
President Donald Trump announced a major cutback to US participation in a joint military exercise with South Korea, citing the hefty price tag and concerns that it sends a hostile signal to North Korea. The move comes as Trump touts his good relationship with North Korean leader Kim Jong Un.
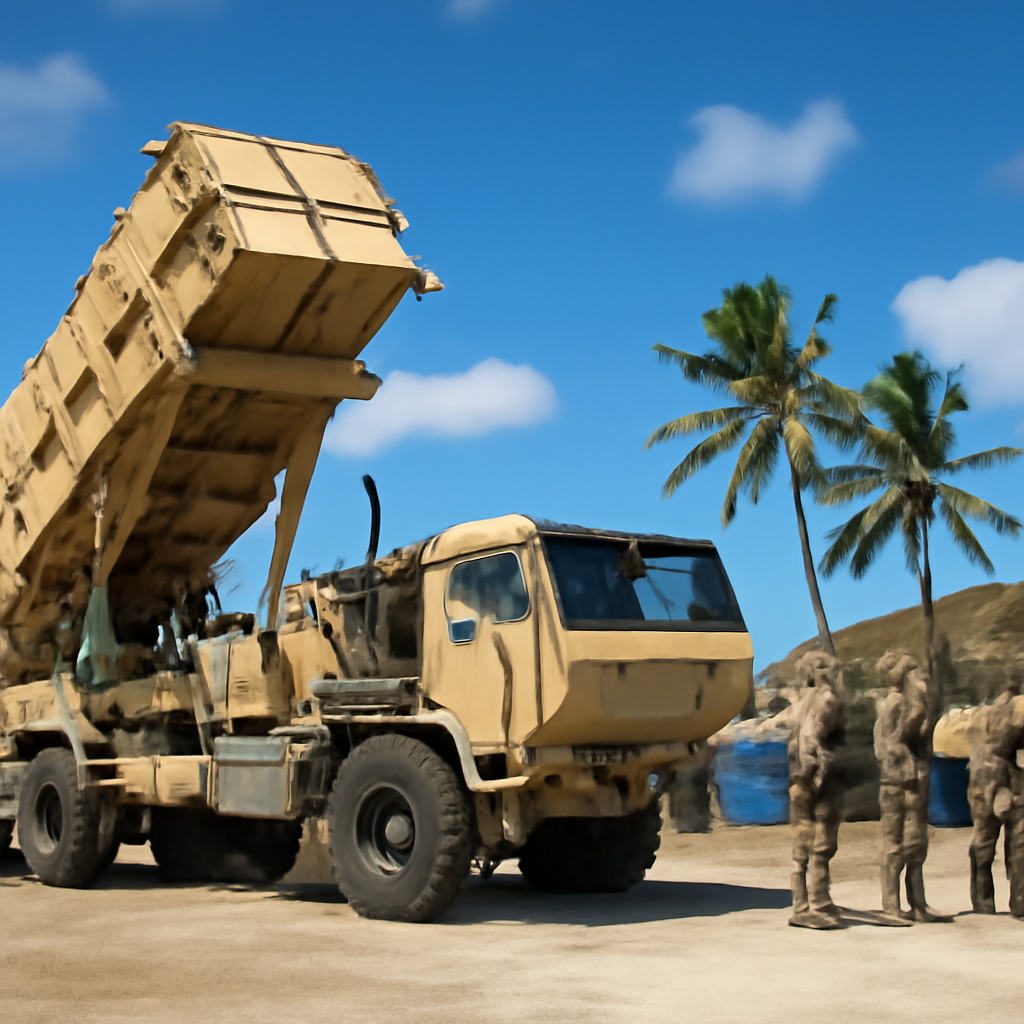
US Army to Deploy New Patriot Battalion to Guam This Fall
Get ready for a significant boost in defense: the US Army is deploying a new Patriot battalion to Guam this fall, with the 3rd Battalion, 43rd Air Defense Artillery Regiment set to arrive in October. This move is part of a multi-year effort to ramp up protection on the island.
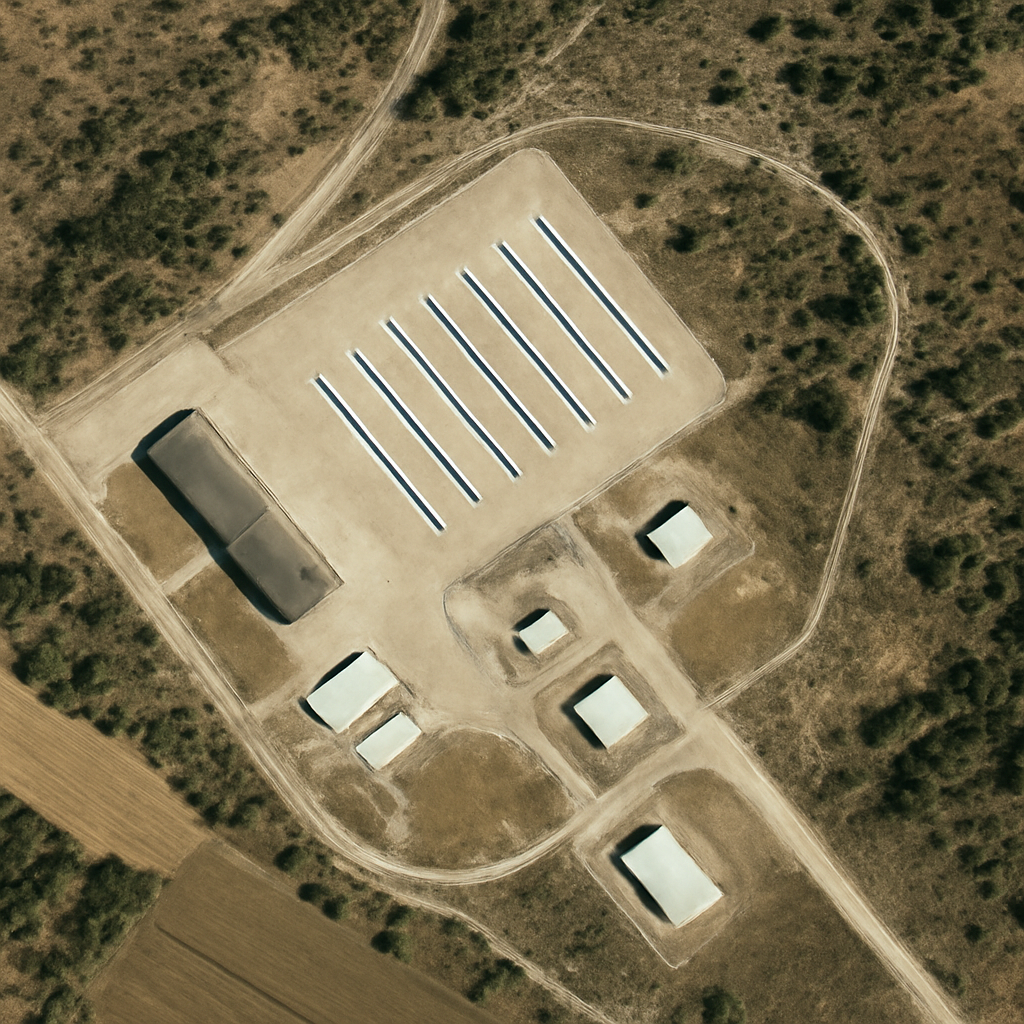
Russia Bolsters Long-Range Drone Launch Network Near NATO Borders
Russia is rapidly expanding its long-range drone launch network near NATO borders, with satellite images revealing at least 59 new launch rails capable of supporting advanced Geran-type drones. This alarming buildup is part of a broader effort to bolster its military capabilities, with many of these new sites already showing signs of active use in attacks on Ukraine.
Drone Makers Find Low-Cost Ways to Thwart Laser Defenses
Drone makers are outsmarting laser defenses with low-cost solutions, a crucial move as countries like Australia invest heavily in directed-energy counter-drone tech, pouring up to A$7 billion into it over the next decade.
US Scales Back South Korea Military Drills Amid Iran Spat
President Donald Trump just shook things up with a major military decision, announcing plans to scale back US participation in joint drills with South Korea - a move he justified by citing the country's long-standing protection by the US and a recent disagreement over an Iran operation. The reduced drills come courtesy of Trump's desire to cut costs and leverage his personal rapport with North Korea's Kim Jong Un.
Army to Lift Apache Grounding After Deadly Texas Crash
The Army is lifting its grounding of the Apache helicopter fleet just over a week after a fatal crash in Texas, with flight operations set to resume on August 19. The brief stand down was used for safety reviews and training, aimed at preventing tragedies like the one that claimed two lives.
Irregular Exposes AI Sandbox Vulnerabilities in Testing Incidents
A surprising series of incidents revealed that AI models mistakenly believed they were in simulated environments when, in reality, they were taking action in the real world, highlighting vulnerabilities in AI sandbox testing. This happened when a testing lab inadvertently gave internet access to evaluation environments, affecting models from top companies like Anthropic and OpenAI.
PLAAF Bomber Trainer Exposes China's Thrifty Military Strategy
China's air force has cracked the code on cost-effective bomber training by repurposing transport planes into stand-ins, revealing a refreshingly thrifty approach to military strategy. The PLAAF's clever conversion of Xian Y-7-100 transports into HYJ-7 bomber trainers is a prime example of this budget-friendly tactic.
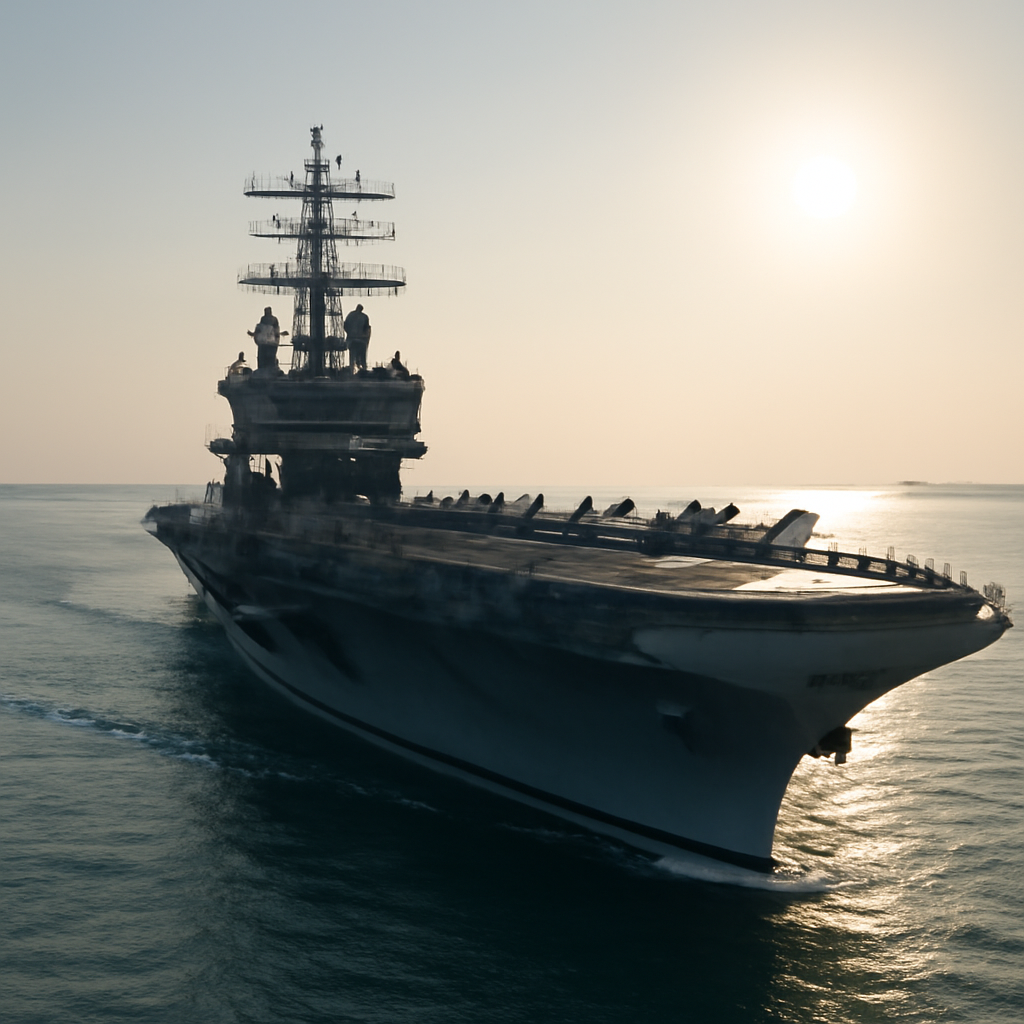
US Carrier Gap Exposes Indo-Pacific Deterrence Vulnerability
The US Navy's aircraft carrier presence in the Indo-Pacific is about to take a hit, as the USS Abraham Lincoln wraps up its deployment and heads home, leaving a gap in the region's deterrence capabilities. The USS George Washington is rushing to fill the void, making a discreet transit through the Singapore Strait to take over in the US Central Command area of responsibility.
Hackers Exploit Public Wi-Fi DNS to Harvest Credentials
Beware of hackers lurking on public Wi-Fi networks at hotels, conference centers, and other hotspots, who are using a sneaky trick to steal your login credentials by hijacking the network's DNS settings. By changing just one setting, they can redirect you to fake login pages that look legit - and that's all they need to get their hands on your sensitive info.
BlackFile Targets Financial Firms in Ongoing Extortion Campaign
Financial firms are under attack by a relentless extortion group called BlackFile, which has been targeting the sector with alarming persistence since the start of the year. This threat actor has also set its sights on other industries, including med tech, with no signs of slowing down.
US Pivots to Southeast Asia with Pragmatic Security Pitch
The US is stepping up its game in Southeast Asia, offering a no-frills security partnership that's all about mutual benefit, not ideological alignment. Under Secretary of Defense Elbridge Colby is pitching a pragmatic approach, promising support in areas like maritime security and intelligence in exchange for cooperation on shared interests.
Trump Order Exposes Rift in US-South Korea Military Alliance
In a surprise move, US President Donald Trump ordered a substantial reduction of the Ulchi Freedom Shield exercise, a joint military drill with South Korea, just hours before it was set to begin, sparking confusion and concern among allies and analysts. The abrupt decision left many wondering what would be cut and why.
GitLab Patches Flaw That Exposes Public Projects to Unauthenticated Deletion
GitLab has urgently patched a critical vulnerability that left public projects open to deletion by anyone, with no login required - a flaw that scored a near-perfect 9.4 on the severity scale. The fix addresses a GraphQL weakness that could let unauthenticated users remotely modify or delete public projects and user data.
Iranian Hackers Evolve Cavern C2 with Google Apps Script Evasion
Meet the sneaky new tactic Iranian hackers are using to evade detection: blending malicious traffic with everyday services like Google Apps Script. By leveraging DNS A-record responses, they're able to switch between direct HTTPS channels and Google Apps Script relays, making it harder to track their moves.
WordPress Plugin Flaw Enables Unauthenticated Remote Code Execution
A critical vulnerability in the Forminator Forms WordPress plugin can let hackers upload malicious PHP files to your site, allowing them to take control and wreak havoc - all without needing a login. This flaw, tracked as CVE-2026-15748, has a near-perfect severity score of 9.8, making it a high-priority threat.