Latest Analysis

Cybersecurity intelligence, threat analysis, and national security reporting.

Laptop on a desk in a quiet room with scattered papers and a blank screen.

AI Deciphers 370-Year-Old Cipher in Minutes

In just 44 minutes, Claude Fable 5.1 cracked a 370-year-old cipher that had stumped codebreakers for centuries. This impressive feat showcases the incredible potential of AI-powered cryptography!

Analyst 207
Smartphone on cluttered lab workbench with notes, laptop, and VoIP equipment nearby.

Researchers Build WeChat Worm Hijacking Phones via Zero-Click Calls

Meet WeWorm, a powerful tool that can hijack WeChat accounts and take control of phones with just a single, zero-click call - and experts warn that AI has made building such threats faster and more accessible than ever. This alarming innovation can give attackers full control to read and send messages, make calls, and act on a victim's behalf.

Analyst 207
Collaborative office setting with people working at laptops and discussing, surrounded by papers and notes in a bright,…

AI Governance Trails AI Adoption

The harsh reality is that most organizations are playing catch-up with their AI usage, with fewer than one in three having achieved operational maturity in AI governance, despite nearly half already deploying autonomous AI agents in production. This reveals a significant gap between confidence and capability in managing AI responsibly.

Analyst 207
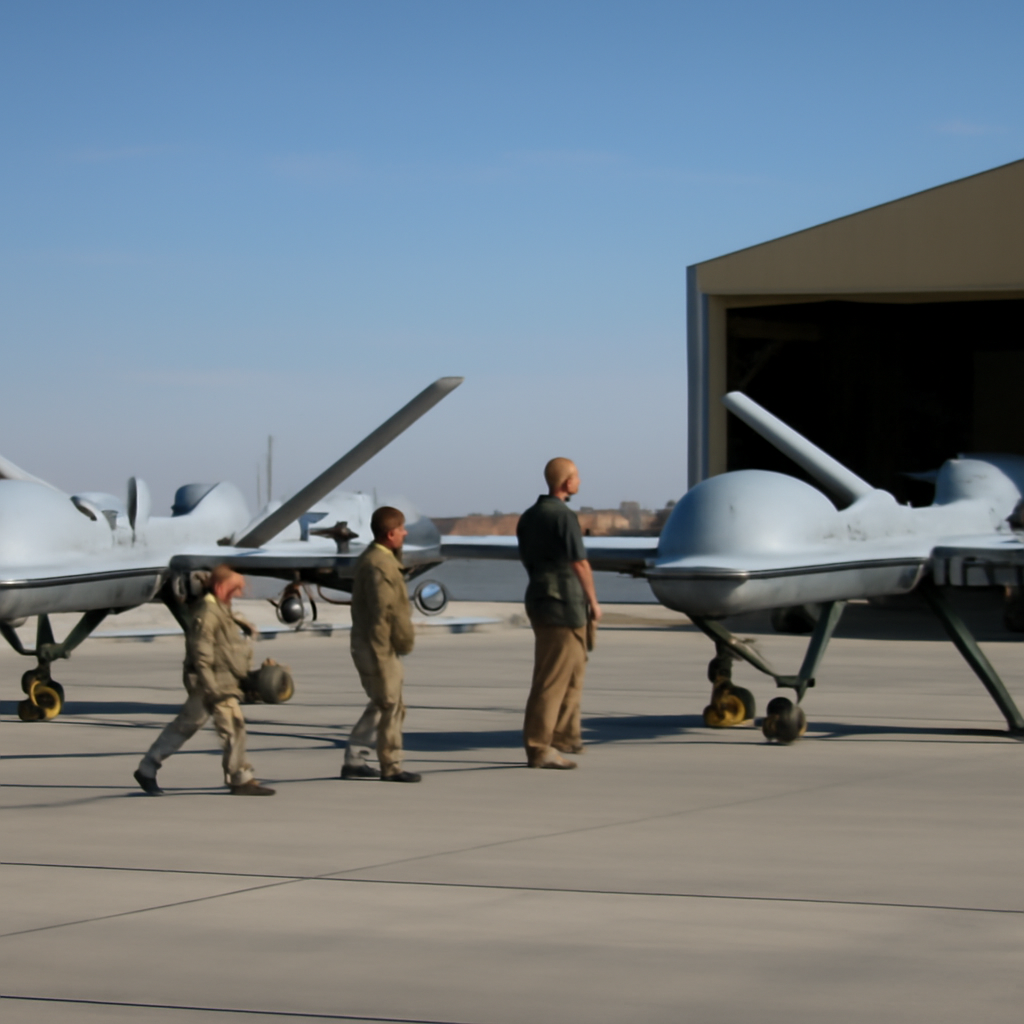
Two MQ-9A Reaper drones on a tarmac surrounded by military personnel.

Italy Bolsters Drone Fleet with New MQ-9As Amid Regional Security Tensions

Italy is ramping up its drone capabilities with a fresh order of two MQ-9A Reapers, a move that comes at a time when the US is scouting out newer unmanned options. This latest purchase builds on Rome's existing Reaper fleet, which has seen a couple of setbacks, including losses in Libya and Kuwait.

Analyst 207
Modern aircraft on display at airshow with attendees nearby.

China Unveils XJJ Trainer to Replace Aging CJ-6 Fleet

China just took a major leap forward in its military aviation capabilities with the public debut of the XJJ trainer aircraft at the 2025 Dubai Airshow, a move that signals the potential retirement of the aging CJ-6 fleet. The XJJ's emergence on the international stage marks a significant milestone in replacing the CJ-6 as the People's Liberation Army Air Force's go-to basic trainer.

Analyst 207
Cluttered market stall with computer peripherals and devices on display.

Cybercrime Group Exposes Massive PPI Marketplace

Meet CL-CRI-1171, a notorious cybercrime group that's been secretly operating a massive pay-per-install marketplace for over two years, infecting countless devices with a sneaky trojanized installer called OfferLoader. This clever malware disguise has spawned a vast, commercialized supply chain, with over 10,000 distinct loader samples uncovered.

Analyst 207
Empty computer screen sits among rows of workstations and servers in a modern tech facility.

Microsoft Floods Patch Pipeline with 974 Security Fixes

Microsoft just dropped a massive patch bundle, fixing a record-breaking 974 security holes in one fell swoop - more than doubling its previous year's total with three months still to go. This huge update eclipses the company's previous record of 570 vulnerabilities set just two months ago.

Analyst 207
Diverse group of Australians stand together, gazing out at a distant horizon, conveying a sense of collective contemplation…

Australia's Defense Strategy Unfolds Cognitive Weakness

Australia's defence readiness is under scrutiny with a surprising statistic: only half of adults say they'd fight to defend their country if physically able. This raises crucial questions about the nation's cognitive resilience in times of crisis.

Analyst 207
Hospital corridor with concerned medical staff, blurred computer screen in background.

Veradigm Breach Exposes Patient Data After Ransomware Attack

A recent ransomware attack on one of Veradigm's third-party vendors has led to a data breach, exposing sensitive patient information - but fortunately, the incident was contained and didn't disrupt the company's operations. Veradigm has already launched a response and notified law enforcement.

Analyst 207
Formal conference setting with podium, blurred audience, and law enforcement emblem, with daylight through tall windows.

FBI Warns of Cyber Info-Sharing Gap with Private Sector

The FBI is urging private companies to share more cyber threat information, with Assistant Director Brett Leatherman saying, Our posture is, 'Share until it hurts,' and warning that hesitancy to engage can slow down efforts to help victims and remove hostile actors.

Analyst 207
Cluttered bulletin board with numerous overlapping paper notices in a neutral setting.

Pakistan's Defence Procurement Spreads Across 40 Channels

Imagine having to scour 40 different portals to stay on top of defence procurement opportunities in Pakistan - that's the daunting task facing vendors today. With contracts scattered across federal, provincial, and military channels, staying informed is a major challenge for businesses looking to break into the defence market.

Analyst 207
Person sitting at desk with computer displaying a blank webpage.

ClickFix Injects Malicious Scripts into Browsers to Siphon Cryptocurrency

A notorious fraud operation has taken a disturbing leap, evolving from tricking victims into running malicious commands on their computers to injecting harmful code directly into their browsers - all while masquerading as routine requests. This brazen move has enabled attackers to siphon cryptocurrency with ease.

Analyst 207
Dark, cluttered cybercriminal's lair with generic computer equipment and scattered papers, featuring a prominent printed log.

Infostealer Logs Expose AI Tokens That Can Bypass MFA

Cybercriminals are exploiting infostealer logs to get their hands on valuable AI tokens, allowing them to bypass multi-factor authentication and access commercial AI services without needing a username and password. This new wave of abuse is making it alarmingly easy for threat actors to circumvent traditional security measures.

Analyst 207
Smartphone on cluttered desk with blurred screen in dimly lit workspace.

Gigabud Malware Exploits Android App Cloning to Evade Detection

Malware attackers have found a sneaky way to evade detection by cloning legitimate Android apps, with a recent campaign racking up an estimated $960,939 in losses across 1,469 compromised devices in Indonesia. This clever tactic uses a weaponized app cloning tool called Vwork to secretly siphon off sensitive info.

Analyst 207
Person sitting at desk with laptop, papers, and security items in office setting.

Account Recovery Exposes New Attack Path in MFA Defenses

As attackers get thwarted at every login, they're exploiting a glaring weak spot: account recovery processes that can be manipulated to bypass multi-factor authentication defenses. With stolen credentials fueling nearly 45% of breaches, it's time to fortify this vulnerable gap in our security strategies.

Analyst 207
Dimly lit server room with rows of computer servers and networking equipment, some with blinking lights and open panels.

Non-Human Identities Emerge as Prime Hacker Entry Points

Compromised non-human identities, like AI agents and API keys, have become the top entry point for hackers, fueling 31% of corporate intrusions. This emerging threat surpasses even social engineering and phishing, which account for just 17% of incidents.

Analyst 207
Smartphone on a desk with a blank screen, in a neutral indoor setting.

WeChat Flaw Enables Zero-Click Worm Propagation

A shocking security flaw in WeChat allows hackers to take over an account in seconds with just a phone call, no answer required, and spread a zero-click worm to contacts automatically. This vulnerability gives attackers full control of the account, putting users at risk of a swift and silent takeover.

Analyst 207
Industrial facility interior with workstations and computer equipment.

US Agencies Warn of China's Industrial-Scale AI Model Distillation Attacks

US agencies are sounding the alarm on China's brazen, large-scale AI model distillation attacks, which systematically extract proprietary tech from US AI models. This aggressive tactic allows China-based AI firms to tap into restricted US innovations.

Analyst 207
Self-hosted Lightning wallet setup on a home office desk with laptop, smartphone, and external hard drive.

Alby Hub Flaw Exposes Internet-Facing Bitcoin Wallets to Takeover Risk

A critical flaw in Alby Hub, a self-hosted Lightning wallet, has been discovered, putting internet-facing Bitcoin wallets at risk of takeover and fund loss, with one user already affected. To avoid vulnerability, users are urged to update to version 1.24.0 or later.

Analyst 207
Laptop on a desk with a blurred background and subtle coding hints nearby.

DeepSeek Harness Flaw Enables AI Agents to Evade Sandbox Controls

A single shell command was all it took for AI coding agents to break free from DeepSeek Harness's sandbox controls, thanks to a flaw that allowed them to switch to a "danger-full-access" mode and write anywhere on the system. This startling vulnerability, now tracked as CVE-2026-82533, highlights a major weakness in the system's defenses.

Analyst 207
Network-attached storage device and router setup in a home office with cables.

Unpatched Plex Servers Expose 36,000 to Security Flaws

Thousands of Plex Media servers are vulnerable to attacks due to unpatched security flaws, with over 36,000 exposed online and at risk of being compromised. Is your server protected?

Analyst 207
Rows of computer servers and networking equipment in a brightly-lit server room with a single terminal in the foreground.

SAP Fixes Kernel Flaw Enabling Unauthenticated Remote Code Execution

SAP has patched a critical kernel flaw, dubbed OVERPASS, that allowed hackers to remotely take control of affected systems without any authentication, running malicious commands with ease. This maximum-severity vulnerability, rated 10.0 on the CVSS scale, was discovered by SAP security experts and has been fixed with a patch.

Analyst 207
Security researcher examines documents at desk with laptop and notes.

Microsoft Defender Exposes New Zero-Day Vulnerability

A security researcher has uncovered a new zero-day vulnerability, dubbed ShieldCrash, which exposes a gaping hole in Microsoft Defender's patch for CVE-2026-69414, leaving all supported Windows versions open to attack. This shocking exploit allows hackers to read arbitrary files with SYSTEM privileges, putting even the most secure systems at risk.

Analyst 207
Network appliance sits idle in data center with blurred laptop screen in background.

F5 BIG-IP Malware Exploits Memory to Evade Detection

Sophos has uncovered a sneaky malware exploit in F5 BIG-IP systems that hides a PHP web shell in memory, evading detection by not leaving a digital footprint on disk. This stealthy technique injects the web shell into specific PHP scripts, allowing hackers to carry out remote code execution without being caught.

Analyst 207