[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
A China-aligned threat group has been exploiting a chain of three zero-day vulnerabilities in Google Chrome and Microsoft Windows, highlighting a coordinated effort within the Chinese computer network exploitation community. This alarming discovery reveals the group's ability to rapidly weaponize and customize exploits across multiple campaigns.
The US military has suffered a staggering blow, losing at least 45 MQ-9A Reaper drones - a quarter of its pre-war fleet - in the Iran conflict, with losses estimated to be around $4 billion. This dramatic depletion has created cascading shortfalls in the US aerial inventory.
In a brazen display of corruption, a defense contractor allegedly funneled a six-figure payment through a shell company to influence a senator's decision on tens of millions in Navy funding. The secret deal was hatched over a casual meeting at a Corner Bakery near the Capitol.
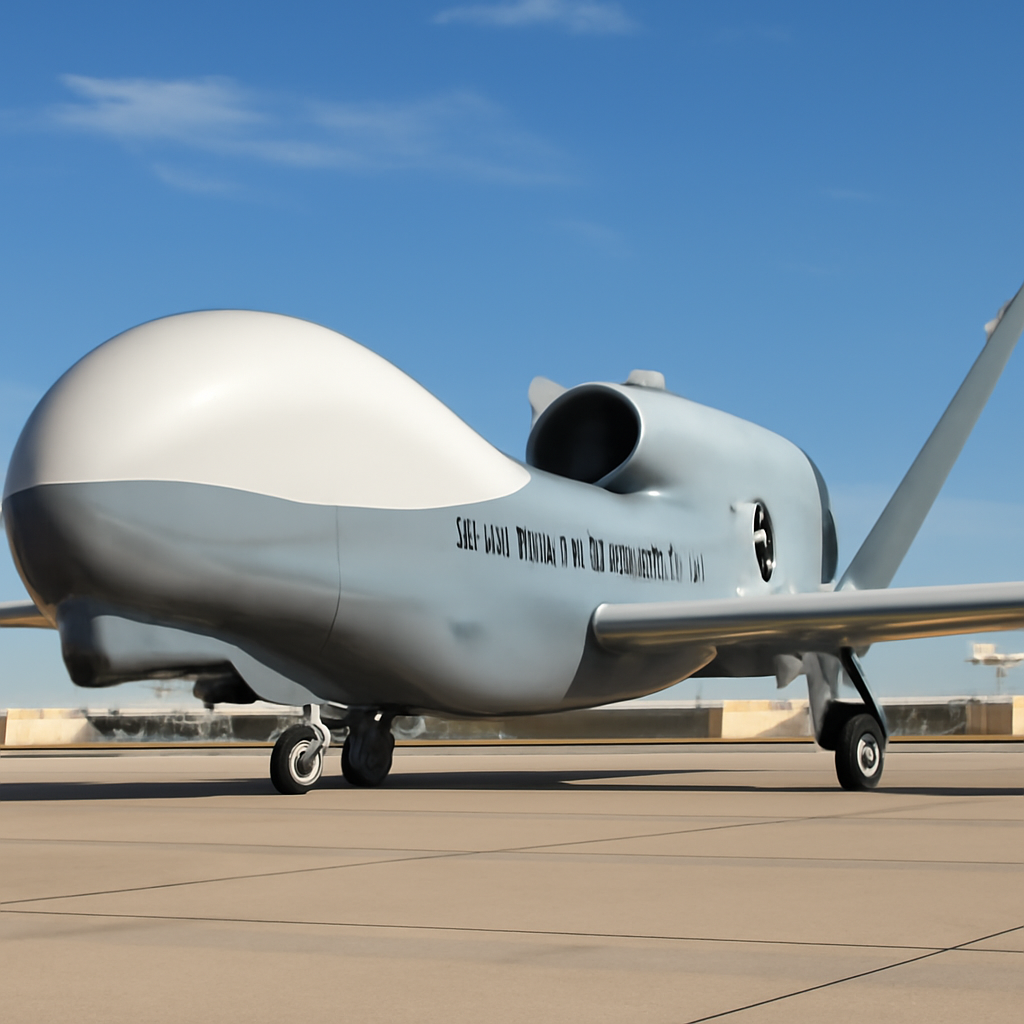
The Royal Australian Air Force has reached a major milestone, declaring Initial Operational Capability for its cutting-edge MQ-4C Triton aircraft and MC-55A Peregrine Intelligence Surveillance Reconnaissance and Electronic Warfare aircraft. This achievement supercharges the RAAF's Intelligence, Surveillance and Reconnaissance capabilities, bolstering its presence in the vast Indo-Pacific region.
Rep. Josh Gottheimer is taking a proactive stance against cyber threats with the AI Cyber Defense Act, a new legislative proposal that would provide critical infrastructure operators with free access to cutting-edge AI technology to identify and fix security gaps. This innovative program aims to safeguard families and communities from potential disasters by staying ahead of emerging threats.
Taiwan's hesitant approach to asserting its sovereignty has created an opening for Beijing to dictate the narrative, undermining the island's status on the world stage. A recent exchange featuring Foreign Minister Lin Chia-lung's straightforward declaration that "Taiping Island is of course an island" highlights the inconsistency and reactivity that Beijing exploits.
As President Trump and Chinese leader Xi meet in Washington, the stage is set for a high-stakes showdown over who gets to shape the rules of artificial intelligence - and whether regulation becomes a powerful tool of influence. The September 24 summit puts the US and China's competing visions for AI governance front and center.
Tribes nationwide are stepping up their tech game, investing in cybersecurity and infrastructure to boost sovereignty and service delivery. With TribalHub's Tribal Net 2026 forum, IT leaders from Native American communities are uniting to share knowledge and strategies for sustainable growth.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
President Donald Trump has sparked a global debate by announcing a bold rebranding of artificial intelligence as "super intelligence", vowing to make the term official in all US documents and urging the world to follow suit. This move has ignited a fresh conversation about the future of tech and its role in shaping the global economy.
The UK is stepping up its support for Saudi Arabia's defense with the deployment of a Royal Air Force Voyager tanker, enabling the kingdom to bolster its air defenses against Houthi attacks. This move underscores the UK's commitment to helping Saudi Arabia and the Yemeni government exercise their right to self-defense.
A brazen data breach by ShinyHunters has compromised highly sensitive information on nearly all FBI agents and job applicants, including personnel records. The group is demanding action from the bureau within a week, raising serious concerns about the security of critical government data.
The Air Force is shaking things up with a major restructure, pulling civilian staff from the China Aerospace Studies Institute (CASI) and assigning military members to take over the mission. Affected employees will keep their current roles for now and be considered for reassignment later.
South Korea is walking a tightrope in the Middle East, caught between US pressure to join the fray against Iran and its own desire to avoid getting entangled in a war, with President Lee Jae-myung drawing a clear red line against deployment. Can Seoul find a way to protect its interests without taking sides?
A massive GDPR breach has hit Sweden, exposing sensitive personal records of 2.2 million people after a cyberattack on Miljödata, a widely-used municipal HR and work-environment software provider, on August 25, 2025. The breach led to a hefty $183,000 fine for inadequate security measures.
Meet CLOSEDQUORUM, a sneaky Windows malware that outsources its decision-making to AI giants like Google Gemini and Mistral, allowing it to autonomously pull off post-compromise actions. This cunning code queries multiple AI models, tallying their votes to determine its next move - and even has a tiebreaker system in place!
Security researchers have uncovered a sneaky technique called TrustSink that allows rogue MFA providers to swipe plaintext passwords during seemingly normal login attempts, and they've demonstrated it works with Microsoft Entra ID. This alarming exploit lets attackers get their hands on sensitive passwords, complete with timestamps and source IP addresses.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
In a massive cyberattack, hackers exploited vulnerabilities in WordPress and Zyxel to steal sensitive government data from 996 devices across 48 countries. The breach exposed device configurations, network info, and critical credentials, with one Western government organization losing over 18,000 records, including accounts and passwords.
Malicious actors have struck again, this time with a fake npm package called tw-pkgprobe-7731 that masquerades as a security research tool to steal credentials from unsuspecting Twilio developers. The package was cleverly designed to evade detection, only collecting and exfiltrating sensitive data when it detected a Twilio developer environment.
WordPress has patched a critical vulnerability (CVE-2026-87902) that could allow hackers to execute malicious code on susceptible servers, giving attackers an easy way to take control. This flaw, rated 9.2 on the CVSS scale, can be exploited without an account or user interaction.
A high-severity zero-day flaw in Check Point's Security Management Server was exploited in targeted attacks on July 23, allowing hackers to upload and execute scripts without logging in. This critical vulnerability, scored 9.8 out of 10 on the CVSS scale, highlights the urgent need for patching and protection.
Meet the hackers who just pulled off a massive heist: ShinyHunters claims to have stolen 2-3TB of sensitive data from FBI systems by exploiting a previously unknown flaw in Oracle PeopleSoft. The breach reportedly exposed personal info of current and former FBI employees, as well as applicant data.
Meet ClosedQuorum, a sneaky new Windows malware that uses AI to call the shots - autonomously deciding its next move by gathering intel from infected hosts and getting advice from a panel of commercial AI models. This cutting-edge threat is making waves as the first publicly documented Windows implant to hand over tactical decisions to AI.
Meet BigDiskBuster, a newly released zero-day tool that cleverly blocks Microsoft Defender updates by maxing out disk space, leaving users vulnerable until a fix is found. Its creator, Abdelhamid Naceri, a former Microsoft security researcher, has made the proof-of-concept tool publicly available on GitHub.
A critical flaw in the Bifrost AI Gateway, known as CVE-2026-90898, allows hackers to execute remote commands on servers with just one simple HTTP request, putting sensitive data at risk. This severe vulnerability has a CVSS score of 9.8, highlighting the urgent need for a fix.