Latest Analysis

Cybersecurity intelligence, threat analysis, and national security reporting.

Laptop screen displays WordPress dashboard in brightly-lit office setting.

Hackers Exploit Breeze Cache Plugin Flaw in WordPress Sites

A critical flaw in the Breeze Cache WordPress plugin, known as CVE-2026-3844, is being actively exploited by hackers, with over 170 attempted attacks reported. This vulnerability allows unauthenticated attackers to upload malicious files and take control of entire websites.

Analyst 207
Government officials walk down a hallway with a large window showing a cloudy sky, near a subtle network diagram pattern.

Germany Revives ISP Data Retention Mandate Amid Privacy Concerns

Germany's government is pushing for a new law that would require internet service providers to store customer connection data for three months to help combat online crimes, sparking concerns about privacy. The proposed mandate, justified as a way to keep the digital space safe from criminals, has been approved by the national cabinet and now awaits parliamentary approval.

Analyst 207
A router on a rack in a network closet with multiple cables connected.

China-Linked Hackers Exploit Global Infrastructure in Covert Network Attacks

Be on high alert: China-linked hackers are secretly building global covert networks using compromised routers and devices, putting anyone who's a target at risk of devastating cyber attacks and data theft. This sinister plot, revealed by a joint advisory from 16 government agencies worldwide, has far-reaching implications for organizations and individuals alike.

Analyst 207
Living room with router and smart device on coffee table near window.

Chinese Hackers Exploit IoT Devices to Obscure Nation-State Attacks

Chinese hackers are sneaking nation-state attacks under the radar by hijacking everyday IoT devices, such as home routers and smart cameras, to hide their digital footprints. This stealthy tactic allows them to evade accountability and strike from the shadows.

Analyst 207
A coding workstation with a laptop, development tools, and papers in a clean, neutral-colored room.

Bitwarden CLI npm package targeted in supply chain attack

Bitwarden swiftly contained a brief supply chain attack on its CLI npm package, confirming that a single malicious release was live for under two hours on April 22, 2026, and assuring users that their vault data remained safe. The incident was quickly remediated, with the compromised access revoked and the malicious release deprecated.

Analyst 207
Rows of computer servers and storage equipment in a brightly-lit server room.

Trigona Ransomware Exploits Custom Tool for Swift Data Exfiltration

Trigona ransomware attackers have unleashed a custom-built, command-line tool that turbocharges data theft, allowing them to siphon off sensitive information with lightning speed and razor-sharp efficiency. This potent tool is the latest weapon in their arsenal, enabling faster and more efficient data exfiltration from compromised environments.

Analyst 207
Concerned employees in business casual attire sit at computer workstations with multiple screens displaying financial data.

Grinex Crypto Exchange Halts Trading After $15M Hack

Grinex, a Kyrgyzstan-registered crypto exchange, has temporarily halted trading and withdrawals after falling victim to a massive $15 million hack. The highly coordinated attack saw over 1 billion rubles stolen, with the funds quickly laundered across multiple blockchains.

Analyst 207
Laptop screen displays Microsoft Teams chat invitation on office desk with papers and chair in background.

Threat Actors Exploit Microsoft Teams for SNOW Malware Deployment

Cyber attackers are exploiting Microsoft Teams by impersonating IT helpdesk staff, tricking victims into accepting chats from unfamiliar accounts and deploying SNOW malware. They start by flooding inboxes with urgent emails, then pose as IT support over Teams, offering to fix the problem.

Analyst 207
Vacant Senate setting with closed folder on empty podium.

Cybersecurity Nominee Plankey Withdraws Amid Senate Gridlock

Sean Plankey, a highly qualified cybersecurity expert with a background at the Department of Energy and National Security Council, has withdrawn his bid to lead the U.S. Cybersecurity and Infrastructure Security Agency after a 13-month confirmation process stalled in the Senate. His nomination, which had initially received committee approval, ultimately succumbed to procedural delays and partisan holds.

Analyst 207
Futuristic cybersecurity workstation with laptop and high-tech equipment in a bright, minimalist setting.

Google Bets on General AI Models for Cybersecurity Needs

Google Cloud is shaking up its approach to cybersecurity by betting on its general AI model, Gemini, to tackle security needs, rather than developing a separate, cyber-focused model. This bold move is based on the impressive performance of Gemini across various domains, including coding and security.

Analyst 207
Small hardware device on a plain surface with a monitor cable running through it in a bright conference setting.

UK Cyber Agency Unveils Device to Secure Computer Monitors

Meet SilentGlass, a game-changing plug-and-play device that easily secures computer monitors from cyber threats, protecting vulnerable IT infrastructure like never before. Developed by the UK's National Cyber Security Centre, this innovative gadget is set to revolutionize desktop security.

Analyst 207
Person holds smartphone with blurred screen, looking concerned in front of public library.

Proton CEO Warns Age Checks Threaten Online Anonymity

Proton CEO Andy Yen warns that mandatory online age checks could spell the end of anonymity, forcing every adult to surrender their ID just to access the internet. He argues that efforts to protect minors will inevitably sweep in adults, creating an ID checkpoint that threatens online freedom.

Analyst 207
Security team works at a workstation with multiple monitors in a brightly-lit operations center overlooking a cityscape.

Anthropic's Claude Mythos Exposes AI Vulnerability Risks

The recent exposure of Anthropic's Claude Mythos highlights a chilling reality: AI tools designed to improve software quality can be easily repurposed to accelerate vulnerability discovery for malicious ends. This underscores the growing threat of AI-powered attacks, as malicious actors exploit commercial tools with minimal friction.

Analyst 207
Docker Hub repository page on a developer's workstation screen shows a manipulated image warning.

Checkmarx KICS Tool Compromised in Supply-Chain Breach

A critical vulnerability was discovered in the Checkmarx KICS tool due to a supply-chain breach, where a malicious Docker image was briefly hosted on DockerHub, exposing users to potential security risks between April 22, 2026, 14:17:59 UTC and 15:41:31 UTC. The breach was quickly identified and rectified, with affected tags restored and malicious images removed.

Analyst 207
Person working at computer workstation with multiple screens and papers in office setting.

NIST Overhauls CVE Prioritization, Shifts Focus to High-Risk Vulnerabilities

NIST is overhauling its approach to CVE prioritization, shifting its focus to high-risk vulnerabilities in response to a staggering 263% surge in submissions between 2020 and 2025. As a result, it'll now prioritize enriching only the most critical CVEs in the National Vulnerability Database.

Analyst 207
Helpdesk worker sits at cluttered desk, staring at computer screen with password reset page.

Password Resets Expose Vulnerability in Corporate Security

Did you know that password resets can cost companies a whopping $70 each, and with stolen credentials involved in nearly 45% of breaches, it's clear that corporate security is vulnerable to attack.

Analyst 207
Vulnerable computer servers and networking equipment in a dimly lit data center.

Cyberattacks Exploit Known Flaws in Supply Chain, AI Tools

A recent cyberattack exploited weaknesses in a company's infrastructure, resulting in a staggering $290 million heist from KelpDAO, highlighting the vulnerability of supply chains to targeted attacks. The attackers manipulated key nodes to gain control and siphon off funds.

Analyst 207
Terminal screen on a laptop in a coding workspace displays code on a blurred background.

Bitwarden CLI Compromised in Checkmarx Supply Chain Attack

A rogue version of the Bitwarden CLI package, identified as @bitwarden/cli@2026.4.0, was compromised in a supply chain attack, stealing sensitive data like GitHub tokens and cloud secrets. The malicious code, hidden in a file called bw1.js, has already been distributed to users, putting their security at risk.

Analyst 207
Cluttered office desk with computer, papers, and open smartphone showing an email inbox.

UNC6692 Exposes Custom Malware Suite via Social Engineering

In a clever social engineering ploy, UNC6692 launched a massive email campaign in late December 2025, flooding targets with messages to create a sense of urgency and distraction, before following up with a convincing Microsoft Teams message that pushed a malicious link. The attackers then cleverly disguised their malware as a legitimate "Mailbox Repair and Sync Utility" patch, hosted on an Amazon S3 page.

Analyst 207
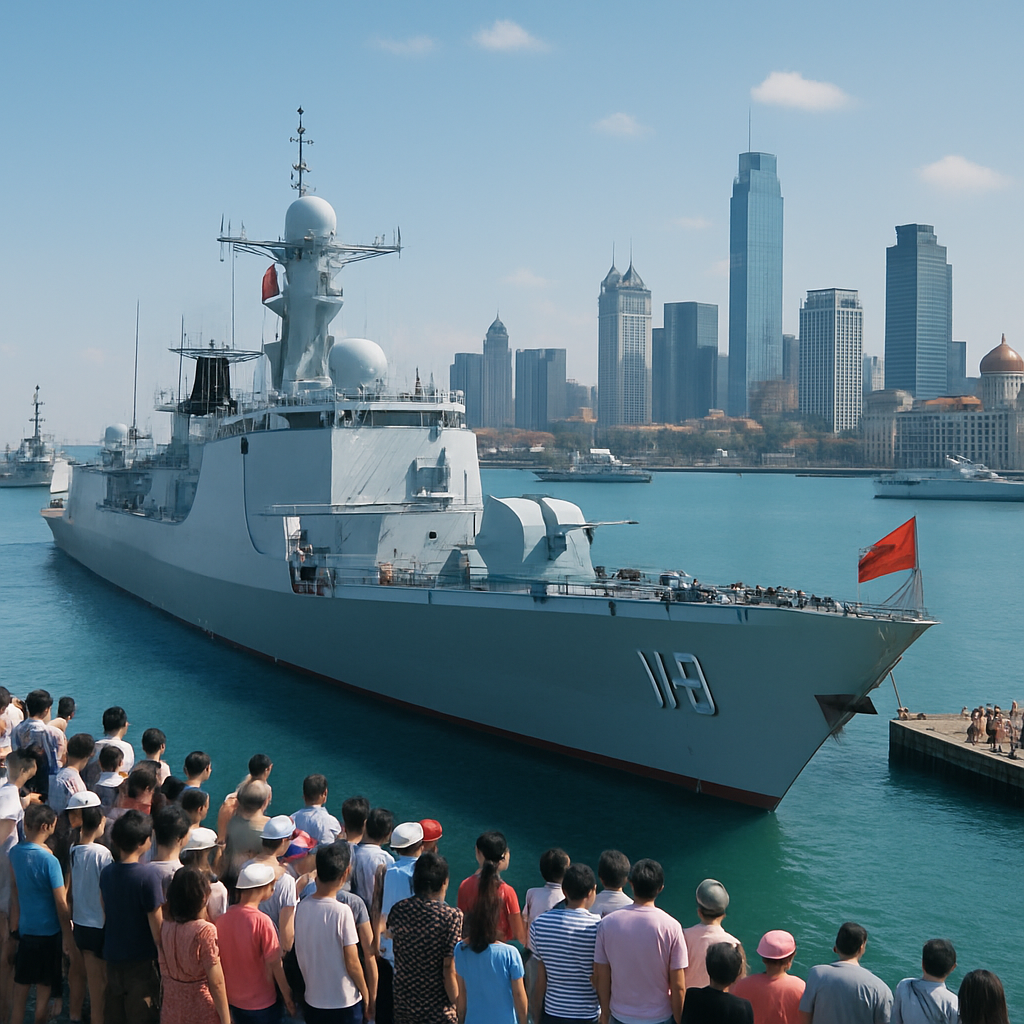
Warship docked in Chinese coastal city harbor with crowd on shore and other naval vessels in distance.

China Shifts Naval Diplomacy Inward

China's naval diplomacy is taking a dramatic turn inward, with a stunning display of 40 warships and public events in 10 cities, showcasing the People's Liberation Army Navy's strength to a domestic audience. This deliberate effort marks a significant shift in the PLAN's approach, prioritizing visibility at home over traditional fleet base displays or foreign port visits.

Analyst 207
Australian defense industry facility with machinery and equipment for guided weapons production.

Australia Bolsters Guided Weapons Program with $26 Billion Boost

Australia is supercharging its Guided Weapons Program with a whopping $26 billion boost, solidifying its national security and forging stronger global supply chains through diverse international partnerships. This massive investment surge is set to bolster the country's defense industry and pave the way for a more robust and resilient future.

Analyst 207
Government agency customer service area with unified AI-powered contact center interface on large screen.

Federal Agencies Target Unified AI-Powered Contact Centers

Federal agencies are shifting their approach to AI-powered contact centers, moving away from fragmented chatbots that created a disjointed experience for citizens, and towards a unified, journey-centric model that offers a seamless and consistent brand experience. This new approach aims to provide one cohesive face to the customer, spanning channels and touchpoints.

Analyst 207
Blurred terminal in cosmetics store with customers in background, hinting at data breach.

Rituals Discloses Data Breach Affecting Millions of Customers

Rituals recently discovered a data breach affecting millions of customers, compromising sensitive personal info like names, email addresses, and home addresses, but fortunately, no passwords or payment details were accessed. The company has since contained the incident, blocked unauthorized access, and notified authorities.

Analyst 207
Rows of computer servers and networking equipment in a brightly-lit data center with a single laptop in the foreground.

AI Targets Cloud Environments With Autonomous Attacks

Imagine a future where AI launches devastating cloud attacks with minimal human intervention - a threat that's no longer theoretical, but a harsh reality as demonstrated by a recent state-sponsored espionage campaign where AI executed 80-90% of the attack autonomously. Palo Alto Networks' Unit 42 has taken this threat to the next level by building a proof-of-concept AI model called Zealot that can execute end-to-end cloud attacks.

Analyst 207