[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongCybersecurity intelligence, threat analysis, and national security reporting.

Former national security officials are challenging the Pentagon's designation of Anthropic as a supply-chain risk, calling it a politically motivated move that's legally flawed and actually undermines national security. They argue that the designation was a misuse of authorities meant to address genuine threats, rather than a legitimate national security concern.
Researchers at Socket have uncovered a sneaky new wave of GlassWorm malware, this time hiding in 73 OpenVSX extensions that behave like sleepers - seemingly harmless at first, but turning malicious after a stealthy update. Six of these extensions have already been activated, unleashing malware on unsuspecting developers.

Medtronic recently reported a cyber breach by the ShinyHunters gang to federal authorities and the SEC, revealing that hackers had infiltrated its corporate IT system. Fortunately, the company has found no evidence that patient safety or electronic connections to customers were compromised.
North Korean hackers are using a sneaky tactic to target crypto executives: they pose as legitimate meeting attendees, harvesting video and audio to make future scams more convincing. They start by sending Calendly invites for fake catch-up meetings, then swap the link with a fake Zoom or Teams URL to gain their victim's trust.
The US Department of Justice has extradited Chinese national Xu Zewei from Italy to face charges of conducting cyberespionage operations on behalf of China's intelligence services, targeting victims including COVID-19 researchers. Xu's alleged hacking activities, directed by China's Ministry of State Security, spanned over a year, from February 2020 to June 2021.
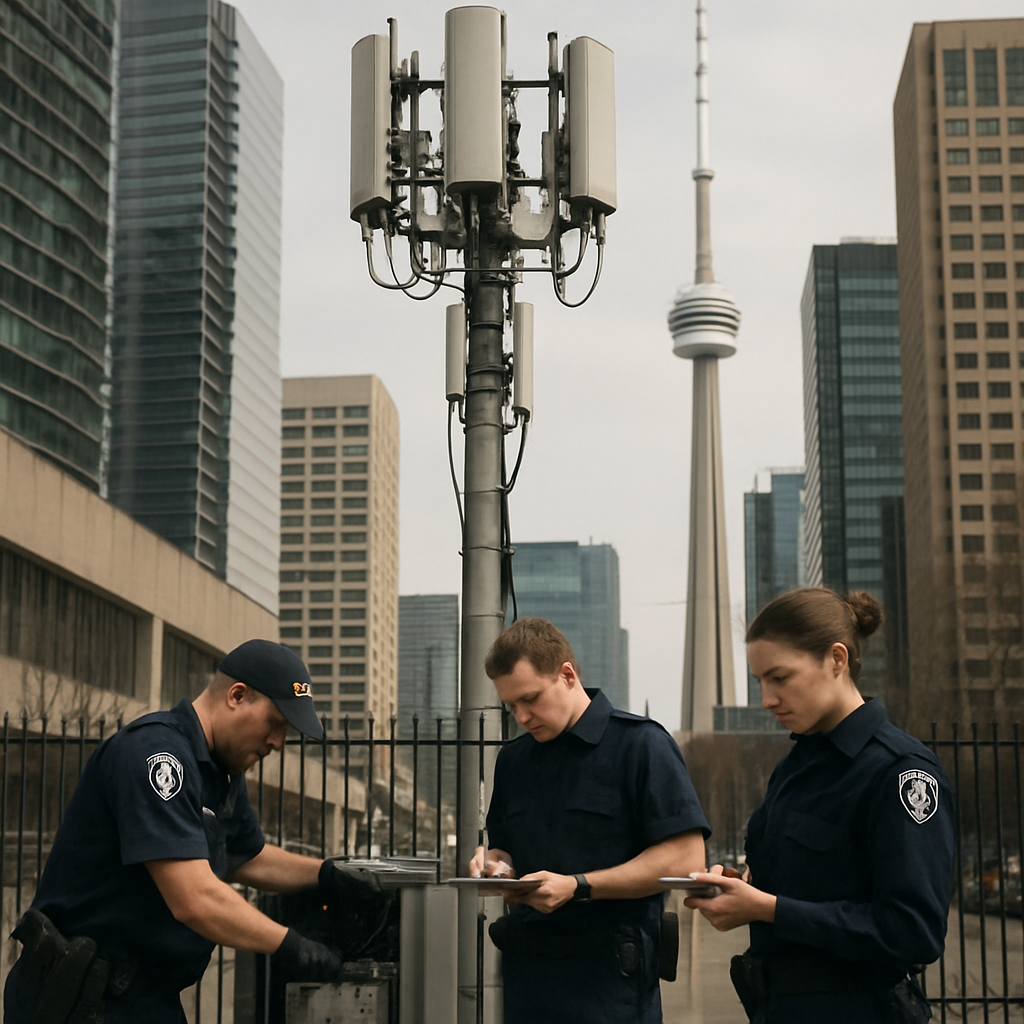
Imagine receiving a text from your bank or favorite store, but it's actually a sneaky scam - that's what happened in Toronto when a rogue cellular tower started sending out mass phishing texts to unsuspecting users. Canadian authorities cracked down on the culprit in a sting operation dubbed Project Lighthouse.
Itron sprang into action after detecting an unauthorized break-in on April 13, swiftly notifying law enforcement, and working with cybersecurity experts to investigate and remediate the breach. The company has since confirmed that it has prevented any further unauthorized activity within its corporate systems.

The Pentagon has supercharged its AI capabilities with Google's cutting-edge model, Gemini 3.1 Pro, now available on its enterprise generative-AI platform, GenAI.mil, marking a major milestone in American AI innovation. This powerful tool is set to revolutionize defense operations and will also be accessible to federal government users.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along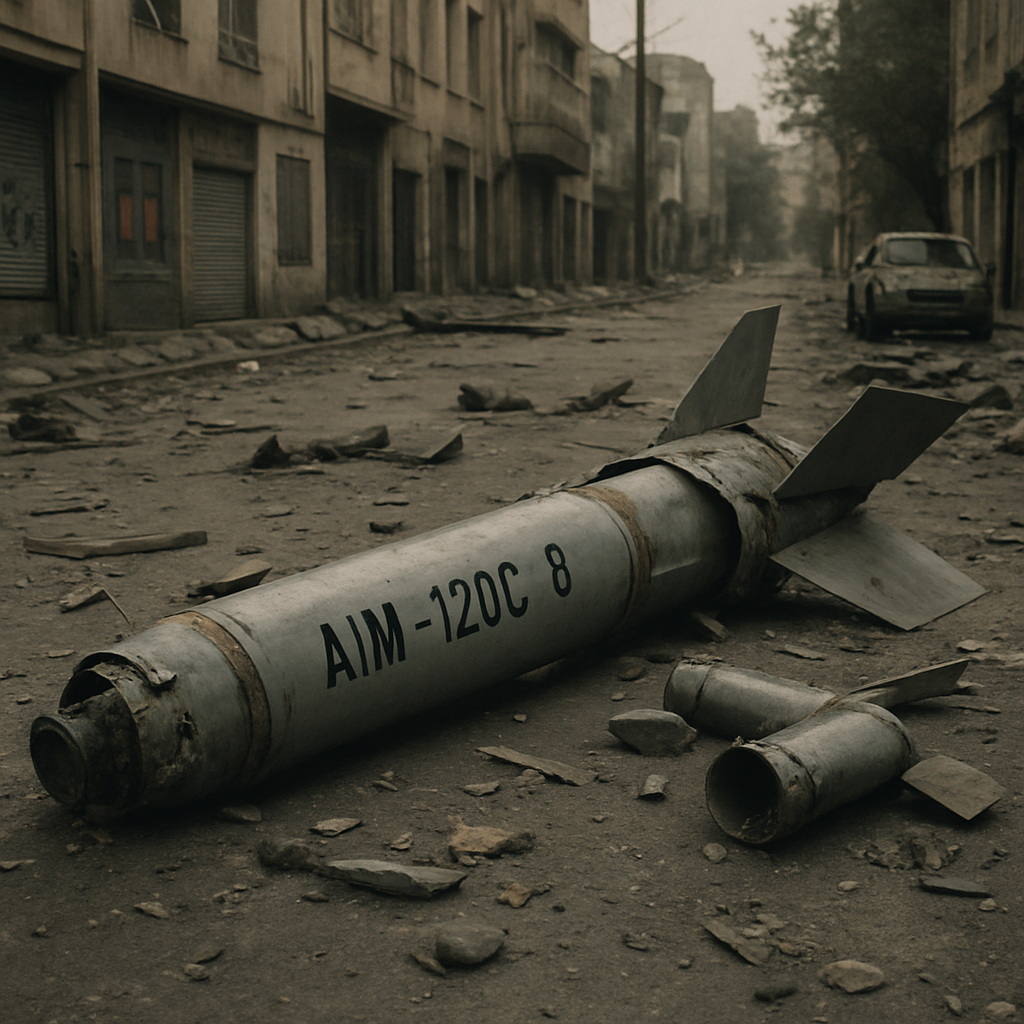
Ukraine has taken a significant leap in its defense capabilities with the deployment of advanced AIM-120C-8 missiles, a crucial upgrade to counter Russian air attacks. The recent recovery of AIM-120C-8 missile wreckage in Dnipro confirms Ukraine's access to these cutting-edge fire-and-forget missiles.

Meet BlackFile, a notorious extortion group wreaking havoc on the retail and hospitality sectors with high-stakes attacks, demanding seven-figure ransoms from its victims. With a modus operandi that includes impersonation and voice-phishing, this threat actor is using pressure tactics to get what they want.

Senators Maggie Hassan and Jim Banks are demanding answers from Navigate360 after a cyberattack compromised its anonymous tip line, putting the sensitive data of students, staff, and schools at risk. The breach allegedly exposed 93 gigabytes of data, sparking concerns over the safety and security of those who rely on the company's services.
Global military spending skyrocketed to $2.89 trillion in 2025 as nations worldwide ramped up their defenses in response to ongoing conflicts, rising tensions, and an increasingly unstable global landscape. Europe led the charge with a 14% surge in defense spending, reaching a staggering $864 billion.
In a major policy shift, Japan has relaxed its decades-long ban on defense equipment transfers, paving the way for controlled arms exports to bolster regional security ties. The move marks a significant departure from the country's 1976 arms embargo, allowing Japan to play a more active role in global defense.
Meet Pedro de Ayala, a 15th-century diplomat who took infosec to new heights by encrypting sensitive royal gossip with clever symbols - only to have his secrets cracked 500 years later by some codebreaking academics. His creative encryption method, which combined symbol substitutions with deliberate omissions, kept his messages safe from prying eyes for centuries.

A massive data breach at ADT has exposed the sensitive information of 5.5 million customers, including names, addresses, phone numbers, and email addresses, which is now being tracked by breach-tracking service Have I Been Pwned. This incident highlights the importance of staying vigilant about your personal data security.
Scammers are making a killing on social media, with nearly one-third of reported losses - a whopping $2.1 billion - originating from these platforms in 2025, according to the FTC. That's an eightfold increase in just five years, making social media a primary target for scammers to swindle unsuspecting consumers.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Checkmarx revealed that a security breach, linked to a March 23 supply chain attack, exposed sensitive GitHub repository data, which has now surfaced on the dark web. The incident has been contained, with no customer data compromised, as the affected repository was separate from Checkmarx's customer production environment.
The recent Medtronic data breach highlights a glaring vulnerability in the medical tech sector, with phishing attacks like this one proving that many organizations are still granting employees far more access than they need. Medtronic has confirmed the breach was contained within its corporate IT systems, with no evidence it impacted patient safety or product operations.
A malicious release of the popular elementary-data package on PyPI, which has over 1.1 million monthly downloads, allowed an attacker to steal developer data through a sneaky backdoor. This widely-used open-source tool for data observability in dbt pipelines became a prime target for the secrets-stealing campaign.
Meet fast16, a sneaky malware framework that's been around since 2005 - five years before the infamous Stuxnet - and is designed to quietly sabotage high-precision software by subtly altering numerical results. This stealthy approach can cause systems to fail, wear out faster, or produce false conclusions, making it a chilling precursor to modern cyber warfare.
The US Treasury has taken a major swipe at a massive scam network based in Southeast Asia, sanctioning 29 individuals and organizations, including Senator Kok An, in a bid to disrupt their financial infrastructure and protect American citizens from further losses. Americans lost a staggering $10 billion to these scams in 2023, a 66% surge from the previous year.

The US Space Force is taking a major leap in missile defense, awarding $3.2 billion in prototype contracts to 11 companies, including industry giants and innovative newcomers, to develop space-based interceptors that can counter threats with speed and agility. This move marks a significant step in the development of a new layer of US missile defense.
A massive data breach at ADT has put 5.5 million people's personal info at risk, including names, phone numbers, addresses, and sensitive details like dates of birth and Social Security numbers. The breach, linked to the ShinyHunters extortion group, has left millions vulnerable to potential identity theft and scams.
Itron has launched a swift investigation into a recent cyber security breach, taking immediate action to assess, mitigate, and contain the incident with the help of external advisors and law enforcement. The company currently believes the breach will not have a significant impact on its operations.