[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
Meet Deep#Door, a sneaky Python-based backdoor framework that hides its malicious payload inside a batch dropper, making it super hard to detect on Windows systems. By embedding its code, it dodges network-based detection and slips into restricted environments with ease.

The moment a new asset goes live with a public IP address, the clock starts ticking - and within minutes, attackers are circling, waiting to pounce on unsuspecting targets. In just 24 hours, a newly exposed asset can go from discovery to compromise, with threat actors exploiting vulnerabilities at an alarming rate.
A shocking 1.8 million RDP servers are currently vulnerable to cyberattacks, leaving them open to exploitation by opportunistic hackers. Canadian authorities have also cracked down on SMS blaster phishing, arresting three men and seizing a device that sent fake texts to unsuspecting phones.

US government agencies have just released a game-changing guide to help protect critical infrastructure systems with practical, layered security strategies. The new zero-trust guidance provides a tailored approach for operational technology environments, balancing safety and uptime needs with robust security measures.
Meet CVE-2026-31431, aka "Copy Fail," a newly discovered Linux flaw that leaves major distros vulnerable to root access - and it's surprisingly easy to exploit, affecting a wide range of systems from 2017 to 2026.
Malicious actors have been using 44 cleverly disguised GitHub facades to spread EtherRAT malware, masquerading as legitimate admin and dev tools between December 2025 and April 2026. These fake repositories were designed to manipulate search results, leading victims to download a malicious MSI installer hidden in a second, secret GitHub account.

UK higher education institutions are under cyber attack, with a staggering 98% reporting breaches in the past year - a sharp jump from 91% the year before. This near-universal vulnerability raises serious concerns about the sector's online security.
Meet DEEP#DOOR, a sneaky Python-based backdoor framework that's harvesting browser and cloud credentials by exploiting a tunneling service, and learn how it infiltrates systems through a clever sequence of stealthy steps. This sophisticated threat starts with a simple batch script that disables Windows security controls and ends with a fully featured Remote Access Trojan (RAT).
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Phishing attacks remain a major threat, with nearly half of UK businesses falling victim to these scams in the past year, and a staggering 85% of breaches involving phishing as the primary entry point. These attacks often rely on human error, using tactics like impersonation emails and fake logins to trick staff into handing over sensitive information.
A cPanel bug, tracked as CVE-2026-41940, was exploited in the wild as a zero-day vulnerability before a patch was released, with attackers making execution attempts as early as February 23, 2026. The flaw forced vendors and hosting providers into emergency mitigation, with cPanel finally releasing a fix on April 28, 2026.
In a major crackdown on crypto scams, a global operation led by Dubai Police has arrested 276 suspects and shut down nine fraudulent investment centers, dealing a significant blow to scammers who thought they were safe from law enforcement. This coordinated effort with US, Chinese, and Thai authorities has brought global justice to victims of these crimes.

A recent investigation by TrendAI has uncovered a concerning China-linked espionage campaign, with a novel spy group infiltrating over a dozen critical networks across Poland and Asia, leaving behind a lingering threat that's experts' biggest worry. The threat group, tracked as Shadow-Earth-053, has been actively compromising networks since December 2024.
A critical cPanel vulnerability, rated 9.8 under CVSS, has been discovered, allowing attackers to craft a simple sequence of requests to bypass authentication and gain root access to servers, putting millions of domains at risk. Emergency patches are available to fix this gaping security flaw.
In a major crackdown on investment scams, Europol and international authorities have dismantled a sophisticated Albanian investment fraud ring, arresting 10 suspects and seizing nearly €900,000 and 443 computers. The alleged scammers are accused of swindling victims out of at least €50m through their professionalized operation.
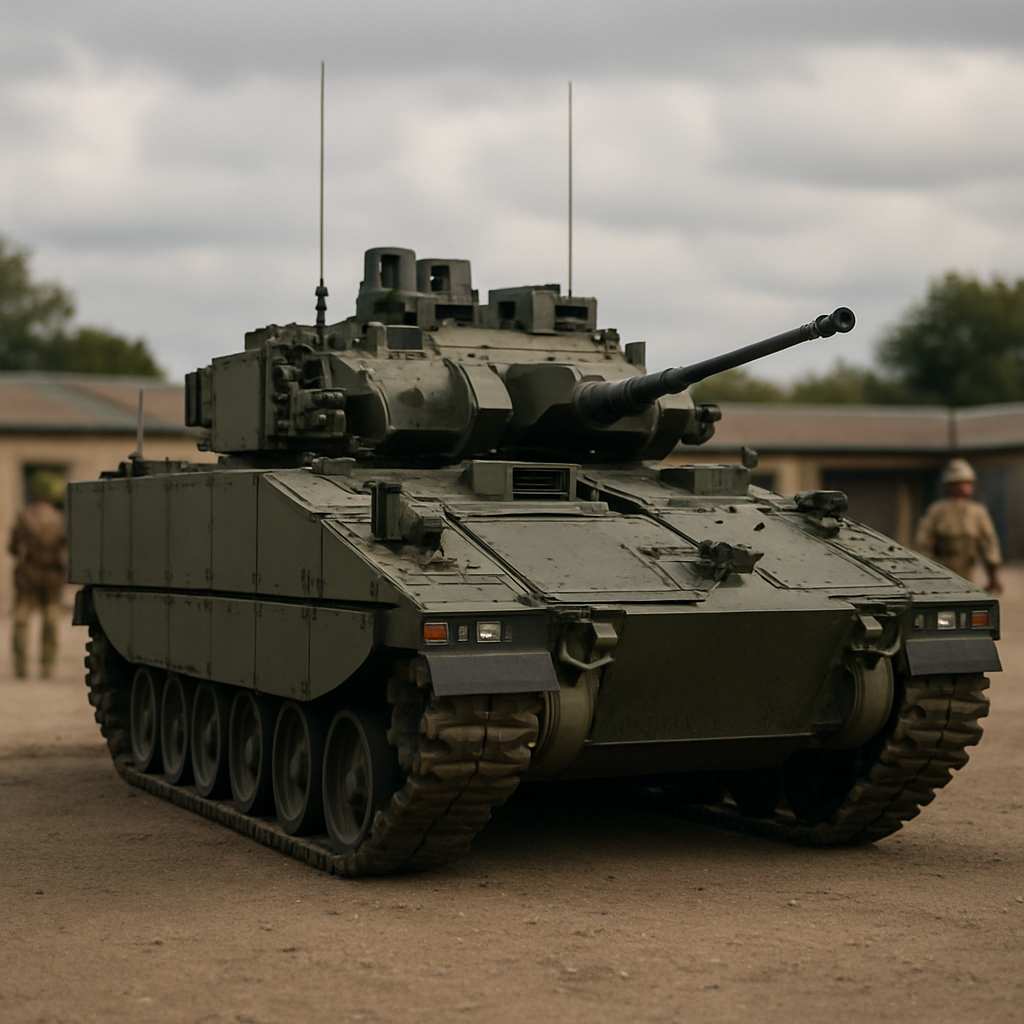
The UK Ministry of Defence has cleared the £6B Ajax armored vehicle for duty, despite reports of troop injuries, with Minister Luke Pollard emphasizing that the safety of personnel is non-negotiable. The move comes after investigators failed to pinpoint a single cause for the symptoms experienced by crews during a recent military exercise.
Organizations are facing a harsh reality: understanding cyber risk is only half the battle, as the real challenge lies in responding effectively when a threat strikes. Marsh's 2026 People Risks report reveals that cyber-related challenges, including cyber-threat literacy, top the list of people risks, ahead of technological change and skills shortages.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
A newly discovered Linux flaw, dubbed "Copy Fail," allows unprivileged users to gain root access on major distributions by exploiting a logic error in the kernel's cryptographic subsystem. This high-severity vulnerability, tracked as CVE-2026-31431, poses a significant threat to Linux systems, enabling attackers to write controlled bytes into the page cache of readable files and escalate privileges.

A fintech firm's most sensitive secrets were left exposed in a shared spreadsheet, with a password that was embarrassingly simple - literally a combination of the company's name and the year. The shocking discovery was made by Stanislav Kazanov during a routine compliance audit, when he stumbled upon a widely accessible SharePoint folder containing a file ominously titled Prod_DB_Root_Creds_DO_NOT_SHARE.xlsx.
Google patched a critical flaw in Gemini CLI that allowed hackers to inject malicious code and take control of host systems, thanks to a report from Novee Security. The vulnerability, scoring a perfect 10.0 on the CVSS scale, has been fixed in recent updates to the @google/gemini-cli and google-github-actions/run-gemini-cli packages.
US Space Command is taking a strategic approach to its funding priorities, opting out of submitting an Unfunded Priority List for FY27 since its top needs are already covered in the President's Budget request. This decision follows extensive collaboration with the Department of Defense and the services to secure a generational investment in space capabilities.

The US Marines are proactively exploring the need for theater ballistic missile defense capabilities, with Lt. Col. Robert Barclay revealing that studies and simulations are underway to determine if this is a crucial requirement for the service's future.
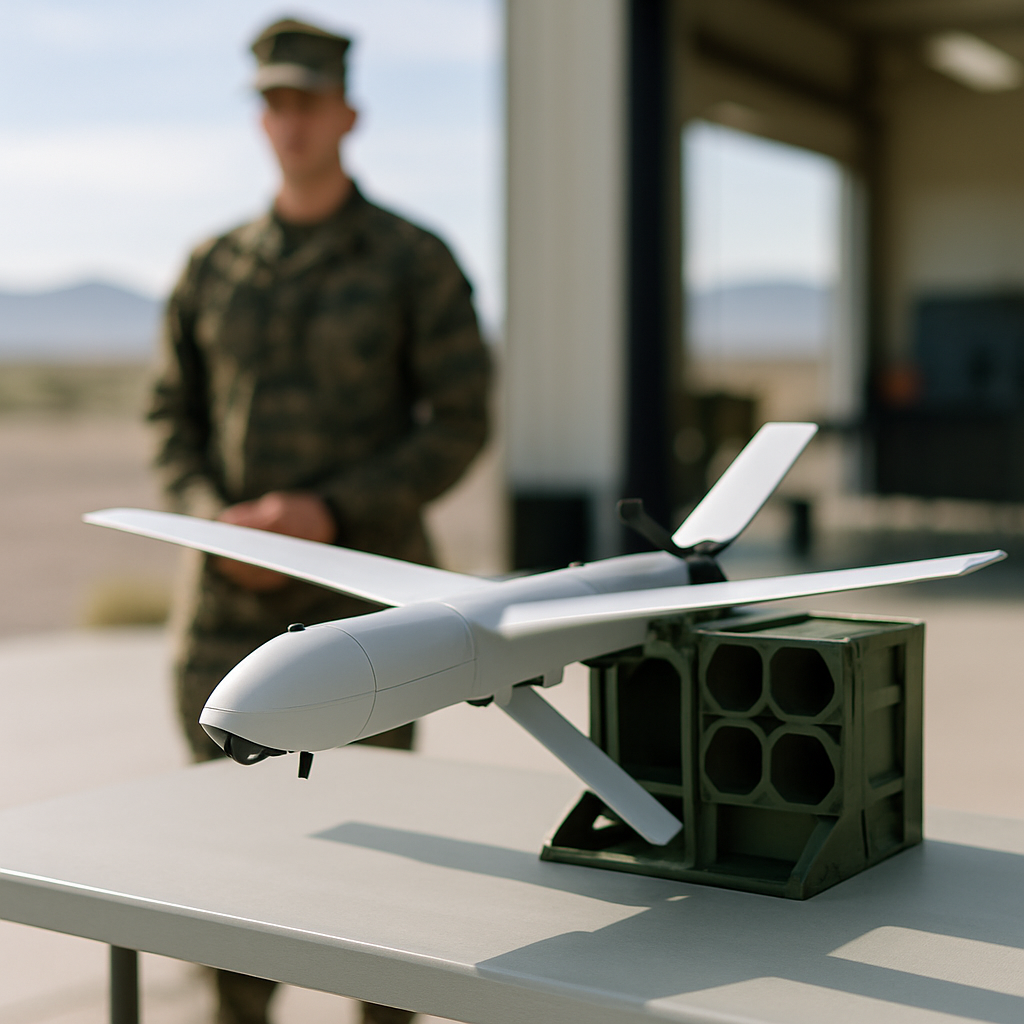
Get ready for a game-changer on the battlefield: the Marine Corps is set to deploy its Light Loitering Munition in June, marking a major milestone with the delivery of live warheads to operational units. This cutting-edge Organic Precision Fires system is the result of rigorous testing and training, and is poised to revolutionize the Marines' firepower capabilities.
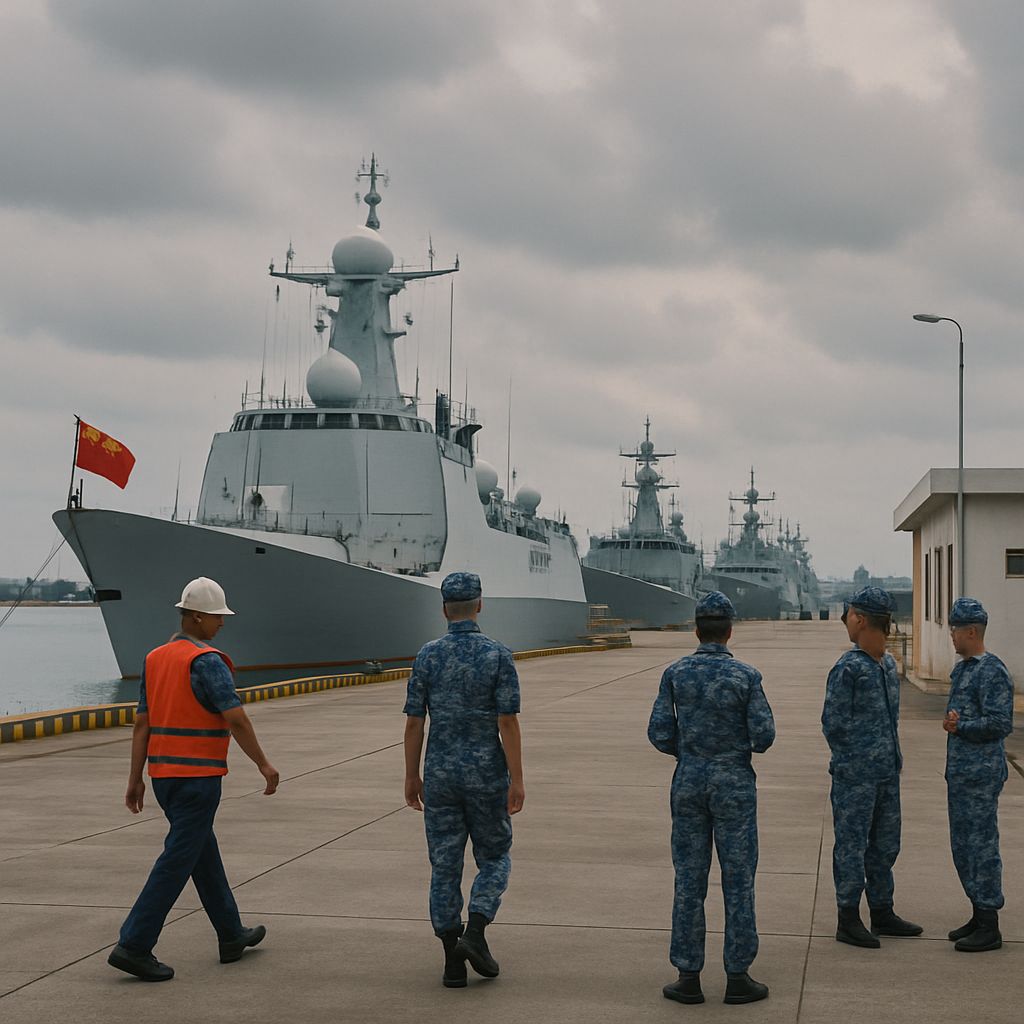
China's growing military presence in the Indo-Pacific waters has become a pressing concern for countries like Australia, India, and Japan, as its increasing frequency and normalization embolden Beijing's coercive behaviour. With its two-ocean strategy and Belt and Road momentum, China is expanding its naval and intelligence footprint across the Indian and Pacific oceans.
The US Marine Corps' top strategist, Lt. Gen. Stephen Sklenka, just issued a stark warning: China has emerged as a peer military rival, matching the US in nearly every measure of national influence. This bold declaration signals a major shift in the global balance of power.