[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.

Rep. Summer Lee is raising red flags about the Trump Administration's cozy ties to commercial spyware, specifically its willingness to let US investment flow into sanctioned companies like NSO Group and use their tools to infiltrate cell phones. She's demanding answers from the Commerce Department about its role in these dealings.

As AI use grows, a hidden risk is emerging: malicious inputs can alter model behavior, bypassing safeguards and putting enterprises at risk. This "prompt injection" tactic is like phishing, targeting the link between user and system to wreak havoc.

Marlon Ferro, the mastermind behind a brazen crypto heist, has been sentenced to 6.5 years for stealing $230 million in cryptocurrency using a cunning mix of online scams and targeted home invasions. He served as the group's instrument of last resort, carrying out daring residential burglaries to get his hands on valuable digital assets.
Being incident response ready means more than just having a plan - it requires immediate visibility into identity and authentication access, including investigator-level read access to crucial systems. Without this visibility, teams are left making blind containment decisions and piecing together timelines with guesswork.
MicroStealer malware is on the loose, targeting education and telecom sectors with a sneaky credential theft attack that's harvesting sensitive data, including browser credentials, cryptocurrency wallets, and system info. This stealthy threat uses a multi-stage delivery chain to quickly swipe valuable info and send it to hackers.

Palo Alto Networks has issued a warning about a critical zero-day vulnerability, CVE-2026-0300, that allows state-sponsored hackers to exploit its firewalls and execute arbitrary code with root privileges. The company is tracking limited exploitation attempts, linked to a cluster of likely state-sponsored threat activity.
Beware of a fake Claude AI site that's really a malware trap: a 505MB archive disguised as a legitimate installer delivers a sneaky Windows backdoor called Beagle. Clicking the download button on the site leads to trouble, not the AI tool you might be expecting.
Even a seasoned expert like Roger Grimes, CISO advisor at KnowBe4, has fallen victim to the pitfalls of weak passwords - in a surprising turn of events, he recalling a time when he accidentally gained access to a client's network using the password "rosebud", famously lifted from a film plot.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Malware was discovered hidden in certain Daemon Tools Lite installers, prompting developer Disc Soft to issue a clean build and confirm a supply chain attack had compromised their system. A malware-free version was released within 12 hours of notification.
Malicious Python packages on PyPI were found to be secretly delivering a new malware called ZiChatBot, which uses Zulip APIs to receive instructions. These seemingly harmless packages covertly dropped malicious components, highlighting the importance of vigilance when downloading code from public repositories.

Scammers are using Vercel's AI tools to create super-realistic phishing sites that mimic popular brands, making it easier for them to trick victims into handing over sensitive info. This clever tactic allows attackers to quickly recreate malicious pages, even if they're taken down.
A dozen critical vulnerabilities in the vm2 Node.js library can be exploited by hackers to break free from sandbox restrictions and run malicious code on vulnerable systems. This serious security flaw has been assigned high CVSS scores, emphasizing the urgent need for users to patch their systems.
The US has officially added cyberattacks to its counterterrorism arsenal, vowing to use offensive cyber operations against those who plan to harm Americans or support terrorist plots. This bold move is part of a new strategy that combines diplomatic, financial, and covert actions to disrupt and deter threats to US interests.
The Department of Defense is leveraging agentic AI tools to revolutionize its operations, with Emil Michael reporting that tasks that once took two weeks can now be completed in just three hours, freeing up teams to focus on high-priority work. This game-changing tech has already shown tremendous success since its rollout on the GenAI.mil platform in December.

Discover how the US is opening its doors to foreign investors, with Commerce Secretary Howard Lutnick leading the charge, promising to make deals happen and offering support for securing visas and setting up operations. America First now means America together, with the government actively seeking partnerships and investments from abroad.
Palo Alto Networks has issued a warning about a zero-day flaw in its PAN-OS software, tracked as CVE-2026-0300, which allows unauthenticated remote code execution with root privileges. This buffer overflow vulnerability in the User-ID Authentication Portal poses a high risk to PA-Series and VM-Series firewalls.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Australia's national security ecosystem is drowning in data, but struggling to cut through complexity - and simply adding more information can make things worse, not better. To stay ahead of evolving threats, its security architecture needs a fresh approach that prioritises what matters most.
In a display of military precision, a US-led live-fire exercise sank a decommissioned Philippine Navy patrol corvette, BRP Quezon, in the strategic Luzon Strait, roughly 50 miles offshore. The vessel, a former World War II-era minesweeper, met its target fate near the Paoay Sand Dunes on Luzon's coast.
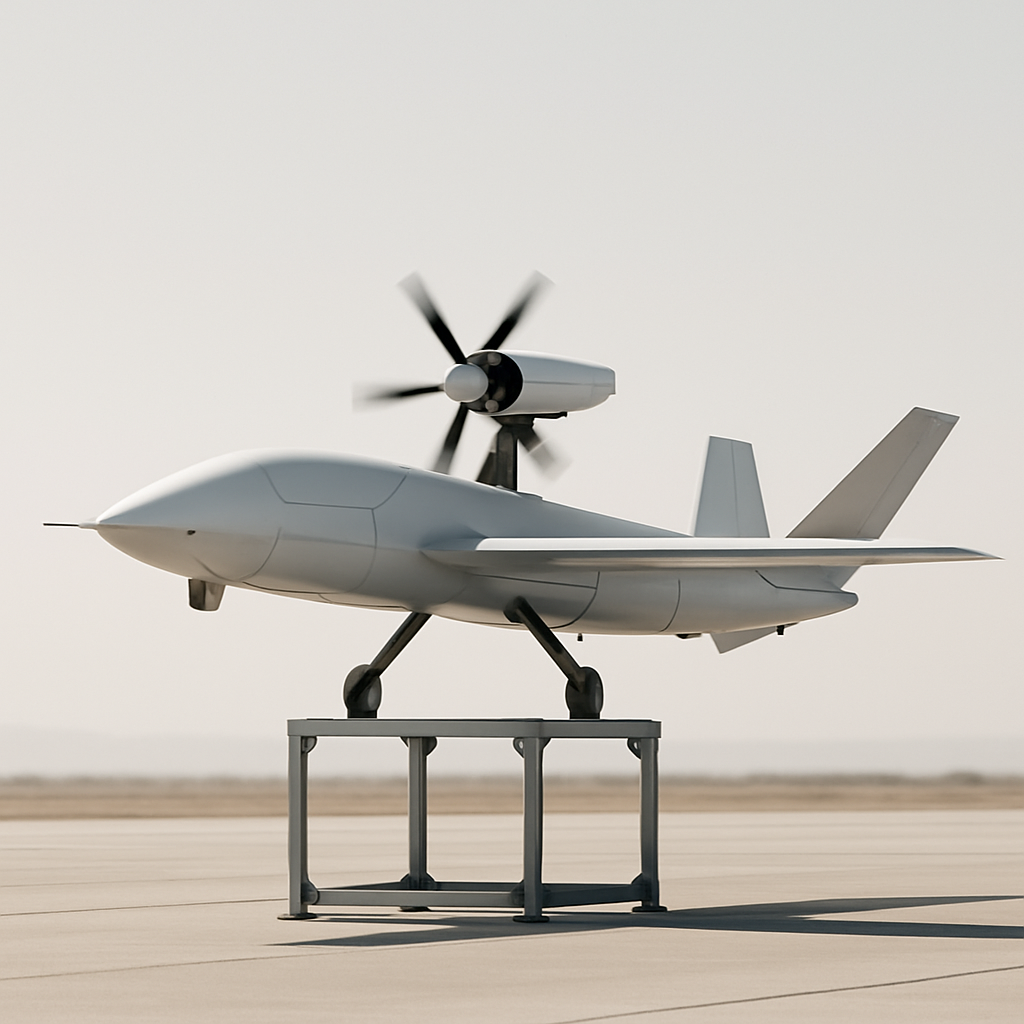
The XRQ-73 drone has successfully taken flight, marking a major milestone in DARPA's hybrid-electric propulsion program, with more test flights planned to further mature the innovative technology. This achievement is a significant step forward, overcoming complex technical challenges and paving the way for future advancements.
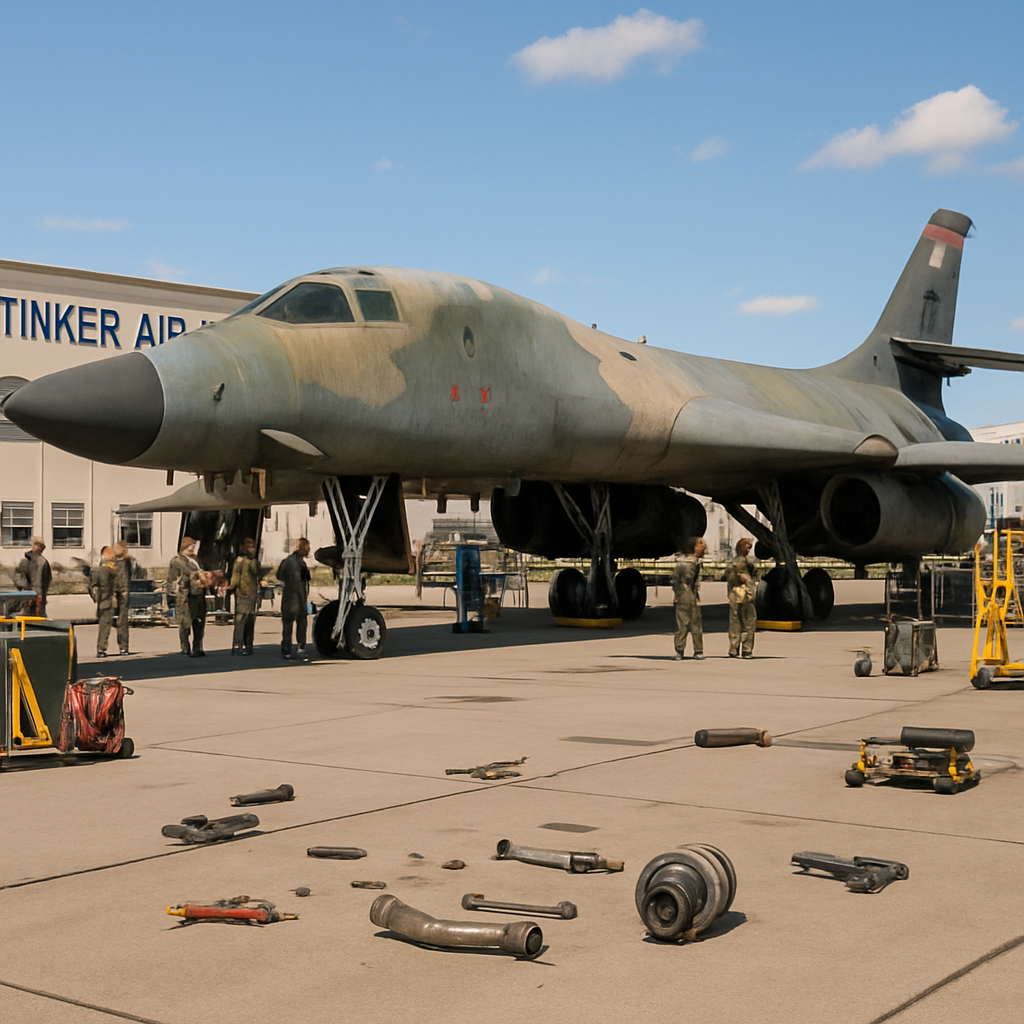
In a remarkable feat of engineering, the US Air Force has breathed new life into a B-1B bomber, reviving it from the Arizona boneyard after a nearly two-year overhaul that saw over 500 components replaced. The Oklahoma City Air Logistics Complex led the massive depot effort, involving over 200 airmen and civilians working tirelessly to return the jet to full operational status.
The Air Force is taking a major leap forward by exploring the integration of AI into its Air Operations Command system, with the goal of equipping planners and operators with cutting-edge tools to stay ahead in the game. By engaging with industry leaders, the government aims to spark innovation and maximize competition for this critical upgrade.
Palo Alto Networks has warned of a critical zero-day vulnerability, CVE-2026-0300, being exploited in the wild, allowing unauthenticated attackers to execute code with root privileges on certain firewalls. This flaw affects a limited number of customers with exposed User-ID Authentication Portals.

The US military has taken a firm stance against Iranian-flagged vessels, as demonstrated by the recent disabling of the oil tanker M/T Hasna with F/A-18 cannon fire, after it ignored warnings to halt its journey to an Iranian port. The US blockade on Iranian ports remains firmly in place.
Malaysia is taking a proactive approach to resolve a potential hiccup in its missile purchase deal with Norway, with Defence Minister Mohamed Khaled Nordin vowing to seek clarifications through diplomatic channels. The country is keen to find a solution that serves its best interests and ensures its defense readiness remains on track.