[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
OpenAI is ramping up Europe's cybersecurity game by granting restricted access to its cutting-edge vulnerability-finding model, GPT-5.5-Cyber, to dozens of European organizations through its new Trusted Access for Cyber program. This move will empower defenders to swiftly protect systems and respond to threats, while also addressing security concerns with greater transparency.
A newly discovered vulnerability, dubbed Dead.Letter, threatens Exim builds that use GnuTLS, allowing attackers to exploit a use-after-free flaw in BDAT handling and potentially execute malicious code. This critical flaw can be triggered when a specific sequence of BDAT and TLS commands is sent, leading to heap corruption and a heightened risk of code execution.
Fortinet has patched a critical remote code execution vulnerability in its FortiAuthenticator and FortiSandbox products, which could have allowed unauthenticated attackers to run unauthorized code or commands. The company has released fixed builds to address the flaw, tracked as CVE-2026-44277, and urges users to update to versions 6.5.7, 6.6.9, or 8.0.3 to stay secure.
The US Navy is taking bold steps to reclaim its maritime dominance, with Acting Secretary Hung Cao calling for urgency and commitment to overcome America's shipbuilding capacity crunch. The Navy's Fiscal Year 2027 Shipbuilding Plan proposes a strategic solution: supplementing domestic yards with targeted overseas shipbuilding.

In a groundbreaking revelation, the Pentagon's Chief Digital & AI Officer disclosed that the recent operation against Iran utilized Palantir's Maven Smart System to strike 13,000 targets in just 38 days. This unprecedented scale of AI-driven military action marks a significant shift in the Defense Department's approach to modern warfare.
The Pentagon has just dropped a bombshell, releasing a batch of previously classified images and footage of Unidentified Anomalous Phenomena, some of which date all the way back to the 1940s. Get ready to dive into the fascinating and often bizarre world of UAPs like never before!
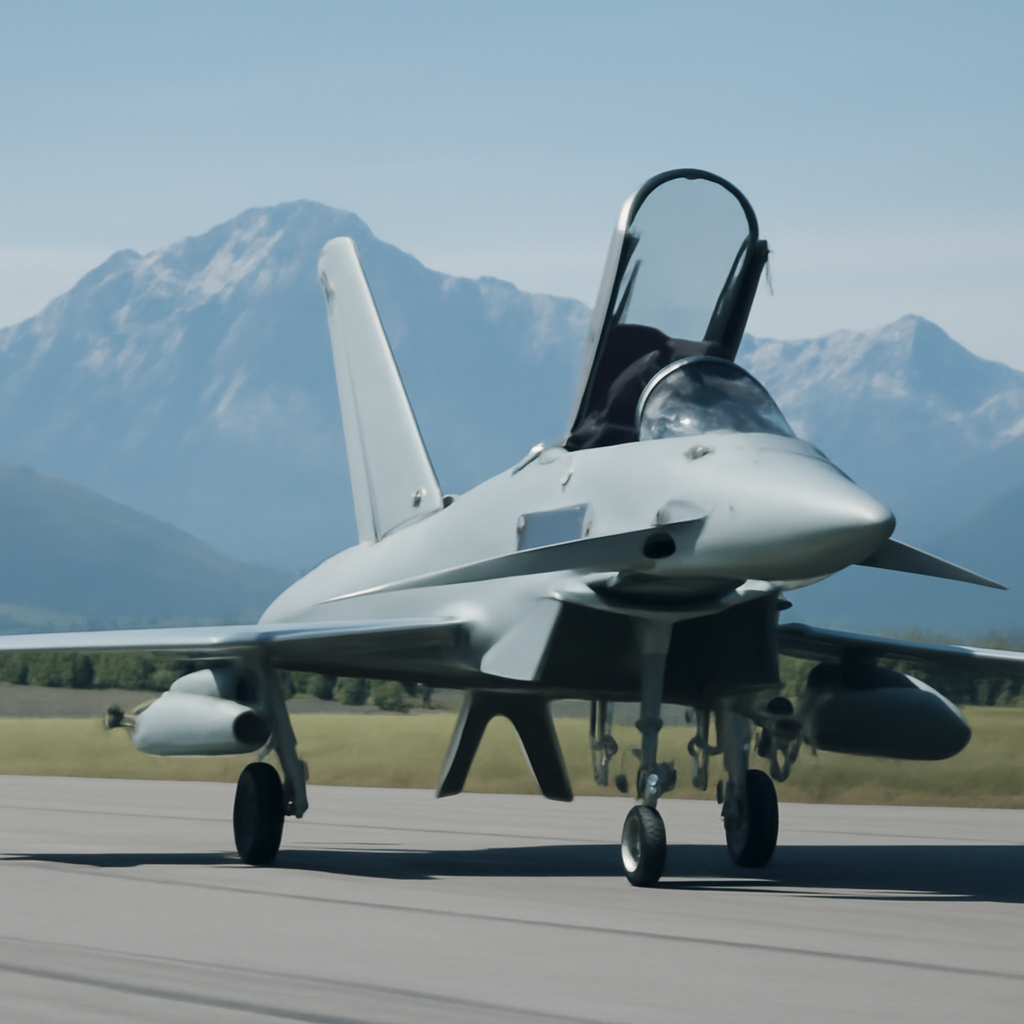
The Austrian Air Force sprang into action, scrambling Eurofighter Typhoons not once, but twice, after US military aircraft strayed into its airspace on consecutive days. On both occasions, the Austrian defenders swiftly identified the intruders - two PC-12 turboprops - and escorted them out, with the second incident prompting a Priority A response at 12:31.
Russia's muted Victory Day parade in Red Square has raised eyebrows, with experts reading it as a telling sign of the Kremlin's growing vulnerability in its war with Ukraine. By citing security concerns, Moscow watered down its usual display of military might, sparking whispers of weakness.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentStay one step ahead of scammers with Android 17's cutting-edge security features, including robust protection against banking scam calls and device theft. Android 17 will work hand-in-hand with banking apps to detect and block spoofed calls, giving you an added layer of defense against financial threats.
Ransomware attacks may be on the decline, but don't let your guard down - attackers are getting smarter, ditching encryption, and selling stolen data, with the manufacturing sector alone losing a whopping $18 billion in just three quarters. The threat may have evolved, but the damage and risk remain very real.
On Pakistan's turbulent western frontier, the Khyber Pakhtunkhwa Police are fighting a losing battle against terror, with chronic underfunding exacerbating the threat to their lives. The devastating May 9 attack in Fateh Khel, Bannu, which claimed 15 policemen's lives, is just the latest tragic reminder of this mismatch between threat and reward.
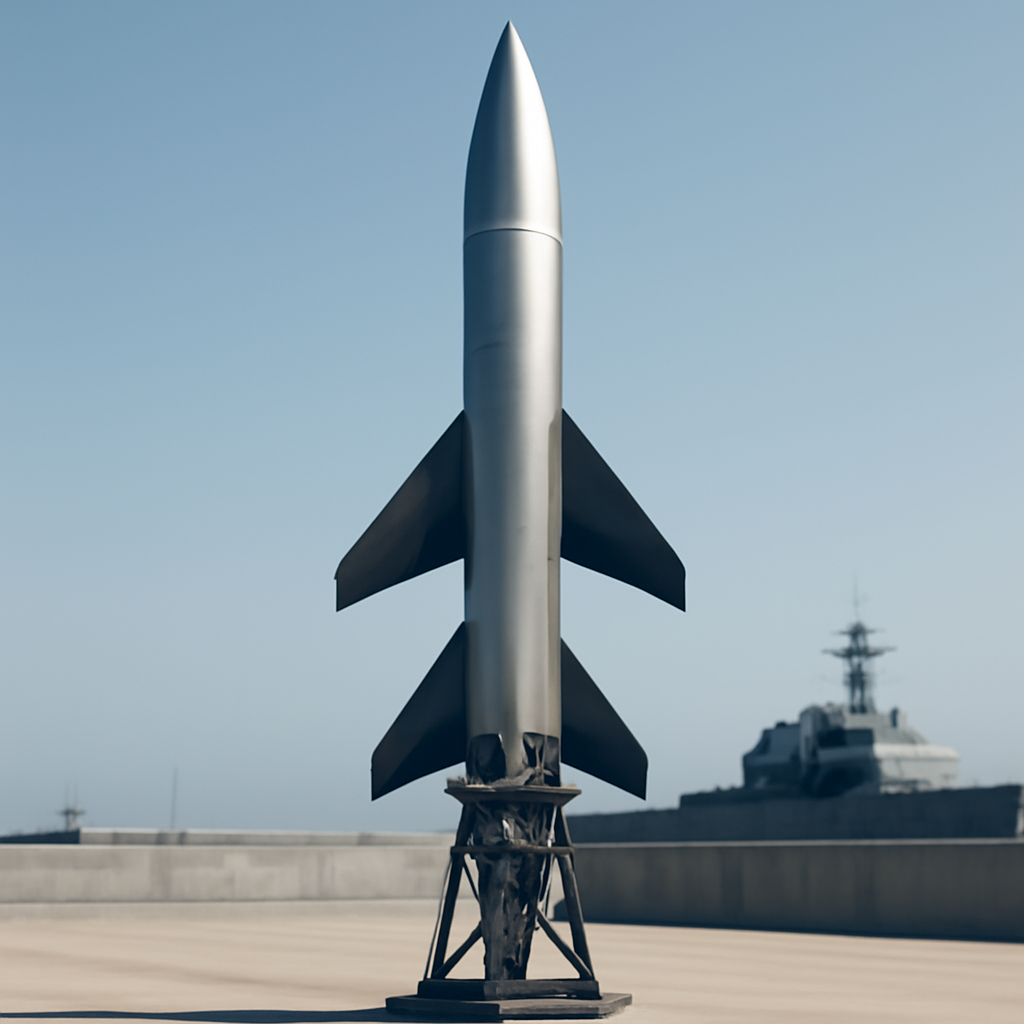
The US Air Force is reviving its ARRW Hypersonic Missile program with a game-changing upgrade, adding an anti-ship capability that enables the missile to track and take down moving targets, including ships at sea. The service is seeking over $296 million in funding to turn this ambitious concept into a tested reality.
Taiwan's defence capabilities are in jeopardy after lawmakers approved a slashed defence budget of $25 billion, down from President Lai's proposed $40 billion, with the reduced funds leaving the island's Porcupine Strategy vulnerable. This cut comes as a significant blow, with a senior research fellow warning it weakens Taiwan's defence capabilities.

Google's new Intrusion Logging feature is a game-changer in the fight against spyware, helping digital forensics researchers uncover sophisticated attacks on Android devices. By recording security incidents like device unlocking and spyware installation, it provides crucial evidence to investigate and take down these threats.

The Department of Energy is putting modernization at the forefront of its agenda, recognizing its critical role in driving technological leadership, securing critical infrastructure, and bolstering national energy resilience. By making modernization its top priority, the department aims to tackle rising threats and achieve key national objectives.
The game-changing moment came when a zero-day threat, nearly sparking a mass attack, was uncovered - and forensic evidence revealed its exploit code was astonishingly built by an AI model. This breakthrough highlights how AI is revolutionizing exploit development, making it faster and more accessible to malicious actors.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along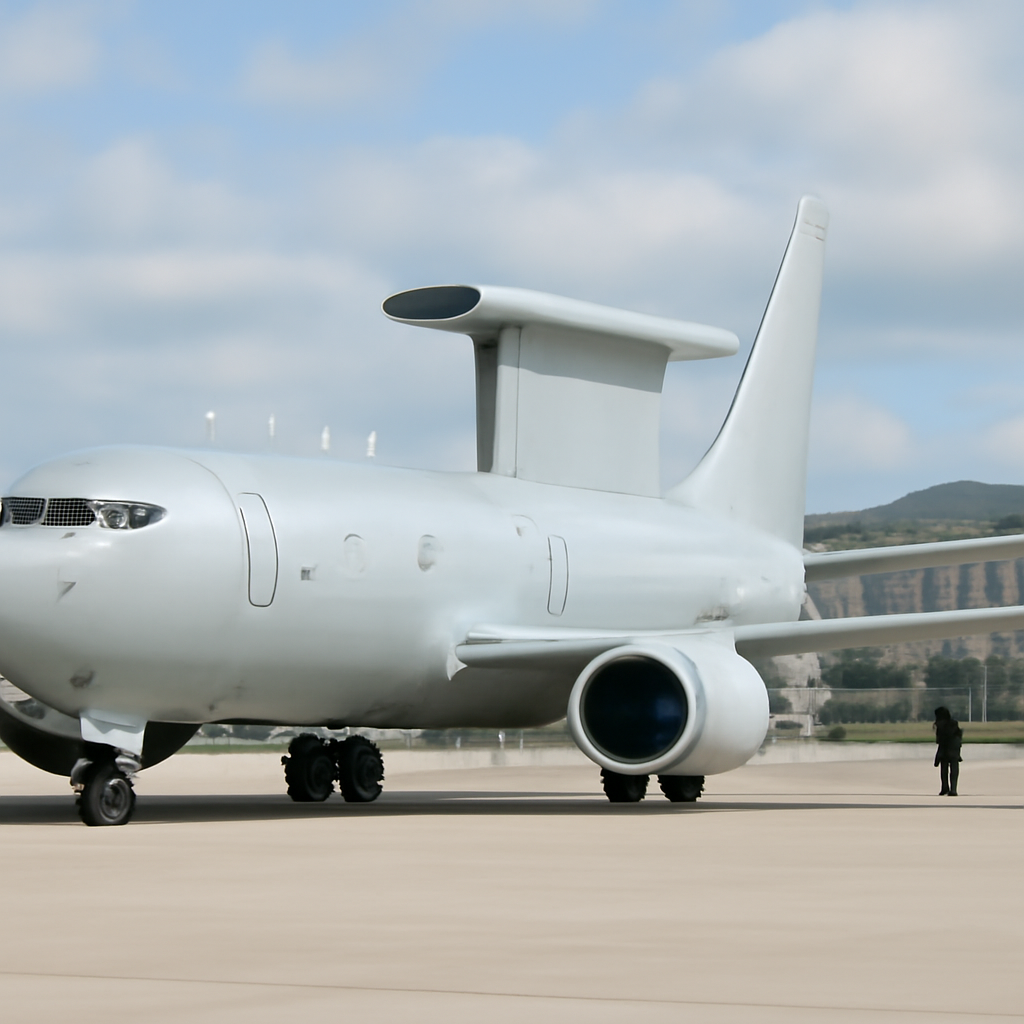
The Pentagon is breathing new life into the Boeing E-7 Wedgetail, reversing its plan to cancel the program and instead sending a budget amendment to revive funding. Defense Secretary Pete Hegseth confirmed the change, citing the aircraft's potential to fill critical gaps on the modern battlefield.

RubyGems has temporarily halted new account registrations amid a significant surge in malicious packages, with security experts warning of a major attack on the platform. The move comes as Mend.io, the organization responsible for securing RubyGems, works to contain the incident.
Škoda's online shop was recently hacked, exposing customer data after attackers exploited a vulnerability in the e-commerce software. The company has since fixed the issue, alerted authorities, and is working with a forensics team to investigate.

As AI systems increasingly become integral to business operations, they're also emerging as a major insider threat, with 7 in 10 APAC organisations now identifying AI as their top data security risk. This new breed of threat is forcing companies to rethink their cybersecurity strategies and take a closer look at the vulnerabilities AI can introduce.
Malware attackers have infiltrated the TanStack npm packages, modifying 84 artifacts in a supply chain attack that could compromise major developer ecosystems. The malicious code, aimed at stealing credentials, was published across 42 packages on May 11, with some, like @tanstack/react-router, downloaded over 12 million times weekly.
OpenAI has launched Daybreak, an innovative initiative that helps developers build secure software from the ground up, accelerating cyber defenders and continuously securing software. By integrating cutting-edge models like GPT-5.5, Daybreak shifts security to the forefront of the software development lifecycle.
A US bank has taken swift action, self-reporting a data leak that exposed sensitive customer information to an unauthorized AI app, sparking concerns over the volume and sensitivity of the compromised data. The bank's proactive disclosure to regulators and customers highlights its commitment to transparency in the face of a data-handling lapse.
Meet TrickMo C, a sneaky new variant of the Android banking trojan that's turning infected devices into programmable network pivots, allowing hackers to intercept sensitive data from banking and cryptocurrency wallet users in France, Italy, and Austria. This malicious software is packed with powerful tools, including reconnaissance, SSH tunnelling, and SOCKS5 proxying capabilities.