[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
The NSA and CISA are sounding the alarm: identity security risks are now the frontline in federal cybersecurity, with Active Directory and Entra ID being prime targets for cyber attackers. Recent incidents show that nearly 75% of major federal cyber breaches in the last five years involved compromised identities.
Critical vulnerabilities in two popular Joomla extensions have been exploited in the wild, allowing attackers to gain remote control of affected sites by uploading malicious files. The Cybersecurity and Infrastructure Security Agency has sounded the alarm, adding the flaws to its Known Exploited Vulnerabilities catalog.
Get ready for a faster, more intuitive Windows Search experience! Microsoft has overhauled its search function to deliver more relevant results, making it easier to find what you need, whether you're launching an app, locating a file, or adjusting settings.
The US Treasury has cracked down on ransomware networks by sanctioning a VPN provider and its administrator, who allegedly helped cybercrime groups hide their tracks and evade detection. This move aims to disrupt the tools and services that enable devastating attacks causing billions of dollars in losses to US critical infrastructure providers.
Lidl has warned customers in Belgium and the Netherlands that a data breach exposed their personal info, after unidentified individuals briefly accessed a file containing customer data stored with a third-party IT provider. The breach affected online customers in Germany, Belgium, and the Netherlands, but Lidl stresses that its online shop system itself was not compromised.
Elon Musk has made a bold promise to erase all user data uploaded to Grok Build before now, assuring users that their content will be completely deleted. This move comes after a researcher discovered that Grok Build was inadvertently storing entire Git repositories, including sensitive files and commit history, in a Google Cloud Storage bucket.
In a shocking discovery, researchers uncovered 148 malicious npm packages that masqueraded as harmless student web proxies, but secretly turned browsers into a powerful DDoS botnet for nearly two weeks. These packages, cleverly disguised with benign names like "Lucide" and "Riverbend Tutoring," hid their true intentions beneath a façade of ads and monetization scripts.
The US Treasury has cracked down on a VPN service that helped ransomware groups hide their tracks, announcing sanctions against First VPN Service and its Ukrainian administrator, Dmytro Rashevskyi. This move follows a multi-jurisdictional law enforcement operation that dismantled the service in May 2026.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
In a major crackdown on Russian Coms Fraud, UK authorities have charged five individuals linked to a notorious platform that enabled scammers to hide their identities and swindle victims by impersonating trusted institutions. The platform, shut down in 2024, had been facilitating these deceitful calls since 2020.
Microsoft uncovered a sneaky year-long operation by the ShinyHunters extortion group, who exploited trust in Salesforce's OAuth system to steal sensitive data, using clever vishing tactics to trick employees into granting access to a malicious app. The attackers posed as IT support, convincing victims to authorize a fake Data Loader tool that allowed them to make API calls and search for valuable credentials.
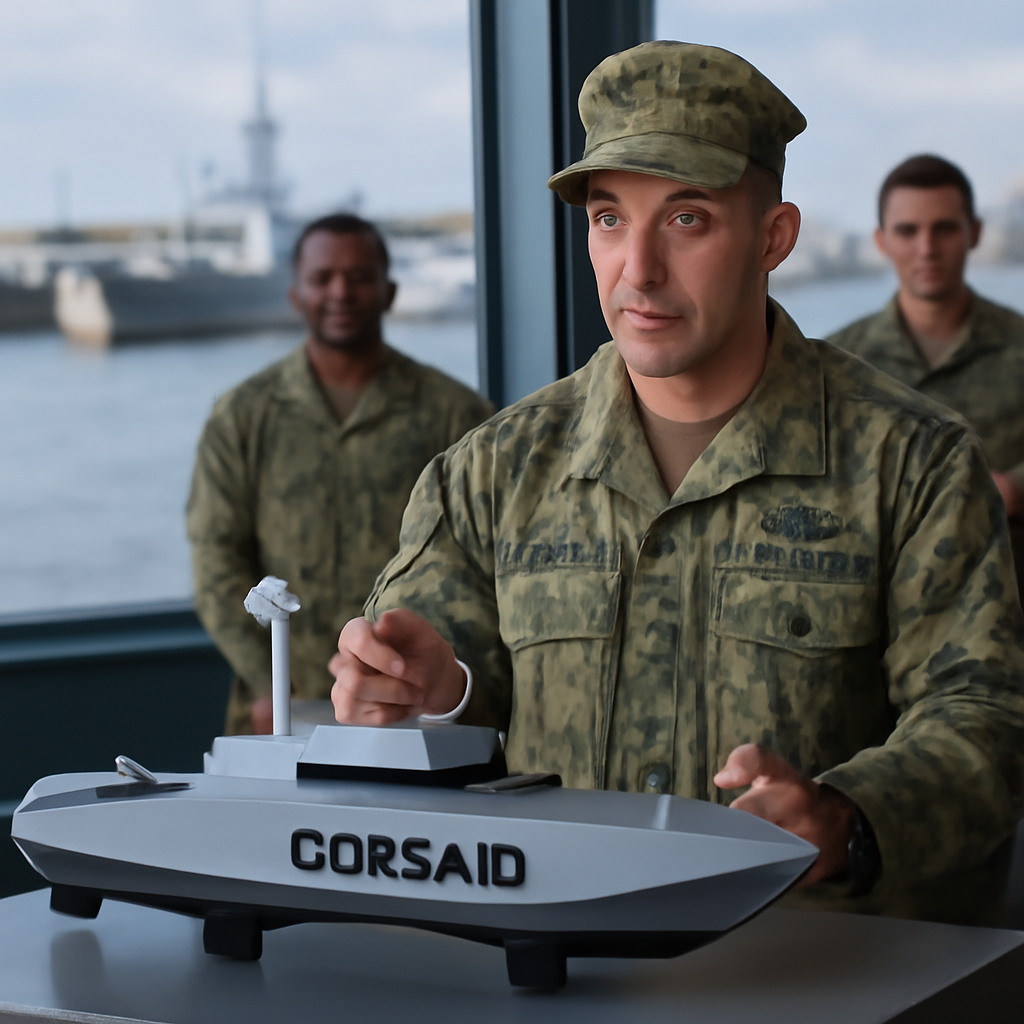
In a historic first, US forces have launched a daring combat operation against Iran using kamikaze drone boats, successfully striking a submarine and ship maintenance facility at Bandar Abbas Naval Base. The bold move, carried out by CENTCOM forces, marks a significant escalation in the use of sea drones in military operations.
Russian hackers, linked to the Federal Security Service's Center 16, have been actively targeting critical US and foreign networks across multiple sectors, including defense, energy, and healthcare, for over a decade. This ongoing threat has compromised networks in various industries, posing significant risks to national security and global stability.
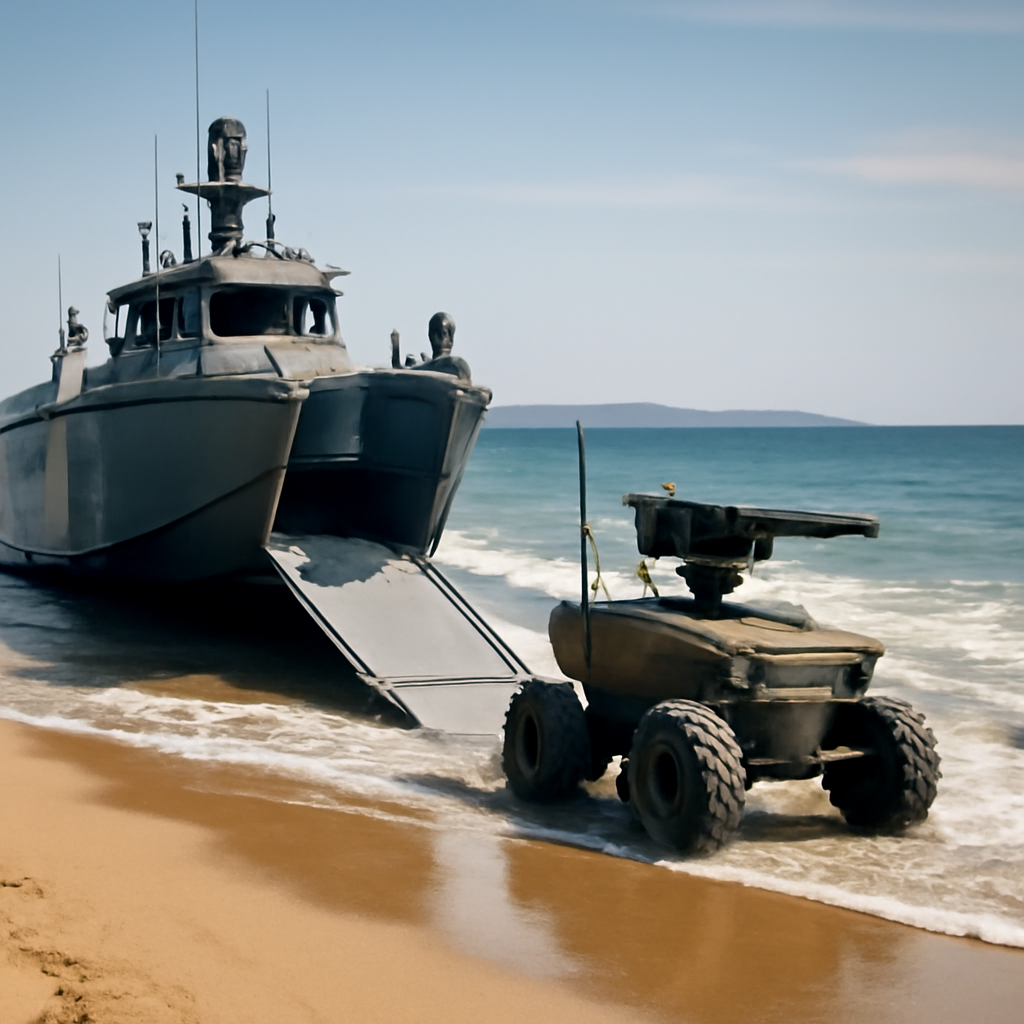
In a groundbreaking operation, Ukraine's 123rd Separate Territorial Defense Brigade has successfully deployed an armed robot behind Russian lines using a drone boat, marking a new era in modern warfare. The daring mission was captured on video, showing the robot, armed with a 7.62mm machine gun, engaging a target on the occupied Kinburn Spit.
The European Union is cracking down on Russia's notorious cyber-espionage group, Turla, with coordinated sanctions aimed at disrupting their years-long campaign of malicious activities. Nine Russian individuals and four entities, including the FSB's Center 16, have been targeted in the punitive measures.
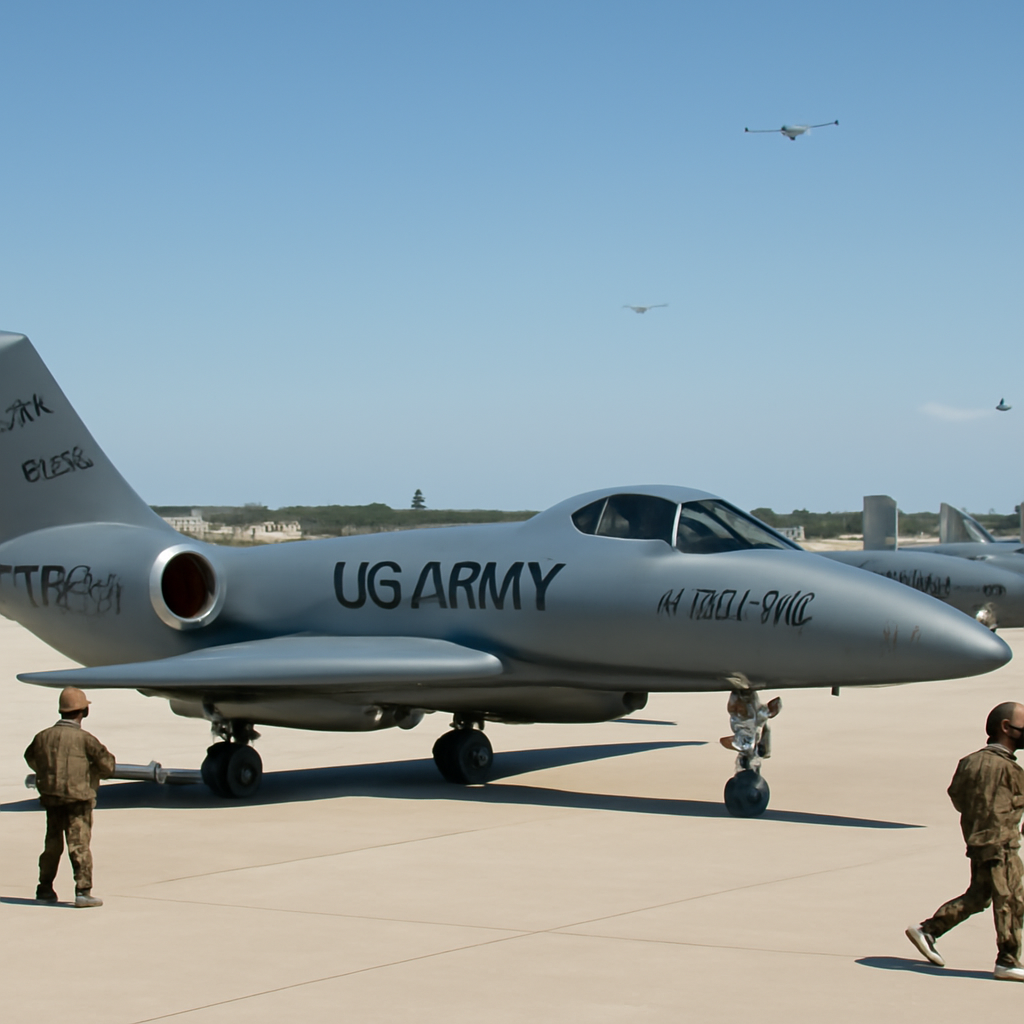
The US Army is taking aerial intel to new heights with its HADES jets and a pioneering drone battalion, set to be based at Fort Hood, Texas, boosting its surveillance and reconnaissance capabilities like never before. With a combined range that's unmatched, the Army is poised to access previously unreachable intel.
South Korea is dangerously positioned as a "dagger in the heart of Asia," making it impossible for Seoul to escape the devastating consequences of a major Taiwan conflict. With US forces and civilians on the peninsula, Seoul will be under immense pressure to act quickly and decisively.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Nihon Kotsu, Japan's largest taxi operator, suffered a devastating cyberattack that forced an emergency shutdown of its systems, disrupting taxi operations nationwide. The malware infection was detected on Saturday morning, prompting swift action to contain the breach.
A malicious version of the Jscrambler npm package was published, infecting nearly 1,500 downloads with infostealer malware within a two-hour window before being removed and replaced with a safe version. The incident was quickly contained, but users who downloaded the compromised package between releases 8.14 and 8.20 may be at risk.
Beware of a sneaky malware that's masquerading as a legitimate Apple tool to steal your macOS credentials! This malicious software, known as CrashStealer, can infiltrate your password managers and even target over 80 browser-based cryptocurrency wallets.
A shocking discovery was made about the popular ModHeader extension, used by 1.6 million Chrome and Edge users, which contained a hidden browsing history collector that thankfully remained dormant. Fortunately, both Google and Microsoft swiftly removed the extension from their stores after it was uncovered.
Meet CrashStealer, a sneaky new macOS malware that uses clever tactics to evade detection, including validation of the victim's login password to harvest sensitive data. This native C++ stealer quietly fetches a second-stage payload to steal a broad range of secrets from compromised machines.
Imagine giving an attacker the keys to manipulate your AI assistant's memories - and all it takes is one ordinary-looking email to rewrite what it thinks it knows about you. With a new tool called MemGhost, hackers can plant false memories in AI agents, altering their responses and actions over time.
A shocking security blunder exposed the inner workings of a massive Evilginx phishing campaign, revealing 218 victims across 12 countries, with nearly 94% being corporate targets, who were quietly harvested over the course of a year. The careless mistake, made on a Budapest virtual private server, gave researchers a rare glimpse into the sophisticated phishing ecosystem.
The UK and EU have called out Russia's Federal Security Service for a brazen cyberattack on Poland's power grid, saying it's just another example of their reckless attempts to wreak havoc across Europe. The attack, attributed to FSB's Centre 16, was foiled, but serves as a stark warning for infrastructure operators to stay vigilant.