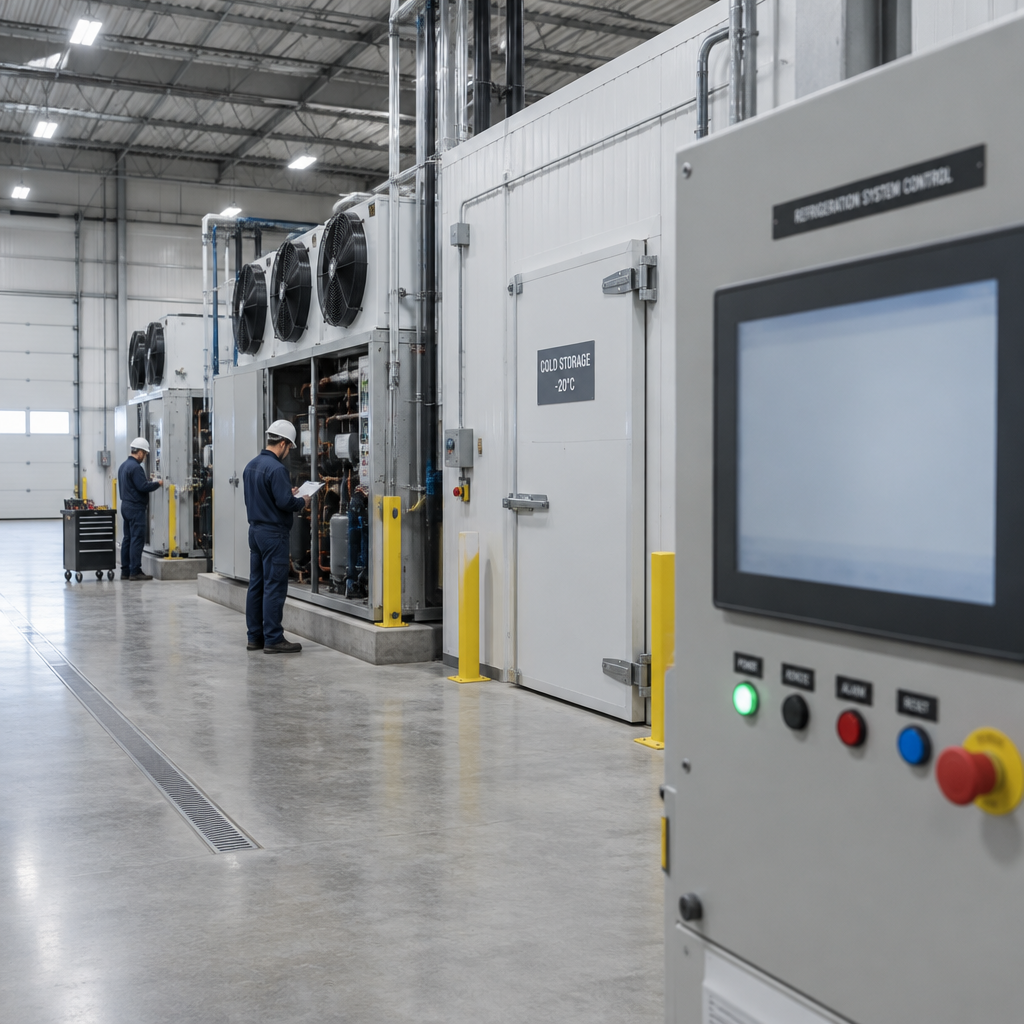
“Every organization that depends on refrigeration and monitoring systems should assume it could be a target. We urge you to review the joint fact sheet and take action now to close known security gaps,” CISA’s acting executive assistant director for cybersecurity Chris Butera warned in a government advisory published November 5.
Why U.S. agencies stepped in
On November 5 the Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI) and other federal agencies published a joint advisory urging organizations to harden industrial refrigeration and cold-chain monitoring systems. The agencies said they “are aware of malicious cyber activity targeting industrial refrigeration and cold chain monitoring systems globally,” pointing to a string of recent incidents in Europe where attackers accessed internet-connected refrigeration controllers and attempted to alter temperature settings.
Concrete incidents in Europe and their impacts
The advisory follows several high-impact incidents. On October 11 it was reported that supermarket chains in France and other European countries were forced to destroy food stock after attackers compromised systems administered by refrigeration provider Danfoss, reportedly programming units to reach temperatures as high as 50 °C (122 °F). A similar disruption was reported on November 1, affecting supermarkets in at least nine European countries. More recently, a cyber-attack on refrigeration equipment provider Coolworld was reported to have driven cold storage rooms at France’s National Blood Service (EFS) to 110 °C (230 °F), an extreme change with immediate risk to medical supplies.

This site is the portfolio.
OSINTSights runs on Cloudflare Workers, D1, R2, and Vectorize, with an AI pipeline on Hetzner ARM. Nubivance designed, built, and operates it. We do the same for clients.
See what we buildHow the attacks are said to work
The authoring agencies described a consistent operational pattern: actors exploiting vulnerabilities or weaknesses in unpatched or internet-accessible controllers to remotely alter settings and force units into continuous heating and defrost cycles. They outlined specific techniques observed or likely to be used, including authentication bypass, arbitrary code injection and weak configurations that enable remote access to internet-exposed systems.
Immediate mitigation steps for operators and owners
The joint advisory set out immediate actions security teams should take. The list below reproduces the controls the agencies recommended for organizations that operate or depend on refrigeration and cold-chain systems:
- Ensure control system devices, particularly controller panels, are not exposed to the internet.
- Should remote access be necessary, protect these systems using a firewall or edge device and update them to the latest version to reduce security vulnerabilities.
- Isolate operational technology devices from business networks.
- Change default passwords and implement strong authentication policies, including phishing-resistant multi-factor authentication (MFA).
- Establish a structured lifecycle management process to identify, retire and replace legacy devices that are end of life.
- Limit access to only those devices and IP addresses authorized to make changes.
- Maintain backup systems offsite and offline and regularly test them.
In their advisory, the agencies highlighted sectors where refrigeration systems are integral — healthcare, chemical, food and agriculture, and transportation — and urged heightened vigilance where automated and remote temperature monitoring is widely used for continuous logging, defrost cycles and energy management.
What Censys’ data shows
Data published by Censys on November 5 showed a significant reduction in directly internet-exposed refrigeration controllers tied to the incident vendors. Censys reported a 53% reduction in internet-exposed controllers across Danfoss StoreView and Copeland/Dixell XWEB products that were compromised during the supermarket incidents on October 11 and November 2, respectively. Censys characterized the drop as consistent with provider action or owners disconnecting devices following the incidents.
What this means for healthcare, food retailers, and cold‑chain providers
Healthcare providers: Facilities that rely on automated refrigeration for blood, vaccines and other medical supplies will be watching the Coolworld report closely; the agencies’ warning and the reported rise to 110 °C (230 °F) at EFS underscore potential immediate patient-safety and supply-chain consequences.
Food retailers: Supermarkets and cold-storage operators that use commercial controllers such as Danfoss StoreView or Copeland/Dixell XWEB face both inventory loss and operational disruption; the reported destruction of food stock after temperatures were driven to 50 °C (122 °F) is the clearest real-world example cited in the advisory.
Cold‑chain providers and vendors: Providers of refrigeration control systems are under pressure to patch internet‑exposed controllers, block unauthorized remote access and accelerate lifecycle management for legacy devices — steps the advisory explicitly prescribes and that Censys’ exposure drop suggests some operators have already begun.
So far, the government and reporting have not attributed the incidents to a particular threat actor. The joint advisory and the observed reductions in exposed devices signal urgent, practical defensive work rather than answers about who conducted the intrusions. The immediate challenge is operational: to close the remote-access pathways that enable attackers to turn cooling systems into heating hazards, test offline backups and protect devices that cannot be taken offline quickly.
The next clear milestone on this story will be whether U.S. operators heed the November 5 advisory and whether further technical analysis links the European incidents to identifiable intrusion methods or actors. Until then, the record is dominated by the visible consequences — ruined inventory, disrupted services and a swift government bid to push basic controls into practice.