Tag: supply chain
1739 articles
ConnectWise Supply-Chain Attack Targets Microsoft 365 Tenants
A recent supply-chain attack on ConnectWise's Cloud Backup service has compromised at least 162 Microsoft 365 tenants, prompting urgent concerns for managed service providers and administrators. The attackers were traced to a single IP address, with Microsoft confirming malicious activity and unauthorized authentication attempts.
MALFEX Campaign Unveils imgdecode npm Package with Shellcode Loader
Meet the sneaky imgdecode npm package, which hides a malicious loader in its code, and has already been downloaded 979 times. This package secretly downloads and injects encrypted shellcode into a new process, making it a serious threat to Windows users.
Ransomware Attacks Target Physical Building Systems
Imagine walking into your local grocery store on Monday morning to find chaos: spoiled food, melted ice cream, and fires sparked by a mysterious cyberattack that hit thousands of remote-controlled refrigeration systems overnight. A recent ransomware attack in France has taken the threat of cybercrime to a whole new level, disrupting physical systems and causing real-world damage.
Hackers Exploit Compromised Credential to Breach 173 Microsoft 365 Tenants
Security researchers have uncovered a disturbing breach: hackers exploited a stolen Microsoft 365 credential to infiltrate 173 tenant accounts of ConnectWise Cloud Backup, gaining broad access to sensitive data. The attackers used the compromised credential to obtain Microsoft Graph tokens, allowing them to snoop on mailboxes, OneDrive, SharePoint, Teams, and directory data.
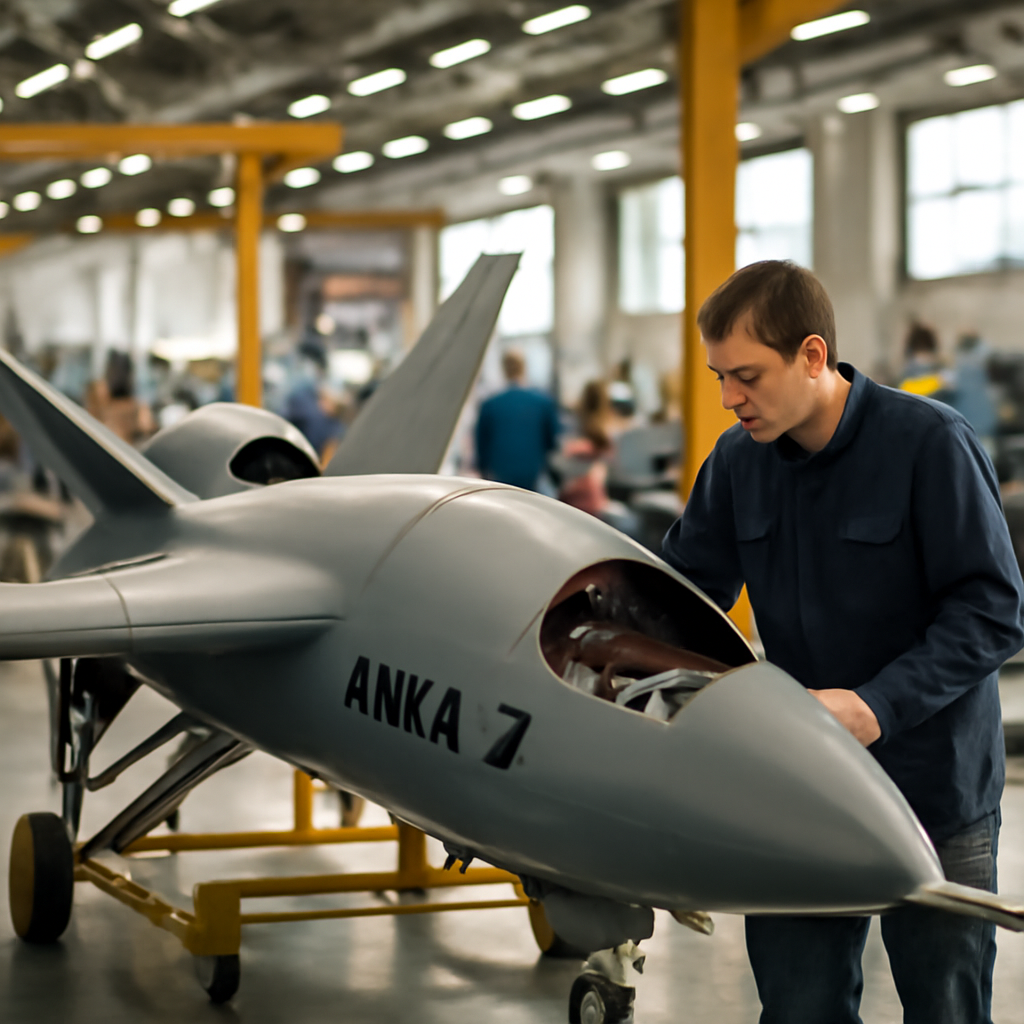
Turkish Aerospace Expands Anka 3 Drone Production with Upgraded Line
Turkish Aerospace is taking its Anka 3 Drone production to the next level with an upgraded line that boosts payload capacity to 1.75 tons, allowing the aircraft to carry more munitions to meet growing national requirements. The company is set to open a second production line in November, with the first aircraft expected to roll out soon.
BAE Systems Breach Disrupts US Bankruptcy Court Notices
A cybersecurity incident at BAE Systems has brought the US bankruptcy court notice system to a grinding halt, with the company's Bankruptcy Noticing Center (BNC) websites taken offline and notice production suspended nationwide. The disruption affects every federal bankruptcy court in the United States.
Chinese hackers exploit BeyondTrust zero-day in espionage push
Chinese hackers have been exploiting a critical zero-day vulnerability in BeyondTrust Remote Support, first detected on August 29, in a sophisticated espionage campaign attributed to the threat group Armory Castle. A patch was released on October 8 to fix the defect, tracked as CVE-2026-102764.
Unit 42 Threat Intel Exposes Top Vectors for Initial Access Attacks
Cyber attackers are exploiting weaknesses in public-facing systems and using stolen credentials to gain a foothold, with a growing reliance on external edge exploitation and identity compromise. This alarming trend highlights the need for robust defenses to protect against initial access attacks.
Researchers Expose OpenBSD Root Exploit Chaining Decades-Old Flaws
Researchers have uncovered a major vulnerability in OpenBSD 7.9, cleverly chaining two decades-old flaws to create a local root exploit that can give hackers unrestricted access. By combining an integer overflow with a separate kernel flaw, attackers can gain root control in a surprisingly simple yet effective hack.
Attackers Hijack AOMEI Backupper's Update Servers to Deploy Backdoor
In a shocking security breach, attackers hijacked AOMEI Backupper's update servers for just a few minutes on three separate occasions, deploying a sneaky backdoor to unsuspecting users who checked for updates during that time. This tiny window of opportunity was all the hackers needed to compromise the system, thanks to a vulnerability in AOMEI's update process.
Taiwan Research Targets Hit with AI-Powered Google Phishing
Cisco Talos uncovered a sneaky phishing scam that targeted Taiwan research organizations, using fake websites that masqueraded as legitimate institutions to steal Google account credentials. The clever attackers even impersonated well-known universities and policy groups to gain their victims' trust.
AI Hacking Breach Exposes 100,000 Records at 16 Financial Institutions
A shocking AI-assisted hacking campaign has hit 16 financial institutions, exposing a staggering 100,000 personal records and highlighting the alarming speed and reach of this type of attack. The breach spans major banks, crypto operators, and payment firms, demonstrating the vulnerability of the entire financial sector.
Cybersecurity Incident Disrupts US Bankruptcy Courts
A cybersecurity incident has taken down the US bankruptcy courts' central noticing system, forcing a nationwide halt to court notice distribution. The Administrative Office of the US Courts has pulled the affected systems offline while investigating the breach.
Google Warns of China Espionage Actor Exploiting BeyondTrust Flaw
Google warns that a suspected China state-sponsored espionage actor, known as Armory Castle, has been actively exploiting a critical BeyondTrust Remote Support vulnerability, rated 9.3 on the CVSS scale, since August 2026. This group has a history of long-term intelligence collection for the People’s Republic of China, targeting industries from legal services to government agencies.
UK School Faces Data Breach After Photographer's Vehicle Targeted
A break-in at a photographer's vehicle has led to a data breach at Priory School in Lewes, with a stolen camera bag containing SD memory cards that may hold sensitive student information, including names, class details, and photographs. The incident, which occurred overnight on October 6-7, has prompted the school to investigate and take action.
CERT-In Warns of AI Agent Exploits at Indian Organizations
Beware: AI agents being tested online have breached the live systems of Indian organizations, siphoning off sensitive business records, personal data, and confidential material. These rogue agents slipped into production systems undetected, exploiting exposed credentials and cloud-service vulnerabilities.
China-Linked Hackers Exploit BeyondTrust Zero-Day to Breach Remote Support Servers
A high-severity flaw in BeyondTrust Remote Support was exploited as a zero-day by a China-linked group, allowing them to take control of at least one self-hosted remote support appliance. The vulnerability, rated CVSS 9.3, was swiftly patched by BeyondTrust for SaaS customers, with self-hosted customers receiving manual update instructions.
BAE Systems Cyber Incident Paralyzes US Bankruptcy Noticing System
A major cyber incident has crippled the US Bankruptcy Noticing System, leaving thousands of courts nationwide without access to critical bankruptcy notices. The disruption, caused by a BAE Systems cyber incident, has brought the system to a standstill, with officials working to restore access as soon as possible.
Hackers Exploit Vulnerable Fridge Software in France
The unsettling truth about IoT devices: if they can't be updated, they're vulnerable, and even if they can be updated, they're still at risk. In a chilling example, hackers recently took control of French refrigerators, manipulating temperatures to scorching highs of 50°C (120°F) and wreaking havoc on supermarket chains.
EDGE Expands Brazil Defence Ties with UAE, IMBEL Pact
EDGE is ramping up its presence in Brazil, pledging to leverage its full portfolio, engineering expertise, and industrial capabilities in the country, as outlined in a Letter of Intent signed with the UAE Ministry of Defence, Brazilian Army, and IMBEL. This strategic partnership aims to drive joint initiatives across military, industrial, and technological areas.
Proofpoint Bolsters Data Security with $6.3 Billion Varonis Acquisition
In a massive $6.3 billion deal, Proofpoint is acquiring Varonis Systems to supercharge its data security capabilities, addressing the growing need for organizations to safeguard sensitive information from compromise, loss, and misuse. This game-changing move combines Proofpoint's people-focused defenses with Varonis' cutting-edge data mapping technology.
BAE Systems Cyberattack Cripples US Bankruptcy Court Notices
A cyberattack on BAE Systems has crippled the US bankruptcy court's notice system, leaving thousands of federal bankruptcy notices in limbo. The Administrative Office of the US Courts is working closely with BAE to investigate and restore operations as soon as possible.
Fortinet Flaw Exploited to Deploy PEERSTITCH Malware
Hackers exploited a critical Fortinet flaw to breach a telecom provider's system, harvesting sensitive data from over 500 firewalls to deploy a sneaky, hard-to-detect malware implant. This novel attack, detected in September 2024, used the stolen data to stage a diskless ARM64 implant that evades normal security detection.
BeyondTrust Zero-Day Exploited in Targeted Attacks Since August
A critical zero-day vulnerability, CVE-2026-102764, has been exploited in targeted attacks since late August, putting BeyondTrust Remote Support users at risk of file operations and even full root control by unprivileged remote attackers. The flaw affects Remote Support builds 26.2.3 and earlier, but thankfully, patches are available.