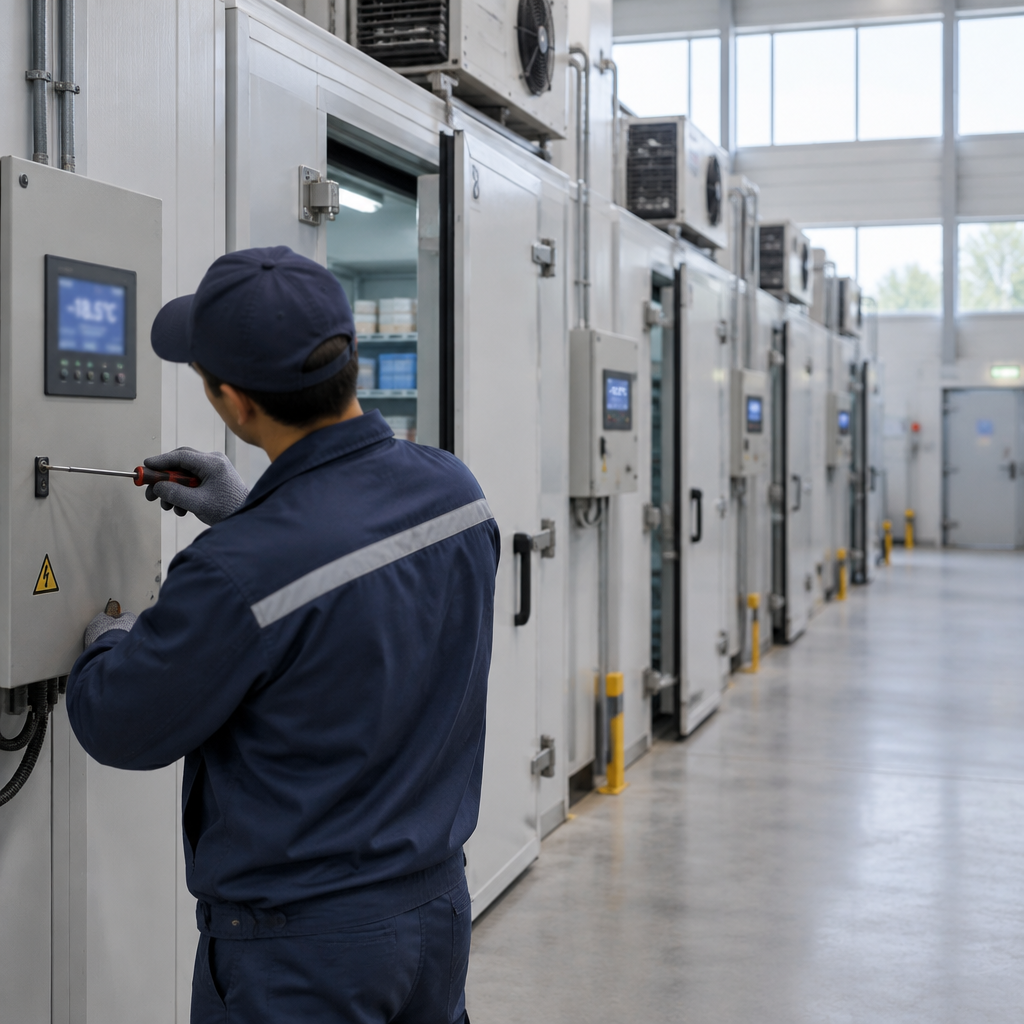
"Every organization that depends on refrigeration and monitoring systems should assume it could be a target," said Chris Butera, CISA’s acting executive assistant director for cybersecurity.
Joint advisory from CISA, the FBI, HHS, USDA, and DOT
On Thursday, five U.S. federal entities — the Cybersecurity and Infrastructure Security Agency (CISA), the FBI, and the departments of Health and Human Services, Agriculture, and Transportation — issued a joint warning that attackers are targeting electronic temperature controls at grocery stores and cold storage facilities. The bulletin did not name a perpetrator; it instead focused on tactics, impacts and specific mitigation steps for operators of refrigeration and monitoring systems.
Reported incidents: military commissaries, French blood banks, and European supermarkets
The advisory follows reporting by Nextgov/FCW that U.S. officials suspect Iran-linked hackers were behind freezer malfunctions at military bases that began in late August and affected roughly six commissaries, the on-base grocery stores that serve military personnel. Reuters had earlier reported that the Pentagon was treating those freezer incidents as possible cyberattacks.
In Europe, the breaches have also taken an operational toll. Hackers targeted refrigeration systems at three regional blood banks in France overnight Sunday into Monday. This week, another wave of supermarket attacks raised fridge temperatures at stores in Sweden, Belgium, Luxembourg and elsewhere, forcing retailers to discard food. Those incidents followed attacks at hundreds of French establishments in October.

This site is the portfolio.
OSINTSights runs on Cloudflare Workers, D1, R2, and Vectorize, with an AI pipeline on Hetzner ARM. Nubivance designed, built, and operates it. We do the same for clients.
See what we buildTechnique and immediate risks: temperature controls, visibility, and fire
The agencies described specific ways attackers can disrupt refrigeration: forcing refrigerators and freezers into continuous heating or defrost cycles and preventing operators from seeing current temperatures. Beyond ruined inventory and damaged equipment, the agencies warned of fire hazards and "potential harm to consumers who use products kept at unsafe temperatures."
According to the advisory, many of these outcomes are possible because digital vulnerabilities tied to refrigeration controls — including devices connected to the internet to remotely monitor or control temperatures — can expose the underlying equipment to hacking and sabotage.
What experts and authorities are saying
"We are seeing these systems targeted across critical infrastructure sectors globally, putting inventory and equipment at risk," said Brett Leatherman, the FBI’s cyber branch operations director. The U.S. government notice stopped short of attributing responsibility; it focused instead on urgent defensive measures for operators.
Nahman Khayet, co-founder and CEO at Alt Security, framed the operational calculus behind such attacks: "They've been playing this game for many years," he said. He added that the high cost and disruption of replacing large refrigeration units — particularly those holding critical supplies — makes operators slow to upgrade or patch equipment, a condition that attackers have exploited in other incidents.
Recommended mitigations for refrigeration operators
- The agencies urged operators to remove control systems from the public internet and secure any remote access they still need.
- They recommended separating refrigeration controls from business networks to limit lateral exposure.
- Other concrete steps include replacing default passwords, installing security updates, and retiring equipment that manufacturers no longer support.
How technologists, hospitals, and retailers are responding
- Technologists and security teams will be watching for exposed control interfaces and prioritizing segmentation and patching to block simple remote access vectors called out in the advisory.
- Hospitals and pharmaceutical suppliers — both singled out as users of refrigeration systems — will need to assess inventory risk and monitor temperature-visibility gaps that the advisory warns could hide unsafe conditions.
- Retailers and commissary managers face immediate operational choices about discarding spoiled stock, performing equipment checks, and accelerating replacement or firmware updates where manufacturers no longer support units.
European authorities have mirrored the U.S. response: the European Commission, ENISA, Europol and national authorities issued a joint warning Wednesday calling for immediate action and are coordinating response and information sharing about the incidents.
The record here is practical and material: attackers are exploiting gaps in refrigeration controls to create real-world losses and hazards, public authorities have issued coordinated warnings and technical steps, and responses range from emergency inventory decisions to network and equipment hygiene. What remains to be seen is whether operators will rapidly apply the technical mitigations the agencies urged — removing exposed controls from the public internet, segmenting networks, and retiring unsupported equipment — before more refrigeration-dependent businesses and services suffer further spoilage, equipment damage or safety incidents.