Tag: united states
385 articles
Snowflake Breaches Expose 100 Million People as Hacker Pleads Guilty
A massive data breach at Snowflake has left a staggering 100 million people vulnerable, after hackers exploited stolen credentials to access sensitive records at over 165 organizations. The mastermind behind the breach, Connor Riley Moucka, has pleaded guilty to multiple charges, including computer fraud and identity theft.
Kali365 Exploits Microsoft Authentication in US Firms
Meet Kali365, a sneaky device-code phishing kit that's exploiting Microsoft authentication to infiltrate US firms, with over 80 public sessions compromised weekly. By masquerading as trusted services, Kali365 tricks victims into handing over access to their Microsoft 365 email, documents, and cloud resources.
White House Charts Course to Secure AI with Flexible Framework
The White House is taking a bold step towards securing AI, with National Cyber Director Sean Cairncross emphasizing the importance of speed, adaptability, and partnership with private-sector defenders to protect the country's systems. By striking a balance between responsible use, security, and mutual benefit, the administration aims to foster a flexible framework that prioritizes collaboration over regulation.
Trump Orders Overhaul of White House Helipad Project
The White House has long needed a helipad of its own to safely land Marine One and preserve the South Lawn's pristine grass, but President Trump's vision for the project has just taken a dramatic turn. He's ordered contractors to start over from scratch, reportedly due to concerns over the helipad's appearance and slope.
Phishing Service Greatness Exploits RingCentral to Target Microsoft 365 Accounts
A recent security bulletin from RingCentral may have inadvertently given hackers a blueprint for a phishing campaign, as a notorious phishing service known as Greatness has begun targeting Microsoft 365 accounts with sophisticated attacks. Greatness, a phishing-as-a-service platform, has upgraded its tactics to include advanced threats like adversary-in-the-middle attacks and device-code phishing flows.
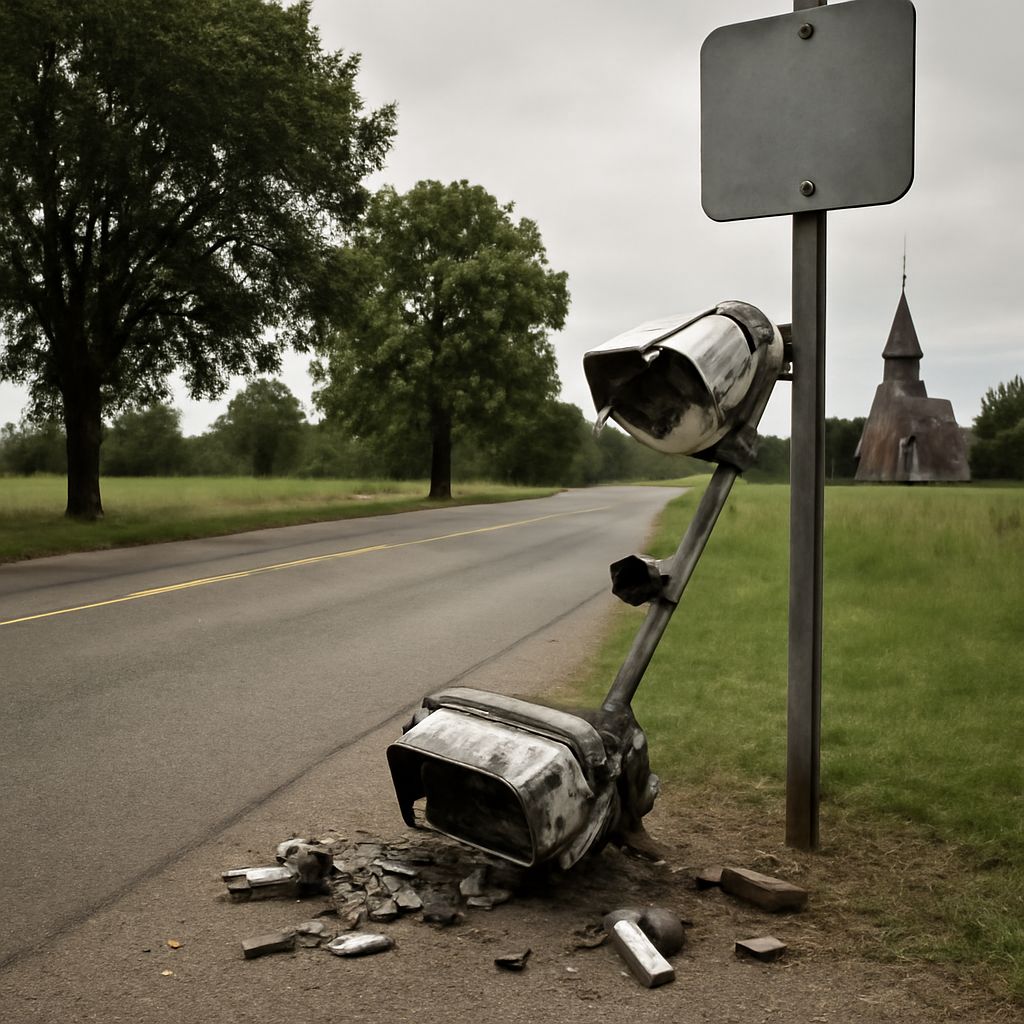
Congressional Candidate Targets License Plate Cameras
Meet Adam Lee Heimerman, an independent congressional candidate with a bold - and potentially costly - stance against license plate cameras, who now faces four felony vandalism charges for allegedly destroying four automated license plate reader cameras in Tennessee. His campaign to represent the state's 2nd Congressional District just got a lot more complicated.
Chinese Threat Actor Exploits Leaked DarkSword Kit to Deploy GHOSTBLADE on iOS Devices
A Chinese threat actor has cleverly exploited a leaked DarkSword kit to deploy GHOSTBLADE on iOS devices, with hosting concentrated in Hong Kong but reaching as far as Japan, the US, and Europe. This surprising attack follows the kit's public leak, which has been rapidly reused to target Apple devices running iOS versions 18.4 through 18.7.
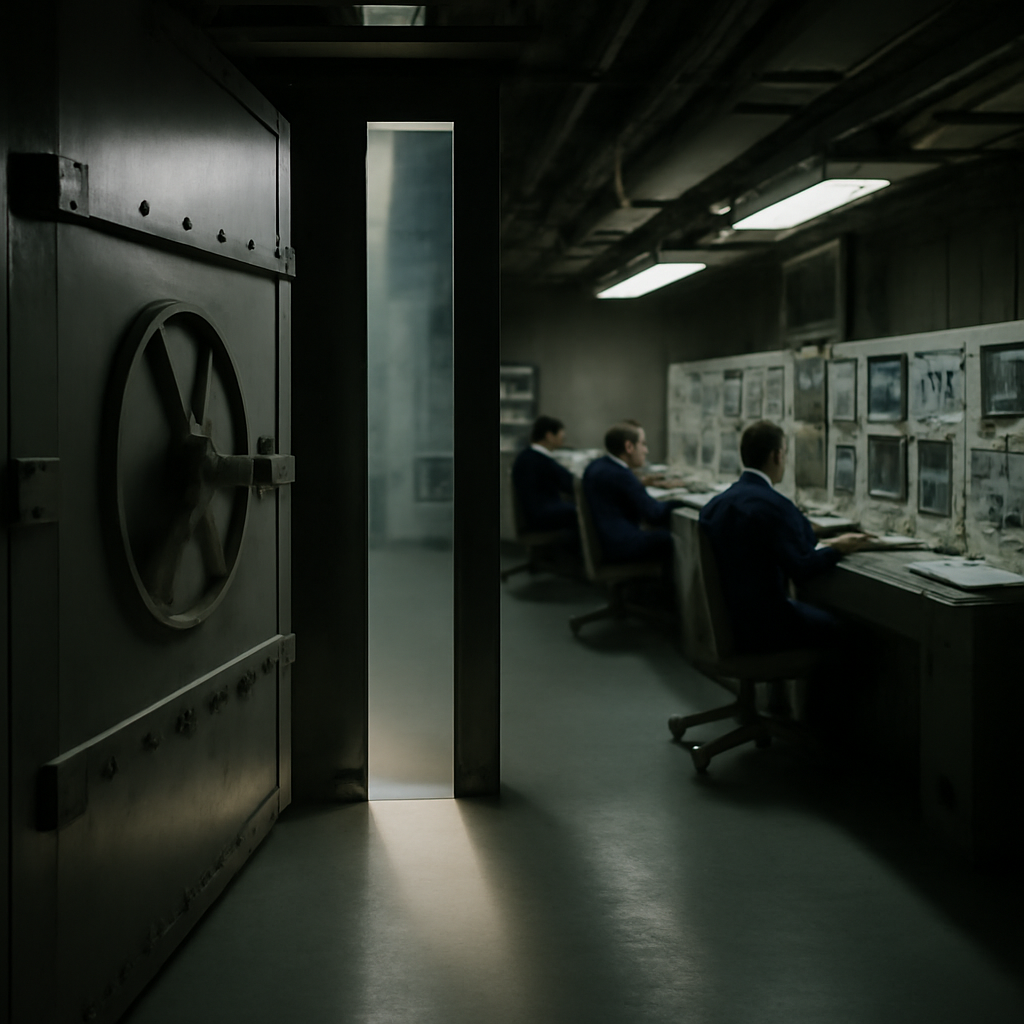
Forum Vigilance Bolsters Online Security Discussions
Meet 2nd Lt. Garret Burgess, a nuclear and missile operations officer who's on high alert 24/7, as captured in a gripping photo inside a launch control center at Malmstrom Air Force Base. He stands guard behind a blast door that safeguards access to the underground control center.
CMMC Pause Spurs Urgent Gap Assessments
The Department of Defense's sudden pause on CMMC Phase 2 has created an urgent need for gap assessments, especially for small and non-traditional businesses struggling to meet compliance requirements. This 60-day review aims to ease the burden, but existing obligations, including Phase 1 self-assessment requirements, remain in force.
Army Launches Reveille Forge for Air Defense Integration Testing
The Army has launched Reveille Forge, a cutting-edge facility that unites military, industry, and academic teams to revolutionize air defense integration testing. Located at Redstone Arsenal in Alabama, this game-changing environment enables seamless collaboration and integration of innovative solutions with existing defense systems.
Analog Devices Exposes Data Breach, Probes Incident
Analog Devices recently uncovered a data breach, swiftly springing into action to contain the incident and minimize damage after detecting unauthorized access to its systems on June 23. The company has launched a thorough investigation, working with cybersecurity experts and law enforcement to understand the breach and prevent future threats.
US Navy Decommissions Key Missile Submarine Amid Capability Gap
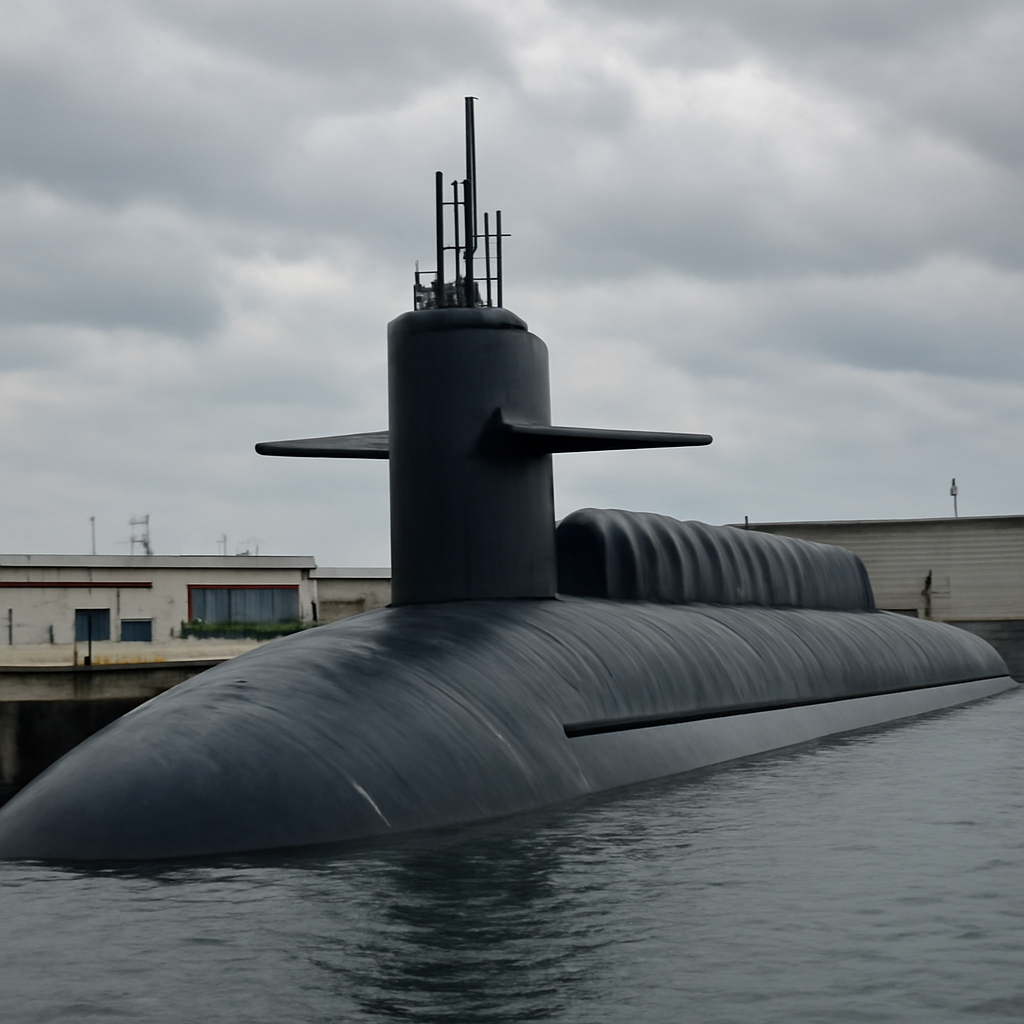
The US Navy is bidding farewell to one of its most powerful submarines, the USS Georgia, a nuclear-powered missile submarine that's served for over 42 years, as it begins its formal inactivation on July 31. This marks the start of the end of its service life, with the submarine ultimately headed for recycling.
Tech Giants Form Alliance to Bolster Open-Source AI Models
In a bid to revolutionize AI security, 37 tech giants, led by NVIDIA, have joined forces to form the Open Secure AI Alliance, championing the development of open-source AI models that boost cybersecurity and foster customization. By uniting behind open models, harness, and tools, the alliance aims to safeguard infrastructure and empower defenders to adapt and deploy robust protections.
Ransomware Breach Exposes Fairlife's Data, Disrupts Production
Fairlife has bounced back from a ransomware attack, with Coca-Cola confirming that the majority of production has resumed at its four US facilities. The breach, which involved unauthorized access and data theft, has had a minimal impact on the retail availability of Fairlife products.
CISA Faces Industry Pushback on Cyber Incident Reporting Rule
Industry leaders are pushing back on a proposed cyber incident reporting rule, arguing it casts too wide a net, with one critic saying it would ensnare far too many companies. The rule, aimed at bolstering national security, has sparked concerns about its broad scope and reporting requirements.
Tech Giants Push Open-Source AI to Bolster Cybersecurity Defenses
Microsoft and over two dozen tech giants are calling on policymakers to back open-source AI, believing it can strengthen America's cybersecurity defenses and foster a vibrant tech ecosystem. By embracing open-source AI, the US can avoid relying on just a few closed systems and instead build a robust and diverse technological landscape.
OnTrac Data Breach Exposes Customer Information After Network Hack
OnTrac recently suffered a network hack, resulting in a data breach that exposed customer information, with the incident detected on March 23 after an intrusion occurred between March 20-22. Fortunately, the company has no evidence of the stolen information being misused or published.
Australia's Drone Policy Exposes National Security Gap
Australia's foreign minister, Penny Wong, has made a bold commitment to the Philippines, vowing to provide surveillance drones built in Australia and the US, shunning cheaper Chinese alternatives in favour of trusted tech. This move comes as Australia's own drone policy reveals a concerning gap in national security.
CISA Overhauls Cybersecurity Collaboration with ANCHOR-CI Framework
The Cybersecurity and Infrastructure Security Agency (CISA) has unveiled a game-changing collaboration framework, ANCHOR-CI, to revolutionize how the federal government and private partners work together to protect critical infrastructure. This fresh approach replaces the two-decade-old CIPAC model, promising a more effective and resilient cybersecurity partnership.
Unions Challenge Pentagon's Abrupt End to Collective Bargaining
Two federal employee unions are taking a stand against the Pentagon's sudden move to scrap collective bargaining agreements, asking a judge to restore their rights and hold the Department of Defense accountable to a fair process. The American Federation of Government Employees and the National Federation of Federal Employees argue that Secretary Pete Hegseth's April decision was made without justification or transparency.
Selective Service System Pursues Draft Simulation Software
The Selective Service System is gearing up to evaluate its emergency response capabilities and is seeking simulation software to help assess its staffing and resource needs. Vendors have until August 14 to submit proposals for the project, with questions due by July 28.
House passes 2027 Defense Bill Amid Senate Stalemate
The House has passed the 2027 Defense Bill with a narrow 216-to-212 vote, despite some lawmakers on both sides expressing disagreement with certain provisions. This key step in a long process sets the stage for further negotiations, particularly with the Senate, where a stalemate currently exists.
Pentagon Seeks $37.5 Billion for Iran War Effort Through 2026
The Pentagon is requesting a hefty $37.5 billion to fund the US military's involvement in the Iran conflict through 2026, covering costs like military pay, operations, and maintenance. This price tag is a significant increase from earlier estimates, leaving many to wonder what exactly is included - and excluded - from the total.
Chick-fil-A Exposes Customer Data in Credential Stuffing Breach
Chick-fil-A is alerting customers to a credential stuffing breach that compromised some of its website and mobile app accounts between June 17 and June 19, 2026, using stolen account credentials from a third-party source. If you have a Chick-fil-A One account, you should check your email for a notification from the company and take immediate action to secure your account.