Tag: supply chain
1752 articles
ShinyHunters Exploits Oracle PeopleSoft Zero-Day to Breach 100 Orgs
ShinyHunters, a notorious data theft group, claims to have exploited a critical Oracle PeopleSoft zero-day vulnerability, CVE-2026-35273, to breach over 100 organizations, including the University of Nottingham. The group allegedly stole sensitive data, posting some of it on their leak site.
Malware Campaign Exploits AI Demand with Fake Guides and Dev Tools
Cyber attackers are now disguising malware as legitimate AI learning guides and developer tools, tricking professionals into opening malicious files that look like trusted educational content. They've been distributing booby-trapped archives labeled as AI study guides and developer tools, such as fake AI-ready PostgreSQL and agentic coding guides.
Cyberattacks Expose AI Agents' Vulnerability to Phishing Risks
A staggering 3.3 billion identity records are now circulating on illicit markets, thanks to a whopping 11.1 million devices infected with infostealers last year - a digital threat landscape that's more vulnerable than ever. This alarming trend highlights the urgent need for robust protection against AI agents' vulnerability to phishing risks.
Coupang Fines $409 Million for Massive Data Breach
Coupang has been slapped with a whopping $409 million fine for a massive data breach that exposed the personal info of 37.55 million people, due to a lax safety management system and negligence in key security measures. The hefty penalty is part of a landmark enforcement action by South Korea's Personal Information Protection Commission.
OceanLotus Targets Vietnam Investors with SPECTRALVIPER Backdoor
The notorious 15-year-old APT group, OceanLotus, is now setting its sights on Vietnam's investors with a cunning new backdoor attack called SPECTRALVIPER, showcasing their relentless adaptability and aggressive tactics. This latest move has left experts wondering if it's a temporary shift or a long-term strategy.
Australia's Financial Data Sits Unconnected to National Security
Russia's cunning tactics have allowed them to sustain oil exports despite sanctions, leveraging a shadow fleet of ageing tankers and layers of shell ownership to conceal their operations. This evasive strategy is just one example of a broader pattern where competitors obscure the source of their money and exploit economic interdependencies to gain leverage.
AI Coding Agents Exposed to 'Agentjacking' Attacks
Beware of "agentjacking" attacks that exploit AI coding agents' implicit trust, allowing hackers to trick them into executing malicious code on developers' machines. This new class of attack starts with a simple exploit of publicly available credentials, putting even the most secure systems at risk.
GitHub Disrupts Supply Chain Attacks by Blocking npm Install Scripts
GitHub is taking a bold step to safeguard the npm ecosystem by blocking install scripts from running by default, tackling the single largest code-execution surface in the ecosystem. This move, part of npm 12's release, aims to prevent supply chain attacks by requiring explicit permission for scripts to run.
Miasma Worm Source Code Leaked, Threatens Open-Source Ecosystem
The Miasma worm's source code leak is a game-changer, putting the entire open-source ecosystem at risk after already infiltrating 73 Microsoft repositories on GitHub. This credential-stealing attack framework operates autonomously, spreading rapidly by infecting developer machines and compromising legitimate repositories.
GitHub Bolsters npm Security to Thwart Supply-Chain Attacks
GitHub's upcoming npm v12 update is a game-changer for supply-chain security, as it will require explicit approval for automated actions like install scripts and dependency resolution that are often exploited by attackers. This move aims to shut down common code-execution paths and give developers, CI/CD pipelines, and security teams greater control over their code.
GitHub Overhauls npm Defaults to Thwart Script-Based Attacks
GitHub is taking a major step to boost npm security by changing its default settings to block automatic execution of install-time lifecycle scripts, a common vulnerability exploited in script-based attacks. Starting with npm 12, these scripts will require explicit permission to run, unless explicitly allowed via a new allowlist mechanism.
China Warns Australia on Critical Minerals Push
China is hitting back at Australia's critical minerals push, slamming Treasurer Jim Chalmers' decision to force China-linked investors to sell their stakes in rare earths developer Northern Minerals as "irrational de-sinicisation". This move has significant implications for Australia's defence, manufacturing, and renewable energy sectors.
Ivanti Patches Zero-Day Flaw Allowing Root Code Execution
Ivanti has patched a high-risk zero-day flaw that could let hackers run malicious code with root access, and fortunately, there are no known cases of exploitation so far. The vulnerability, tracked as CVE-2026-10520, affects the company's Sentry secure mobile gateway and allows for OS command injection permitting root execution.
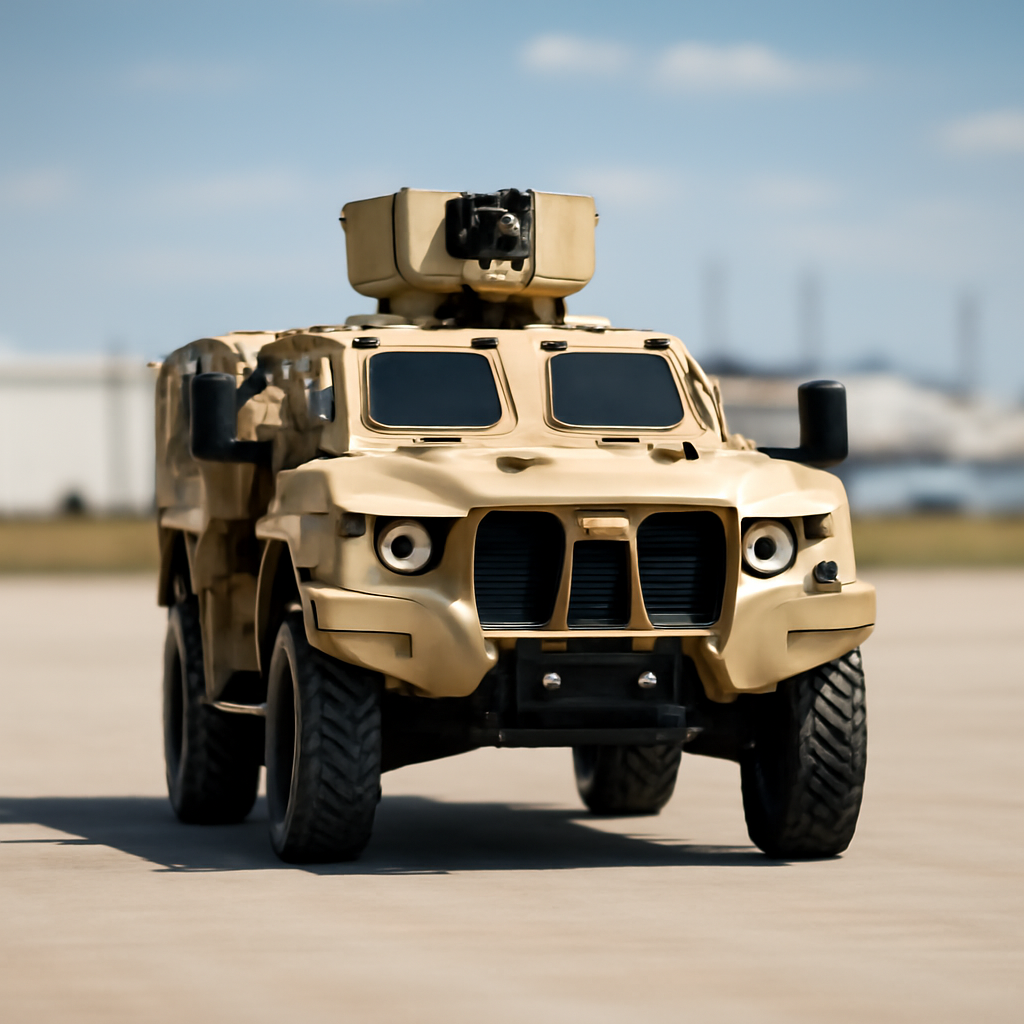
Oshkosh Seeks to Fill Marine JLTV Readiness Gaps with New Bid
Oshkosh Defense is stepping up to help the Marine Corps bridge critical readiness gaps with its combat-proven JLTV A1, a production-ready vehicle that can be delivered quickly. By leveraging its existing production capabilities, Oshkosh aims to provide a reliable solution to the Marines' urgent need for a trusted vehicle.
CISA Overhauls Risk Prioritization Approach for Federal Agencies, Private Sector
CISA is shaking up its approach to risk prioritization, urging a smarter strategy for applying patches and tackling vulnerabilities. Acting director Nick Andersen emphasizes the need to focus on what matters most, rather than rushing to apply every patch as soon as it's released.
Veeam Patches Backup Flaw That Enables Remote Code Execution
Veeam has urgently patched a critical backup flaw, CVE-2026-44963, that allowed remote code execution with just domain user credentials, scoring a severe 9.4 out of 10 in severity. The update to version 12.3.2.4854 fixes this vulnerability, preventing attackers from running malicious code on the Backup Server.
Miasma Worm Spreads as Open-Source Toolkit Compromises GitHub Repos
A newly discovered open-source toolkit, known as Miasma Worm, is wreaking havoc on GitHub repositories, allowing attackers to execute a range of malicious activities via stolen credentials. This powerful supply chain attack toolkit can compromise multiple platforms, including PyPI, npm, and RubyGems, and even spread through AI coding tools and SSH-based lateral movement.
GitHub Disrupts Microsoft Repos Hosting Password-Stealing Malware
In a lightning-fast response, GitHub and Microsoft swiftly contained a malware incident on June 5, removing 73 repositories and restoring disrupted developer workflows in a mere 105 seconds. The quick takedown prevented password-stealing malware from causing further harm, showcasing the companies' commitment to protecting their platforms.
Veeam Vulnerability Enables RCE Attacks on Backup Servers
A newly discovered vulnerability in Veeam Backup & Replication could allow an authenticated domain user to launch a remote code execution attack on your backup server - a critical target for hackers. Patch now to protect your data: update to version 12.3.2.4854 or later to fix the flaw.
Russia-Aligned Groups Exploit WinRAR Flaw to Deploy Stealers in Ukraine
Despite a July 2025 patch, a vulnerability in WinRAR, known as CVE-2025-8088, continues to be exploited by Russia-aligned groups, including SHADOW-EARTH-066, to deploy stealers in Ukraine. This highlights the risks of unmanaged software leaving exploited entry points open long after a fix is released.
PyPI Packages Poisoned in Hades Supply Chain Attack
Malicious actors have launched a supply-chain attack on the Python Package Index (PyPI), infecting 19 packages with 37 tainted versions that can download and execute a hidden JavaScript payload. This sneaky Hades campaign uses poisoned Python packages to spread its reach, putting developers and users at risk.
Australia Shifts to Just-in-Case Logistics Amid Contested Indo-Pacific
Australia is transforming its logistics strategy from efficient but fragile just-in-time systems to a more resilient just-in-case approach, prioritizing redundancy and preparedness to withstand disruption and conflict in the increasingly contested Indo-Pacific region. This shift means embracing higher costs and complexity to ensure endurance in the face of coercion and uncertainty.
Qilin Ransomware Breach Tally Grows with Essex Trust Confirmation
Two years after a devastating ransomware attack, the NHS breach count continues to grow, with an Essex trust now confirming that sensitive patient records were stolen by the notorious Qilin gang. The incident serves as a stark reminder that the impact of this cyberattack is still being felt, with hospitals working tirelessly to identify and warn affected patients.
CISA Mandates Patching of Exploited Check Point VPN Bug
A critical vulnerability in Check Point VPNs, known as CVE-2026-50751, has been exploited in dozens of organizations worldwide, with one incident linked to Qilin ransomware. This bug allows hackers to bypass authentication and establish remote access, putting targeted organizations at risk.