Tag: supply chain
1740 articles
Jewelbug APT Exploits Dual Agenda with Espionage and Crypto Fraud
Meet Jewelbug, a notorious APT group that's been pulling off a double heist - stealing sensitive info and swindling victims out of crypto - all from the same interconnected operation. Their massive haul includes over 1 million implant check-ins and 580,000 stolen cookies, with targets spanning government systems and service providers across the Middle East, Southeast Asia, and South Asia.
Akira Ransomware Actors Exploit Safe Mode to Evade EDR Protections
Cyber attackers have found a sneaky way to bypass EDR protections by exploiting Safe Mode, leaving security systems blind to their malicious activities. In one recent incident, an exposed SonicWall VPN with no multi-factor authentication was all it took for hackers to gain entry and start wreaking havoc.
US Military Grapples with China Rare Earth Dominance
The US military is facing a daunting reality: a single fighter jet, like the F-35, requires over 400 kilograms of rare earths to build, highlighting the alarming dependence on these critical minerals. China, which controls a whopping 70% of rare earth mining and 90% of processing, holds the reins on the global supply chain.
Jewelbug Hacker Group Exposes Dual Threat of Espionage and Crypto Fraud
Meet Jewelbug, a China-based hacker group that's been wreaking havoc with a dual threat of espionage and crypto fraud, leaving a trail of over a million compromised implant check-ins and thousands of stolen credentials in its wake. By cleverly injecting a single malicious script into a shared webmail template, Jewelbug gained write access to sensitive government webmail accounts, making off with valuable data.
Uber Freight Probes Data Breach Claims by Helix Hacking Group
Uber Freight is investigating claims that a hacking group called Helix has stolen nearly 1 million files from the company, posting them online as evidence. The breach has sparked an urgent probe into unauthorized access to Uber Freight's systems and data repositories.
VMware vCenter flaw exploited for reverse SSH access globally
A critical VMware vCenter flaw, CVE-2026-59310, is being exploited globally, with 361 Internet-connected systems across 47 countries already compromised. This severe vulnerability allows unauthenticated attackers to execute arbitrary code, making swift action essential to prevent further breaches.
Compromised AWS Key Exposes 1500+ UK Charities to Data Breach
Over 1,500 UK charities are reeling after a data breach at CRM provider Beacon exposed their personal information, likely due to a compromised AWS access key. This devastating cyber-attack has left countless organizations vulnerable, sparking urgent concerns about data security.
Trezor Breach Exposes 14,000 Customer Records
Trezor revealed that its shipping partner, ShipMonk, suffered a security breach, exposing a whopping 14,000 customer records, and fortunately confirmed that its own systems and devices remain secure. The breach, which occurred between May 10 and August 8, 2026, was discovered on August 10, 2026.
Google Cloud Accelerates Post-Quantum Security Push with 2027 Milestone
Google Cloud is proactively bolstering its defenses against future quantum computer threats, aiming to complete a major milestone in its post-quantum security migration by 2027. The tech giant has mapped out a multi-year plan to adopt quantum-resistant cryptography, tackling key risks in data security and digital signatures.
AI Coding Tools Expose Open Source to Supply Chain Attacks
New research reveals a shocking vulnerability in AI coding tools: many suggested package names don't exist or point to outdated or compromised packages, leaving open-source projects open to supply chain attacks. This alarming gap in code-generation models highlights a pressing need for better safeguards.
VMware vCenter Flaw Exploited Days After Disclosure
Within days of Broadcom's advisory, a critical VMware vCenter flaw, CVE-2026-59310, was exploited, putting 361 victim IP addresses across 47 countries at risk. This severe vulnerability allowed attackers to turn a logging service into a gateway to infiltrate operating systems worldwide.
UK Watchdog Reprimands ACRO for 2023 Data Breach Failings
A major security blunder at the Criminal Records Office (ACRO) left 10,920 people vulnerable to a data breach after a hacker gained unauthorized access to its website and content management system for a staggering eight months. The Information Commissioner's Office (ICO) has now reprimanded ACRO for its failings in preventing this massive breach.
US Army Tackles Readiness Crisis with New Industry Engagements
The US Army is facing a pressing readiness crisis, with an aging fleet and looming modernization challenges that won't arrive quickly enough to ease the strain, warns Brig. Gen. Beth Behn. As a result, the Army is bracing for a long-term supply-chain and sustainment headache.
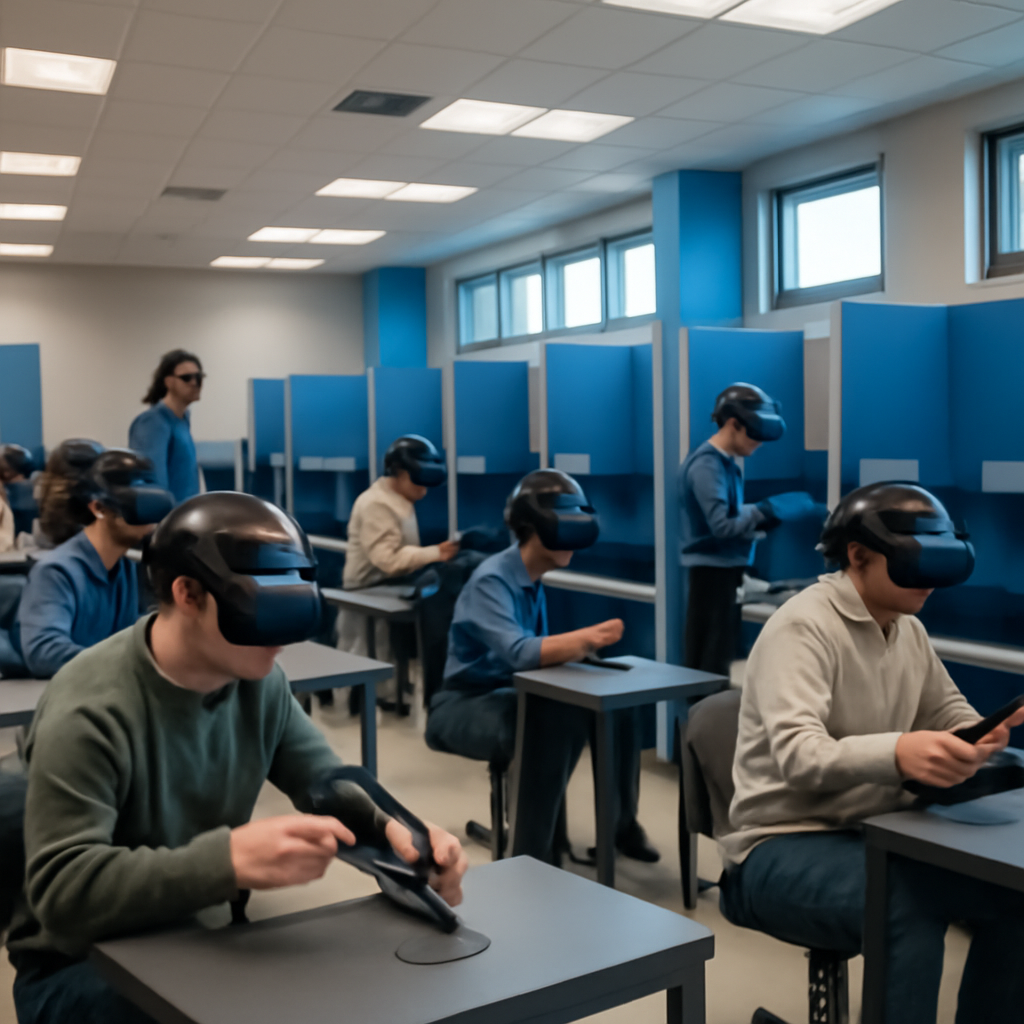
HII Ingalls Shipbuilding Deploys Virtual Reality to Accelerate Welding Training
Ingalls Shipbuilding is revolutionizing welding training with a cutting-edge virtual reality lab, where novices can practice with a 48-station setup that simulates real-world experience without the intimidation. This innovative approach has already helped around 1,000 students, including apprentices and new employees, build confidence and skills before moving to traditional instruction.
Foreign Arms Makers Abandon Pakistan Deals Amid Concerns Over Unlicensed Maintenance, Security Controls
Pakistan's defence market is becoming increasingly reliant on China, with a whopping 80% of its major arms imports coming from the country between 2021 and 2025. This dominant share has jumped from 73% in the previous five-year period, solidifying China's position as Pakistan's top arms supplier.
Ransomware Attacks Pivot to Identity-Based Exploits
Ransomware attacks are taking a new and more personal approach, with a whopping 80% now targeting identities rather than software flaws. Malicious emails, phishing, and compromised credentials are the top entry points, making identity-based exploits the new favorite tactic of ransomware operators.
Attackers Exploit SharePoint Flaw After Public PoC Release
Microsoft warned that a critical SharePoint flaw, patched in July 2026, could allow attackers to bypass authentication and disclose files or modify data. This vulnerability, tracked as CVE-2026-55040, has now been exploited by attackers following the public release of a proof-of-concept exploit.
City-Forum Attacks Exploit Salesforce, ServiceNow Portals for Data Theft
A single IP address, 158.220.87.79, has been linked to a massive data-theft campaign targeting corporate and public portals, including Salesforce and ServiceNow, for over a year with no signs of slowing down. This persistent threat has compromised multiple organizations worldwide, spanning industries from telecom and finance to security and government.
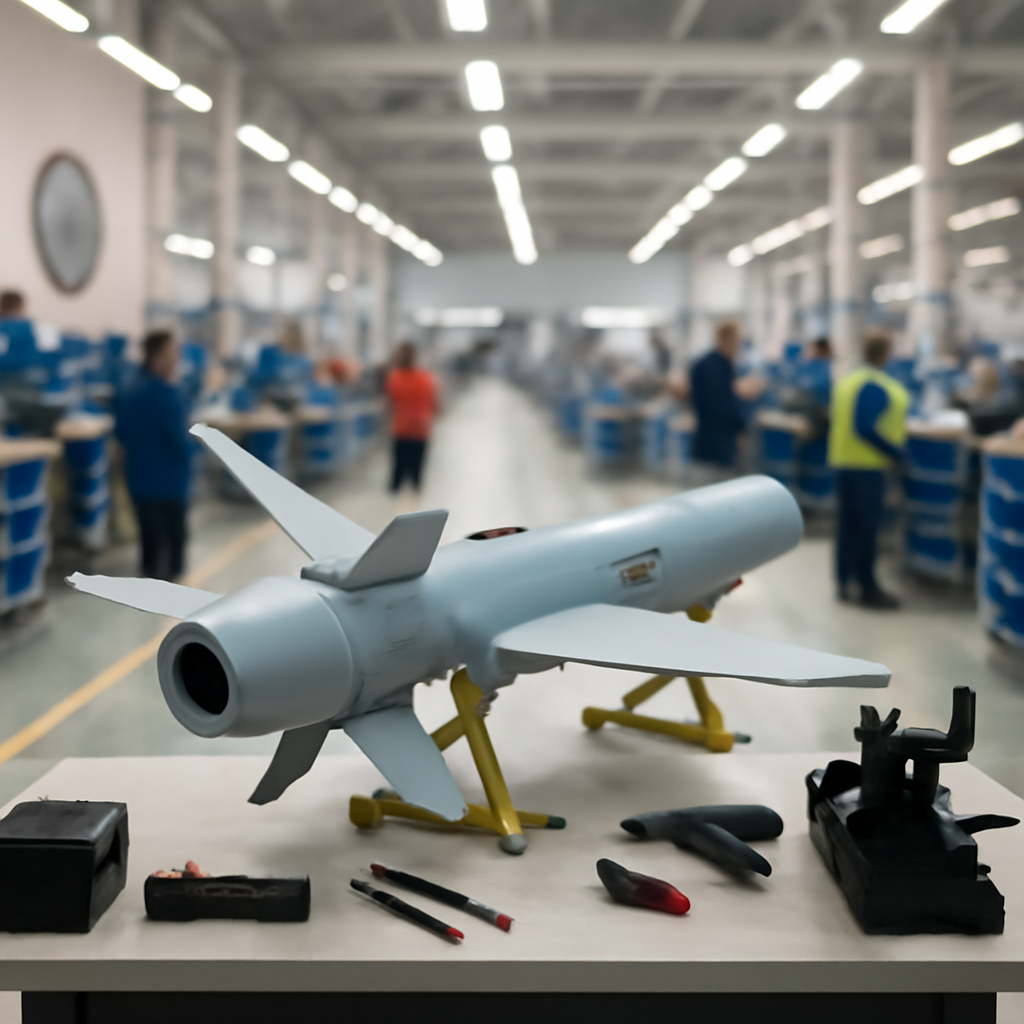
Defense Industry Targets Affordable Munitions Mass Production
We're at a critical juncture where combat power hinges on rapidly delivering advanced capabilities at scale - and L3Harris is rising to the challenge with affordable munitions production. With a proven track record of delivering over 1,200 unmanned aerial vehicles and completing more than 50 successful flight tests, the company is poised to revolutionize mass production.
Lazarus Exploits Windows Zero-Day to Deploy Trojan Backdoor
Meet the sneaky Trojan backdoor, Troy, that's been secretly infiltrating defense and aerospace companies worldwide by exploiting a newly discovered Windows zero-day vulnerability. This stealthy attack, part of Operation Dream Job, tricks victims with fake job offers on LinkedIn before deploying the malware.
Uber Freight Probes Data Breach by Helix Extortion Group
Uber Freight is investigating a data security incident after a hacktivist group claimed to have breached its systems, but fortunately, the issue has been identified, contained, and resolved, with operations now secure and running smoothly. The breach hasn't disrupted daily operations, and the company is working to put customers' minds at ease.
Fake Remote Workers Exploit Hiring Process Gaps
Scammers are exploiting gaps in the hiring process to land remote jobs, using stolen credentials and impersonating others to get their hands on sensitive corporate information. They're taking advantage of the rise of remote work to gain access to company networks and exfiltrate proprietary data.
Gunra Ransomware Targets Infrastructure via Fortinet Flaws
Gunra Ransomware is exploiting critical Fortinet flaws, including CVE-2024-55591, to gain super-admin privileges and infiltrate government and critical infrastructure networks. This alarming vulnerability allows remote attackers to craft requests and bypass authentication, putting sensitive systems at risk.
Akira Ransomware Gang Foiled by Safe Mode Reboot
In a surprising twist, an Akira ransomware affiliate inadvertently sabotaged its own attack by rebooting a victim's system into Safe Mode, thwarting the mass-encryption step but not before exfiltrating sensitive credentials and files. This unexpected turn of events highlights the unpredictable nature of cyber attacks.