Tag: supply chain
1739 articles
Hackers exploit Collabora flaw to backdoor Nextcloud servers
Hackers are actively exploiting a critical flaw in Collabora Online's CODE Server app for Nextcloud, allowing them to backdoor servers and putting sensitive data at risk. This vulnerability, tracked as CVE-2026-110447, affects specific Nextcloud app versions and has been under attack since mid-September.
Hackers Disrupt French Supermarkets by Exploiting Refrigeration Controller Flaws
In a shocking sabotage, hackers jacked up temperatures in refrigeration controllers to as high as 122°F (50°C), causing widespread food spoilage and fires across nearly 700 French supermarkets. The brazen attack, carried out on a Sunday night, left a trail of destruction and disruption in its wake.
Alliances Scramble for Critical Minerals
Imagine a world where one country controls the lion's share of critical minerals - think 98% of processed gallium and germanium, 95% of refined magnesium, and over 90% of rare earths and battery-grade graphite. China's dominance in the global processing capacity for these essential resources raises significant strategic implications.
Unit 42 Exposes PEERSTITCH, Novel FortiGate Implant
In a shocking discovery, Unit 42 uncovered PEERSTITCH, a novel FortiGate implant used by attackers to exfiltrate sensitive data from over 500 firewalls, all originating from a single compromised appliance. The breach began with a clever exploitation of a previously unknown vulnerability, CVE-2024-47575, in FortiManager's FMG-Access channel.
US Army Braces for Supply Chain Impacts as Critical Mineral Deadline Looms
The US Army is gearing up for potential supply chain disruptions as a critical mineral deadline approaches, with some impacts expected as early as January. The Army is bracing for a gradual effect, rather than a catastrophic one, as defense companies work to map their supply chains and comply with new rules.
Ransomware Groups Exploit VPN Vulnerability
Ransomware groups like Qilin and Settra are sneaking into organizations by exploiting a VPN vulnerability, disguising their malicious activity as legitimate remote work. This allows them to steal credentials, move laterally, and deploy ransomware undetected until it's too late.
Malicious Packages Infiltrate Arch Linux Repository with Rootkit Malware
Malicious actors have struck the Arch Linux community by uploading trojanised packages to the Arch User Repository, cleverly disguising them as legitimate AUR helpers like yay and paru. The fake packages, including a malicious yyay package, used identical source code and URLs to blend in with the real deal.
Citizen Lab Exposes Candiru Spyware Infections Through Targeted Online Ads
Meet the sneaky spyware that can infect your device with just a single online ad - no clicks required. Citizen Lab researchers uncovered a cunning ad-delivery chain used by Discover-Tech to spread zero-click spyware, infecting targets with alarming precision.
NGINX Disrupts Multiple Flaws, Including Possible RCE and TLS Session Forgery
NGINX just dropped a critical update to squash five vulnerabilities, including a long-standing flaw dating back to May 2005 that could lead to code execution or crashes in certain configurations. The patches fix memory bugs, a TLS session-ticket weakness, and an HTTP/3 parser issue that could put your system at risk.
Adtech Firm Exposes Online Ads as Spyware Vector
Meet Discover-Tech, an Israeli adtech firm with a shady secret: its Controlium platform has been caught exploiting online ads to spy on users across over 70,000 mobile apps and 120,000 websites.
Danfoss Controllers Disappear After Cyber-Attack
A massive 71% of internet-exposed Danfoss StoreView control panels in France vanished within just three days following a cyber-attack that crippled hundreds of supermarkets, suggesting a frantic effort to pull systems offline rather than fix them. This sudden disappearance was tracked by Censys researchers, who monitored the dramatic decline from 1,825 exposed hosts on October 11 to just 537 by October 14.
Fake AI Attacks Target US Companies via Impersonated Brands
US companies are under attack by fake AI campaigns that impersonate trusted brands like Claude, ChatGPT, and Copilot, spreading malware and stealing sensitive data. Attackers are using clever tactics, such as sponsored search results and fake download websites, to trick victims into compromising their business accounts.
Air Force Exposed to Malware Risk via Unsecured USB Drives
The Air Force's use of CDs and later USB drives to transfer mission data between unclassified and classified systems created a vulnerability that allowed malware to slip into sensitive areas, reveals Justin Henkel, former Air Force IT security expert. This simple habit, born from convenience, ended up bridging the gap between secure and unsecure environments.
Microsoft Disrupts Global Phishing Network Behind 1 Billion Messages
Microsoft and Japanese police have joined forces to take down a notorious phishing network, known as Yam Store or Storm-3119, that was responsible for a staggering 1 billion phishing emails and texts sent to over 75,000 organizations since January 2026. This underground marketplace was selling compromised accounts, licenses, and storage to threat actors, fueling a massive wave of cyber scams.
Langflow Exploit Attempts Surge Amid Authenticated RCE Flaw
Authenticated hackers are on the hunt, with 1,423 attempts recorded to exploit a critical remote-code-execution flaw in Langflow, a vulnerability that scores a near-perfect 9.9 on the CVSS scale. This alarming spike highlights how quickly attackers pounce on high-risk weaknesses.
GhostAction Exploits 1,900 GitHub Accounts, Hits 30,000 Repositories
Malicious actors launched a massive attack, dubbed GhostAction, that compromised nearly 1,900 GitHub accounts and infected over 30,000 repositories with a malicious workflow. The concentrated surge, which occurred on October 8-9, 2026, put thousands of users and organizations at risk.
UK Watchdog Cites Police for Data Leak Lapses
The UK's Information Commissioner's Office has reprimanded the Metropolitan Police Service for failing to properly protect data when using a retail crime intelligence platform, highlighting the importance of balancing innovation with robust data safeguards. Organizations must prioritize risk assessments and effective oversight to avoid similar data protection lapses.
Cisco Email Flaw Exploited in Zero-Day Attacks
Cisco is urging customers to upgrade to a fixed software release after a critical vulnerability in its Secure Email Gateway was exploited in active zero-day attacks, allowing hackers to gain root access with just a malicious email. The flaw, scored 9.8 out of 10 on the CVSS scale, enables remote attackers to write files and execute commands with root privileges on the appliance operating system.
Microsoft Disrupts Vast Chinese-Language Phishing Kit Network
Microsoft swooped in to dismantle a massive Chinese-language phishing kit network that had been bombarding over 75,000 organizations worldwide with a staggering 1 billion+ emails and SMS messages since January. The campaigns, tracked as Storm-2990, were fueled by a commercial ecosystem of customizable phishing kits.
Army Revamps Munitions Procurement Amid Iran War
The Army is ramping up production of Patriot air-defense missiles, with a goal of producing 2,000 interceptors annually, but discussions are underway to potentially surge production even further to meet evolving demands amid the ongoing war with Iran. Gen. Frank Lozano says the service is exploring ambitious targets, including 4,000, 6,000, or even 8,000 missiles per year.
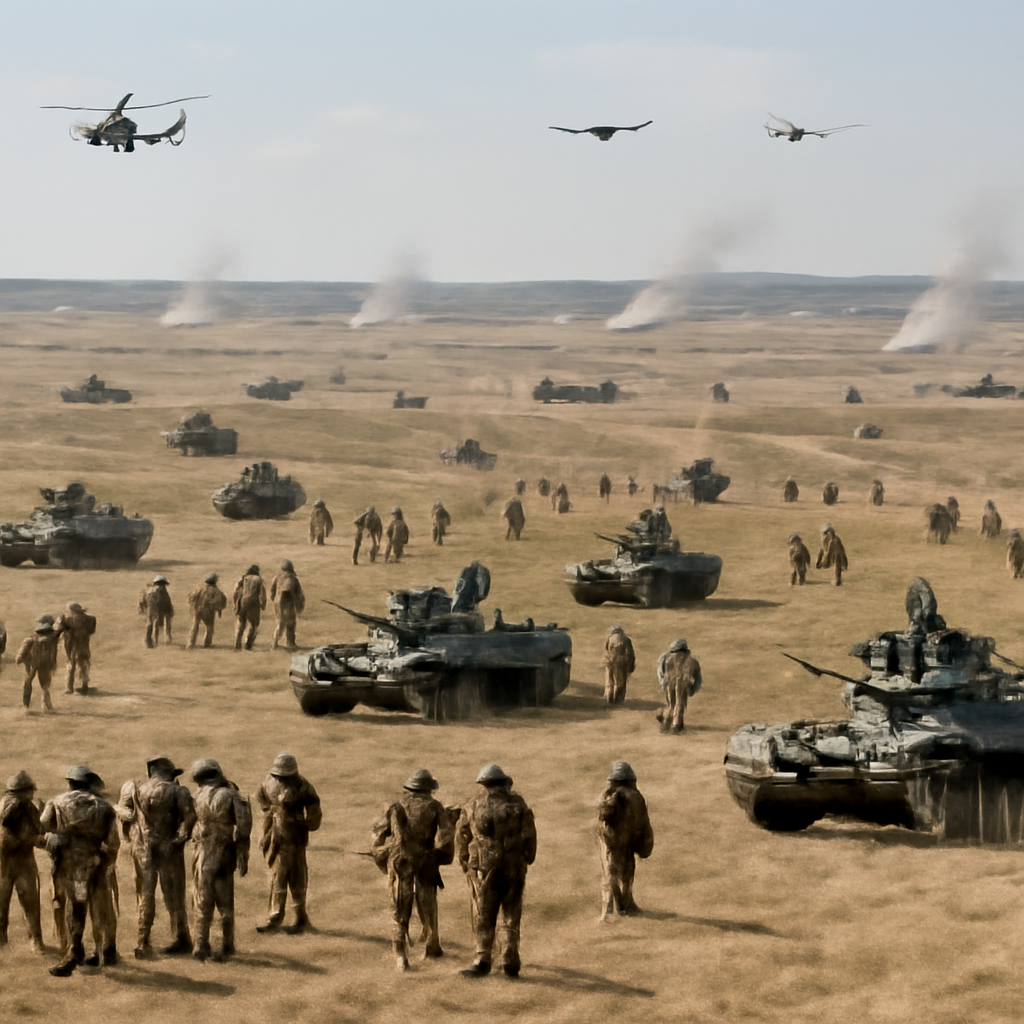
China Learns from Russia's Ukraine War Experience
China sent a team to Russia's massive Tsentr military exercise, where troops from over 30 countries practiced tactics learned from the Ukraine conflict on a mock battlefield. The drills, involving 47,000 personnel and 600 aerial drones, gave China valuable insight into Russia's wartime strategies.
Researchers Craft Billion-User Chrome Exploit in Six Days
In just six days, a team of four researchers harnessed the power of a publicly available AI model to craft a Chrome exploit that earned them a whopping $250,000 bounty from Google. With the help of OpenAI's GPT-5.6 Sol model, they chained together three zero-day Chrome vulnerabilities, proving that innovation and speed can pay off big time.
Hackers Exploit Flaw in Collabora's CODE App to Backdoor Nextcloud Servers
Hackers have exploited a critical flaw in Collabora's CODE app to compromise Nextcloud servers, planting web shells to gain unauthorized access. This vulnerability, tracked as CVE-2026-110447, highlights the importance of keeping your Nextcloud server security up to date.
Cisco Discloses Active Attacks on Secure Email Gateway Flaw
Cisco is warning users of its Secure Email Gateway of an actively exploited flaw that could allow hackers to run commands as root, giving them total control of the system. This critical vulnerability, scored 9.8, is being targeted by attackers who are sending crafted email attachments to take advantage of the weakness.