Tag: nation state
1338 articles
Qihoo 360 Unveils AI Bug-Finder to Rival Anthropic's Mythos
Qihoo 360 CEO Zhou Hongyi has unveiled an AI bug-finder, positioning it as a powerful countermeasure to restricted Western tools, likening Anthropic's Mythos to a "cyber nuclear weapon". This new Chinese innovation aims to level the playing field in cybersecurity.
Loitering Munitions Converge on Long-Range Strike Designs
Loitering munitions have revolutionized long-range strikes, as seen in Ukraine's recent launch of hundreds of LMs at multiple regions, including a daring attack on Russia's Gazprom Neft Moscow Oil Refinery, just 14 km from the Kremlin. This new class of munitions has eliminated the need for high-cost platforms, allowing for more flexible and affordable precision strikes.
Cellebrite Tool Exploited by Russia to Infiltrate Activist's Phone
Russian authorities exploited a loophole in Cellebrite's UFED tool, using it to extract data from activist Andrey Pivovarov's phone, even after the device was no longer receiving updates. This security gap allowed the authorities to access the phone's data as far back as June 2021.
macOS Malware Embeds Fake Errors to Evade AI Analysis
Meet macOS.Gaslight, a sneaky new malware family from a North Korean-linked threat actor that's got a clever trick up its sleeve - embedding 38 fake system messages to throw off AI analysis tools. This tiny 3.5 KB payload is packed with deception, making it a formidable foe for cybersecurity experts.
Iranian Hackers Exploit Credentials in Cal Water Breach
Cal Water swiftly sprang into action when an Iranian-linked group, Handala, claimed to have hacked their system, activating their cybersecurity response plan and launching a thorough investigation. Thankfully, experts from Mandiant found that the breach was limited to third-party accounts, containing no evidence of a larger-scale attack.
Gaslight Malware Exposes AI-Assisted Analysis Limits
Meet Gaslight, a sneaky new macOS malware that uses fake system-failure messages to trick AI-powered analysis tools into doubting themselves. Created by North Korea-aligned threat actors, this Rust-based implant is a clever and concerning threat to cybersecurity.
Australia's Security Threats Converge as AI Compresses Risk Timeline
When Australia's critical infrastructure is disrupted, it will be a shock, but not a surprise - and with AI supercharging threats, that disruption may come sooner than we think. The warning signs are clear: AI is rapidly expanding the offensive toolkit, making threats more immediate, concurrent, and devastating.
Hackers Exploit Cisco Zero-Day for High-Level Access at Telecom Provider
In a chilling cyberattack, hackers exploited a previously unknown Cisco zero-day vulnerability to gain unrestricted access to a major telecom provider's system, creating a rogue admin account with full control. The breach, detected in March, was carried out in two waves, allowing the attackers to infiltrate the provider's SD-WAN Manager devices.
ASIO Disrupts Nation-State Cyber Sabotage Targeting Australian Infrastructure
ASIO director general Mike Burgess revealed that nation-state hackers had infiltrated a critical Australian infrastructure provider's network, gaining login credentials to sabotage it at will. The alarming breach was thwarted thanks to ASIO's swift action and dedicated response.
Threats Expose Gaps in US Air-and-Missile-Defense Industrial Base
The US air-and-missile-defense system is struggling to keep up with today's threats, revealing gaps in real time, because its industrial base was designed for a bygone era. It's clear that we need a new approach, with more innovators and fresh ways to design, build, and deploy critical technologies like munitions and hypersonics.
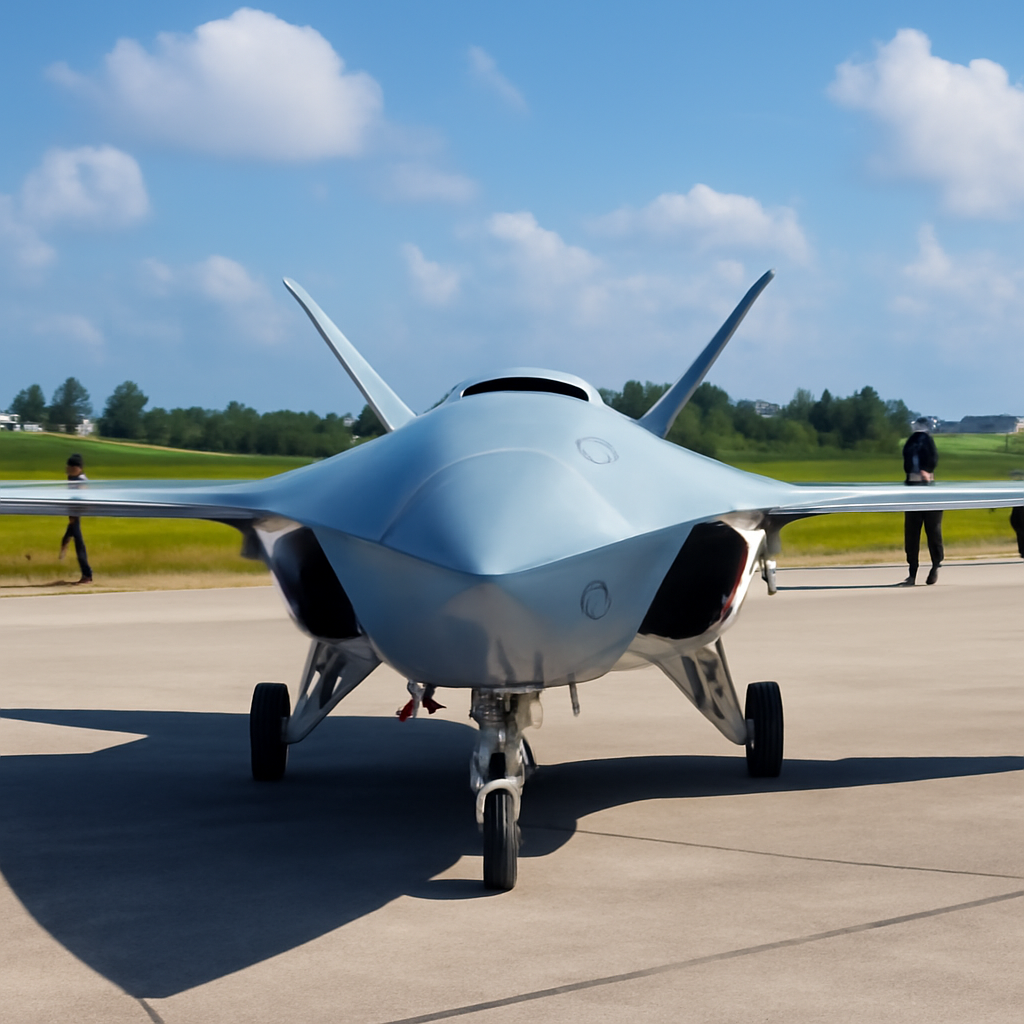
MQ-28 Ghost Bat Drone Deploys in Major Pacific Combat Exercise
The MQ-28 Ghost Bat drone made its debut in a major Pacific combat exercise, demonstrating its cutting-edge capabilities as a force multiplier that can fly alongside crewed fighters and extend their reach. This milestone marks a significant step forward in human-machine teaming and showcases the US commitment to a free and open Indo-Pacific.
Governments Struggle to Secure Open-Source Software
The alarming reality is that years of underinvestment in open-source software security are catching up with us, with a new supply chain compromise emerging almost every week. A recent scan by Project Glasswing found over 6,000 high-risk vulnerabilities in popular open-source projects, but only a tiny fraction have been patched.
SharkLoader Targets Global Entities with Cobalt Strike Deployment
Kaspersky researchers have uncovered a sophisticated campaign, dubbed StrikeShark, where hackers exploited vulnerabilities like ProxyLogon to deploy SharkLoader malware and gain access to high-stakes targets worldwide. The attackers used multiple publicly disclosed flaws to compromise internet-facing services, hitting diplomatic entities, software vendors, and more.
North Korea-linked Backdoor Exploits AI Triage Tools
When building AI triage tools, it's crucial to treat sample contents as potentially hostile input, not instructions, to prevent malicious manipulation. Experts warn that failing to do so can allow attackers to sneak hostile content into your model.
Social Engineering Attacks Target Service Desks
Service desks have become a prime target for cyber attackers, who often find it easier to manipulate staff into divulging sensitive information than to crack the technology itself. In a string of recent incidents, hackers have successfully impersonated employees to gain access to internal systems, as seen in the 2025 UK attacks on major retailers like Marks & Spencer, Co-op, and Harrods.
MuddyWater Exploits Ransomware Disguise for Cyber Espionage
The line between ransomware attacks and nation-state espionage is rapidly blurring, as cyber groups like MuddyWater now disguise their operations as financially motivated ransomware attacks to further their strategic objectives. MuddyWater, linked to Iran's Ministry of Intelligence and Security, has been caught posing as the Chaos ransomware group in a deliberate campaign.
Mistic Backdoor Enables Long-Term Access in Ransomware Attacks
Cyber attackers have deployed a sneaky backdoor called Mistic, allowing them to maintain long-term access to infected systems during ransomware attacks, all while staying remarkably under the radar. This stealthy threat uses clever tactics like running payloads in memory and mimicking legitimate Microsoft security tools to evade detection.
AI Enables Faster, Cheaper Cyber-Attacks
Cyber attacks just got a whole lot faster, cheaper, and sneakier thanks to AI, which is now a key player in the cybercrime world, enabling attackers to launch more sophisticated and elusive threats. ReliaQuest reports that AI is revolutionizing the attack workflow, making it easier for attackers to scale, customize, and slip past traditional defenses.
Iranian Drone Swarm Poses Questions After F-15E Downing
An F-15E pilot described a chilling scene before ejecting from his downed jet: a swarm of Iranian drones moving in unison, resembling a jellyfish with smaller drones clustered beneath larger ones like legs. This unprecedented encounter has raised more questions than answers.
Space Force Must Prepare for Complex Warfare Scenarios
The Space Force must gear up for a new era of complex warfare, where the lines between attack and defense are increasingly blurred. Imagine a world where cyber-attacks, satellite jamming, and mysterious sabotage converge to challenge our national security.
FortiBleed Exposes 110 Million Credentials in Global Firewall Hack
A recent global firewall hack, dubbed FortiBleed, has exposed a staggering 110 million credentials, putting countless individuals and organizations at risk. This massive breach was made possible by a sophisticated five-stage pipeline that allowed hackers to capture sensitive information, including cleartext and hashed credentials, from compromised devices.
US Eyes Civilian Hackers to Bolster Cyber Operations
The US is considering a game-changing move: enlisting civilian hackers to help breach foreign computer systems, with a pilot program proposed in the Senate Armed Services Committee's defense policy bill. This bold plan would bring private sector expertise under the operational control of US Cyber Command.
Scattered Spider Members Plead Guilty Over Major Cyberattacks
Two young members of the notorious Scattered Spider group have pleaded guilty to cyberattack charges in London, admitting to crippling Transport for London's computer systems and putting human welfare at risk. The guilty pleas come as prosecutors reveal the group's victims paid a staggering $115 million in ransom payments.
Scattered Spider hackers plead guilty to TfL cyberattack
Two young hackers, part of the notorious Scattered Spider group, have pleaded guilty to orchestrating a devastating cyberattack on Transport for London, causing millions in losses and disrupting the lives of countless commuters. The breach, which lasted several days in September 2024, forced TfL to acknowledge that sensitive customer data had been stolen.