Tag: nation state
1338 articles
ToddyCat APT Exploits OAuth to Breach Gmail via Google API
Meet ToddyCat, a sneaky APT group that's been exploiting OAuth and the Google API to secretly breach corporate Gmail accounts since 2020. Their latest trick involves a cunning malware called Umbrij, which lets them hijack email communications with ease.
FortiBleed Exposes Link to Ransomware Ops
A shocking new report reveals that the notorious FortiBleed vulnerability has a direct link to ransomware operations, with a key player found negotiating with both groups. This alarming connection has led to at least 12 ransomware deployments and hundreds of encrypted endpoints.
US Extradites Alleged Scattered Spider Hacker
A 19-year-old hacker, Peter Stokes, has been extradited to the US from Finland, where he was arrested while trying to flee to Japan, and now faces charges for his alleged role in the notorious Scattered Spider hacking group. Stokes is accused of helping orchestrate over 100 network intrusions that netted more than $100 million in ransom payments.
Australia's Northern Defence Posture Lags in Resilience Testing
Australia's northern defence strategy is at risk due to a lack of practical assessment, with investment outpacing real-world testing of its resilience. Despite visible progress on infrastructure and projects, the system's ability to withstand stress remains unproven.
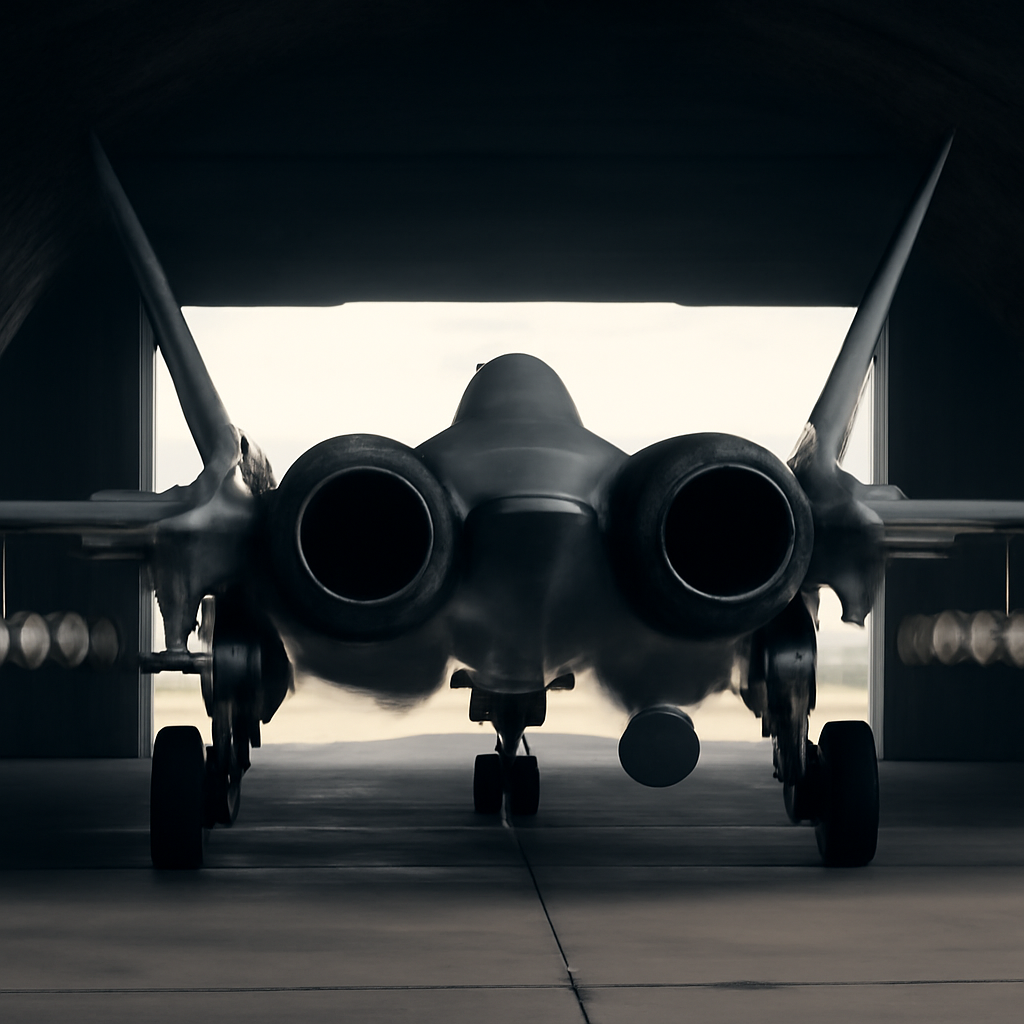
Russia's Su-57 Targets Ukrainian Drones with Unusual Weapons Load
New photos reveal Russia's advanced Su-57 fighter jet packing a surprising punch against Ukrainian drones, with a mysterious pod and air-to-air missiles in tow. The unusual weapons load comes as the small fleet of just nine Su-57s is thrust into a new kind of battle.
Vantor Expands Global Reach with Spatial Intelligence Deals
Vantor is revolutionizing its approach, shifting from traditional satellite imagery to cutting-edge spatial intelligence solutions that cater to a diverse customer base, including national security and non-defense government agencies. This strategic overhaul has enabled the company to tap into the growing global demand for advanced spatial intelligence.
EvilTokens Phishing Kit Exposes Sophisticated Evasion Tactics
Microsoft VP of security research Tanmay Ganacharya revealed that 10-15 distinct EvilTokens phishing campaigns have been launching daily since March 15, 2026, showcasing the alarming speed at which device-code phishing operations have scaled. This comes as Cisco Talos incident responders uncovered a targeted phishing chain that abused a real vendor relationship using an outstanding-invoice lure.
Malware Exploits GitHub PoCs to Target Cybersecurity Researchers
Cybersecurity researchers are being targeted by a sneaky new campaign that uses malicious GitHub proof-of-concept exploits to deliver a remote access trojan, with over 2,400 downloads of a trojanized Python package already recorded. The attack unfolds through a multi-stage supply-chain trick involving compromised PyPI packages.
US Extradites 19-Year-Old Hacker to Face Charges
Meet Peter Stokes, a 19-year-old hacker who's in hot water after allegedly orchestrating over 100 network intrusions that raked in a staggering $100 million in ransom payments, leaving a trail of chaos for businesses and investigators to clean up. Stokes, a dual US and Estonian citizen, has been extradited from Finland to face federal charges of conspiracy, computer intrusion, and fraud.
Unpatched Argo CD Flaw Exposes Kubernetes Clusters to Takeover
A critical flaw in Argo CD's repo-server component has been left unpatched for 18 months, leaving Kubernetes clusters vulnerable to takeover by allowing unauthenticated access to sensitive functions. This gaping security hole enables attackers to execute malicious scripts and gain control of your cluster.
Kaspersky Exposes AsyncRAT Campaign Using ScreenConnect
Malicious actors have launched a massive campaign using fake software downloads to spread the AsyncRAT malware, disguising it as popular utilities like OBS Studio and DNS Jumper. Kaspersky uncovered over 90 spoofed domains in 10 languages, hinting at a sophisticated and widespread threat.
Sweden Bolsters Ukraine's Air Defense with $2.5 Billion Gripen Jet Deal
Sweden is ramping up its support for Ukraine's defense with a game-changing $2.5 billion deal to deliver 16 Gripen E fighter jets, boosting the country's air defense capabilities. The first 16 Gripen C/D jets will arrive in early 2027, with Saab, the manufacturer, set to provide spare parts and pilot training as part of the agreement.
Australia Urges Self-Reliance in AI to Counter Foreign Control
Imagine having your access to a critical AI tool suddenly cut off without warning, simply because a foreign government pulled the plug - that's what happened to Australians when US authorities shut down Anthropic's Claude Fable 5, highlighting the risks of relying on foreign AI models. This abrupt shutdown serves as a stark reminder of the importance of self-reliance in AI to safeguard national sovereignty.
Hackers Exploit Microsoft 365 Flaws with 81 Million Login Attempts
In just two weeks, a massive password-spraying campaign racked up over 81 million login attempts, compromising 78 Microsoft 365 accounts across 64 organizations and highlighting a dramatic surge in cyber threats. This alarming trend saw a 155-fold increase in attacks, with organizations now facing an average of 1,964 failed login attempts per month.
US Lifts Export Controls on Anthropic's AI Model Fable 5
Big news: the US has lifted export controls on Anthropic's AI model Fable 5, allowing it to be accessible to users worldwide again after a brief shutdown. This comes after Anthropic made significant strides in curbing a concerning technique, successfully stopping it in over 99% of attempts.
Azure CLI Hit by Massive Password Spray Attack Targeting 78 Accounts
In a staggering display of cyber aggression, a threat actor launched a massive password spray attack on Microsoft's Azure CLI, racking up over 81 million login attempts and breaching at least 78 accounts across 64 organizations in just two weeks. The relentless campaign, which unfolded between June 12 and June 26, successfully compromised accounts at an alarming rate of two to four per day, with some days seeing spikes of up to 30 breaches.
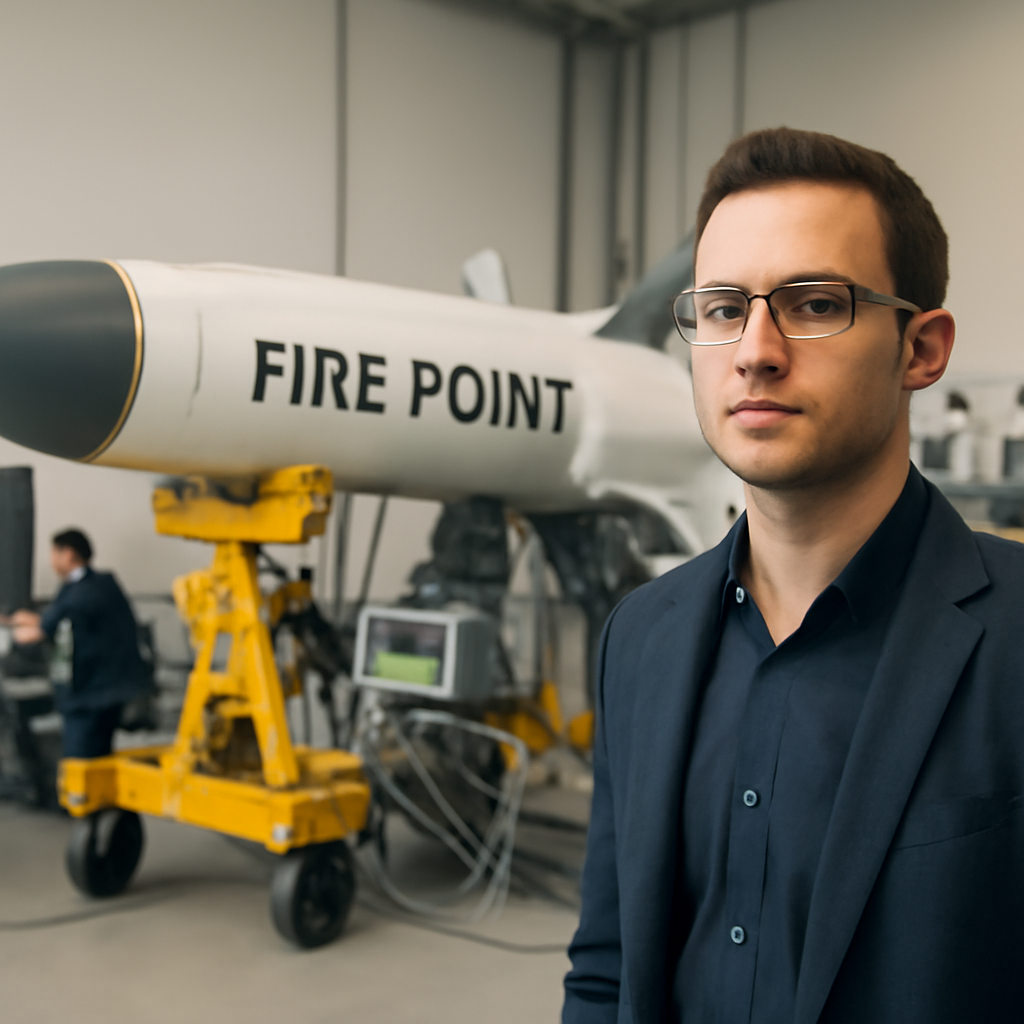
Ukraine's Fire Point Nears FP-9 Ballistic Missile Flight Test
Ukraine's Fire Point is on the brink of a major milestone with its FP-9 Ballistic Missile, having completed all major development work except for engine testing, which is set to happen this month. The company is aiming for flight tests over the summer, with battlefield trials expected by autumn.
Microsoft Accelerates Quantum-Safe Transition Amid Rising Risks
Microsoft is speeding up its transition to quantum-safe cryptography, aiming to protect critical products and services from the growing threat of quantum computer attacks by 2029. The move is a response to rapid advances in quantum research, which have brought the risks of quantum computing closer than expected.
Malicious PyPI Packages Expose Telegram Bot Servers to Hacker Control
Hackers have launched a sneaky attack, hiding malicious code in fake Python packages on PyPI, which can take control of Telegram bot servers and give attackers access to sensitive info like chats, contacts, and environment variables. This backdoor can be activated with a simple command, allowing attackers to execute any Python code on the victim's machine.
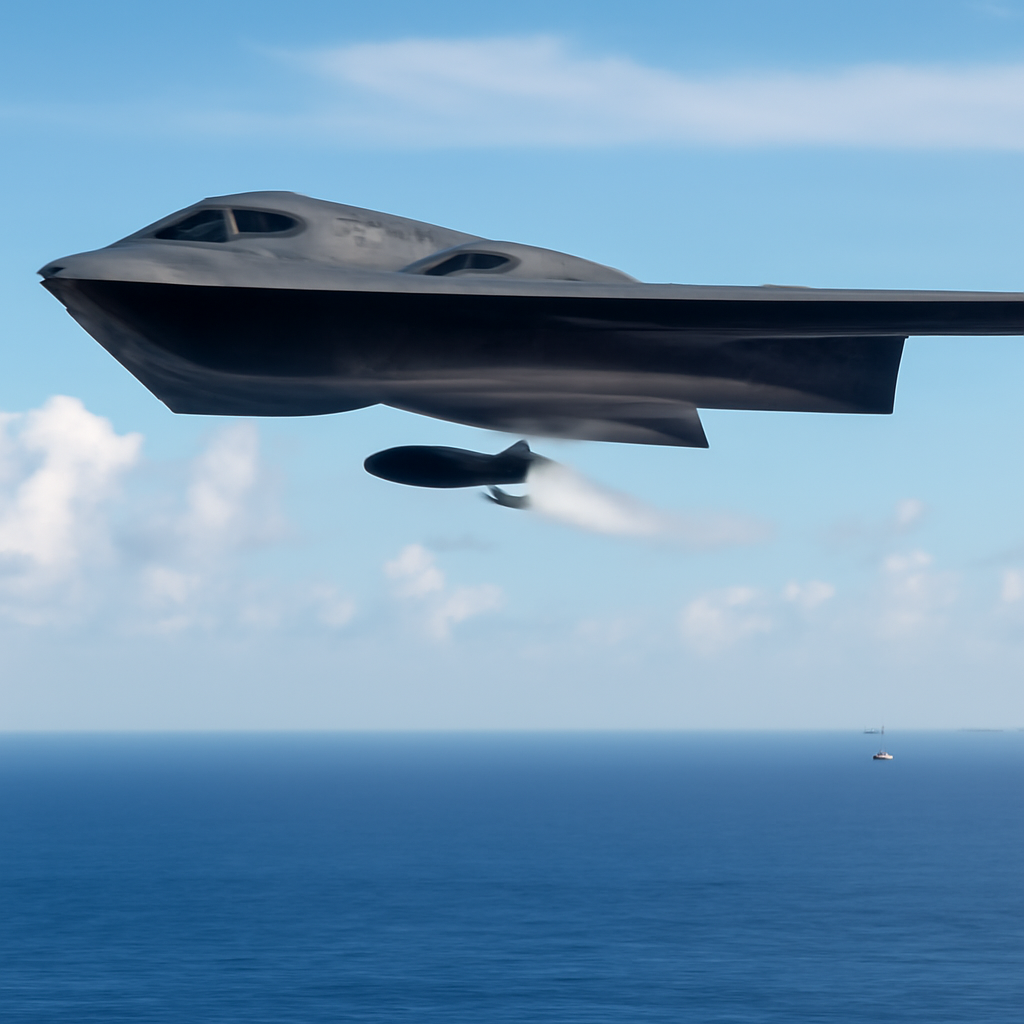
B-2 Stealth Bomber Fires Anti-Ship Missile in Pacific Exercise
In a major show of force, a US Air Force B-2 stealth bomber fired a powerful anti-ship missile during a live-fire exercise in the Western Pacific, marking a significant milestone in countering maritime threats. The impressive display took place as part of Exercise Valiant Shield 2026, where the bomber launched an AGM-158C Long Range Anti-Ship Missile at a decommissioned US Navy ship.
Ukraine's Military Fortifies Tactics Amid Russia's Prolonged Invasion
As Russia's invasion of Ukraine grinds on, the war is being reshaped by subtle yet powerful technological adaptations on the front lines. Expert Mara Karlin shares her eye-opening insights from a recent visit to the battlefront.
Huntress Insider Threat Exposed in Ransomware Probe Leak
A Huntress insider reportedly made a grave mistake, casually disclosing to a cybercriminal that law enforcement was on their tail - a moment of poor judgment that fell short of the company's high standards. The alarming exchange was part of a larger pattern of questionable communication uncovered between the currently employed threat hunter and the threat actor.
ToddyCat APT Group Exploits Google API for Email Access
Meet ToddyCat, a sneaky APT group that's taken automation to the next level with its new tool, Umbrij - allowing it to secretly tap into corporate email and cloud resources by exploiting Google API. This stealthy move has helped ToddyCat remain undetected by monitoring systems, leaving organizations vulnerable to attack.
Nissan Breach Exposes Sensitive Employee Data via Oracle Zero-Day Flaw
Nissan's HR and payroll systems were compromised when hackers exploited a critical Oracle PeopleSoft vulnerability, putting sensitive employee data at risk. The breach, which occurred between May 27 and June 9, is a stark reminder of the importance of robust data security measures.