Tag: nation state
1338 articles
GitHub Repositories Targeted in FakeGit Malware Campaign
A massive FakeGit malware campaign has infected nearly 7,600 GitHub repositories, cleverly disguising itself as legitimate projects and even tricking AI agents with convincing READMEs and fake developer profiles. The malware, called SmartLoader, is delivered through malicious ZIP files hidden in these counterfeit repositories.
Malware Hides in Microsoft 365 Calendars via HOLLOWGRAPH Campaign
Meet HOLLOWGRAPH, a sneaky malware that's hiding in plain sight - using Microsoft 365 calendars to pull off a highly targeted espionage threat. This compact implant is reading and writing secret messages, all while masquerading as a harmless calendar event.
Russian Hackers Exploit IP Cameras to Spy on NATO, Ukraine Military Logistics
Russian hackers are exploiting internet-connected security cameras to spy on NATO and Ukraine's military logistics, with over 87,000 cameras across the EU and Ukraine vulnerable to a known exploit. This alarming operation, revealed by Dutch intelligence, has left sensitive sites exposed to Russian surveillance.
Russian Hacker Exploits Google AI to Control Botnet
A solo Russian hacker, going by the name "bandcampro", cleverly exploited Google's AI tool to build a sneaky botnet operation that was incredibly lightweight, consisting of just three plaintext files totaling 5 KB. This made it easy to replicate and dispose of, allowing the hacker to stay one step ahead.
UK Police Chiefs Push for Cybercrime Risk Orders After TfL Hack
The UK's National Crime Agency has hailed a major cybercrime case as its most complex investigation to date, after two men were jailed for their role in the massive TfL hack, and is now calling for new powers to tackle the growing threat of cybercrime. The case has sparked renewed demands for Cybercrime Risk Orders to help manage and mitigate cyber risk.
RubyGems Packages Targeted in SleeperGem Supply Chain Attack
Researchers have uncovered a sneaky supply chain attack, dubbed SleeperGem, that uses malicious RubyGems packages to infiltrate developer machines and download additional payloads. The attack relies on three rogue packages, each acting as a loader to fetch a second-stage payload.
SonicWall SMA Zero-Days Exploited to Gain Root Access
A newly identified threat actor, UTA0533, has been caught exploiting zero-day vulnerabilities in SonicWall SMA VPN appliances to gain root access, using custom malware and other sophisticated tactics. This alarming attack was uncovered during an incident response in July, with two compromised appliances detected in a single environment.
Russian Hackers Exploit ClickFix CAPTCHAs to Spread Malware in Ukraine
Ukraine's Computer Emergency Response Team (CERT-UA) warns that Russian hackers, part of the notorious Sandworm group, are using manipulated CAPTCHAs to trick victims into downloading malware, specifically targeting Ukraine with data-stealing attacks. They've been linked to a series of social engineering scams that spread malware through legitimate websites.
Hackers Exploit ViPNet Software to Target Russian Government Agencies
A sophisticated cyber attack, dubbed HelloNet, has been targeting high-profile Russian organizations, including government agencies, energy companies, and educational institutions, since at least May. The hackers are exploiting a popular networking software to deliver a powerful proxy and loader, allowing them to gain a foothold and spread their reach.
US, Iran Escalate Strikes on Infrastructure Targets
Tensions are running high as the US and Iran exchange blows, with President Trump vowing to hit hard and expand targets to power plants and bridges, sparking a week of escalating strikes and counterattacks on infrastructure across the region. The Pentagon is ramping up its military presence, shifting aviation and tanker assets into position to support the growing conflict.
GoldenEyeDog Exploits DigiCert Breach for Code-Signing Certificates
In a chilling example of malware mastery, the GoldenEyeDog group exploited a DigiCert breach to snag code-signing certificates, which they then used to cloak their malicious software in a veneer of legitimacy. This brazen heist highlights the group's cunning and capabilities, which have been under scrutiny since at least 2015.
UK Sentences Scattered Spider Members to 66 Months for Cyberattacks
In a major cybercrime crackdown, two young men have been sentenced to 66 months in jail for their role in a 2024 cyberattack that crippled Transport for London's network operations. Thalha Jubair and Owen Flowers were arrested and pleaded guilty, marking a significant win for the UK's National Crime Agency after nearly two years of investigation.
Trump Escalates Claims of Election Compromise Despite Debunked Evidence
The White House touted a prime-time speech as proof of foreign interference and widespread voter irregularities, but it fell flat, with critics calling it a dud. Despite claims of a bombshell, the declassified documents so far have failed to validate allegations of election compromise.
China Builds Massive Supply Ship for Carrier Groups
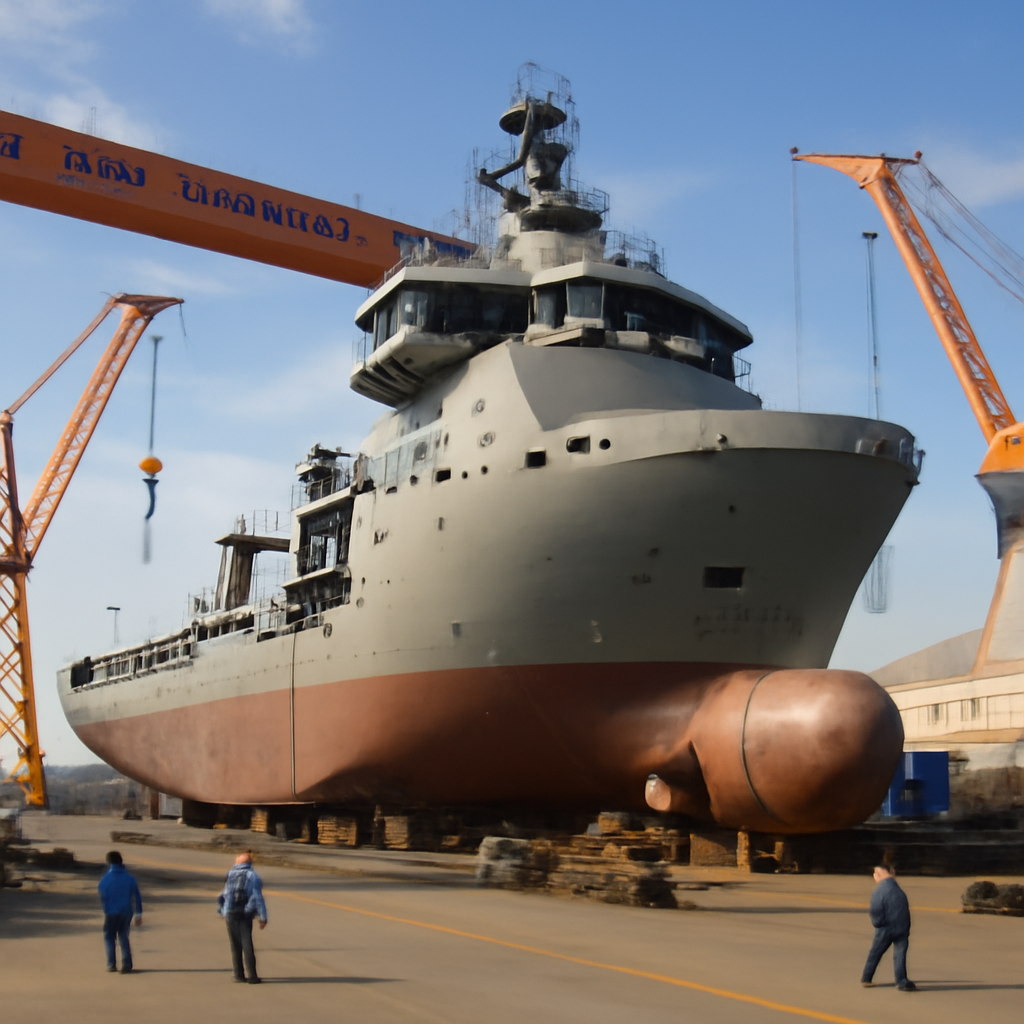
China is building a massive supply ship that has caught the world's attention, particularly in the US, as it signals a new era of maritime power. This hulking vessel, rising from the shipyard on Longxue Island, is set to support China's carrier groups and challenge traditional naval dominance.
Southeast Asia Accelerates Military Modernization Amid Geopolitical Tensions
Southeast Asia is rapidly upgrading its military arsenal, with Indonesia leading the charge with major deals, including the purchase of 42 Rafale fighter jets from France and talks to acquire South Korea's KF-21 Boramae fighters. The region's defense modernization is gaining momentum and shows no signs of slowing down.
North Korean Hackers Exploit Coding Tests with Steganography-Laced Malware
North Korean hackers are targeting software developers with a sneaky malware attack, hiding steganography-laced payloads in coding tests to steal sensitive data and cryptocurrency. This latest campaign, tracked as REF9403, is just another example of the DPRK's relentless pursuit of valuable information.
US Misidentifies Russian Hacker in Extradition Bid
A Russian man named Aleksandr Ermakov has been wrongly detained in an Armenian jail on a US extradition request, with his lawyers claiming he is not the REvil ransomware suspect the US is actually after. His family and lawyers are now racing against time to clear his name and prevent his deportation to the US.
GoSerpent Malware Targets Southeast Asian Governments for Espionage
A stealthy cyber threat, known as GoSerpent, has been secretly targeting Southeast Asian governments and diplomats since late 2025, with the goal of gathering sensitive intelligence. This sophisticated malware has been evolving, with a new set of malicious tools deployed as recently as May 2026.
CISA Orders Emergency Patch for Exploited Fortinet Vulnerabilities
The US Cybersecurity and Infrastructure Security Agency (CISA) has issued an emergency directive requiring federal agencies to patch or mitigate two critical Fortinet vulnerabilities within a tight three-day window, underscoring the severity of these flaws. This urgent action follows the discovery of a critical OS command injection vulnerability in FortiSandbox, allowing attackers to execute unauthorized code or commands.
US Indicts Russians for Running Bulletproof Hosting Services
The FBI has struck a major blow against cybercrime by indicting three Russian nationals and two companies for operating bulletproof hosting services that enabled devastating attacks on US critical infrastructure. This significant move disrupts the backbone of cybercriminal operations, dealing a crucial win for online safety.
South Korea Develops Sovereign AI Model for Bug Detection
South Korea is racing to develop its own AI model for bug detection by 2026, driven by concerns that relying on foreign models could leave the country vulnerable at critical moments. The homegrown AI model aims to rival leading security-focused models, ensuring the nation has control over its bug-finding capabilities.
ViPNet Update System Exploited in HelloNet APT Campaign
Kaspersky uncovered a sneaky APT campaign, HelloNet, that exploited the ViPNet Update System to spread malware, starting as far back as May 2026. The attackers cleverly used a malicious library to hijack the ViPNet updater, allowing them to siphon off sensitive info and clean up their tracks.
China Weighs Risks in J-35 Fighter Jet Sale to Pakistan
A potential deal for Pakistan to acquire 40 advanced J-35 fighter jets from China has been rumored since 2024, but remains unconfirmed - if finalized, it could drastically shift the balance of power on the Indian subcontinent. The sale would mark a significant boost for Pakistan's military, but China is reportedly exercising caution to avoid giving Islamabad too great an advantage.
China-Linked Malware Resurfaces in Taiwan with Advanced Backdoors
Meet Daxin, a sneaky kernel-mode rootkit that's been upgraded with advanced backdoors, allowing it to hijack legitimate connections and evade detection by blending into normal network activity. This China-linked malware has a unique trick up its sleeve, monitoring incoming TCP traffic to carry out encrypted communications undetected.