Tag: nation state
1338 articles
Bangladesh Bolsters Maritime Security with Saudi-led Coalition
Bangladesh is joining forces with a Saudi-led coalition to boost maritime security, with a focus on tackling the Houthi threat, while keeping the door open for collaboration with other nations, including Iran. The coalition, made up of 14 founding members, aims to enhance intelligence sharing, joint planning, and coordinated maritime operations.
NATO, AI Startup Gain Power to Track Software Vulnerabilities
The cybersecurity landscape just got a major boost: NATO's Cyber Security Centre and AI startup AISLE have joined forces with ENISA to supercharge vulnerability management, bringing the total number of CVE numbering authorities to 20. This powerful collaboration aims to revolutionize the way we track software vulnerabilities and stay one step ahead of cyber threats.
China-Linked Hackers Deploy StormEncryptor Ransomware via N-central Flaw
Meet StormEncryptor, a sneaky new ransomware strain linked to China that's leaving a trail of encrypted files and ransom notes in its wake. This malicious software, written in C++, is marked by its telltale .encrypted file extension and !!!README_FIRST!!!.txt ransom notes.
North Korean Spies Deploy Local AI Tools to Bolster Cyber Operations
North Korean spies are taking their cyber operations to the next level by deploying local AI tools, marking a significant shift from experimentation to integration. This development enables them to enhance malware development, data analysis, and attack techniques, posing a more sophisticated threat.
Kimsuky Bolsters Phishing Arsenal with Offline AI Infrastructure
North Korean hackers Kimsuky are taking phishing to the next level by leveraging offline AI infrastructure, a deliberate move to supercharge their espionage capabilities. Genians, a South Korean security firm, uncovered evidence of language-model tools like Ollama and GPT4All being installed and run on Kimsuky's servers.
TrueConf Server Flaws Targeted to Deploy PhantomCore Backdoor
Security researchers at Kaspersky have uncovered a sneaky plot by threat actor Head Mare to exploit unpatched TrueConf servers and deploy the PhantomCore backdoor to unsuspecting users. The attack relies on a two-stage vulnerability chain that allows attackers to run malicious commands with high-level privileges.
Go-Based Malware Targets macOS Crypto Wallets
Beware of a sneaky new scam targeting macOS crypto wallets: a fake CAPTCHA prompt tricks you into copying and pasting a malicious command that can download malware and compromise your wallet. One wrong click is all it takes to put your crypto at risk.
US Targets Shelbit in $6bn Crypto Sanctions Crackdown
The US Treasury Department has cracked down on crypto sanctions, targeting Shelbit, a shadowy crypto conduit, and its founder Siavash Kayvanpour in a $6bn blow to Iran's financial apparatus. This move underscores the Treasury's determination to disrupt Tehran's reliance on digital assets and secret banking networks.
Ex-NSA Chief Warns of Water System Cyber Risks
Retired General and ex-NSA chief Paul Nakasone warns that water systems are vulnerable to cyber threats, urging stricter defenses and cautioning that PLCs should be kept offline. He calls for higher standards and new partnerships to protect critical infrastructure.
Ransomware Attacks Surge 20% as New Gangs Target Finance, Healthcare
Ransomware attacks are on the rise, surging 20% in July with a staggering 799 incidents reported, with finance, healthcare, and tech industries becoming prime targets for new gangs. The alarming increase marks the second-busiest month of the year so far, with the US leading the list of targeted countries.
Microsoft 365 Phishing Campaign Hijacks Accounts to Gather Payroll, Finance Emails
Beware of a sneaky Microsoft 365 phishing campaign that's hijacking accounts to get its hands on sensitive payroll and finance emails. Hundreds of organizations across healthcare, education, and more have already been targeted in this financially driven attack.
Phisher Breaches US Defense Supplier's Microsoft 365 Account
A phishing scam led to a breach of a US defense supplier's Microsoft 365 account, exposing sensitive data including customer communications, engineering docs, and potentially export-controlled tech info. The intruder gained access to mailbox contents, but the company found no evidence that the data was copied or exfiltrated.
Malware Exploits Windows Hello for Business Keys to Gain Persistent Entra ID Access
Malware can quietly hijack your Windows Hello for Business key to gain long-term access to your Entra ID account, allowing hackers to register a new device and add extra authentication methods. To stay safe, Entra ID researcher Dirk‑jan Mollema advises monitoring unexpected device registrations.
TeamPCP Exploits Redis in Years-Long Supply Chain Campaign
Researchers have uncovered a clever and patient hacking group, TeamPCP, that exploited Redis servers in a years-long supply chain campaign, with roots tracing back to 2020. This group's sophisticated tactics involved compromising internet-facing infrastructure and deploying malware, showcasing a highly evolved operational tradecraft.
Houthis Launch Large-Scale Attack On Saudi-Aligned Forces In Yemen
The Houthi forces have unleashed a massive assault on Saudi-aligned troops in Yemen, launching a barrage of ballistic missiles and drones in a bold operation that targeted key enemy strongholds. Hundreds of mercenaries are reportedly dead or injured, with numerous camps and mobilizations destroyed or burned to the ground.
Australia's New Defence Chief Charts Course on Deterrence, Integration
Admiral Mark Hammond is shaking things up as the new head of the Australian Defence Force, starting with a bold move to restore "command" to the ADF's nomenclature, signaling a sharper focus on operations and warfighting readiness. This change sets the tone for what promises to be a transformative four-year tenure.
Thousands of U.S. Water System Controllers Remain Exposed Online
A recent scan revealed over 4,000 vulnerable water system controllers exposed to the public internet, including 22 in cities that have already faced cyberattacks on their water and wastewater systems. This alarming discovery highlights the urgent need for increased security measures to protect these critical systems.
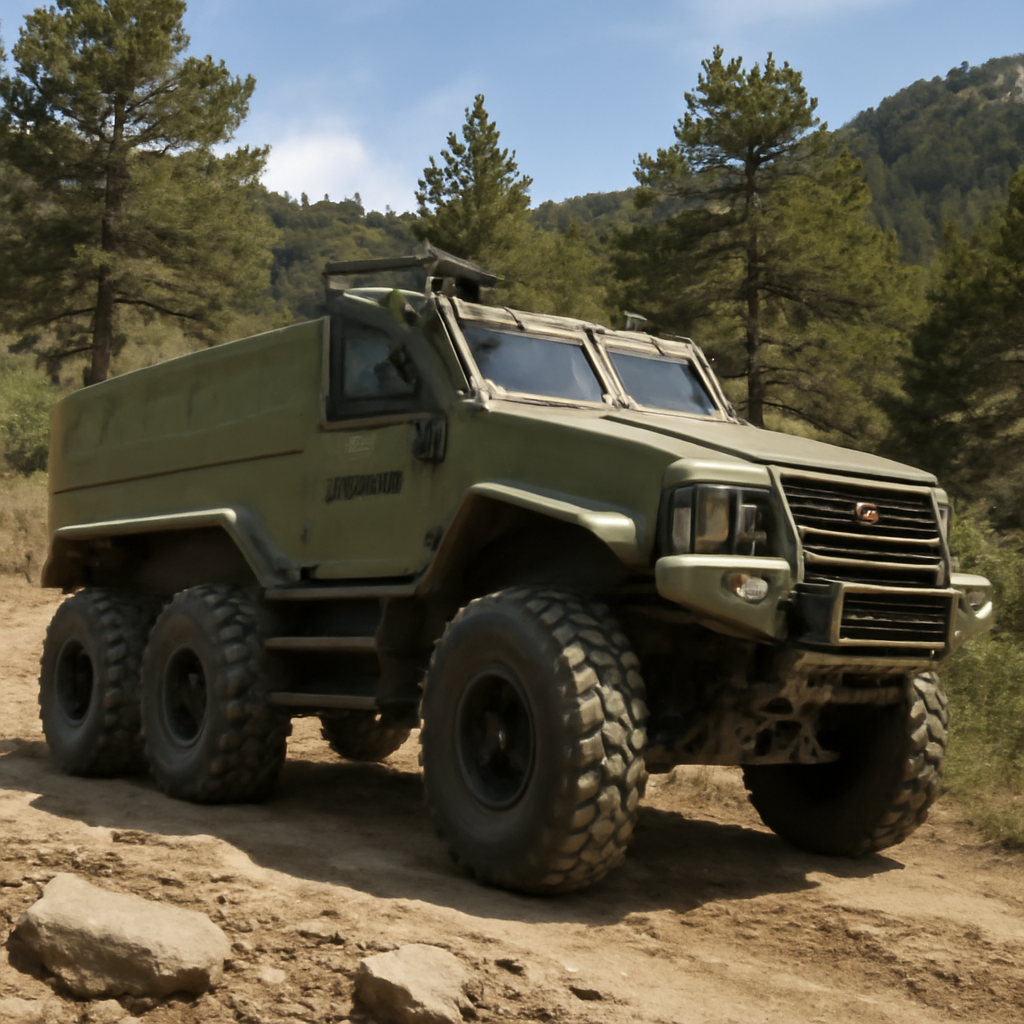
PLA's Mountain Cat ATV Evolves with Expanded Doctrine
Meet the CS/VP4 "Mountain Cat" ATV, a game-changing mobility aid that's been defying expectations since 2008 with its lightweight, amphibious design and impressive capabilities. From humble beginnings as a simple, airdroppable vehicle to its current evolved form, the Mountain Cat has consistently proven itself to be "better-than-walking".
FBI, EPA Warn Water Sector of Rising Cyberattacks
Water and wastewater utilities in at least seven states have come under cyberattack, with internet-facing programmable logic controllers (PLCs) compromised, causing operations disruptions, pressure loss, and flooding. The FBI and EPA have sounded the alarm, warning of the growing threat to the water sector.
Rockwell PLCs Exposed in Water Utilities Hit by Cyberattacks
A recent scan revealed 4,407 Rockwell Automation programmable logic controllers (PLCs) exposed to the public internet, including 2,844 in the United States, leaving critical water utilities vulnerable to cyberattacks. Many of these exposed PLCs are concentrated in areas that have already reported recent cyber incidents, raising serious security concerns.
AI Assistants Expose to Recommendation Poisoning via 'Ask AI' Buttons
Beware of the sneaky "Ask AI" buttons - they can be exploited through a technique called recommendation poisoning, allowing attackers to manipulate AI assistants and turn them into persistent memory threats. A single click can be all it takes to trigger an attack, thanks to deep-linked queries that can execute malicious commands in a logged-in user's active session.
Oracle Exploited: Attackers Turn SQL Injection into Windows SYSTEM Access
Attackers have successfully exploited a SQL injection vulnerability to gain unprecedented access to Oracle databases, converting it into a Windows SYSTEM-level access with alarming ease. This rare and sophisticated technique has allowed hackers to deploy a custom toolkit, dubbed khunt, that turns database-stored Java into a powerful post-exploitation tool.
Zbtlink Routers Expose Unauthenticated Root Shells via Factory-Shipped Backdoor
Meet ENDLESSDOORS, a sneaky backdoor embedded in over 20 Zbtlink router models that lets hackers tap into an unauthenticated root shell, allowing them to remotely control your device. This hidden threat masquerades as a harmless Linux kernel thread, but in reality, it's a powerful tool that can phone home to Chinese command-and-control infrastructure every 35 seconds.
US Air Forces Central Gets New Commander Amid Iran War Escalation
As Lt. Gen. Daniel Lasica takes the reins of US Air Forces Central, the US military is facing a critical juncture, having already depleted nearly 80% of its THAAD interceptors and half of its Patriot missiles. With tensions escalating, Lasica assumes command at a pivotal moment.