Tag: latin america
35 articles
OpenAI Disrupts Russian, Iranian AI Influence Ops Targeting Western Media
OpenAI just took down a massive AI influence operation that was spreading disinformation across Latin America, targeting Ukraine's reputation and fuelling heated debates in Argentina and Bolivia. The network, dubbed Dark Clark, was using a fake journalist persona and think tank to seed false narratives into mainstream reporting.
Warlock Targets SharePoint Deployments with Ransomware via Exploited Flaws
Warlock, a suspected China-linked threat actor, has launched targeted ransomware attacks on at least four organizations, including critical infrastructure operators, via exploited flaws in on-premises Microsoft SharePoint Server deployments. The victims, located in Portuguese- and Spanish-speaking countries, span across Europe, Africa, and Latin America.
US Treasury Sanctions Tren de Aragua Members Over $40 Million ATM Hacks
The US Treasury Department has cracked down on eight members of the notorious Venezuelan gang Tren de Aragua, sanctioning them for their roles in a brazen $40 million ATM hacking scheme that targeted US bank and credit union machines. Using malicious software, the gang forced ATMs to spit out cash, which was then laundered and transferred to members worldwide.
Data Quality Overtakes Skills as Top Threat Hunting Barrier
Even the best threat hunters can come up empty-handed if their data is incomplete, inconsistent, or hard to access. Data quality has now overtaken skills as the top barrier to effective threat hunting, with 50% of cybersecurity practitioners citing it as their biggest hurdle.
China's Salt Typhoon Targets Latin America with Sophisticated Backdoor Malware
Meet Salt Typhoon, a notorious PRC-backed espionage group that's set its sights on Latin America, infecting government agencies with sophisticated backdoor malware. In just a few months, they've targeted a whopping 90% of their victims in the region, hitting countries including Argentina, Ecuador, and Venezuela.
FamousSparrow Deploys SparroWocky Backdoor in Latin America Push
Meet SparroWocky, a sneaky new backdoor that's been secretly targeting government agencies across Latin America since August 2025, courtesy of the China-aligned threat actor FamousSparrow. This modular malware mastermind can run commands, steal files, and even take screenshots, wreaking havoc on unsuspecting hosts.
FamousSparrow Targets Latin America with SparroWocky Backdoor
Meet SparroWocky, a sneaky new backdoor that's helping the China-aligned threat actor FamousSparrow wreak havoc in Latin America. This modular C++ backdoor has been taking center stage since August 2025, replacing its predecessor SparrowDoor as the group's go-to tool.
China-linked hackers deploy SparroWocky malware in Latin American govt espionage attacks
China-linked hackers are targeting Latin American governments with a new, sneaky malware called SparroWocky, designed to secretly collect intelligence on the region's responses to growing US pressure. The espionage campaign, tracked by ESET researchers, has hit government organizations in at least eight countries across the region.
Malware Exploits Browser Flaws to Force Install Malicious Extensions
A sneaky malware operation, tracked as KREMLIN, has infected 1,515 systems, mostly in Brazil, by secretly installing malicious Chrome and Edge extensions that steal sensitive info. This cunning toolkit impersonates banks to trick victims into giving up their credentials and session tokens.
KREMLIN Malware Targets Chrome, Edge to Steal Credentials
Researchers uncovered a sneaky malware operation, dubbed KREMLIN, that's been targeting Chrome and Edge users since May 2025, infecting over 1,515 systems worldwide, with a staggering 98% of them located in Brazil. The malware uses a clever multi-stage attack to steal credentials, starting with a fake JavaScript file that tricks victims into unleashing the threat.
AI-Powered Attacks Target Latin America With Advanced Proxy Networks
Latin America's transportation, government, and water utility sectors are under siege by sophisticated AI-powered attacks that leverage advanced proxy networks and living-off-the-land techniques to infiltrate and exfiltrate sensitive data. These multi-stage intrusions have already compromised key organizations in Mexico and Ecuador.
Latin America Rebalances China Ties
Honduras's diplomatic shift towards China in 2023 came with a hefty price tag: its shrimp exporters lost access to Taiwan, resulting in plummeting sales, shuttered businesses, and thousands of job losses. The economic fallout has sparked domestic backlash, with the Honduran congress launching probes into Chinese business activities.
Breeze Comet Exploits Brazilian Payment Systems in Hundreds of Fraudulent Transactions
Meet Breeze Comet, a financially motivated threat actor that's been wreaking havoc on Brazilian payment systems with hundreds of fraudulent transactions, exploiting customized malware and compromised websites to siphon off tens of thousands of dollars. Their tactics are evolving, and Latin American countries should beware of potential expansion.
EDGE Expands Cyber Defense Reach with Brazil Military Partnership
EDGE Group is teaming up with the Brazilian army to launch a groundbreaking Cyber Defense Centre of Excellence, positioning Brazil as a leader in Latin American cyber excellence. This strategic partnership combines cutting-edge tech, expertise, and knowledge to bolster Brazil's cyber defenses.
GoCaracal Malware Exploits Ethereum for Covert C2 Communications
Researchers have uncovered a sneaky new malware, GoCaracal, that uses Ethereum to secretly communicate with its controllers, and with medium confidence, they've linked it to the notorious Dark Caracal group. This clever malware was used in a recent attack on a Venezuelan communications organization.
Colombia Secures KC-390 Airlifters in $336 Million Embraer Deal
Colombia's Aerospace Force has sealed a $336 million deal with Embraer for two KC-390 Millennium airlifters, with deliveries set for 2029 and 2030. This strategic move is part of a broader modernization plan, with the FAC choosing the KC-390 after a rigorous analysis.
Brazilian Schools Exposed to Cyberattacks via Weak Credentials, Outdated Systems
Brazilian schools are under cyberattack, with weak credentials and outdated systems leaving them vulnerable to hackers. New data reveals a hotbed of incidents in São Paulo, Rio de Janeiro, and Pernambuco, with private institutions bearing the brunt of high-severity ransomware attacks.
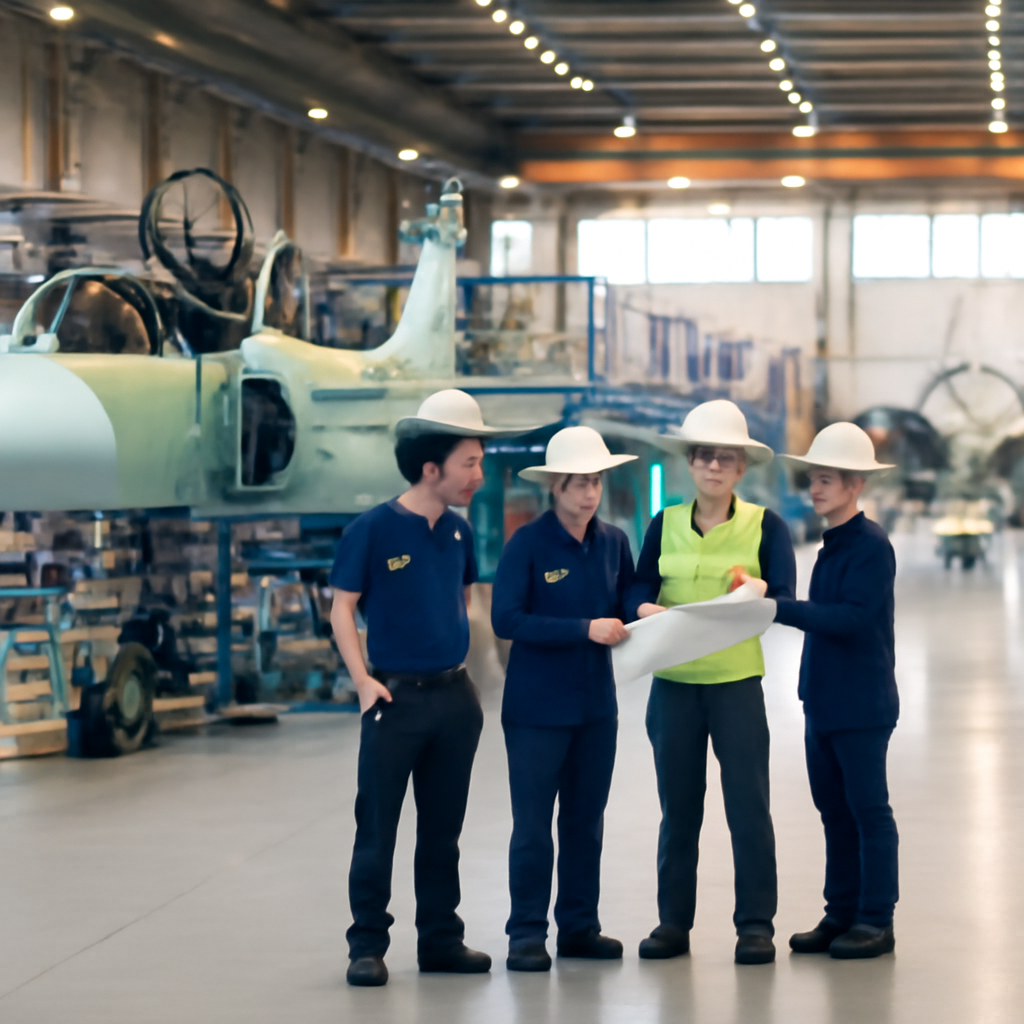
Saab and Embraer Expand Gripen Production Capacity in Brazil
Saab and Embraer are ramping up production of the Gripen fighter jets in Brazil, with a new agreement that authorizes the production of 20 additional Gripen E/F fighters at Embraer's Gavião Peixoto facility. This expansion solidifies their long-term commitment to Latin America and strengthens their industrial partnership.
US Military's War on Drug Trafficking Fails to Yield Results
Despite a massive military effort, with 66 strikes and 221 lives lost, the US war on drug trafficking seems to be having little impact, with cocaine flows to the US remaining steady. The Pentagon's Operation Southern Spear has been touted as a tough new approach, but so far, results are scarce.
BitLocker Extortion Tactics Target Firms via Printer Ransom Notes
Cybercriminals are using a clever and intimidating tactic to extort money from companies, deploying BitLocker to lock down files and leaving ransom notes printed out on physical printers. The attackers guarantee their promises will be kept, boasting a flawless online reputation to back up their threats.
Infostealer Infection Enables Argentine FA Breach
A single compromised computer with high-level access likely gave hackers the keys to the Argentine Football Association's database and internal email system, thanks to an infostealer infection that went undetected for months. The breach, traced back to September 8, 2025, highlights the devastating impact of a simple infection on a high-privilege machine.
SCMBANKER Malware Targets Mexican Banking Users with ClickFix Lures
Mexican banking customers beware: a sneaky new malware campaign, dubbed REF6045, is using fake CAPTCHA pages and social tricks to install a powerful PowerShell toolkit called SCMBANKER on unsuspecting victims' devices. This stealthy attack has been targeting Mexico's financial ecosystem, putting fintech users, payment-processor clients, and cryptocurrency exchange customers at risk.
Ousaban Trojan Expands to Spain, Portugal with Advanced Evasion Tactics
Meet Ousaban, a sneaky banking Trojan that's evolved from decade-old tactics to target unsuspecting customers in Spain and Portugal, starting with a clever phishing PDF disguised as a broken file. This highly optimized threat profiles its victims before striking, making it a force to be reckoned with.
Brazil Probes Hack of Emergency Alert System After Rogue Alert
A bogus emergency alert sent shockwaves across Brazil, pinging mobile devices in multiple states with a mysterious message reading "Alerta extremo - Defesa Civil:misantropi4". The authorities are now scrambling to investigate the hack, with SEDEC and Federal Police on the case.