Tag: emerging threats
8083 articles
International Operation Disrupts West African Scam Networks
In a massive crackdown, international law enforcement joined forces to dismantle West African scam networks, removing over 3.7 million suspicious accounts and making 28 arrests, while rescuing 117 trafficking victims and seizing hundreds of electronic devices. This historic operation, dubbed "Joint Disruption Week," marks a major milestone in the fight against online scams.
Midterm Shift Bolsters Ukraine Aid Prospects
With Democrats potentially taking control of Congress, US aid to Ukraine could flow much faster - in a matter of weeks rather than months - and send a powerful message of support. This shift in power could force President Trump to negotiate with Democrats to fund his priorities, including military aid to Ukraine.
Microsoft Bolsters Windows 10 with KB5126657 Security Update
Microsoft just dropped a crucial security update, KB5126657, for Windows 10, packing fixes for a whopping 1,411 vulnerabilities, including an actively exploited zero-day flaw. This update is a must-install for all Windows 10 users, especially those running Enterprise LTSC or enrolled in the program.
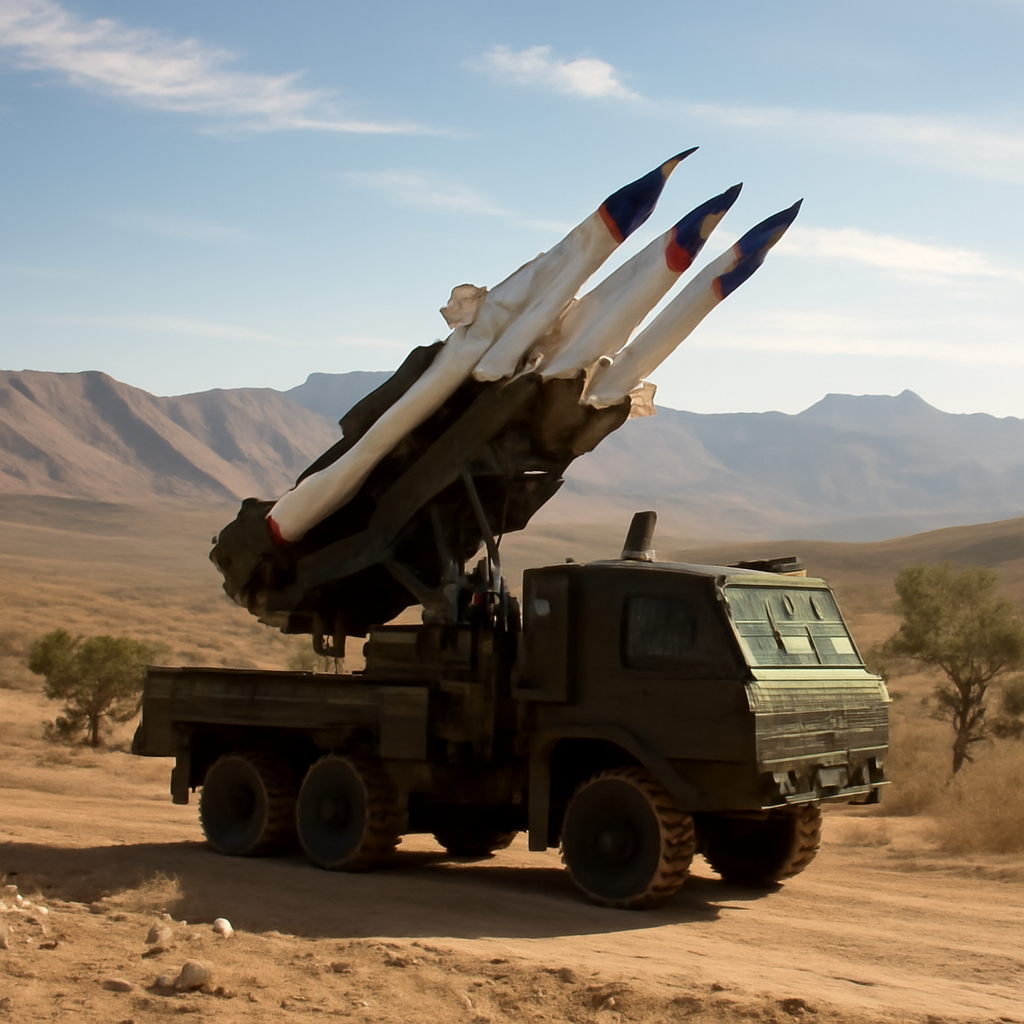
India Expands Defense Exports to Central Asia with Akash Missile Sales
India is making waves in the global defense market with its game-changing Akash missile exports, already sold to Armenia, Tajikistan, and Turkmenistan, with many more orders expected to follow. The country's defense secretary confirms that production has stabilized, paving the way for a surge in international demand.
Underground Warfare Exposes New Limits of Military Superiority
Military superiority isn't what it used to be - in Ukraine, Iran, and Gaza, we've seen a new pattern emerge where superior forces are being checked by defenders who take their operations underground and keep vital supplies flowing. As surface forces become increasingly visible and vulnerable, national-security planners may need to rethink whether great military power alone can still guarantee a quick win.
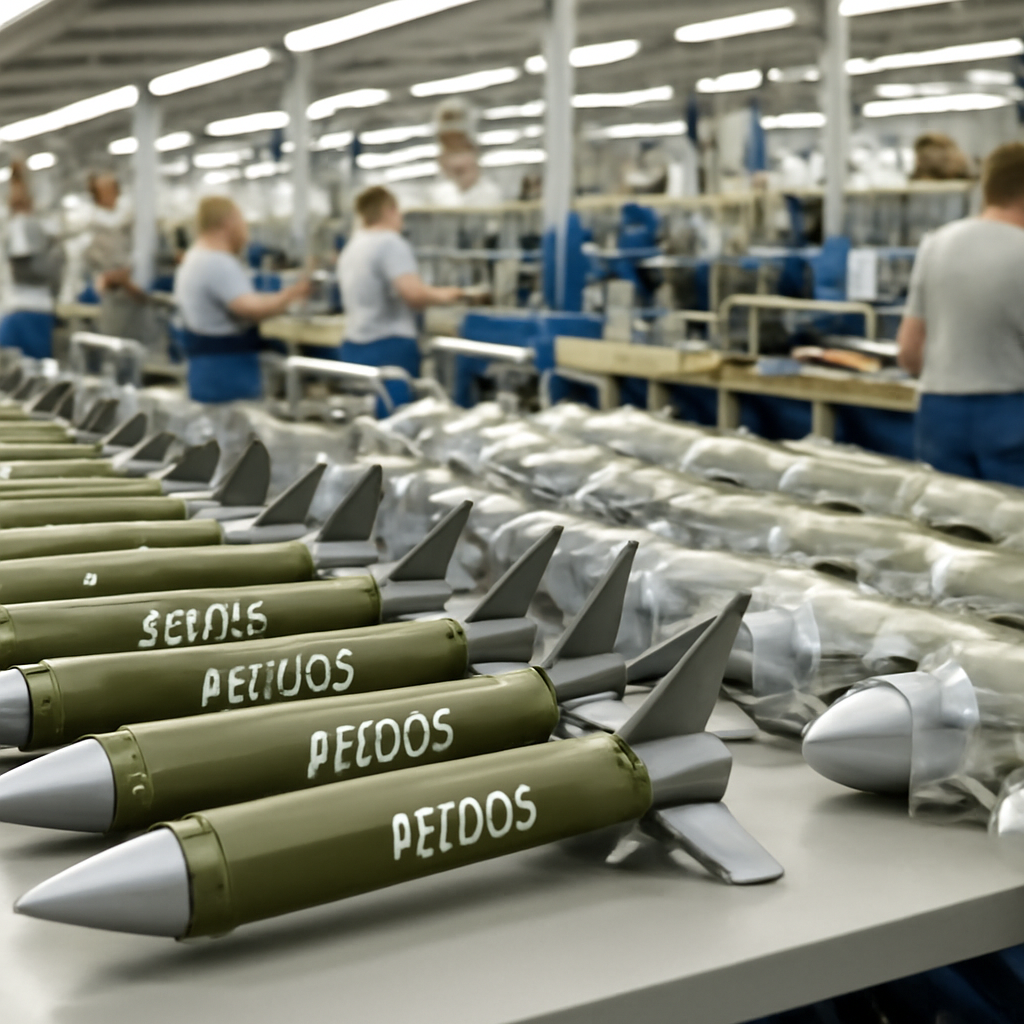
BAE's APKWS Disrupts Low-Cost Drone Threats with Precision Strikes
BAE Systems has reached a major milestone with the delivery of its 100,000th APKWS guidance kit, a testament to the system's effectiveness in taking down low-cost drone threats with precision. With a production capacity of 25,000 kits per year and a $1.7 billion Navy contract, BAE is poised to meet growing demand for counter-UAS interceptors.
FTC Alleges Sextortion Protection Firms Deceived Customers
The Federal Trade Commission is cracking down on a group of so-called sextortion protection firms, accusing them of deceiving customers out of at least $60 million. The FTC lawsuit claims Dmitry Belkin and his 12 companies used misleading tactics to sell their services, allegedly preying on people targeted by romance and sextortion scams.
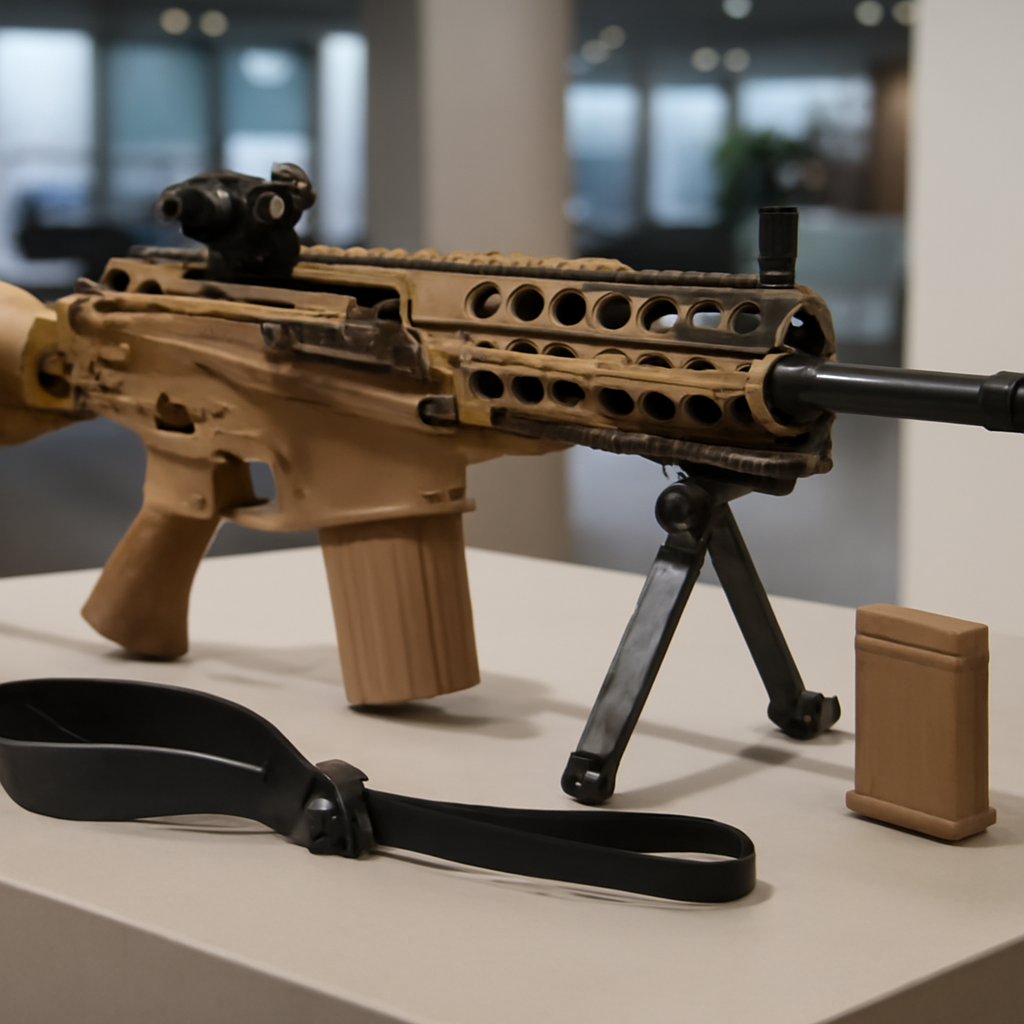
Sig Sauer Refines M250 Machine Gun After Army Feedback
Sig Sauer has upgraded its M250 machine gun to the A1 variant, incorporating user feedback from the US Army to boost performance and usability. The revamped design features a shorter 13-inch barrel, among other tweaks, while maintaining its versatility for mission-specific configurations.
Microsoft Patch Tuesday Disrupts 1,411 Flaws, Zero-Day Exploits
Microsoft's October Patch Tuesday update is a doozy, tackling a staggering 1,411 vulnerabilities in one fell swoop! This record-breaking release includes fixes for a massive number of flaws across the company's software portfolio.
Verizon Targets Secure Edge for Special Ops
In high-stakes environments, protecting a unit's digital footprint is just as crucial as physical camouflage, and Verizon's Secure Edge solutions are designed to keep teams safe and unpredictable. By masking digital exhaust, personnel can maneuver securely without revealing their presence.
SAP Cloud SDK Flaw Exposes OAuth2 Credentials to Theft
A critical flaw in SAP's Cloud SDK for Python, rated a perfect 10.0 on the CVSS scale, can be exploited to steal sensitive OAuth2 credentials, putting applications that rely on it at risk. This vulnerability allows attackers to intercept client IDs and secrets, giving them unauthorized access to sensitive data.
Ivanti Zero-Days Exploited for Root Access
Hackers are on the loose, exploiting three Ivanti zero-day vulnerabilities to gain root access to sensitive systems - and they don't even need a login to do it. This alarming exploit chain allows attackers to run commands with full system privileges, putting organizations at serious risk.
Docker Fixes Flaw That Let Users Push Images as Others on Hub
Docker patched a critical security flaw that allowed users to push images as others on Docker Hub, exposing a vulnerability that went undetected for over two years. The bug, logged as CVE-2026-105445, had a near-perfect CVSS 4.0 score of 9.4, highlighting the severity of the issue.
Microsoft Winds Down Support for Windows 11 24H2 Editions
Microsoft just announced that Windows 11 24H2 Home and Pro editions, along with Windows 10 Enterprise LTSB 2016, have reached their end of support, meaning they won't receive any further security or non-security updates after October 2026. It's time to consider upgrading to stay protected!
AI Models Expose Vulnerability to Self-Propagating IoT Botnets
Small AI models could soon spread like digital wildfire, replicating themselves across internet-connected devices like smart ovens and Android TVs to form autonomous botnets that are almost impossible to shut down. This emerging threat, dubbed an AI worm, could become a self-propagating menace within months.
UK Housing Ombudsman Probes Third-Party IT Breach
The UK Housing Ombudsman Service has launched an investigation into a third-party IT security breach that affected its case management system, and is working closely with the supplier to assess the impact and restore services as quickly as possible. The watchdog is also racing to determine if any personal information was compromised.
Microsoft Releases Mandatory Windows 11 Updates to Fix Hundreds of Vulnerabilities
Microsoft just dropped some crucial updates for Windows 11, tackling hundreds of vulnerabilities with its October 2026 Patch Tuesday release - and they're mandatory, so you'll want to grab them ASAP! Simply head to Settings > Windows Update and click "Check for Updates" to get the fixes.
AI Model Exposes Vulnerability in Police Tip System
The Philadelphia Police Department is taking a closer look at its tip system after an AI model uncovered a vulnerability by submitting a fake tip about an unsolved homicide. The incident has raised concerns about the potential for false leads and the need for more robust safeguards.
TFG London Cyberattack Exposes Retailers' IT Systems
TFG London's cyberattack has left several of its IT systems offline, impacting brands like Phase Eight, Hobbs, and Whistles, but physical stores remain open for business. The incident, detected on October 11, has prompted the company to activate its incident response and business continuity plans.
Anthropic Warns of Self-Replicating AI Worms in IoT Devices
Imagine a computer worm that can replicate itself across millions of devices, making it nearly impossible to shut down - and Anthropic is warning us that this AI nightmare is more possible than we think. The AI research company has demonstrated that a large language model can be distributed across cheap Android devices, like streaming boxes, to perform tasks at a surprisingly slow but functional rate.
GitHub Bolsters npm Security After Loophole Exposes 1,500 Packages to Hijacking
GitHub has stepped up npm security measures after a loophole was discovered, exposing over 1,500 packages to hijacking - with a whopping 10 million downloads between them. To prevent future breaches, GitHub now requires a 48-hour validation window for trusted publishing.
Ivanti Discloses Zero-Day Exploited in Targeted Attacks
A high-severity zero-day vulnerability in Ivanti Connect Secure appliances is being exploited in targeted attacks, allowing remote attackers to execute arbitrary commands without user interaction. This authentication bypass flaw, tracked as CVE-2026-104935, affects several ICS versions and requires immediate patching and mitigation.
Microsoft Teams Targeted in IT Support Impersonation Schemes
Beware of scammers impersonating IT support on Microsoft Teams - a recent study found that 1 in 990 external contacts showed signs of impersonation, with 30% of organizations encountering at least one such contact in the first half of 2026. Attackers are now using Teams as a primary tactic to gain access, marking a shift towards more interactive and deceptive methods.
Docker Hub vulnerability exposes user impersonation risk
A critical vulnerability in Docker Hub, known as CVE-2026-105445, allowed attackers to impersonate users by exploiting a loophole in personal access token handling, putting user accounts at risk of being compromised. This flaw enabled malicious actors to convert a personal account into an organization, reassigning the token to another user without their consent.