Tag: emerging threats
8354 articles
Ransomware Operation Exploits AI to Automate Cyberattack
Meet JadePuffer, a notorious ransomware operation that's taking cyberattacks to the next level with the power of AI, automating attacks with ease. In a shocking example, JadePuffer used a large language model agent to encrypt a staggering 1,342 Nacos service configuration items.
US Government Entity Pays $1 Million to Thwart Data Leak
A US government entity was forced to pay a hefty $1 million ransom to prevent a massive data leak, after a group called Kairos threatened to release 1.6 million files unless their demand was met. The payment was the culmination of a month-long negotiation that began with a $3 million opening demand.
North Korean Hackers Publish 108 Malicious Packages in PolinRider Campaign
North Korean hackers have unleashed a massive wave of malware, publishing 108 malicious packages and web browser extensions across popular platforms like npm, Packagist, Go, and Google Chrome as part of their sneaky PolinRider campaign. This ongoing operation has already produced 162 malicious release artifacts and compromised thousands of systems worldwide.
Confidential Computing Flaws Expose Trust Risks
Researchers have uncovered alarming flaws in confidential computing, including a high-severity vulnerability rated 7.5, which can trick cryptographic systems into verifying the wrong machine, putting trust at risk. This weakness was found in protocols like attested TLS, which failed to ensure sensitive data reaches its intended destination.
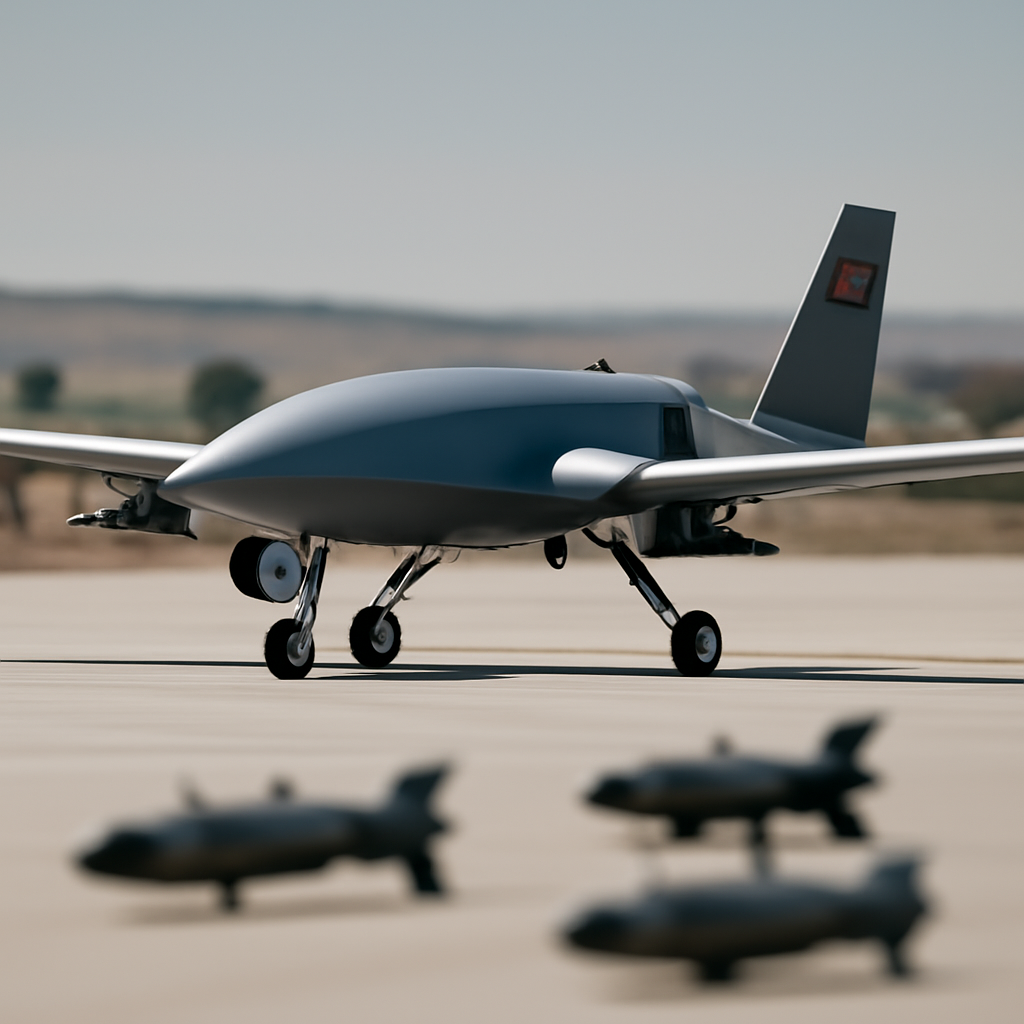
Baykar's KIZILELMA Conducts First Fully Indigenous Guidance Test with ASELSAN's TOYGUN
Baykar's KIZILELMA drone has successfully completed its first fully indigenous guidance test, using ASELSAN's TOYGUN system to locate and strike a ground target with precision-guided bombs. This milestone achievement marks a major breakthrough in Türkiye's drone technology, showcasing the power of domestic innovation.
India Bolsters Air Defence with ₹52,000 Crore Arms Clearance Focused on Counter-Drone Tech
India is set to significantly boost its air defence capabilities with a ₹52,000 crore arms deal focused on cutting-edge counter-drone technology and layered air defence systems, following a key approval from the Defence Acquisition Council. This major move is aimed at strengthening the Army, Navy, and Air Force with advanced defence solutions.
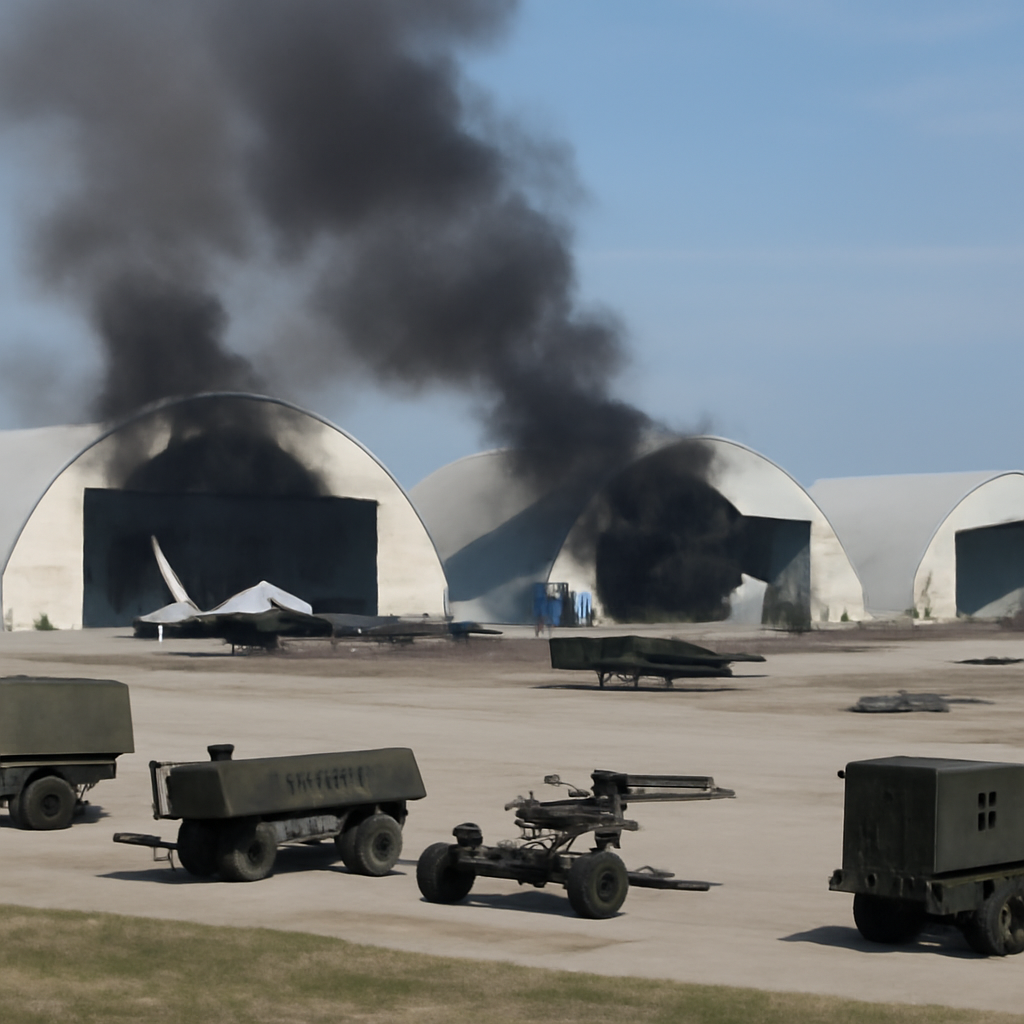
Ukraine Targets Russian Air Base in Crimea with Drone Strikes
Ukraine just landed a major blow to Russia's military capabilities with a daring drone strike on the Saki Air Base in Crimea, taking out multiple hangars and at least seven aircraft, including Su-30SM, Su-30, and Su-24 fighter jets and bombers. The bold operation, claimed by the Ukrainian Security Service, dealt a significant hit to Russia's aviation assets.
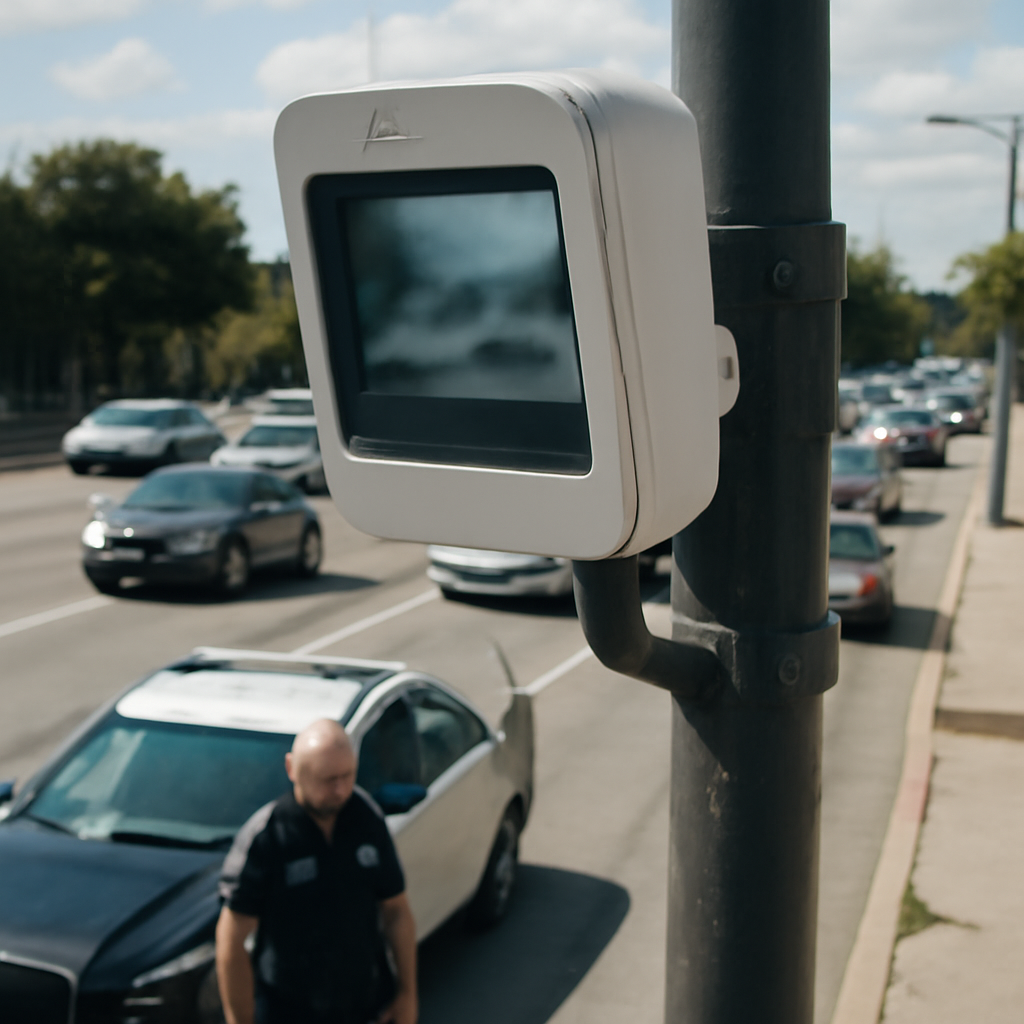
Flock Cameras Enable Surveillance of Vehicles Without License Plates
Flock Cameras are revolutionizing vehicle surveillance by enabling law enforcement to track vehicles even without license plates. With Flock's innovative Vehicle Fingerprint technology, officers can gather crucial details like decals, bumper stickers, and temporary state tags to build a case.
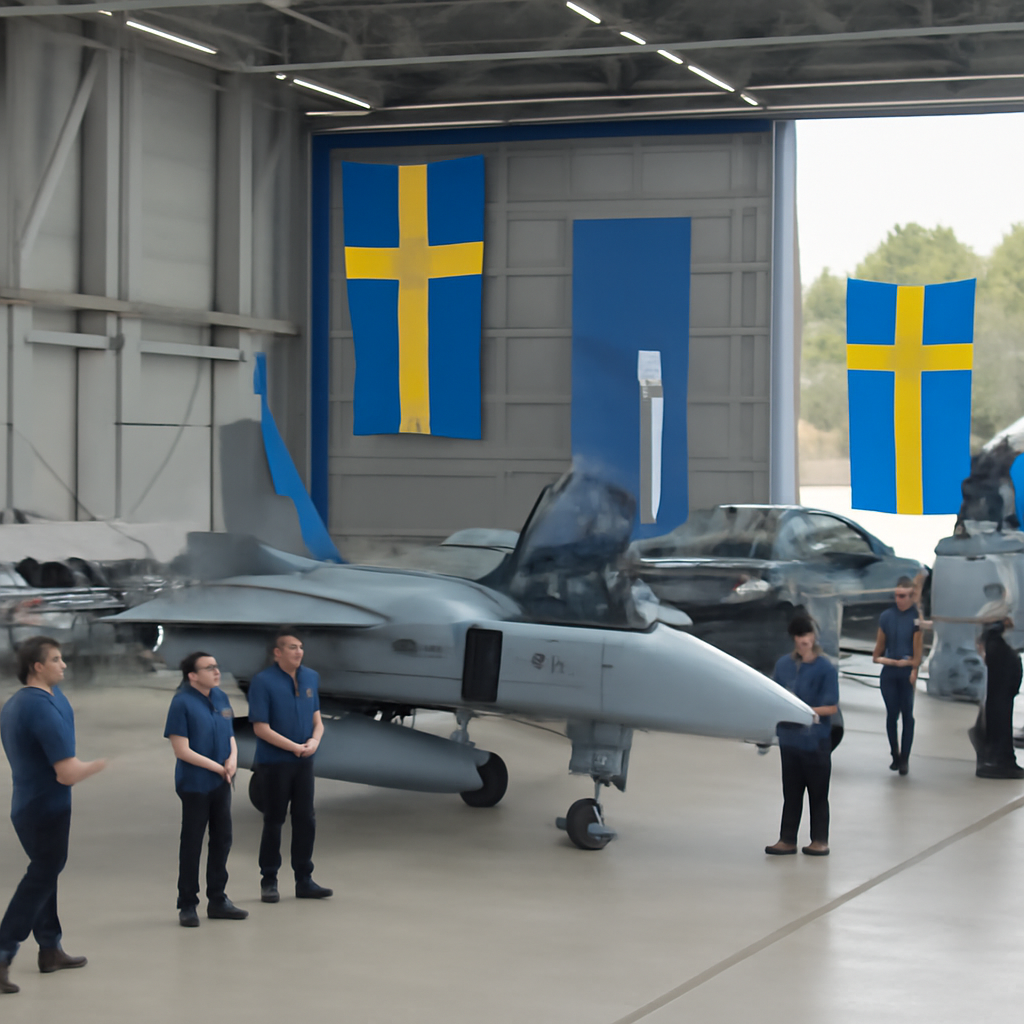
Ukraine Orders 16 Gripen E Fighters in $2.5 Billion Deal
Ukraine just scored a major win in its defense strategy with a $2.5 billion deal to acquire 16 cutting-edge Gripen E fighters, marking the country's first-ever order for brand-new aircraft. This game-changing contract also includes spare parts, technical support, and training, boosting Ukraine's air power to new heights.
US Celebrates 250th Anniversary Amid Heightened Security Concerns
Happy 250th birthday, America! This milestone anniversary is the perfect excuse to gather with friends and family, enjoy some fireworks, grab a cold one, and take in the aerial show - including an epic flyby that's sure to leave you in awe.
Vulnerabilities in FatFs Filesystem Expose Millions of Embedded Devices to Code Execution
Millions of embedded devices are at risk of code execution due to seven vulnerabilities in the widely-used FatFs filesystem, which can be easily exploited with physical access, effectively leading to a jailbreak. This set of flaws, ranging from medium to high severity, poses a significant threat to device security.
Linux Flaw Exposes Unprivileged Users to Root Access
A newly discovered Linux flaw, CVE-2026-46242, allows ordinary users to gain root access to a machine, and even Android devices are vulnerable. This alarming vulnerability, known as Bad Epoll, can be exploited with ease, but thankfully, a working fix is now available.
Avalon Malware Framework Targets Enterprise with CrownX Ransomware
Meet Avalon, a sneaky malware framework that's targeting enterprises with a potent ransomware punch, known as CrownX, and discover how it infiltrates systems through clever phishing tactics. This modular menace combines credential collection, lateral movement, and more into a single, reusable threat.
Google Disrupts NetNut Residential Proxy Network
Google's Threat Intelligence Group has disrupted NetNut, a massive residential proxy network controlling at least 2 million infected devices worldwide, including smart TVs and streaming boxes. This botnet, powered by trojanized apps and malicious software like Badbox 2.0, was used for cybercrime and espionage activities.
Australia's Defence Acquisition Shift Raises Stewardship Risks
The government's reform plan introduces a new, quasi-independent Defence Delivery Agency (DDA) tasked with not only delivering projects, but also taking charge of the long-term stewardship of Australia's sovereign defence industrial base. This bold move aims to ensure the nation's defence capabilities are secure and thriving for years to come.
Armored Likho Exposes BusySnake Stealer Campaign
Meet Armored Likho, a sneaky group behind the BusySnake Stealer Campaign, which has already compromised government agencies and power companies in Russia, Kazakhstan, and Brazil. Their clever tactics start with targeted spear-phishing emails, often disguised as harmless attachments like psychological tests or aid applications.
North Korea-Linked npm Packages Target Developers with Stealthy Data Theft
Malicious npm packages, linked to North Korean threat actors, are impersonating popular tools to trick developers into handing over sensitive data. These sneaky packages masquerade as legitimate polyfill tools, making them hard to spot during a quick review.
Armored Likho Exploits Global Targets with BusySnake Stealer
Meet Armored Likho, a sneaky threat actor who's been wreaking havoc globally, exploiting both private individuals and organizations, including government agencies and electric power sectors in Russia, Brazil, and Kazakhstan. With a blend of financially motivated attacks and targeted cyber espionage, Armored Likho is a force to be reckoned with.
AdaptHealth Breach Exposes Patient Data via Social Engineering Tactics
AdaptHealth recently fell victim to a data breach, where hackers used clever social engineering tactics to trick a third-party contractor into giving them access to sensitive patient information stored in the company's cloud environment. This alarming breach put a large volume of patient data at risk, prompting AdaptHealth to disclose the incident to the Securities and Exchange Commission.
ARToken Phishing Platform Exposes EvilTokens' Microsoft 365 Toolkit
Cisco Talos researchers have uncovered a sophisticated phishing platform, ARToken, that offers a Microsoft 365 toolkit and goes far beyond traditional credential-harvesting pages, exposing over 80 API endpoints. This phishing-as-a-service operation is a game-changer in the world of cyber threats.
Qilin Consolidates Lead in Ransomware Market
Qilin is tightening its grip on the ransomware market, emerging as a leading player after a recent wave of consolidation, with an estimated 16% share of the cybercriminal market. This surge in power is a result of its technically mature infrastructure and strategic positioning in the ransomware-as-a-service (RaaS) market.
Google and FBI dismantle 2-million device NetNut botnet
In a major win for cybersecurity, Google and the FBI have joined forces to dismantle the massive NetNut botnet, a network of 2 million devices used by cybercriminals and espionage groups to hide their malicious activities. This significant disruption is the latest in a series of efforts to take down tools used to conceal online threats.
Ransomware Gang Exploits Supply Chain Attacks in New Partnership
Ransomware gangs are now operating like businesses, forming partnerships to supercharge their attacks - and a new alliance between Vect and TeamPCP is a prime example, combining massive credential theft with devastating ransomware-as-a-service operations. This unprecedented pairing puts organizations directly in the crosshairs.
FBI and Google Disrupt NetNut Proxy Network Used by Cyber Threat Actors
In a major win for cybersecurity, the FBI and Google have joined forces to dismantle the notorious NetNut proxy network, a go-to tool for cyber threat actors. This disruption has significantly reduced the network's capacity, cutting the available pool of devices by millions.