Tag: emerging threats
8354 articles
RedWing Malware Targets Android Users with Bank Fraud as a Service
A new, ready-to-use bank-fraud tool called RedWing is being rented on Telegram, allowing even novice criminals to hijack Android users' phones and steal their banking information. This malicious kit is sold as a complete package, complete with step-by-step guides and how-to videos, making it alarmingly easy for scammers to get started.
KDDI Breach Exposes 12.2M Customer Emails
A massive data breach at KDDI Corporation has put 12.2 million customer emails and 7.6 million passwords at risk, all stemming from a single unpatched vulnerability in a third-party software system. This staggering incident highlights the importance of robust cybersecurity measures, even for seemingly secure systems.
Cloud Worm CAI Disrupts Rivals, Steals Secrets and Mines Crypto
Meet CAI, a malicious botnet that's disrupting rival operations, swiping sensitive secrets, and mining cryptocurrency - all while eliminating competing malware to maintain its grip on compromised targets. This centralized worm is a powerhouse of credential theft and cryptomining, making it a force to be reckoned with.
Tenda Routers Expose Admin Access via Hidden Backdoor
Tenda routers have a shocking security flaw: a hidden backdoor that can give attackers full control of your device, allowing them to hijack your admin access. This vulnerability, tracked as CVE-2026-11405, lets hackers easily bypass standard login security and take over your router.
GitHub Agentic Workflows Exposed to Data Leak Threat via Public Issues
GitHub's Agentic Workflows are vulnerable to a data leak threat, as researchers have demonstrated a clever technique called GitLost that tricks AI agents into spilling private content from secure repositories into public comments. All it takes is a simple public issue to launch the attack, with no stolen credentials or special access required.
Meta Disrupts Phishing Campaign Targeting Facebook Business Users
Watch out for phishing scams targeting Facebook Business users - red flags include broken graphics, suspicious links, and unsolicited emails promising exciting opportunities. Experts warn that cybercriminals are getting sneaky, using legitimate-looking emails and Messenger chatbots to trick victims into taking action.
Phishers Exploit Microsoft Device Code Flow to Hijack M365 Accounts
Cyber attackers have cleverly exploited Microsoft's device code login flow to hijack M365 accounts, using a sneaky collaboration-style lure to trick users into handing over session tokens without even needing to steal passwords. This clever tactic abuses the OAuth 2.0 Device Authorization Grant, designed for constrained devices, to bypass security measures like multifactor authentication.
China-Aligned Hackers Exploit Roundcube Servers at US, Canada Universities
China-aligned hackers are targeting universities in the US and Canada, exploiting vulnerable Roundcube webmail servers to gain access to sensitive physics and engineering departments with potential national security links. This latest campaign highlights the ongoing threat of email-based attacks and the need for robust server security.
Victims of Predatorgate Sue Spyware Maker for €8 Million
Eight individuals targeted in Greece's Predator spyware scandal are taking a stand, suing the spyware maker for €8 million in moral damages after their devices were hacked between 2020 and 2021. Led by lawyer Zacharias Kesses, the group is seeking justice and accountability for the victims of this massive digital breach.
Spain foils pro-Russian hacktivist's escape plan
Spain's National Police have thwarted a daring escape plan by a suspected pro-Russian hacktivist, exposing his secret communications with terrorist groups and freezing his cryptocurrency assets. The suspect, allegedly part of the notorious CyberArmy of Russia Reborn and Z-Pentest groups, was caught after a months-long investigation sparked by a tip from the FBI.
Pakistan Scrambles to Match India's Integrated Battle Groups
India takes a giant leap in military strategy with the launch of its first five Integrated Battle Groups, a game-changing formation that combines 5,000 troops into a single, powerhouse unit. This bold move has sparked a scramble in neighboring Pakistan to keep pace with its rival's innovative military might.
Watling Exposes Shifts in Global Power Rules
The global rules of power have changed, and recent strategic failures reveal a harsh truth: it's not technology that's the problem, but flawed decision-making. From intelligence missteps to misguided priorities, the consequences can be catastrophic, as seen in the US's unprepared response to Iran's retaliation.
US Army Websites Targeted in 404 Hijacking Campaign
The US Army has confirmed that two of its websites, oil.army.mil and ai2c.army.mil, were recently hijacked in a 404 error page defacement campaign, displaying politically charged messages that denigrated high-profile figures and promoted a separatist cause. The incident was discovered by independent researcher Ronald Lovelace and reported to US Army officials.
Poland to Mass-Produce Low-Cost Barracuda Cruise Missiles
Poland is set to start mass-producing the game-changing Barracuda cruise missiles, a precise, affordable, and electronic warfare-resistant defense system, in partnership with Anduril Industries. This breakthrough move comes after a memorandum was successfully converted into a production program, paving the way for thousands of missiles to bolster the Polish Armed Forces.
Writer AI Flaw Exposes Session Tokens Across Tenants
A critical flaw in Writer AI, dubbed WriteOut, could let an outsider hijack any account and take over an entire organization with just a single link - no login credentials required. This shocking vulnerability highlights the urgent need for robust security measures in AI-powered platforms.
China-Aligned Hackers Exploit Roundcube Flaws to Infiltrate Universities
China-aligned hackers have launched a sneaky attack on universities, exploiting two flaws in the popular Roundcube webmail client to steal credentials and gain persistent access. At least a few dozen universities are believed to be affected, with Proofpoint researchers confirming fewer than 10 intrusions so far.
FBI Traces Scattered Spider Hacker via Persistent Windows Device ID
In a brazen ransom email, the attackers boldly declared, "IMPORTANT: WE STOLE THE DATA, CONTACT UMMEDIATELY," leaving no doubt about their malicious intentions. The hackers infiltrated the retailer's network through a clever help-desk ploy, tricking staff into resetting passwords and gaining control of critical accounts.
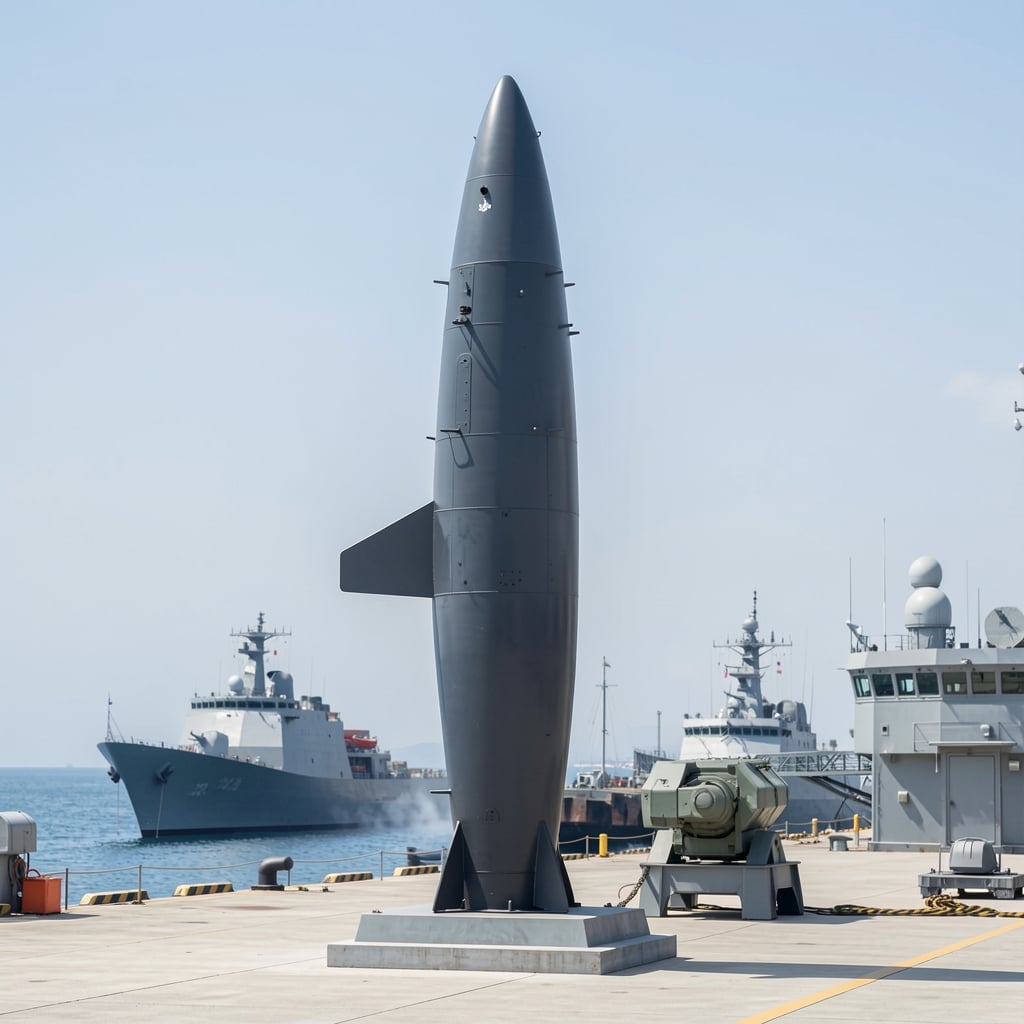
China Unveils JL-3 Submarine-Launched Ballistic Missile
China has just revealed its latest game-changer: the JL-3, or 'Giant Wave 3', a third-generation intercontinental-range submarine-launched ballistic missile that's set to take the country's military capabilities to new depths.
GitHub Actions Expose Vulnerability in CI/CD Pipelines
A single misstep in a GitHub Actions workflow can become a four-step chain to permanent credential exposure, putting your entire CI/CD pipeline at risk. Researchers have uncovered a class of vulnerabilities, dubbed Cordyceps, that can be exploited in a surprisingly simple way.
Google Sues Chinese Scammers Over Gemini AI Misuse
Google is taking a stand against scammers, suing a group called Outsider Enterprise that uses its Gemini AI feature to create fake websites and scam people through text messages. The group, which operates on Telegram, offers phishing-as-a-service, making it easy for non-tech-savvy scammers to target victims.
Scattered Spider Morphs into Decentralized Cybercrime Network
Meet Scattered Spider, a notorious cybercrime collective that's evolved into a decentralized network of independent clusters, sharing tactics and tools to wreak havoc online. This fresh analysis by Group-IB shatters the traditional view of a single, unified gang, revealing a more complex and dynamic threat.
Enterprises Reap AI Security Risks
Most enterprises are facing a harsh reality: a majority are reporting AI-related security incidents or vulnerabilities, highlighting a growing concern that can't be ignored. This stark statistic sets the tone for a crucial conversation about the intersection of AI and security.
AI Reshapes Software Supply Chain Security Risks
The software supply chain security landscape has dramatically shifted in just 20 months, with AI tools and models now integral to building, deploying, and running software - and bringing new risks to the table. The old question of "what's in your code?" has given way to a more complex concern: what happens when AI coding assistants and autonomous agents start suggesting or producing code?
Linux Flaw Enables VM Escape on Intel, AMD Devices
A newly disclosed 16-year-old Linux kernel vulnerability, dubbed Januscape, allows hackers to easily escape virtual machines and compromise their host systems - all with just a few clicks from within the guest system. This shocking security flaw, tracked as CVE-2026-53359, has been lurking in the kernel for nearly two decades.