Tag: emerging threats
8086 articles
Google Certificates Targeted in ccTLD Hijacks
Google thwarted a sneaky attack where hackers hijacked three country-code domains to obtain fake HTTPS certificates for several Google sites and other organizations, quickly blocking the unauthorized certificates through Chrome's emergency response system. The compromised domains included .gh, .sl, and .as, which were manipulated by attackers to gain DNS control.
Russia-Aligned UAC-0099 Refines MATCHBOIL Malware
The operators of UAC-0099, a group likely aligned with Russian interests, have been steadily refining their MATCHBOIL malware, making it a more potent tool for future attacks. This deliberate evolution shows a clear intent to evade detection and enhance the malware's flexibility.
Hacker Convicted for Stealing $53 Million from Uranium Crypto Exchange
Meet Jonathan Spalletta, a 36-year-old hacker who callously swiped $53 million from a decentralized crypto exchange, Uranium Finance, and now faces charges for computer fraud and money laundering. His alleged crimes not only shut down the platform but also showcased his apparent disdain for cryptocurrency, referring to it as "fake internet money".
Microsoft Bolsters Teams with Deepfake Detection Tools
Microsoft is stepping up its game to keep Teams meetings secure by integrating deepfake detection tools from trusted third-party providers, helping organizations spot synthetic audio and video. This new feature, set to roll out globally in November, will enable Teams to flag suspicious meeting content.
ASOS Breach Exposes Customer Data After Credential Theft
ASOS recently fell victim to a sneaky social engineering attack, where hackers tricked an employee into handing over their login credentials, allowing the attackers to access sensitive customer data stored on third-party platforms. The company quickly sprang into action, locking down the affected platforms to prevent further damage.
Wazza Phishkit Targets US, EU, Australia with Multi-Stage Routing
Meet Wazza Phishkit, a sophisticated threat that's targeting banking, manufacturing, and government organizations across the US, Europe, and Australia with a multi-stage routing chain designed to evade detection. This engineered delivery system uses a series of checks to route visitors to its final lure, making it a complex and formidable phishing threat.
UK, Germany Forge Cybersecurity Alliance to Counter Russian Threats
Britain and Germany are joining forces to tackle the growing threat of Russian cyberattacks, as Prime Minister Andy Burnham and Chancellor Friedrich Merz meet in Berlin to strengthen their countries' security partnership. The alliance aims to safeguard infrastructure, businesses, and democracies from the increasing danger of cyber sabotage.
Chinese Hacker Exploits AI in South Korean Bank Data Heist
Meet the new face of cybercrime: AI-powered hacking. A Chinese hacker recently used agentic AI tooling, alongside traditional tactics, to pull off a massive data heist at a South Korean bank.
Malicious Firefox Extensions Target Crypto Wallets, Exfiltrate Recovery Phrases
Beware of malicious Firefox extensions that masquerade as helpful tools but secretly steal your crypto wallet secrets, including recovery phrases and private keys, by intercepting them during wallet import flows. These sneaky add-ons can even fake legitimate wallet interfaces to trick you into handing over sensitive info.
Dark Web Kingpin Gets 40 Years for Facilitating $430 Million in Illegal Transactions
Meet Raheim Hamilton, aka Sydney and ZeroAngel, the dark web kingpin behind Empire Market, who just got 40 years for facilitating a whopping $430 million in shady deals. He and his partner made it easy for users to stay under the radar with cryptocurrency, encryption, and even a rating system for vendors who could best conceal their illicit goods.
Atlassian Vulnerability Exploited in Wild, Targeting Multiple Products
A critical Atlassian vulnerability, CVE-2026-21589, with a near-perfect CVSS score of 9.3, is being actively exploited in the wild, putting multiple products at risk. This flaw allows for arbitrary file access, posing a significant threat to users of eight Atlassian Data Center products.
FBI Warns of Ongoing FortiBleed Threat to Fortinet Devices
The FBI and US Secret Service have sounded the alarm: a whopping 86,644 Fortinet devices across 194 countries are compromised, and the FortiBleed threat is still very much active, leaving organizations at risk of being locked out of their own systems. This widespread campaign targets Fortinet FortiGate firewalls and SSL VPN gateways, putting businesses and individuals on high alert.
Europol, US GAO Warn of Looming Quantum Threat to Global Cryptography
The clock is ticking: Europol and the US GAO are sounding the alarm on the urgent need for post-quantum cryptography to safeguard global security, warning that proactive defence is crucial to protecting cryptocurrencies and more. Immediate action is needed across government and industry to address this looming threat.
DOJ Charges MonsterCloud Owner with Defrauding Ransomware Victims
Meet Zohar Pinhasi, the mastermind behind MonsterCloud, who's accused of pulling off a despicable scam that left ransomware victims paying twice - once to the hackers, and again to him for fake decryption services. By posing as a hero with secret tools, he allegedly re-victimized his clients and lined his pockets with a hefty profit.
Ransomware Hits Unprepared Small Business, Leads to Shutdown
A small construction company's confident dismissal of expert help - "you're too expensive" - turned to desperation when a ransomware attack crippled their operations, forcing a shutdown. Just weeks earlier, they'd rejected a proposal from a cybersecurity consultant that could have prevented the disaster.
US Offers $10 Million Bounty for HAFNIUM Hacking Suspect
The US government is putting out a $10 million reward for information that leads to the identification or capture of Zhang Yu, a Chinese national accused of being involved in the notorious 2021 Microsoft Exchange Server attacks as part of the HAFNIUM hacking group. This move sends a strong message to others who help hide China's cyber operations: they could be next.
Malware Worm Exploits Tensorlake npm Package to Steal Credentials
A malware worm has been discovered exploiting the popular Tensorlake npm package to steal sensitive credentials, with the first malicious commit occurring on October 7, 2026, at 01:20 a.m. UTC. The compromised package, version 0.5.144, was quickly taken down after publishing to the npm registry on October 8, 2026.
Samsung Galaxy S26 Exploited Three Times at Pwn2Own Ireland
The Samsung Galaxy S26 proved to be a vulnerable target at Pwn2Own Ireland, falling to three separate zero-day exploits on day two of the competition, with security researchers scoring big with their discoveries. Each successful hack earned them a hefty payday, with a total of $232,500 in cash awards doled out that day.
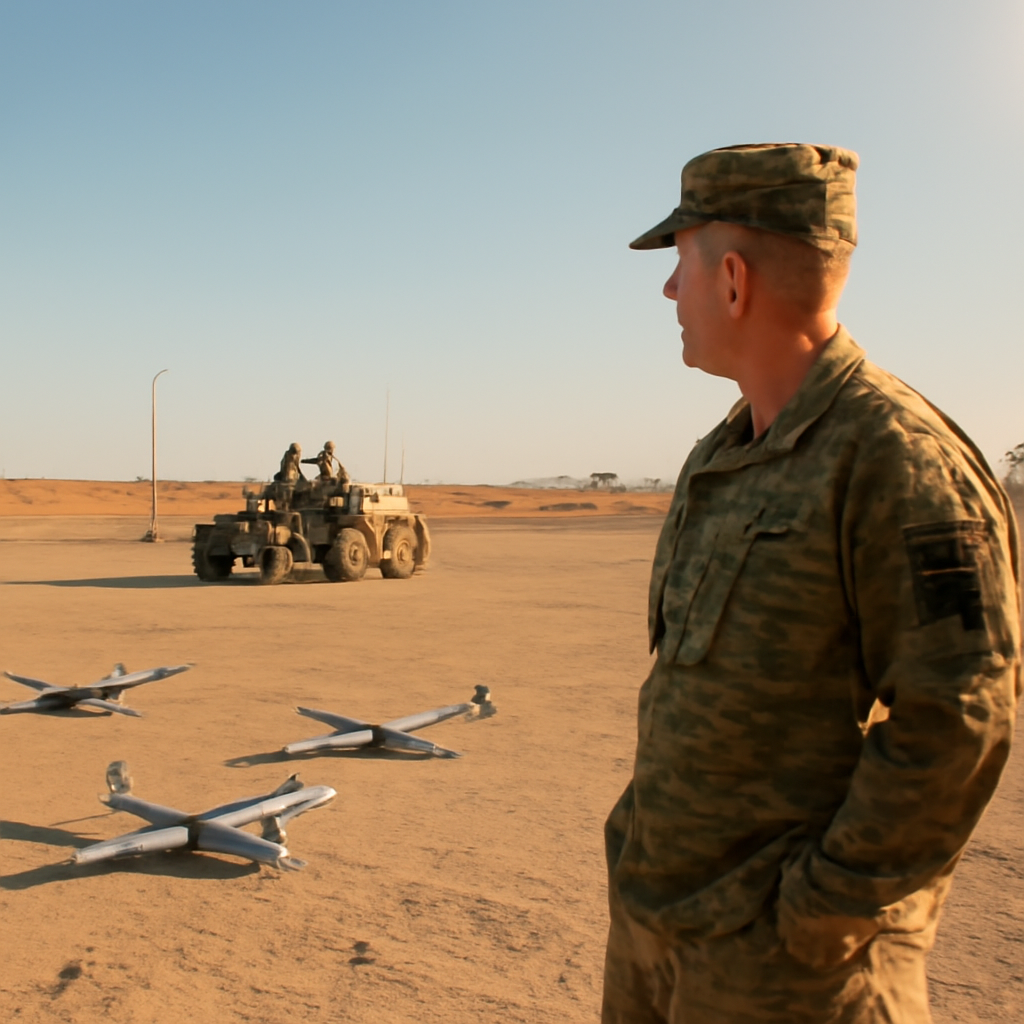
US Military to Test Counter-Drone Tech in Urban Warfare Exercise
The US military is rethinking its approach to homeland defense, recognizing that protection from threats isn't just about what's outside, but also what's inside - and that includes countering the growing menace of drones. In a recent exercise at Yuma Proving Ground, military officials tested cutting-edge counter-drone tech in a simulated urban warfare scenario.
Pentagon Exposes Lagging Investment in Hardened Aircraft Shelters
The sudden departure of B-1 bombers from RAF Fairford in the UK was no coincidence - US President Donald Trump revealed that credible threats had prompted their removal, narrowly averting a potential attack on the base. The bombers had been stationed at the forward bomber hub since March, supporting operations against Iran.
Putin's Legacy Exposes Russia's Authoritarian Entrenchment
In Russia, freedom and despotism have a vicious cycle: live long enough, and you may see freedom's dawn, only to be plunged back into darkness. This unsettling pattern is a stark reality under Putin's rule, where authoritarianism has taken hold.
Pentagon Bolsters Counter-UAS Arsenal with Layered Defenses
The Pentagon is supercharging its drone defense capabilities with a multi-layered approach, led by Brig. Gen. Matthew Ross, to stay ahead of evolving threats. This cutting-edge strategy combines new sensors, effectors, and innovative thinking to protect what matters most.
FBI Disrupts Deepfake CSAM Market with Website Seizures
The FBI has taken a major step in the fight against child exploitation by seizing two websites, NudeLeaksTeens and NLTVIDS, that were selling and distributing shocking content. These sites were offering horrific collections of child sexual exploitation material, including a 189GB collection of 315 girls' images and videos for just $64.90.
Expertise Erodes as Self-Styled Analysts Flood Online Debate
The rise of self-proclaimed analysts on platforms like X, YouTube, and Substack has made expertise a rare commodity, diluting the value of informed opinion in online debates. When everyone claims to be an expert, true authority gets lost in the noise.