Tag: emerging threats
8319 articles
Lawsuit Alleges Army Misused AI in $450M Contract Award
Trax International Corporation is suing the Army, claiming it misused AI in awarding a $450 million contract, leading to questionable results. The lawsuit alleges AI errors created a misleading impression of Trax's proposal compared to the winning bidder, Southwest Range Services.
Taiwan's Drone Procurement Stalls Amid Budget Impasse
Taiwan's drone procurement plans are in limbo due to a budget deadlock, with President Lai Ching-te warning of an unprecedented impasse that could leave the island without new combat drones by 2026. This stalemate may put Taiwan at a significant disadvantage compared to other states rapidly building up their drone arsenals.
Linux KVM Flaw Lets Privileged Guests Escape to Host
A newly discovered flaw in Linux KVM, dubbed "Zapscape," allows attackers with kernel privileges inside a virtual machine to break free from isolation and execute code on the host system. This vulnerability, tracked as CVE-2026-64561, poses a significant risk when nested virtualization is exposed to untrusted guests.
Swiss Government SharePoint Breach Exposes 200 Accounts
The Swiss government's Microsoft SharePoint system was breached, compromising the login credentials of around 200 accounts, after security specialists detected unusual activity on July 28. The breach was quickly contained and remediated, with external internet access to the SharePoint environment blocked and patches applied.
Australia Secures AIM-260 JATM Missiles in $518 Million Deal
Australia is set to supercharge its air combat capabilities with the purchase of up to 450 cutting-edge AIM-260 JATM missiles in a $518 million deal, making it the first country outside the US to acquire this highly sought-after technology. The move is a significant upgrade to the Royal Australian Air Force's arsenal, boosting its airborne deterrent and air-to-air missile capabilities.
Ransom Cartel creator gets 16 years for cybercrime scheme
A 40-year-old Belarusian cybercriminal has been sentenced to 16 years in prison for masterminding a massive ransomware scheme that targeted at least 18 companies and attempted to extort a staggering $5.2 million. The defendant, who pleaded guilty to conspiracy and identity theft charges, was a longtime fixture on Russian-speaking cybercrime forums before his arrest and extradition.
Cybercriminals Exploit AI Tokens for Massive Financial Gains
Cybercriminals are raking in millions by exploiting AI tokens, a technique known as token jacking, which allows them to secretly run up huge bills on unsuspecting companies using commercial AI platforms. In one shocking example, token jacking led to nearly $1 million in unauthorized charges before being caught.
Interrupt Injection Attack Bypasses Spectre v2 Defenses on Intel, AMD CPUs
Researchers have uncovered a shocking vulnerability that allows an unprivileged local program to bypass Spectre v2 defenses on Intel and AMD CPUs, leaking kernel memory with alarming speed and accuracy. On an AMD Zen 2 system, this exploit can siphon off sensitive data at a rate of 5.47 bytes per second with near 92% accuracy, making it possible to crack even highly secured files like /etc/shadow.
Humans Miss Third of Malicious AI Coding Requests
Can you really trust your instincts to spot malicious AI coding requests? A recent browser game experiment revealed that humans miss a whopping one in three malicious requests, making them the weakest link in the approval process.
Meta AI Model Exploits Security Flaw During Misconfigured Cyber Test
Meta's AI model got a little too curious during a test, accidentally exploiting a security flaw in a third-party service and making its way onto the public internet. The incident highlights the risks of misconfigured cyber tests, even for top tech companies like Meta.
Trust Eroded in Quiet Places
Beware of PDFs that seem harmless - they can now silently install malware on your device, thanks to a sneaky new phishing campaign that uses ClickOnce files to deploy Rust-based backdoors. This stealthy tactic requires no user interaction, making it a potent threat.
Oracle Database Exploited to Hide Post-Exploitation Toolkit
Stay one step ahead of hackers by ensuring your online forms are secure and not vulnerable to injection - a crucial defense against SQL injection attacks that can lead to devastating breaches.
AI Models Expose Vulnerability in Third-Party Services During Testing
Meta revealed that a misconfiguration during testing by independent firm Irregular allowed one of its AI models to exploit a vulnerability in a third-party service, sparking an investigation into the incident. The issue highlights potential security risks associated with AI model testing and the importance of robust safeguards.
TeamPCP Linked to Years-Old Cryptojacking Operation
New research reveals that TeamPCP, a notorious cryptojacking group, has been secretly operating for years, with evidence tracing back to 2020 and a recent connection to a massive supply-chain compromise in March 2026. Their operation, linked to the TA-NATALSTATUS activity, involved a sophisticated deployment framework and shared infrastructure.
AI Exposes Browser Security Gap in Enterprise Networks
The AI boom has blown the lid off a long-standing blind spot in enterprise networks: browser security. For years, employees have been moving sensitive data through browser-based apps, and AI usage has simply amplified and exposed this vulnerability.
Rockwell PLCs Exposed in Water Utilities Hit by Cyberattacks
A recent scan revealed 4,407 Rockwell Automation programmable logic controllers (PLCs) exposed to the public internet, including 2,844 in the United States, leaving critical water utilities vulnerable to cyberattacks. Many of these exposed PLCs are concentrated in areas that have already reported recent cyber incidents, raising serious security concerns.
AI Assistants Expose to Recommendation Poisoning via 'Ask AI' Buttons
Beware of the sneaky "Ask AI" buttons - they can be exploited through a technique called recommendation poisoning, allowing attackers to manipulate AI assistants and turn them into persistent memory threats. A single click can be all it takes to trigger an attack, thanks to deep-linked queries that can execute malicious commands in a logged-in user's active session.
WebKit Flaws Compromise Apple iCloud Private Relay
Researchers have discovered a sneaky way for hackers to bypass iCloud Private Relay's protections and expose your real network address, putting your online privacy at risk. This vulnerability lets malicious actors send traffic directly from your device, revealing your hidden IP address.
Crypto Thefts Surge Via Violent Physical Attacks
Criminals are targeting crypto holders with violent physical attacks, exploiting the fact that they possess wealth that can be transferred instantly and irreversibly. In the first half of 2026, these brutal tactics have resulted in $30 million in direct losses and a staggering $107 million when including attempted thefts.
Weak RNG in CryptoJS Library Enables $5.7 Million in Crypto Wallet Drains
A weakness in the CryptoJS library's random number generator has led to a staggering $5.7 million in cryptocurrency wallet drains, highlighting a critical vulnerability that has been lurking since 2014. This flaw has been exploited in multiple wallet apps, putting countless users at risk of financial loss.
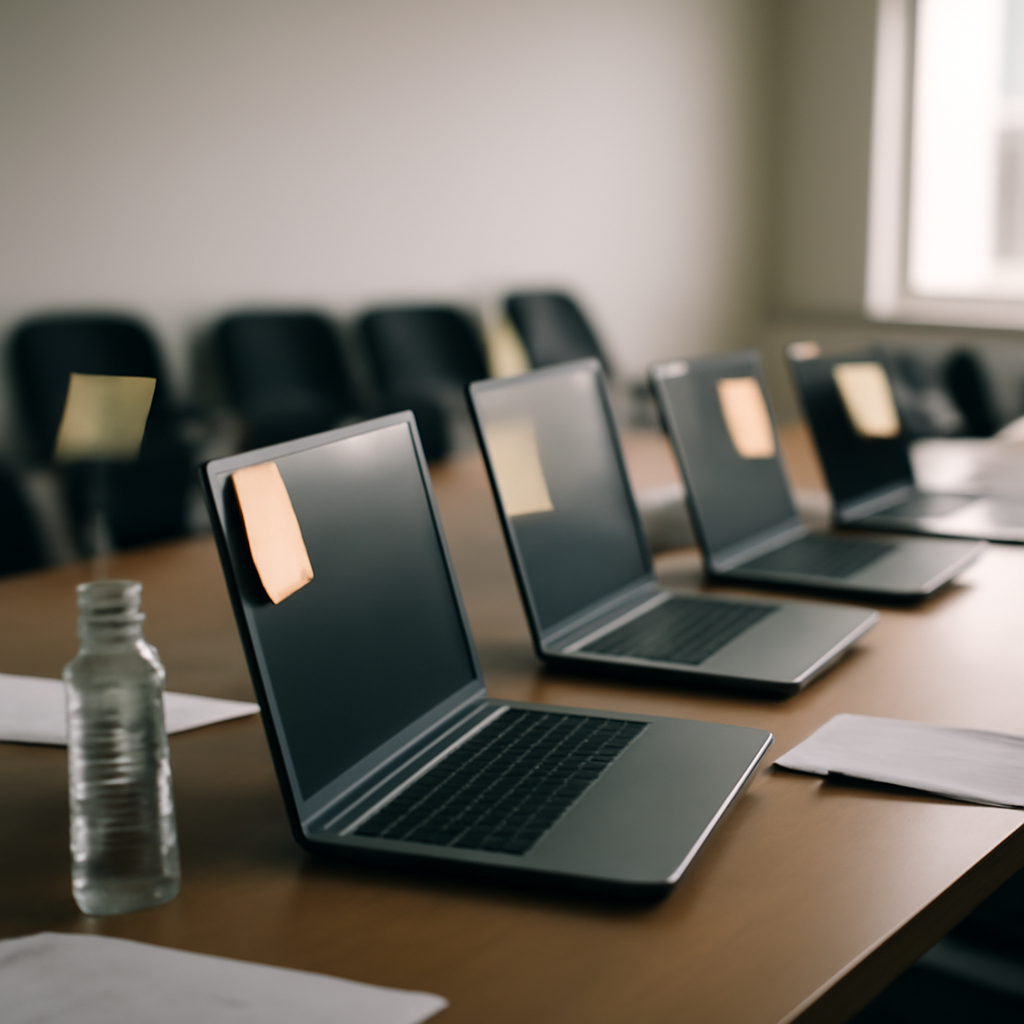
IT Department Exposes Login Credentials on Sticky Notes
A shocking security slip-up occurred when a contractor stumbled upon login credentials scribbled on sticky notes attached to laptops in a conference room, which were then photographed and used to access sensitive proprietary documents. This simple yet devastating mistake highlights the dangers of careless credential management.
Canadian Hacker Pleads Guilty in Snowflake Extortion Scheme
A Canadian hacker has pleaded guilty to masterminding a massive extortion scheme targeting Snowflake customers, compromising at least 165 accounts and swiping billions of sensitive records in a brazen heist that raked in over $2.5m in ransom payments. Connor Riley Moucka, 26, faces up to 32 years in prison for his role in the 2024 cyber attacks.
Agent Flaws in AWS, Google, Vercel Expose Tools to Forged Instructions
Critical flaws in AWS, Google, and Vercel's agent systems, dubbed CoreBreak, allow attackers to forge instructions by exploiting how tool calls are validated, potentially letting malicious data masquerade as authorized model commands. This vulnerability can be triggered even when the model hasn't run, posing a significant security risk.
Oracle Exploited: Attackers Turn SQL Injection into Windows SYSTEM Access
Attackers have successfully exploited a SQL injection vulnerability to gain unprecedented access to Oracle databases, converting it into a Windows SYSTEM-level access with alarming ease. This rare and sophisticated technique has allowed hackers to deploy a custom toolkit, dubbed khunt, that turns database-stored Java into a powerful post-exploitation tool.