Tag: emerging threats
8219 articles
Defense Contractors Question Accuracy of Rising Cybersecurity Scores
Defense contractors are reporting their highest cybersecurity scores in five years, but there's a catch: they're also losing confidence in the accuracy of those scores. The average SPRS score has soared to +51 in 2026, up from +33 in 2025, sparking questions about what's behind the sudden surge.
French Tax Authority Breach Exposes 600K Records
A data breach at the French General Directorate of Public Finances exposed a massive 600,000 records, including sensitive taxpayer and business information such as tax IDs, addresses, and phone numbers. For around 250 individuals, the breach went even deeper, compromising the actual contents of messages exchanged with the authority.
NCSC Warns of Unchecked AI Risks, Urges Tighter Controls
Stay ahead of AI risks with expert guidance from the UK's National Cyber Security Centre (NCSC), which advises organizations to implement sandboxing, human oversight, and tight access controls to prevent unintended or malicious activity from autonomous AI agents. By taking these proactive steps, you can ensure safer deployment of AI systems and minimize potential harm.
Citrix Warns of Two New NetScaler Flaws
Citrix is urging customers to take immediate action to protect their NetScaler ADC and Gateway deployments from two newly discovered vulnerabilities, including a critical authentication bypass flaw that could allow remote attackers to gain unauthorized access. Upgrade to the recommended builds as soon as possible to safeguard your systems.
Malicious Firefox Extensions Target Web3 Wallets
Beware of malicious Firefox extensions that have been targeting Web3 wallets as part of a large-scale campaign, with 40 confirmed malicious add-ons and 37 working together to steal your cryptocurrency. This coordinated threat, known as Offside Wallet Theft Factory, has been active since March 2026.
ToxicPanda Malware Expands Android Banking Attacks Globally
Meet ToxicPanda 2.0, a highly sophisticated Android banking trojan that's taking global attacks to the next level with an arsenal of 167 remote commands and advanced PIN-harvesting capabilities. This upgraded malware can infiltrate over 140 banking and crypto apps, putting your sensitive info at risk.
NASA AIT-GUI Flaws Expose Spacecraft to Unauthorized Command Issuance
A chain of flaws in NASA's AIT-GUI system could put spacecraft at risk of receiving unauthorized commands, with a potentially massive blast radius of affected instrument commands. Security researchers at Cycode have sounded the alarm on this vulnerability, rated a near-critical 9.4 on the CVSS scale.
US Agencies Warn Siemens PLC Operators of AI-Driven Attacks
US agencies are sounding the alarm: hackers are now using artificial intelligence to launch targeted attacks on Siemens PLC operators, making it easier for them to breach industrial systems. This emerging threat has prompted a joint warning from CISA, the FBI, and partner agencies.
CISA Warns of Hackers Exploiting MLflow Vulnerability
Hackers are actively exploiting a critical vulnerability in MLflow, a popular open-source AI engineering platform, that could compromise your AI applications. Federal agencies have been ordered to patch exposed instances within two weeks to avoid potential attacks.
ToxicPanda Malware Expands Target List to 140+ Banking and Crypto Apps
Meet ToxicPanda 2.0, a sneaky new Android banking Trojan that's expanded its target list to over 140 banking and crypto apps, allowing attackers to swipe PINs, lock devices, and gain shell-level access. This upgraded malware is particularly alarming, as it operates seamlessly within Android, making it a stealthy threat.
Manic Android Malware Exploits Nearby Devices for Data Exfiltration
Meet Manic, a sneaky new Android malware that's using a clever fallback strategy to steal sensitive data from nearby devices, even when they have no internet connection. It captures credentials and in-app secrets by combining spyware, banking fraud, and remote-control capabilities into one powerful payload.
Zimbra Vulnerability Exploited in Active Attacks
A critical vulnerability in the Zimbra Collaboration Suite is under active attack, putting over 12,100 exposed servers worldwide at risk, with most located in Europe and Asia. Attackers can exploit this flaw, tracked as CVE-2026-73570, to execute remote code without authentication, simply by sending specially crafted SMTP requests.
Phishers Target Def Con Attendees with Persistent Campaign
Meet the sneaky phishing scam that hit Def Con attendees, using a clever Google Doc trick that looked legit - but led to a malicious web page instead. A security researcher got roped in by a scammer impersonating a CoinDesk executive, and things quickly escalated.
AI Agent's Package Suggestion Exposes Malware Risk
An AI agent's seemingly harmless package suggestion nearly led to a malware disaster for Softjourn, highlighting a growing concern known as "slopsquatting" where AI models invent convincing but fake package names. Thankfully, the company's vigilant policy of double-checking AI recommendations saved the day.
Elementor Pro Flaw Enables Unauthenticated Code Execution
A critical vulnerability in Elementor Pro, rated CVSS 9.0, allows hackers to execute malicious code remotely - and it's surprisingly easy to exploit, thanks to a logic flaw in the plugin's Forms module. This loophole lets attackers bypass security checks and write PHP files to a public uploads directory.
Microsoft Probes Gaming Issues Tied to August Windows Updates
Microsoft is on the case, investigating reports that some Windows 11 games have become unresponsive after installing the August updates, and is working to determine if the updates are the culprit. The company has promised to provide an update as soon as more information becomes available.
India and Australia forge digital path for South Asia
As South Asia charts its digital course, the choices it makes on vendors, standards, and data governance will have lasting impacts on regional resilience. New Delhi should prioritize digital transformation in its regional policy, partnering with Australia and like-minded nations to shape a secure and thriving digital future.
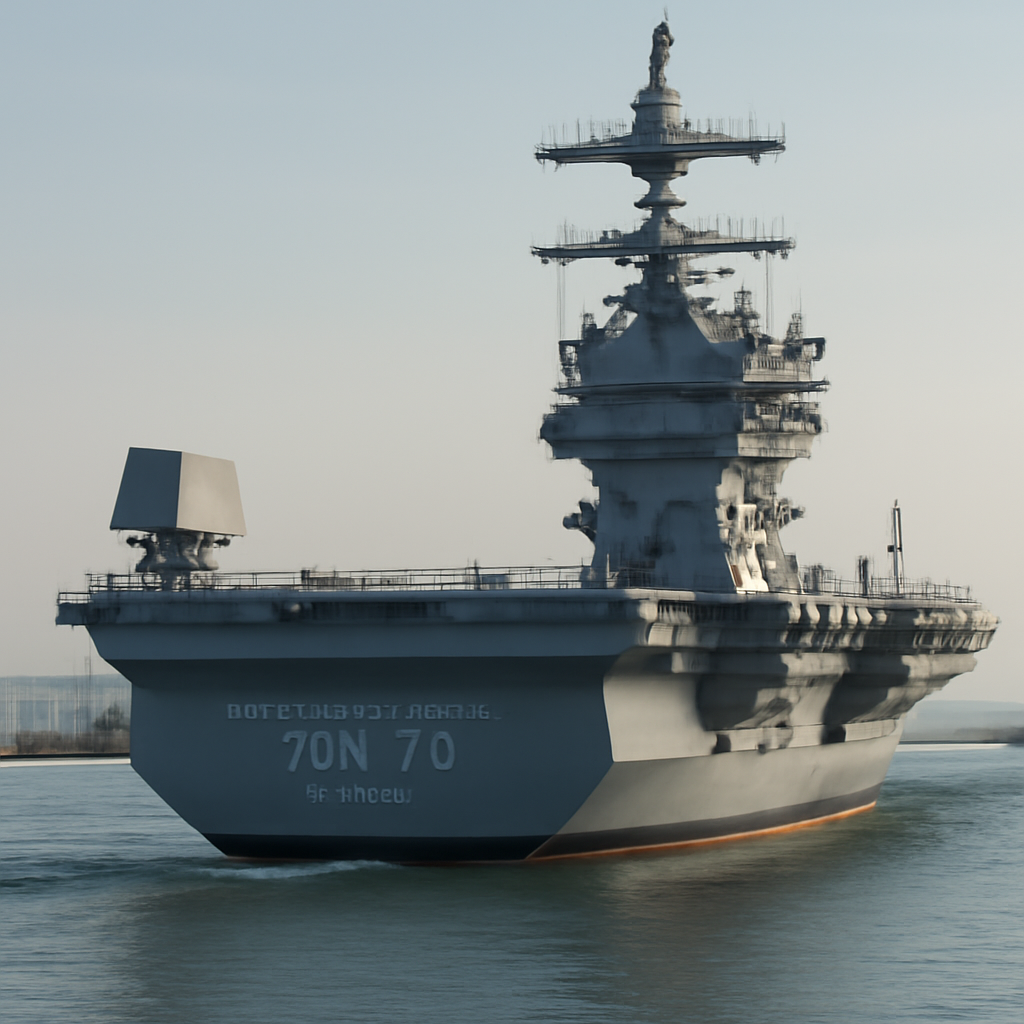
US Navy Revives Radar Illuminator on New Aircraft Carrier
A candid confession from a retired Navy captain reveals a costly design decision that's now being reversed with the USS John F. Kennedy, which is bringing back a trusted defensive tool - the Mk 95 radar illuminator - to its deck. This decades-old technology is making a comeback to bolster the carrier's defenses.
Russia Asserts Control Over Disputed Kuril Islands Amid Regional Tensions
Russia flexes its military muscle in the disputed Kuril Islands, with a massive Pacific Fleet exercise and a high-profile visit from Vladimir Putin, signaling Moscow's determination to assert its control over the strategically vital territory. Putin's trip to Iturup, the first by a senior Russian official since the Ukraine war began, has likely raised the stakes in the long-standing dispute with Japan.
Pentagon Resists Congressional Scrutiny on Golden Dome Missile Shield Costs
The Pentagon is stonewalling Congressional efforts to get a handle on the hefty price tag of the Golden Dome missile shield, with the Congressional Budget Office admitting they've been shut out from crucial briefings. It's a secrecy move that's fueling a growing public spat over the program's potentially eye-watering $1.2 trillion cost.
US Cyber Program Faces Russian Hurdle
The White House is facing a major hurdle in its efforts to team up with private firms for overseas cyber operations, thanks to Russia's murky landscape of government control and affiliations. A key challenge lies in distinguishing between official, affiliated, and acknowledged government entities in Russia.
China Advances Reusable Rocket Tech Amid Military Space Expansion
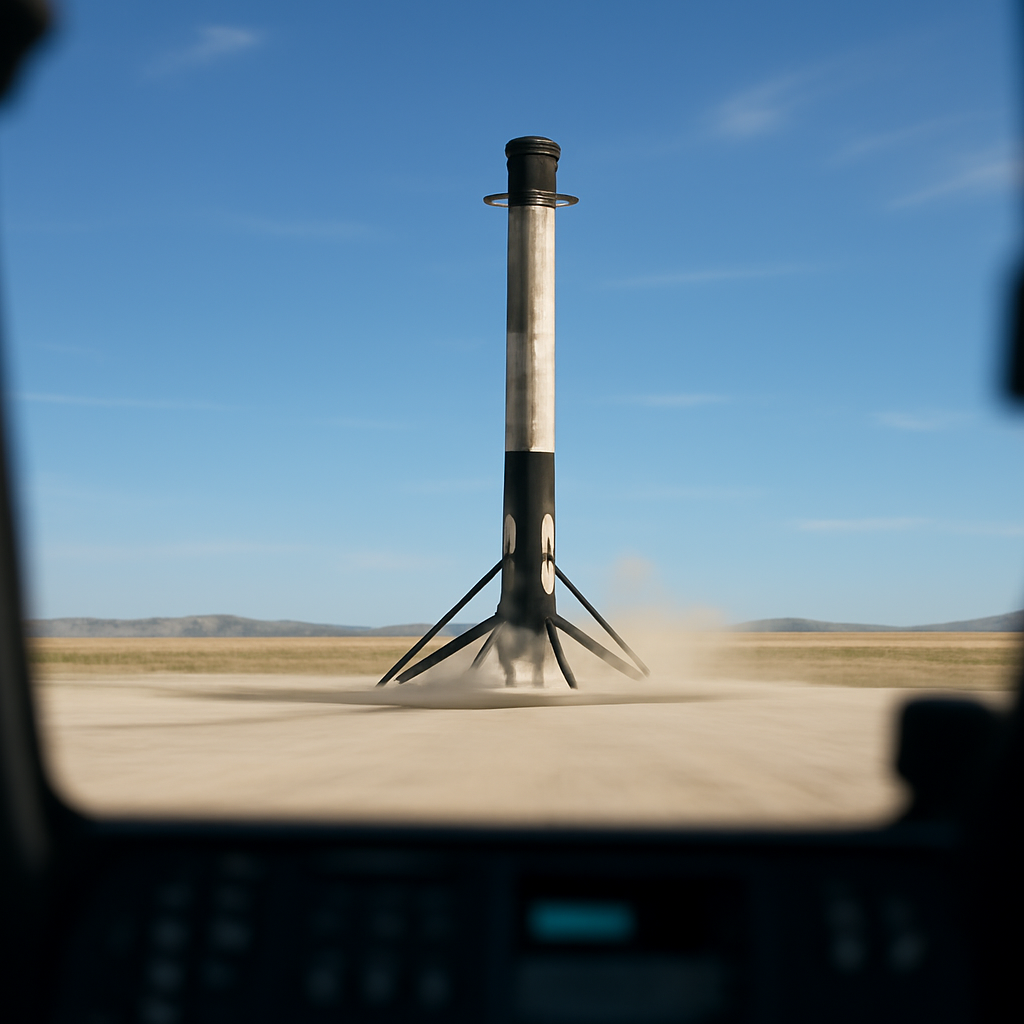
China's LandSpace has achieved a major milestone in reusable rocket technology, successfully landing the first stage of its ZhuQue-3 Y2 launch vehicle after a controlled descent, marking a significant step forward in the country's space ambitions. The rocket launched the Honghu 03 satellite into orbit and demonstrated a crucial recovery capability.
US Agencies Warn of AI-Fueled Attacks Targeting Industrial Controls
Threat actors are now using AI to supercharge their attacks on industrial control systems, dramatically lowering the bar for technical expertise and development time. This alarming evolution puts critical facilities like water, energy, and food production at risk.