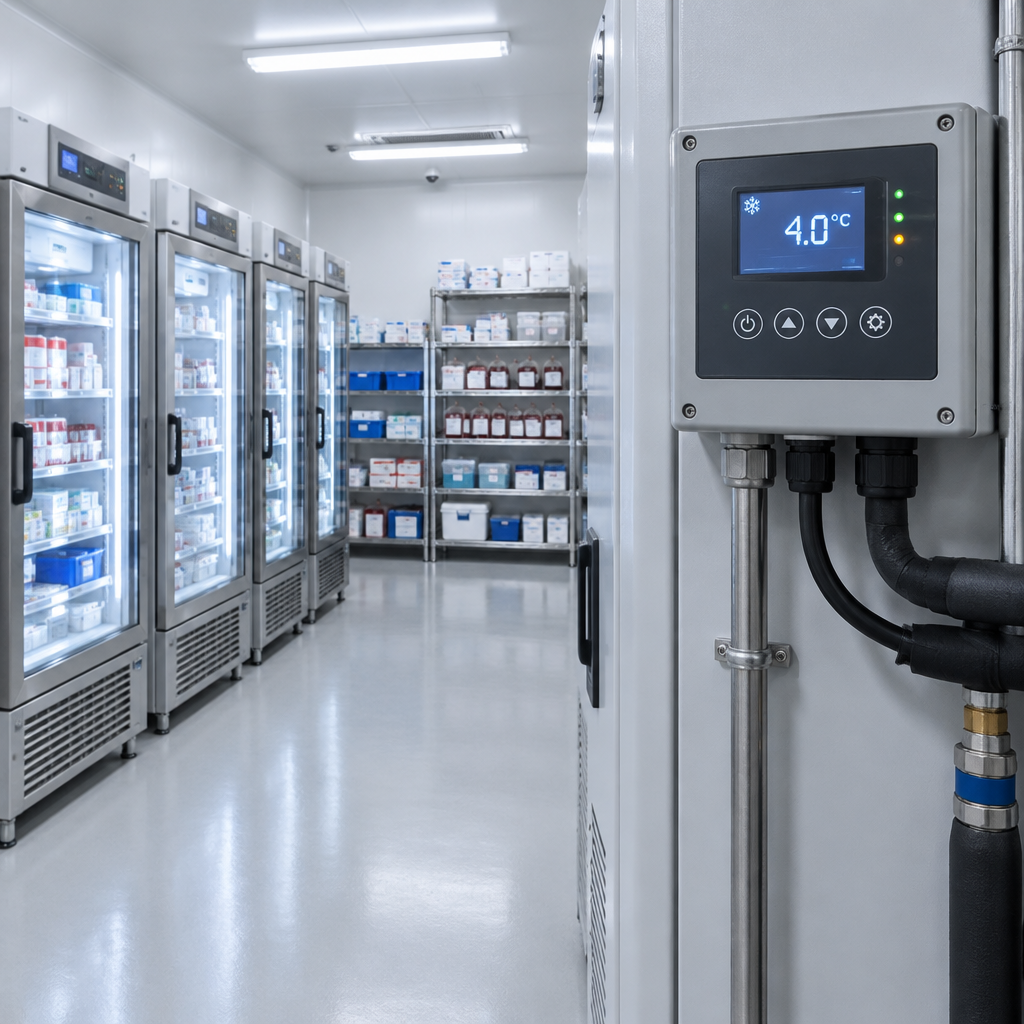
"The Danfoss controller attacks put a big ‘look here’ sign for malicious hackers onto the refrigeration units; no surprise there are now follow-on copycat attacks that are expanding from the initial attacks," says John Gallagher, Vice President at Viakoo.
European retailers and the Danfoss controller attacks
Last month more than 700 French supermarkets were reported affected by cyberattacks against refrigeration systems, causing food spoilage and in some instances, fires. On November 3, Reuters reported a similar cyberattack spreading across Europe and impacting several retailers on the continent. The outlets listed by Reuters include Ahold Delhaize, Carrefour, Colruyt Group, Coop, De Laet & Van Haver, Edeka, ICA, and Musgrave.
Gallagher framed the pattern as a classic copycat expansion from a specific vulnerability — in this case, controllers made by Danfoss — that has put refrigeration units in the crosshairs. The immediate operational impact for retailers has been lost stock and safety incidents; the longer-term impact, experts warn, is a new class of operational technology (OT) targets for adversaries who can reach equipment remotely.
France's national blood service and the 110°C command
In a striking escalation, a refrigeration attack in France hit the country’s national blood service. Reports confirm hackers raised temperatures in three cold stores holding vital blood products. Thomas Plank, CEO and Co‑Founder of Tributech, described the alarming specifics: “The worrying part isn’t that attackers reached a freezer. It’s that a freezer holding plasma accepted an instruction to heat itself to 110°C. No legitimate operator would ever send that command, so it should have been rejected regardless of who sent it or which system it came through.”
Plank further said this attack reportedly came through a refrigeration service provider, not the blood service itself, highlighting a supply‑chain blind spot: third parties with remote access to physical equipment and devices that trust whatever arrives on that channel.

Nobody's watching your logs at 2 AM.
Full SOC coverage without building one. Nubivance deploys and manages Rapid7 InsightIDR and MDR for organizations that need detection and response, not another dashboard.
Get coverageU.S. military refrigeration malfunctions under investigation
Separately, the New York Times has suggested a link between the recent European activity and a series of refrigeration malfunctions that occurred during the summer across U.S. military facilities. Officials are now investigating whether those malfunctions were part of an offensive cyber operation. The reporting raises the possibility that similar remote‑access techniques are affecting not only commercial cold chains and healthcare supply but also government and defense facilities.
Security experts' prescriptions: beyond patching
Several security leaders quoted in the reporting rejected a patch‑only mentality. Robert Costello, Chief Digital and Information Officer at Merlin Group, warned, “These attacks continue to highlight the fragility of control systems. As the manufacturer highlights, sometimes software updates cannot completely resolve these issues, and the hardware in these systems must be replaced with more modern technologies.” Costello added that zero‑trust principles can help but often require a full rebuild of long‑lived OT environments.
Louis Eichenbaum, Federal CTO at ColorTokens, framed the risk in sweeping terms: “These attacks demonstrate just how effective a cyberterrorism campaign could be. Our adversaries are increasingly targeting the foundational elements of human life: water, electricity, and now our food supply.” He urged organizations to move security beyond intrusion prevention toward mission continuity, listing concrete measures: identify exposed assets, eliminate unnecessary internet access, enforce strong authentication, implement microsegmentation, maintain comprehensive asset visibility, deploy zero‑trust access controls, enable continuous monitoring, and have tested recovery procedures. “Ultimately,” he said, “our adversaries don’t need to steal data to cause harm. They only need to disrupt the systems that sustain our daily lives.”
Gallagher offered immediate operational steps: put any internet‑facing consoles behind firewalls, turn off remote access controls, update firmware, rotate passwords, decommission end‑of‑life systems, and segment networks so remaining systems’ access can be controlled.
What this means for technologists and security teams, retailers and service providers, and blood banks and military facilities
- Technologists and security teams: Experts in the story recommend identifying exposed assets, eliminating unnecessary internet access, enforcing strong authentication, implementing microsegmentation, and maintaining continuous monitoring and tested recovery procedures to keep essential services operating during an attack.
- Retailers and refrigeration service providers: The incidents highlight a third‑party remote‑access blind spot. Gallagher’s checklist — firewalls, disabling remote controls, firmware updates, password rotation, decommissioning end‑of‑life gear, and network segmentation — maps directly to immediate operational mitigation steps retailers and their vendors can take.
- Blood banks and military facilities: The confirmed heating of plasma stores to 110°C and the ongoing investigations into U.S. military refrigeration malfunctions underline acute risks to life‑critical supplies and to mission readiness. Plank’s observation that the attack came through a service provider emphasizes the need to secure supply‑chain access channels and to ensure equipment rejects anomalous commands.
Experts quoted in the reporting worry this pattern could be reconnaissance or testing ahead of larger operations. As Louis Eichenbaum put it, “My greatest concern is that we may be witnessing adversaries testing our defenses ahead of something much larger.” The common thread across retailers, healthcare providers, and government facilities is the same: legacy controllers, trusted remote channels, and internet exposure create exploitable opportunities — and the defenses being urged require coordinated, often costly changes to hardware, architecture, and operational practice.
Read the original reporting: https://www.securitymagazine.com/articles/102721-fridge-cyberattacks-now-targeting-blood-banks-us-military-bases