[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Beware of malicious AI plugins on the JetBrains Marketplace that masquerade as helpful coding assistants but secretly steal your AI API keys. Over 70,000 installations have been recorded from at least 15 compromised plugins that have surprisingly evaded the marketplace's security checks.
A massive software supply chain attack just hit Mastra, with over 140 malicious packages published in a single day by a compromised npm account. The swift and coordinated assault, dubbed easy-day-js, unfolded over just two days, catching defenders scrambling to respond.
Microsoft is racing against the clock to fix a critical vulnerability in Defender, known as RoguePlanet, after a proof-of-concept exploit was released, allowing hackers to elevate privileges regardless of real-time protection settings. A patch is in the works, but no release date has been given.

Kodak recently suffered a data breach at the hands of hackers known as ShinyHunters, who gained temporary access to sensitive company data. The company has launched a swift investigation with external cybersecurity experts and is working closely with law enforcement to mitigate the impact.
A critical Joomla flaw, tracked as CVE-2026-48907, is being actively exploited, allowing attackers to upload and execute PHP code - and the US Cybersecurity and Infrastructure Security Agency (CISA) is warning users to take immediate action. A patch is available in version 2.9.99.5 of the Widget Factory Joomla Content Editor.
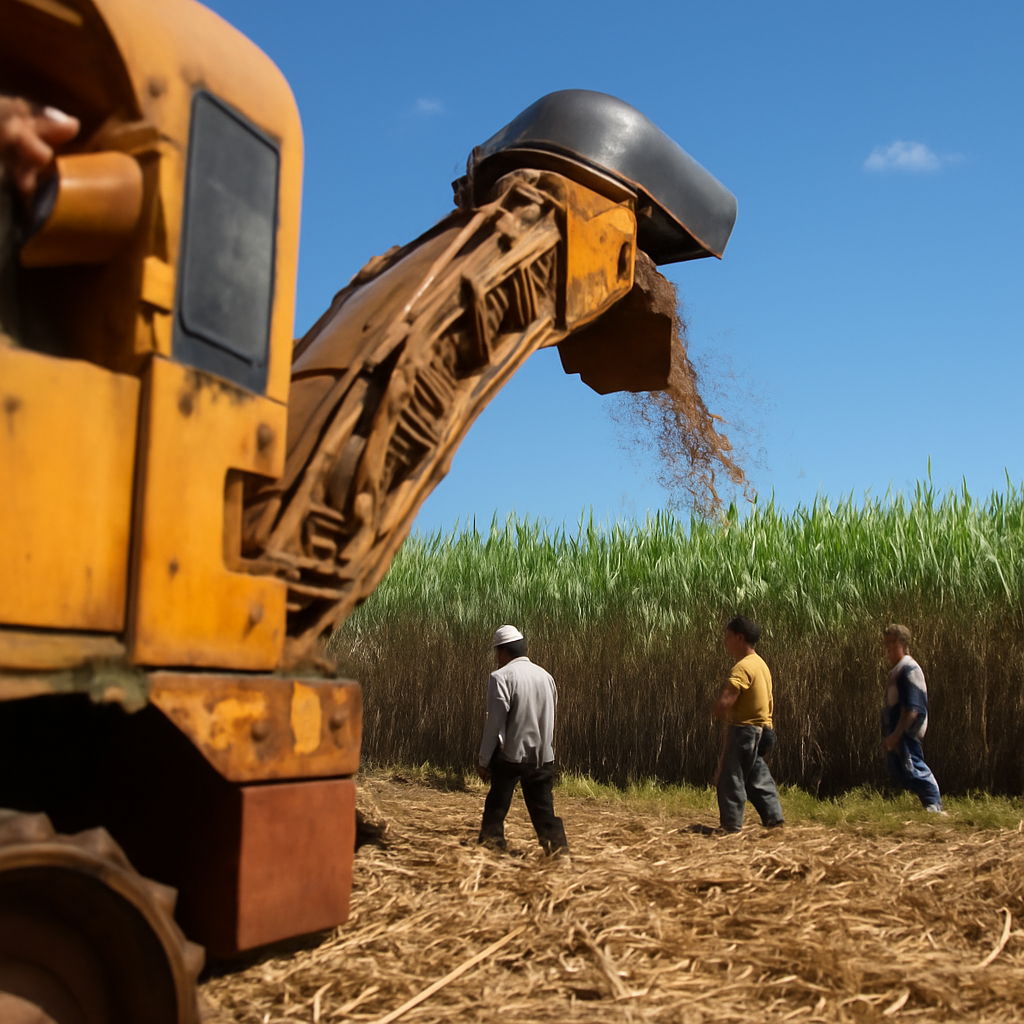
Mackay Sugar is making a sweet recovery after a cyberattack halted operations, with significant progress made over the weekend in restoring systems and a staged restart of crushing operations on the horizon. The company is getting back on track, with manual crushing already underway at its Farleigh Mill and harvesting expected to resume soon.
Beware of malicious JetBrains plugins masquerading as helpful tools - at least 15 have been detected stealing AI API keys from unsuspecting developers, with a staggering 70,000 installations. These fake plugins have been secretly siphoning off sensitive information since October 2025.
When Roman Imankulov asked his local AI agent to vet a suspicious code repository, it swiftly warned him away, saying "Don't run this code, just walk away - there's a trap." This near-instant response likely saved Imankulov from a malicious npm supply chain attack.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Beware: the Rokarolla malware is targeting 217 banking and crypto apps, allowing hackers to seize near-total control of your Android phone. It disguises itself as legitimate apps, often sneaking in through malicious websites offering fake Chrome or TikTok downloads.
Meet the BabaDeda Loader, a stealthy malware framework that's evolved to deliver a wider range of threats, including information stealers and remote access trojans, with alarming effectiveness. This revamped loader combines multiple evasion techniques to target vulnerable organizations, particularly in education and finance.
Police officers across the US have been caught misusing Flock surveillance cameras to obsessively and illegally stalk over a dozen individuals nationwide. This shocking abuse of power raises serious concerns about the protection of citizens' privacy and safety.
Critical Fortinet Sandbox vulnerabilities are under active attack, with hackers exploiting flaws like CVE-2026-39813, a severe path traversal bug that allows authentication bypass. Fortinet patched these bugs in April, but users must upgrade ASAP to avoid being compromised.
A simple mistake on breach notices sent by third-party vendor Xsolis sparked skepticism among patients when the letters misnamed Rochester Regional Health as "Rochester Regional Medical Center", leading many to dismiss them as scams. This misstep undermined trust and raised questions about the effectiveness of the breach notification process.
Cal Water is taking swift and decisive action to investigate allegations of a cybersecurity incident, swiftly activating its response plan and working around the clock to get to the bottom of the claim. The utility confirms that its probe, launched after learning of the alleged hacking by an Iran-linked group on June 11, 2026, is ongoing with no known operational disruptions reported so far.
Meet the sneaky ransomware gang that hijacked Microsoft Teams to secretly control its victims' systems for two whole months, using sophisticated cyber tradecraft to stay under the radar. They pulled off this impressive heist with a custom backdoor and some clever C2 traffic disguises.
Meet Rokarolla, a sneaky Android banking trojan that's taking aim at 217 banking and cryptocurrency apps with an arsenal of 137 remote commands, giving attackers alarming control over infected phones. This malicious malware is designed to outsmart even Google's Play Protect defenses, putting your financial security at risk.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
A China-linked espionage group has unleashed a stealthy backdoor that infiltrates Windows systems, targeting government bodies in Honduras, Taiwan, Thailand, and Pakistan. The malware, known as SprySOCKS, boasts advanced espionage features and kernel-level stealth, making it a formidable threat.
The Federal Trade Commission is sounding the alarm on imposter scams, which have led to a staggering $3.5 billion in losses - nearly triple the amount reported in 2020. This pervasive form of fraud has become the most reported category, accounting for almost a third of all fraud reports filed with the FTC.
Meet Rokarolla, a sneaky Android banking trojan that's taking device takeover to a whole new level, allowing scammers to isolate and exploit victims like never before. This malicious malware doesn't just steal credentials - it gives attackers total control over your phone.
A recent report has exposed a shocking security gap in a leading cardiac monitor manufacturer's system, leaving sensitive clinical monitoring data vulnerable to data thieves. This alarming breach highlights the urgent need for enhanced medical-device security and protection of patient information.
Meet Backdoor.Turn, a sneaky new threat that uses Microsoft Teams to hide its tracks and wreak havoc on your network for months on end - and it's surprisingly sophisticated. This Go-based RAT masquerades as legit traffic by exploiting Teams' TURN relay servers.
The US Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning about a critical cPanel plugin flaw, CVE-2026-54420, that's being actively exploited by hackers, posing a significant risk to all user-end plugin versions prior to 2.4.8. This vulnerability allows attackers to escalate privileges to root, putting your online security at risk.
ESET has uncovered a Windows variant of the SprySOCKS backdoor, previously thought to only affect Linux, marking a significant expansion of its capabilities. This new variant, version 1.8, uses driver-based stealth and can communicate through TCP, UDP, and WebSocket channels.
Cyber attackers are actively exploiting three high-severity Fortinet FortiSandbox vulnerabilities, CVE-2026-39813, CVE-2026-39808, and CVE-2026-25089, which were patched just last month and carry a near-critical CVSS score of 9.1. These flaws have been targeted in wide-ranging exploits over the past 24 hours, according to threat intelligence firm Defused Cyber.