Emerging Threats

Healthcare worker standing near medical equipment with blurred records in foreground.

UK Watchdog Cautions Healthcare Worker Over Royal's Medical Records Breach

When trust in healthcare settings is broken and personal info is mishandled, swift action is taken - as seen in the ICO's recent decision to issue a formal caution to a former healthcare professional for misusing sensitive patient data. The watchdog is clear: people's personal info must be safe from exploitation.

Analyst 207
Hospital corridor with blurred patient room doors and a lone computer workstation.

INC Ransomware Targets 830+ Victims, Expands as Major RaaS Threat

The INC ransomware group has rapidly grown into a major threat, claiming over 830 victims since August 2023, with US organizations making up more than 65% of those affected. Sectors such as legal services, manufacturing, and healthcare are among the most targeted, as INC expands its reach as a prominent Ransomware as a Service (RaaS) operation.

Analyst 207
Person working at desk with laptop and smartphone, surrounded by clutter, in a dimly lit room with a large window.

Malware Campaign Exploits AI, Fake GitHub Stars to Spread Crypto Clipper

This sneaky malware uses AI and fake GitHub stars to spread a crypto clipper that can steal your cryptocurrency by swapping your wallet address with the attacker's - and it's been designed to harvest small, repeated thefts from over 15,500 cryptocurrency wallet addresses. The malware operates stealthily, watching your clipboard for crypto wallet addresses and replacing them with an attacker-controlled address.

Analyst 207
USB drive plugged into a laptop on a cluttered office desk with cityscape in background.

Microsoft Exposes Windows Clipper Malware Campaign Using USB Worm.

Microsoft's security team has uncovered a sneaky malware campaign that's been secretly stealing cryptocurrency from Windows users since February 2026, using a clever combination of a USB worm and a stealthy Tor-based command center. The malware, known as a Windows Clipper, uses Windows Script Host and ActiveX to launch a Tor proxy and communicate with its command center.

Analyst 207
Brightly-lit office with CRM workstation, laptop on desk, and city view through window, hinting at a breached business…

Klue OAuth Breach Enables Icarus Extortion Attacks on Salesforce Data

A recent OAuth breach at market intelligence platform Klue has enabled a new extortion group called Icarus to steal sensitive Salesforce CRM data from multiple organizations, sparking a wave of ransom demands. Salesforce has swiftly responded by disabling the connection between Klue's Battlecards app and its platform to protect customers.

Analyst 207
Person working on laptop with Microsoft Teams open in a brightly-lit office setting.

DragonForce Hackers Exploit Microsoft Teams to Conceal Backdoor Traffic

Meet Backdoor.Turn, a sneaky malware that uses Microsoft Teams to hide its secret communication with hackers, leveraging the platform's relay infrastructure to stay under the radar. By masquerading as a legitimate connection, it allows attackers to remotely control infected systems undetected.

Analyst 207
Law enforcement officers from multiple countries gather in a government briefing room.

Law Enforcement Disrupts SocGholish Botnet Linked to Evil Corp

In a major win for cybersecurity, an international coalition of law enforcement agencies has dismantled the notorious SocGholish botnet, liberating nearly 15,000 compromised WordPress sites and taking down 106 servers and domains used by cybercriminals. This bold operation has effectively cut off the cybercrime gang's access to thousands of infected computer systems.

Analyst 207
Dimly lit server room with rows of computer equipment and a blurred figure in the background.

Telco Exposes Customer Data in Cleartext, Ignoring Basic Security Protocols

A new hire was granted sudo-level access to a live production database on their first day, with management's casual instruction to "take a look" - and promptly uncovered customer records stored in easily accessible cleartext. This alarming lapse in security protocols left sensitive customer information, including full personal details and payment numbers, exposed and vulnerable.

Analyst 207
Rack of networking equipment in a brightly-lit municipal network closet.

Fortinet and Ivanti Exploits Fuel LATAM Infrastructure Attacks

In a shocking revelation, a coordinated campaign dubbed Operation Escaneo has been exposed, targeting critical infrastructure across Mexico, Ecuador, and Portugal, with a staggering 3,708 sessions recorded over just 13 days. The attackers exploited vulnerabilities in Fortinet and Ivanti perimeter appliances to gain entry into government, tax authorities, utilities, transport, telecoms, and banks.

Analyst 207
Formal setting with podium in front of large window, neutral color palette.

Nation-States Drive 75% of UK Critical Infrastructure Cyber-Attacks, NCSC Warns

The UK's National Cyber Security Centre has warned that a staggering 75% of critical infrastructure cyber-attacks in the UK are driven by nation-states, with 200 incidents reported in the past year alone. This alarming trend highlights the growing threat of state-sponsored cybercrime, with countries like Russia, China, and Iran linked to many of these attacks.

Analyst 207
Busy Southeast Asian city street with people using smartphones and laptops amidst modern buildings and shops.

Cybercrime Exploits APAC's Rapid Digitalization

Cybercrime is rapidly overtaking traditional crime in APAC, with nearly a third of crime in over half the region's countries now online, according to Interpol's latest report. The alarming trend highlights the urgent need for stronger cross-border collaboration to combat the evolving threat.

Analyst 207
Smartphone lies cracked on a bench in a bustling Asia-Pacific city street.

Cybercrime Surges Across Asia and South Pacific, Hits 30% of All Crime

Cybercrime is surging across Asia and the South Pacific, now accounting for over 30% of all recorded crime, with organised networks leveraging AI, ransomware, and social engineering on a massive scale. The rapid rise is driven by rapid digital adoption and new technologies.

Analyst 207
Microsoft headquarters with a laptop and cybersecurity setup, emphasizing protection and security.

Microsoft Tackles RoguePlanet Defender Flaw with Imminent Patch

Microsoft is working on a patch to fix a serious security flaw in Microsoft Defender, known as RoguePlanet, which could allow hackers to gain elevated privileges on affected systems. A high-quality security update is imminent to address this vulnerability and protect users.

Analyst 207
Laptop screen on a desk in a brightly-lit indoor setting with blurred smartphones and tablets in the background.

Malware Campaign Exploits Fake Reviews to Spread Crypto Clipper

A single threat actor cleverly mimicked legitimate brands to spread Crypto Clipper Malware, using fake reviews, tutorial videos, and promotions on trusted platforms to manufacture credibility for a malicious crypto tool. They created a convincing illusion of a trusted product, complete with inflated download counts and coordinated five-star reviews.

Analyst 207
Technicians work on equipment in the background of a brightly-lit network operations center with rows of computer racks.

Attackers Exploit Critical Fortinet Vulnerabilities Disclosed in April

Security researchers have confirmed that hackers are actively exploiting critical vulnerabilities in Fortinet's FortiSandbox product, first patched in April, with multiple independent groups jumping on the bandwagon. The exploitation attempts, observed as early as June 9, involve OS-command injection and path-traversal flaws.

Analyst 207
Interior of a Kodak facility with industrial and corporate elements, blurred computer equipment, and a neutral-toned server…

Kodak Breach Exposes 2.2M Records to ShinyHunters Threat Group

Kodak has confirmed a major data breach, with the ShinyHunters threat group claiming to have stolen 2.2 million records, including sensitive customer information. The company is working closely with law enforcement and cybersecurity experts to address the breach.

Analyst 207
Network equipment and servers in a server room with blinking lights and laptop screens in the foreground.

Fortinet Firewalls Compromised in Massive Password-Stealing Attack

A massive password-stealing attack has compromised around 75,000 Fortinet firewall devices, putting credentials of major corporations across 194 countries at risk and leaving a trail of full network compromises in its wake. The breach, dubbed FortiBleed, has created a verified database of working credentials for some of the world's largest enterprises, threatening nearly every sector of the global economy.

Analyst 207
Cluttered computer workstation with laptop and cables in a small, cramped business office setting.

Hackers Exploit Tailscale for Persistent Access After C2 Takedown

Meet Poisson, a French-speaking hacker who left a digital trail of 339 commands over 33 days, revealing a clever exploit that allowed them to maintain persistent access to a small French automotive business even after a C2 takedown. The intruder's step-by-step playbook was surprisingly left in an open storage bucket, giving Cato Networks researchers a glimpse into their tactics.

Analyst 207
Cluttered room with stacked laptops and equipment, cables visible through laptop screen.

North Korean Hiring Scam Exposed with AI, US Laptop Farms

Meet the ingenious AI-powered sting operation that busted a North Korean hiring scam, exposing a massive laptop farm churning out fake remote IT workers. A suspicious resume sparked the investigation, leading to a shocking discovery of a closet full of machines impersonating candidates for Western companies.

Analyst 207
Rows of equipment racks and networking gear in a brightly-lit server room.

FortiBleed Exposes 73,000 Fortinet VPN Credentials Worldwide

A massive security breach has exposed a whopping 73,000 Fortinet VPN credentials worldwide, putting tens of thousands of firewall endpoints at risk, including those of major companies like Chevron, Samsung, and Mercedes-Benz. The alarming leak, discovered by security researcher Bob Diachenko, contains sensitive information like usernames, email addresses, and plaintext passwords.

Analyst 207
Cloud computing setup with laptop and servers in a bright office, hint of phishing activity.

GitHub Phishing Kit Targets Mexican Banks via Cloud Services

A sneaky GitHub phishing kit called "GitBait" has been targeting customers of 12 Mexican banks for three years, cleverly using cloud services like GitHub Pages and Google Sheets to stay under the radar. This cunning operation relied on over 100 GitHub-hosted domains to steal credentials, making it a challenging case for investigators.

Analyst 207
Cybersecurity team members look concerned and overwhelmed while analyzing data on a large screen.

AI-Powered Attacks Exacerbate Alert Fatigue in Cybersecurity Teams

Cybersecurity teams are drowning in data, but struggling to turn it into action - and AI-powered attacks are making alert fatigue worse. With AI-powered attacks topping the list of concerns for 41% of cybersecurity leaders, it's clear that teams need a new approach to stay ahead.

Analyst 207
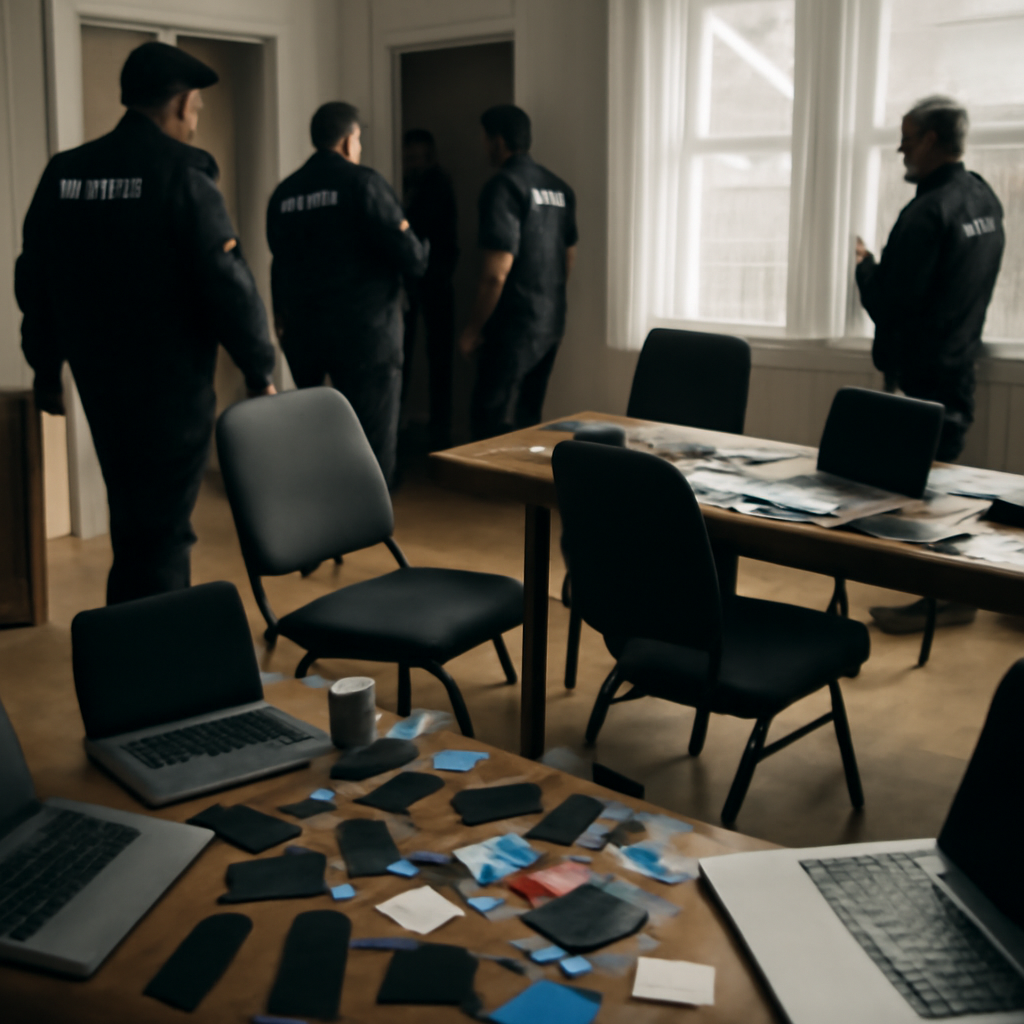
Police officers raid a makeshift call centre, finding scattered laptops, phones, and bank cards amidst abandoned chairs.

Dutch Police Disrupt Helpdesk Scam Ring with In-Person Tactics

Dutch police stormed a makeshift call centre in Amsterdam, catching six suspects in the act of running a helpdesk scam ring and making off with multiple laptops, phones, and bank cards. The daring raid, which happened on June 10, has put a dent in the operation, but police warn that further arrests may be on the horizon.

Analyst 207
Developer workstation with laptop, monitor, and coding materials, surrounded by a potted plant and papers, with a JetBrains…

Malicious Plugins Exfiltrate AI API Keys

Beware of malicious AI plugins masquerading as coding assistants on the JetBrains Marketplace - they might just steal your AI API keys. These 15 sneaky plugins, active since October 2025, cleverly exfiltrate API keys to attacker-controlled servers, all while functioning as promised.

Analyst 207